Acronis TRU and VirusTotal collaborated to hunt and analyze three campaigns—FileFix (a ClickFix variant using clipboard-based web payload delivery), SideWinder (document-based attacks exploiting CVE-2017-0199 and CVE-2017-11882), and Shadow Vector (judicial-themed malicious SVGs targeting Colombia)—by combining Livehunt, Retrohunt, VT Diff, and metadata filtering to map infection chains and infrastructure. The investigations produced YARA/livehunt rules, IOC pivots (e.g., decoy RTF hash and multiple SVG hashes), and practical VT hunting techniques for detecting web-based and document-based threats. #FileFix #SideWinder
Tag: THREAT HUNTING
Threat intelligence gathers and contextualizes external data about who might attack, their motives, and relevant indicators, while threat hunting proactively searches internal environments for hidden or ongoing intrusions that defenses missed. Together they form a feedback loop that improves detection, prioritization, and response by enriching hunts with intelligence and feeding findings back into intelligence programs. #RecordedFuture
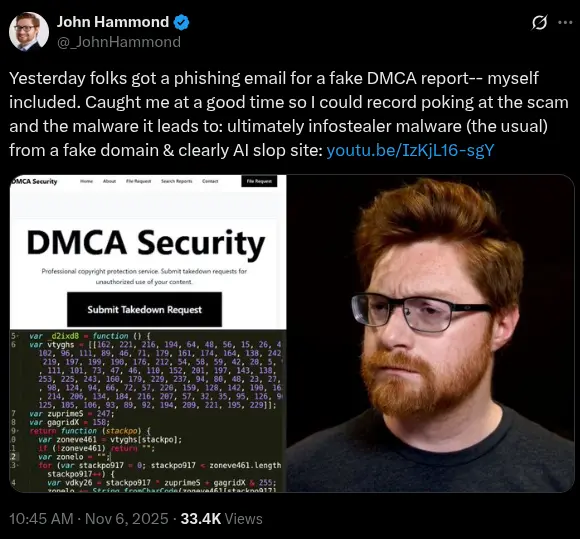
On November 5, 2025, multiple high-profile YouTube creators reported receiving fake DMCA takedown notices that linked to malicious downloads, prompting researchers to analyze the campaign and disclose numerous related domains and IPs. Public analysis identified phishing domains (e.g., dmca-security[.]com, ms-team-ping4[.]com), rotating infrastructure with distinctive host banners and certificates, and additional related domains discovered via DNS and host-response pivots. #dmca-security #ms-team-ping4
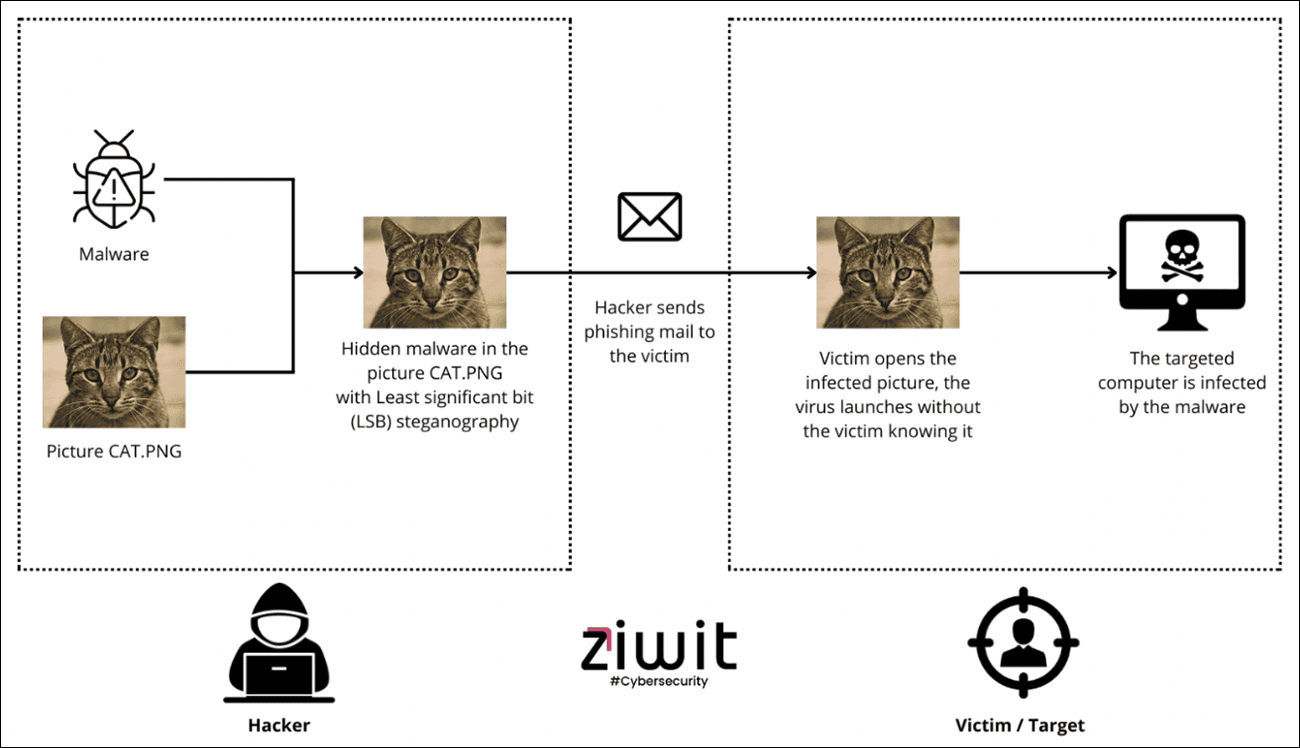
Arctic Wolf Labs discovered a Brazilian-origin Loader-as-a-Service called Caminho that uses LSB steganography to hide .NET loaders inside images hosted on legitimate platforms and delivers diverse payloads including REMCOS RAT, XWorm, and Katz Stealer. The multi-stage campaign uses spear-phishing with obfuscated JS/VBS and PowerShell stages, in-memory .NET loading and process injection,…
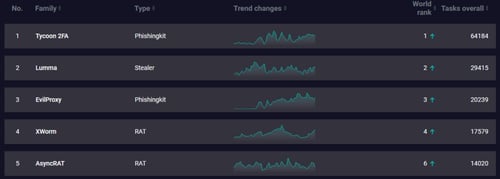
Tycoon 2FA is a Phishing-as-a-Service platform that uses an Adversary-in-the-Middle reverse proxy to capture credentials and session tokens from Microsoft 365 and Gmail logins, bypassing 2FA/MFA by relaying codes in real time. The kit uses obfuscated JavaScript, bot/debugger checks, hosted assets on services like Amazon S3, and dynamic templates to tailor attacks to organization-specific policies. #Tycoon2FA #Microsoft365 #Gmail
Agentic AI transforms traditional AI tools into autonomous systems capable of planning, executing, and collaborating across services, which offers significant operational advantages but also introduces new security risks. Proper governance, controls, and oversight are crucial to harness its benefits while minimizing vulnerabilities. #AgenticAI #AutonomousSystems…
DORA forces EU financial organizations to adopt proactive, testable ICT risk management, moving security “left of boom” to detect threats before they materialize using Indicators of Future Attack (IOFA)™. Silent Push maps its IOFA-centric platform to DORA’s five pillars to provide continuous monitoring, incident response support, resilience testing, third-party risk visibility,…
Ransomware threats are accelerating in volume, velocity, and sophistication—driven by RaaS, AI-enabled attacks, and identity-based intrusions—making traditional, signature-based detection insufficient. Organizations need timely, relevant, intelligence-driven data and integrated technologies (threat intelligence, ML/AI, behavioral analytics, automation) to detect and prevent ransomware early. #Ransomware-as-a-Service #RecordedFuture

European organizations experienced a significant 13% rise in ransomware attacks, with UK targets most affected, according to CrowdStrike’s 2025 European Threat Landscape Report. The report highlights the prominence of big-game hunting and the increasing menace of violence-as-a-service linked to heightened criminal activities across Europe. #CrowdStrike #RansomwareGroups…

Security Operations Centers face challenges including alert fatigue and lack of context, which hinder effective threat detection and response. Integrating continuous exposure management enhances SOC workflows by providing real-time attack surface visibility and contextual threat intelligence. #MITREATTACK #ExposureManagement…
Datadog observed a rise in supply-chain and developer-tooling attacks in Q3 2025, including widespread npm account compromises via phishing and a self-replicating npm worm (Shai-Hulud) that exfiltrated GitHub tokens and propagated across packages. The report also highlights malicious VS Code extensions, AI-assisted malware (e.g., LameHug) using external LLM APIs, and persistent risks from long-lived cloud credentials and fraudulent deepfake job profiles. #Shai-Hulud #S1ngularity
The FCC plans to revoke cybersecurity regulations previously imposed on telecom companies following Chinese hacking attacks linked to Salt Typhoon. The agency argues that telecoms have already taken voluntary security measures and that the earlier regulations were overly rigid and unnecessary. #SaltTyphoon #ChineseHackers…
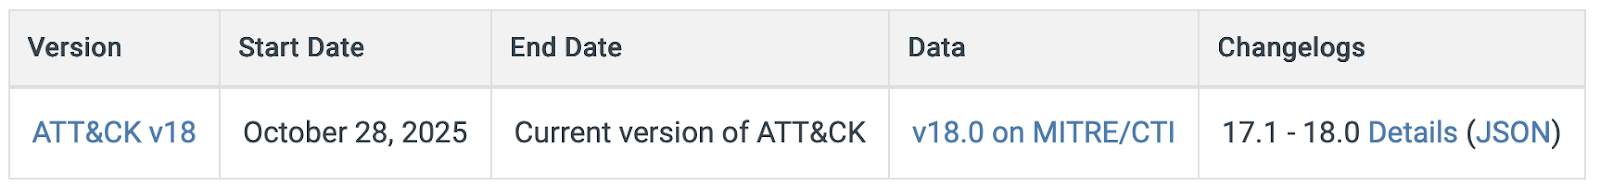
MITRE ATT&CK v18.0 replaces legacy Detections and Data Sources with a behavior-driven two-tier model of Detection Strategies and Analytics, improving telemetry mapping and cross-tactic correlation to better reflect real-world adversary behavior. The release adds 12 new techniques across Enterprise, Mobile, and ICS and signals future tactic reorganization and expanded coverage while vendors like Picus Security map tests and detections to the new model. #DET0525 #AN0850

This article explores the critical importance of detecting lateral movement within internal networks after initial intrusion, focusing on internal devices like routers, printers, and IoT devices. It emphasizes monitoring for suspicious connections to high-risk countries and internal endpoints to prevent escalation and exfiltration activities. #CyberThreatHunting #InternalNetworkSecurity
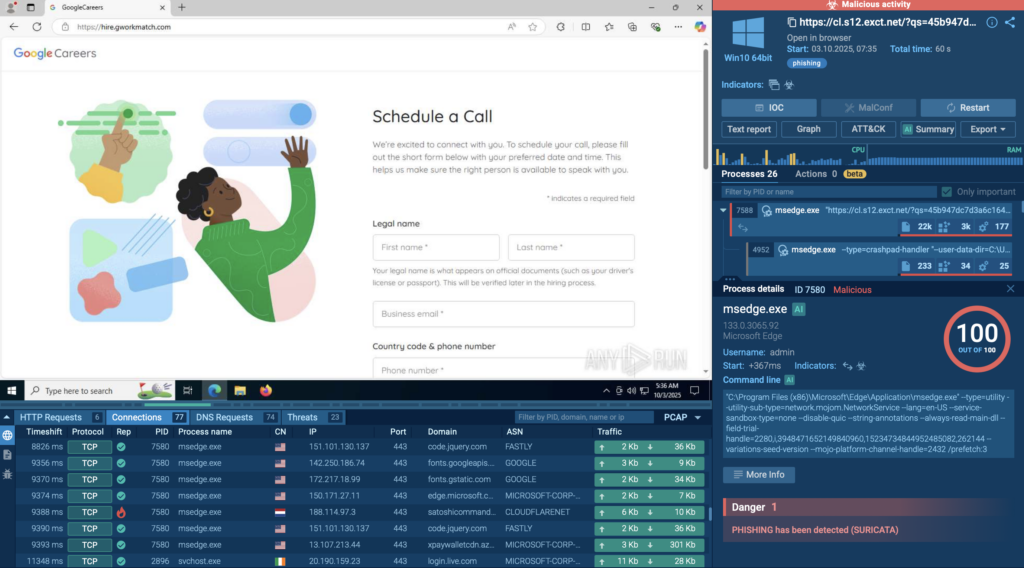
October saw rapid evolution of phishing and ransomware campaigns that increasingly abused legitimate cloud services (Figma, ClickUp, Salesforce, Azure Blob Storage) and layered CAPTCHAs and redirects to evade detection, with new toolsets like TyKit and LockBit 5.0 expanding impact to Microsoft 365 accounts, ESXi, and Linux systems. #TyKit #LockBit5 #Figma #ClickUp…