Privileged access is the primary pathway attackers use to achieve high-impact compromises, and protecting both human and non-human privileged identities across on-premises and cloud environments is essential. Mandiant recommends a defense-in-depth PAM strategy—tiering, least privilege, PAWs, MFA, secrets management, detection (high-fidelity session telemetry and anomaly analytics), and practiced response including coordinated credential rotation—to reduce dwell time and blast radius. #Mandiant #GoogleSecOps
Tag: THREAT HUNTING
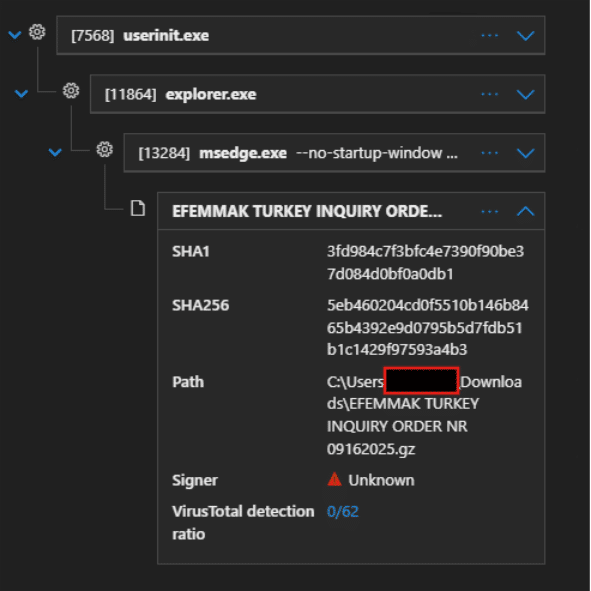
CyberProof observed a surge in a Remcos infostealer campaign in Sep–Oct 2025 that used malicious email attachments, obfuscated PowerShell, and process hollowing of msiexec into RMClient.exe to deploy Remcos and harvest browser-stored credentials. The operation used compromised or malicious domains (e.g., icebergtbilisi.ge) to host payloads and employed continuous download-and-execute loops to ensure delivery. #Remcos #icebergtbilisi.ge
A critical unauthenticated RCE vulnerability in Windows Server Update Services (CVE-2025-59287) was actively exploited in the wild shortly after Microsoft released an emergency patch on Oct. 23, 2025, prompting CISA to add it to the KEV catalog. Unit 42 observed exploitation chains leveraging unsafe deserialization via GetCookie() and ReportingWebService endpoints, with…
APT-C-60 intensified operations against Japanese organizations in Q3 2025, deploying SpyGlace backdoor versions 3.1.12–3.1.14 with refined delivery (direct VHDX attachments), enhanced evasion, and sophisticated abuse of GitHub, StatCounter, and Git for stealthy payload distribution. #APT-C-60 #SpyGlace #GitHub #StatCounter
AzureHound is an open-source data collection tool used to enumerate Microsoft Entra ID and Azure resources via Microsoft Graph and Azure REST APIs, and while intended for defensive testing, threat actors have misused it for cloud discovery and privilege escalation mapping. Recent activity links its misuse to actors such as Curious…
This article highlights the malicious use of the Windows utility auditpol.exe by attackers to disable and hide security audits and forensic traces. Monitoring and detecting unauthorized execution of auditpol can serve as a crucial early warning for security threats. #AuditpolMisuse #SecurityAuditing
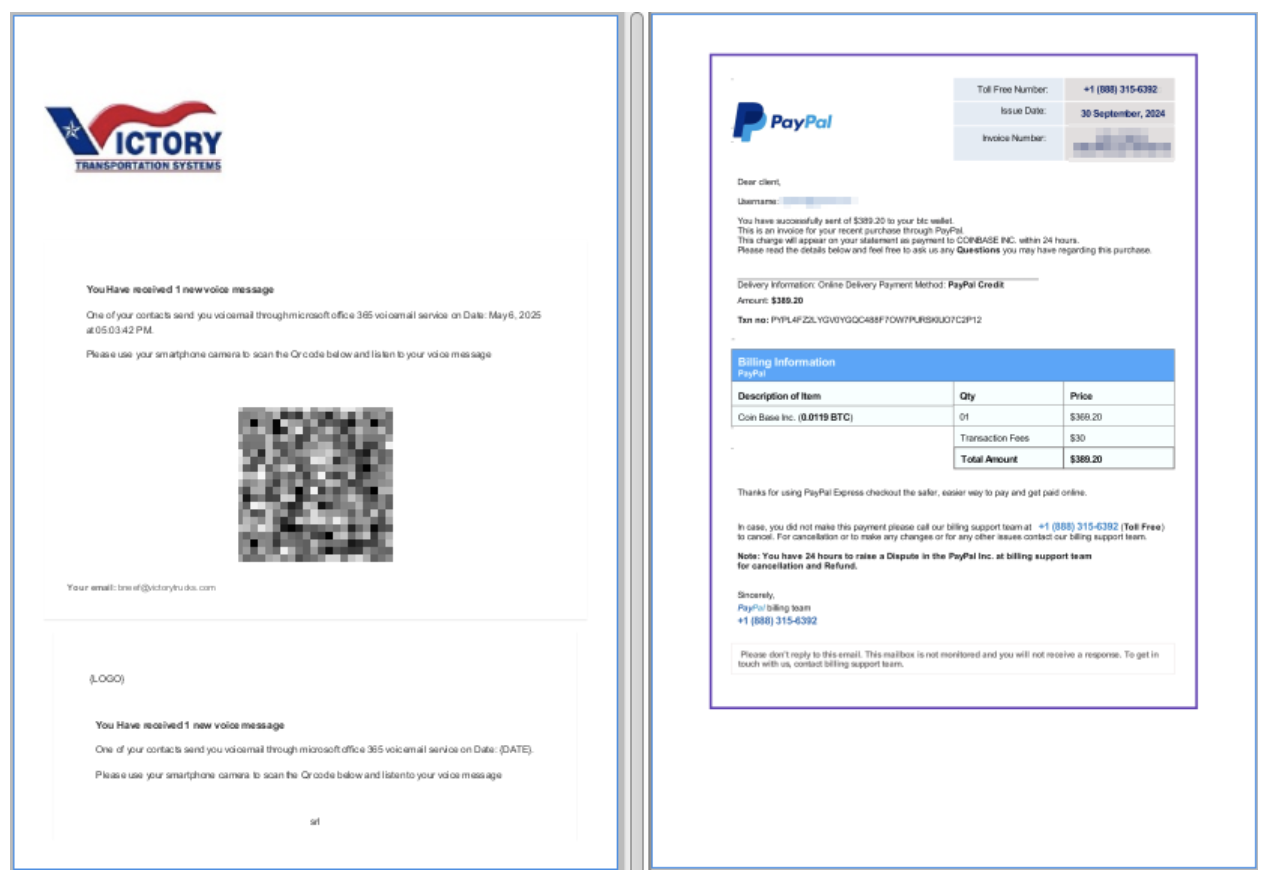
Proofpoint released an open-source tool called PDF Object Hashing to create detection rules that fingerprint PDFs by their internal object structure, enabling detection and clustering even when PDFs are obfuscated, encrypted, or have changing lure content. The technique has been used internally to track multiple threat actors including UAC-0050 and UNK_ArmyDrive…
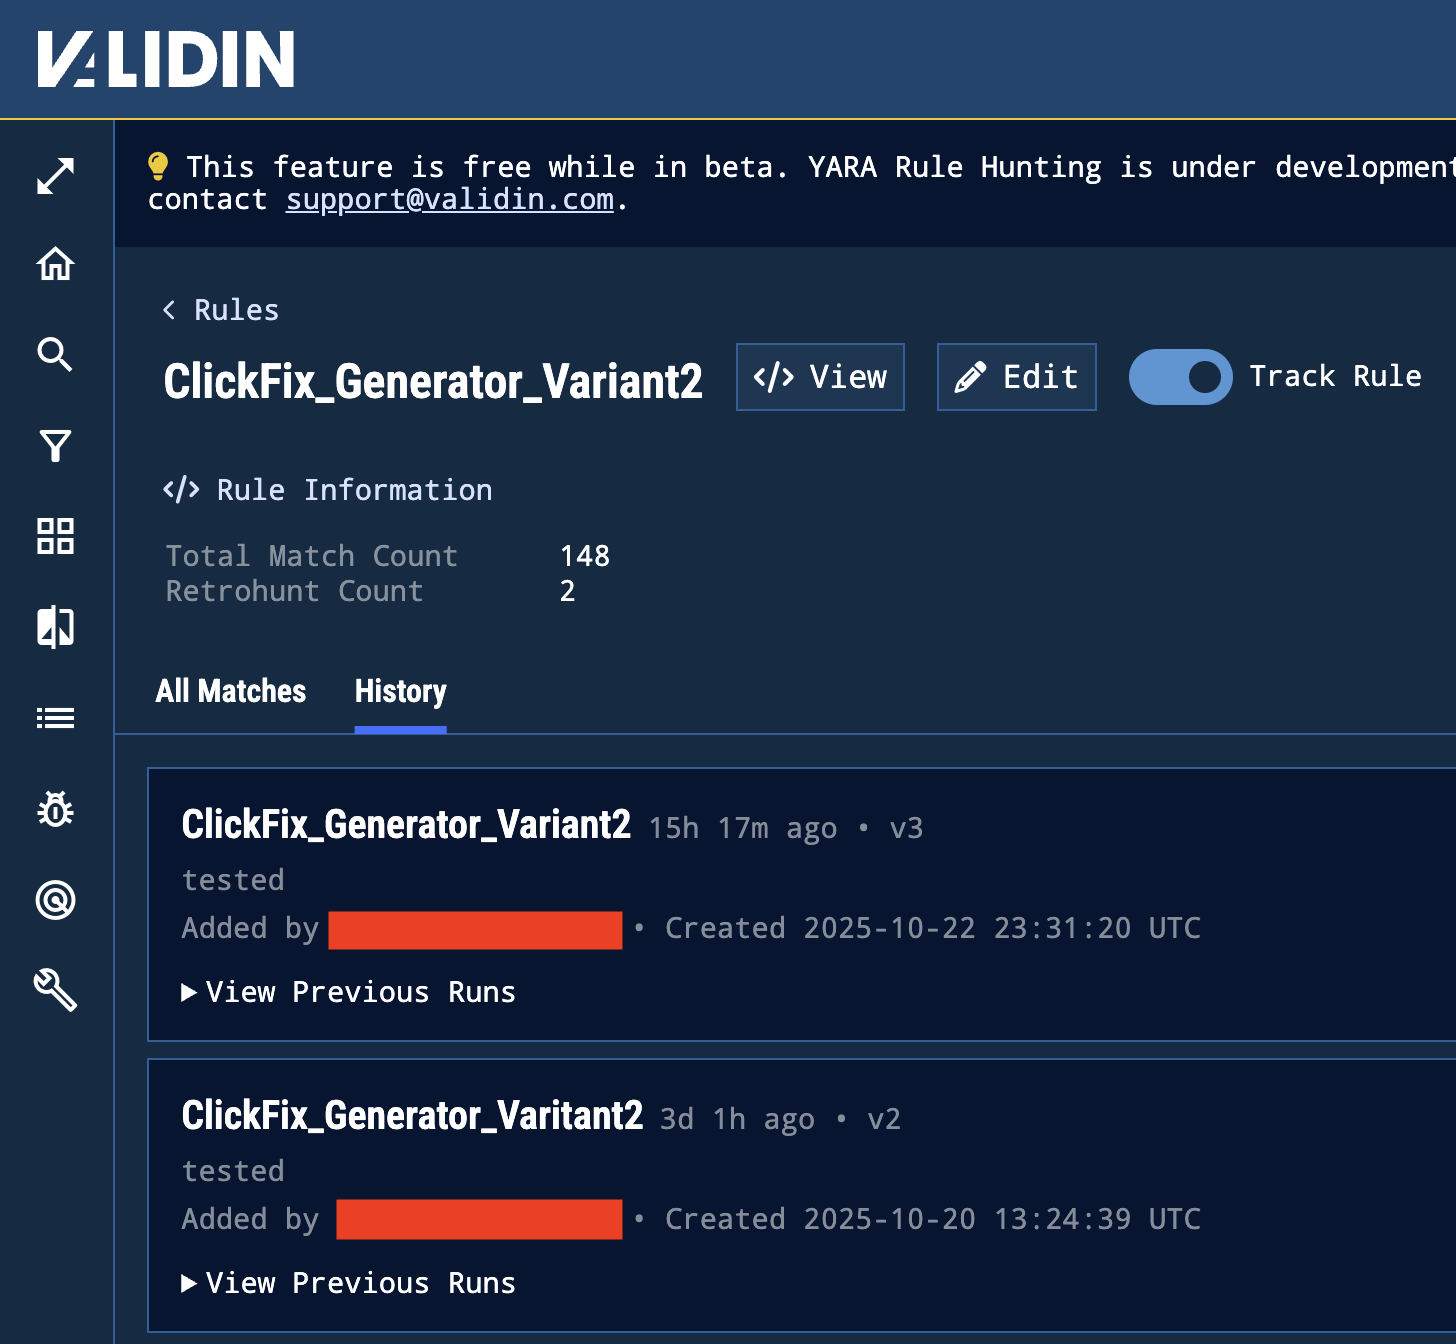
Validin has extended its YARA-X integration to run YARA rules continuously on live host response data, enabling timestamped, contextual detections across a dataset of over 850 million daily host responses. New features include a YARA playground, rule versioning, Projects for collaborative investigations, and demonstrated detections of ClickFix-related HTML and JavaScript injections. #ClickFix #IUAM
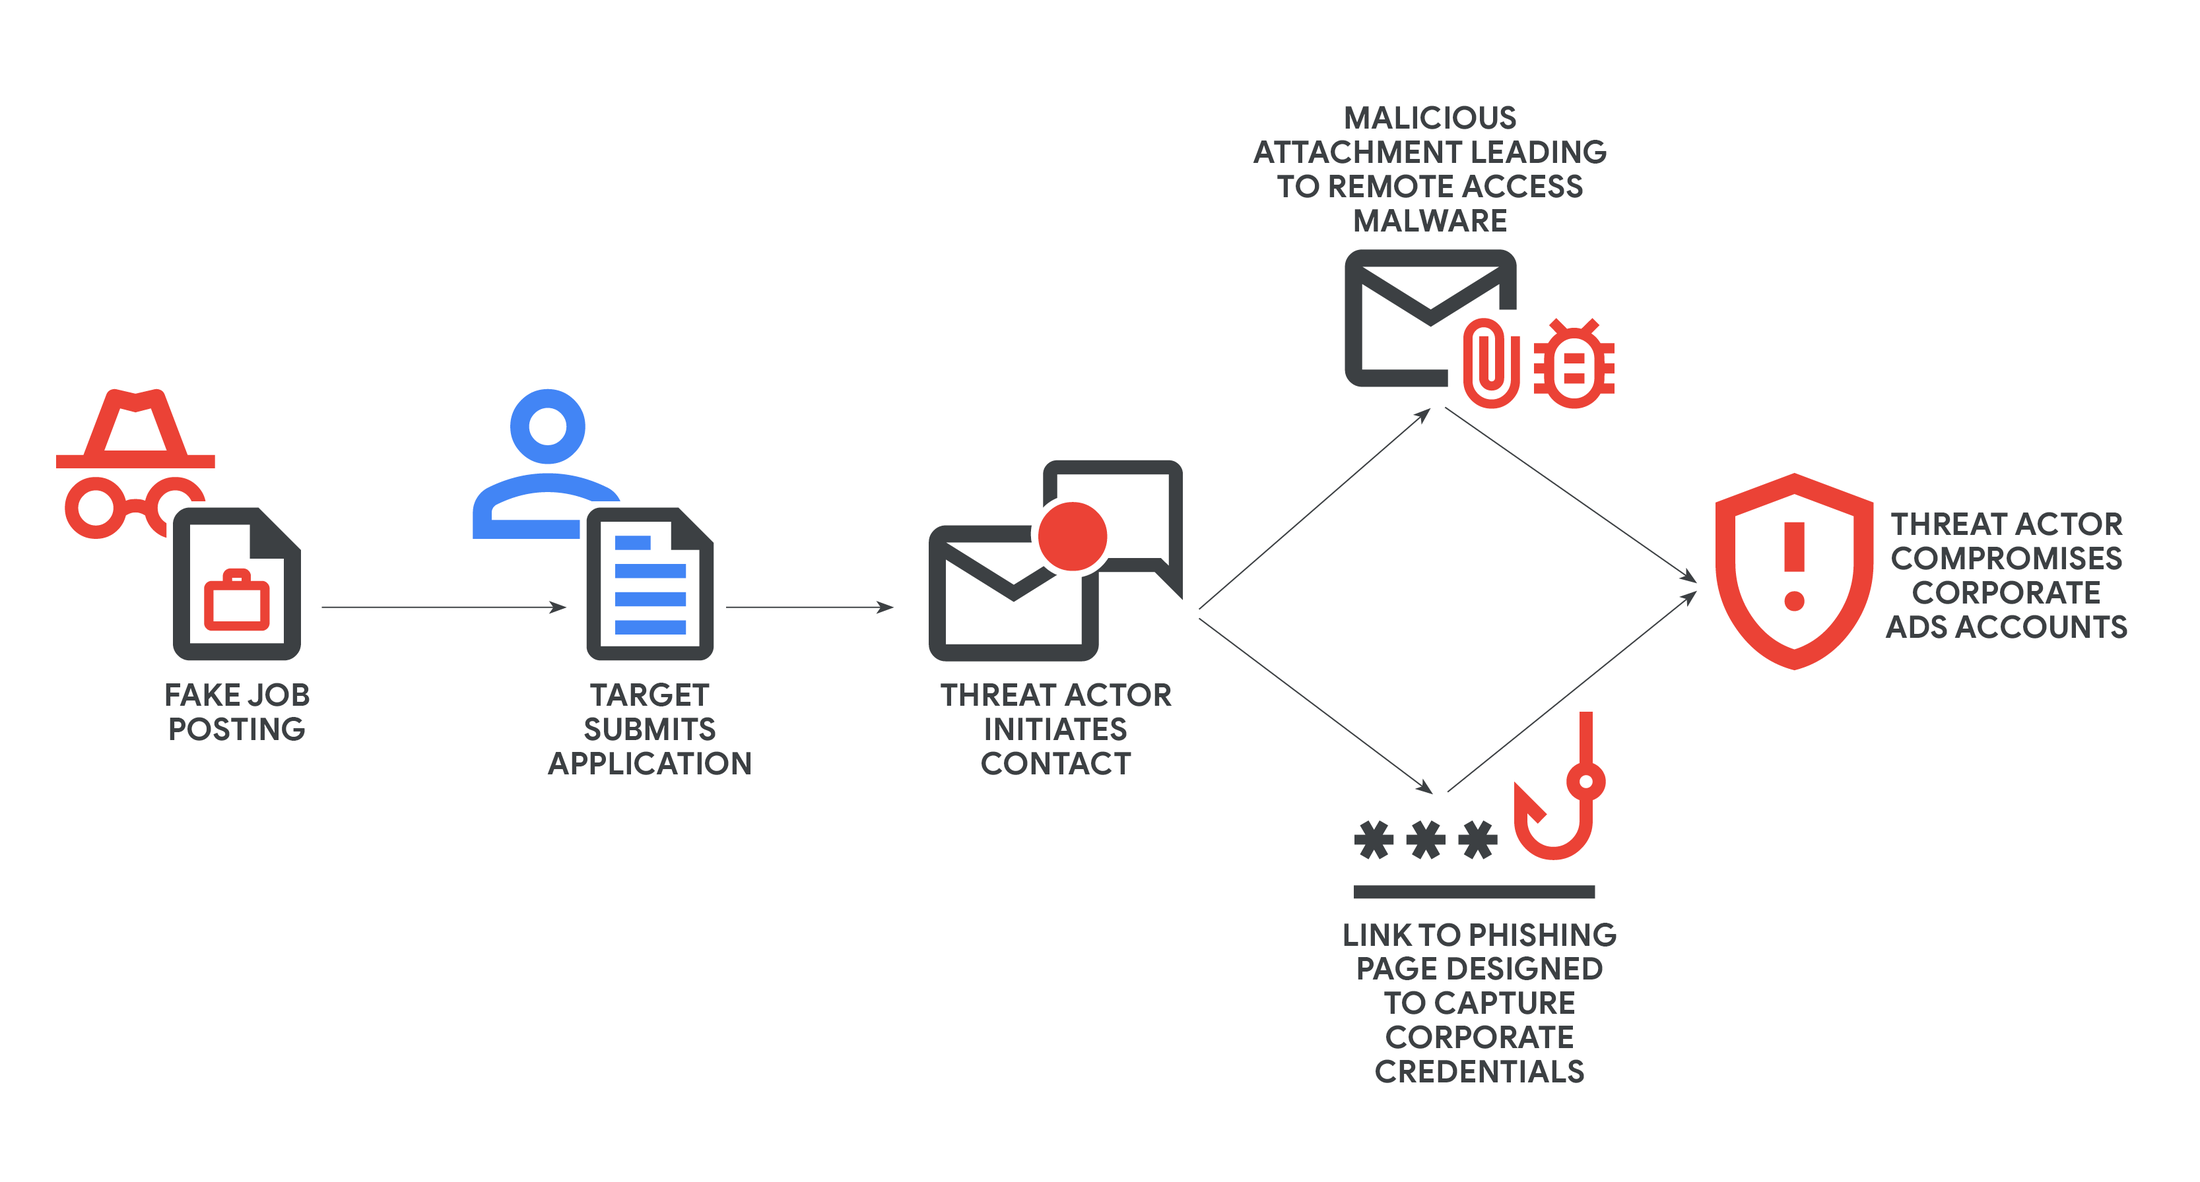
GTIG tracked a Vietnam-based cluster UNC6229 that uses fake job postings on legitimate platforms and abused CRM/SaaS services to socially engineer digital advertising workers into downloading RATs or entering credentials on phishing pages to steal corporate ad/social accounts. The campaign leverages personalized follow-ups, password-protected attachments, and convincing phishing kits (including MFA-capable pages) to monetize access by selling ad inventory or compromised accounts. #UNC6229 #staffvirtual.website
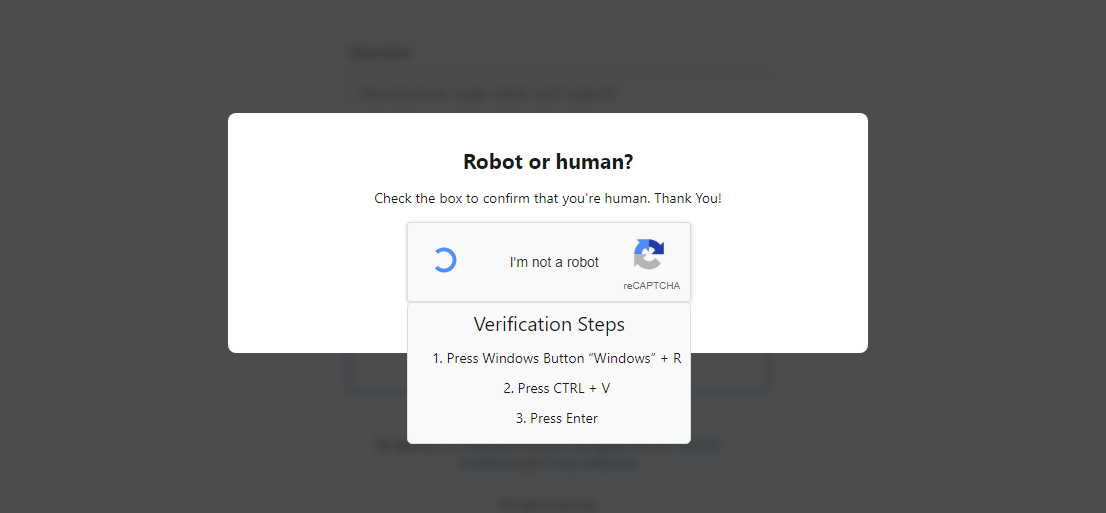
eSentire’s TRU investigated numerous 2025 incidents where threat actors abused legitimate NetSupport Manager RMM, primarily delivered via the ClickFix social engineering vector and executed through PowerShell/JSON, Run Prompt loaders, and MSI-based installers. The report clusters activity into three distinct actor groups (EVALUSION, FSHGDREE32/SGI, XMLCTL), provides IOCs and deobfuscation guidance, and includes detection tooling such as a Yara rule and an unpacking utility. #NetSupport #ClickFix
Infoblox and UNODC-linked research uncovered Vault Viper (Baoying Group / BBIN), a large iGaming white-label operator distributing a custom “Universe Browser” that routes traffic through China and installs persistent background programs with functionality consistent with RATs and information stealers. The investigation ties Vault Viper to transnational organized crime networks including Suncity and convicted Triad leader Alvin Chau, and documents a vast DNS and C2 footprint used to support online gambling, fraud, and money laundering. #VaultViper #UniverseBrowser
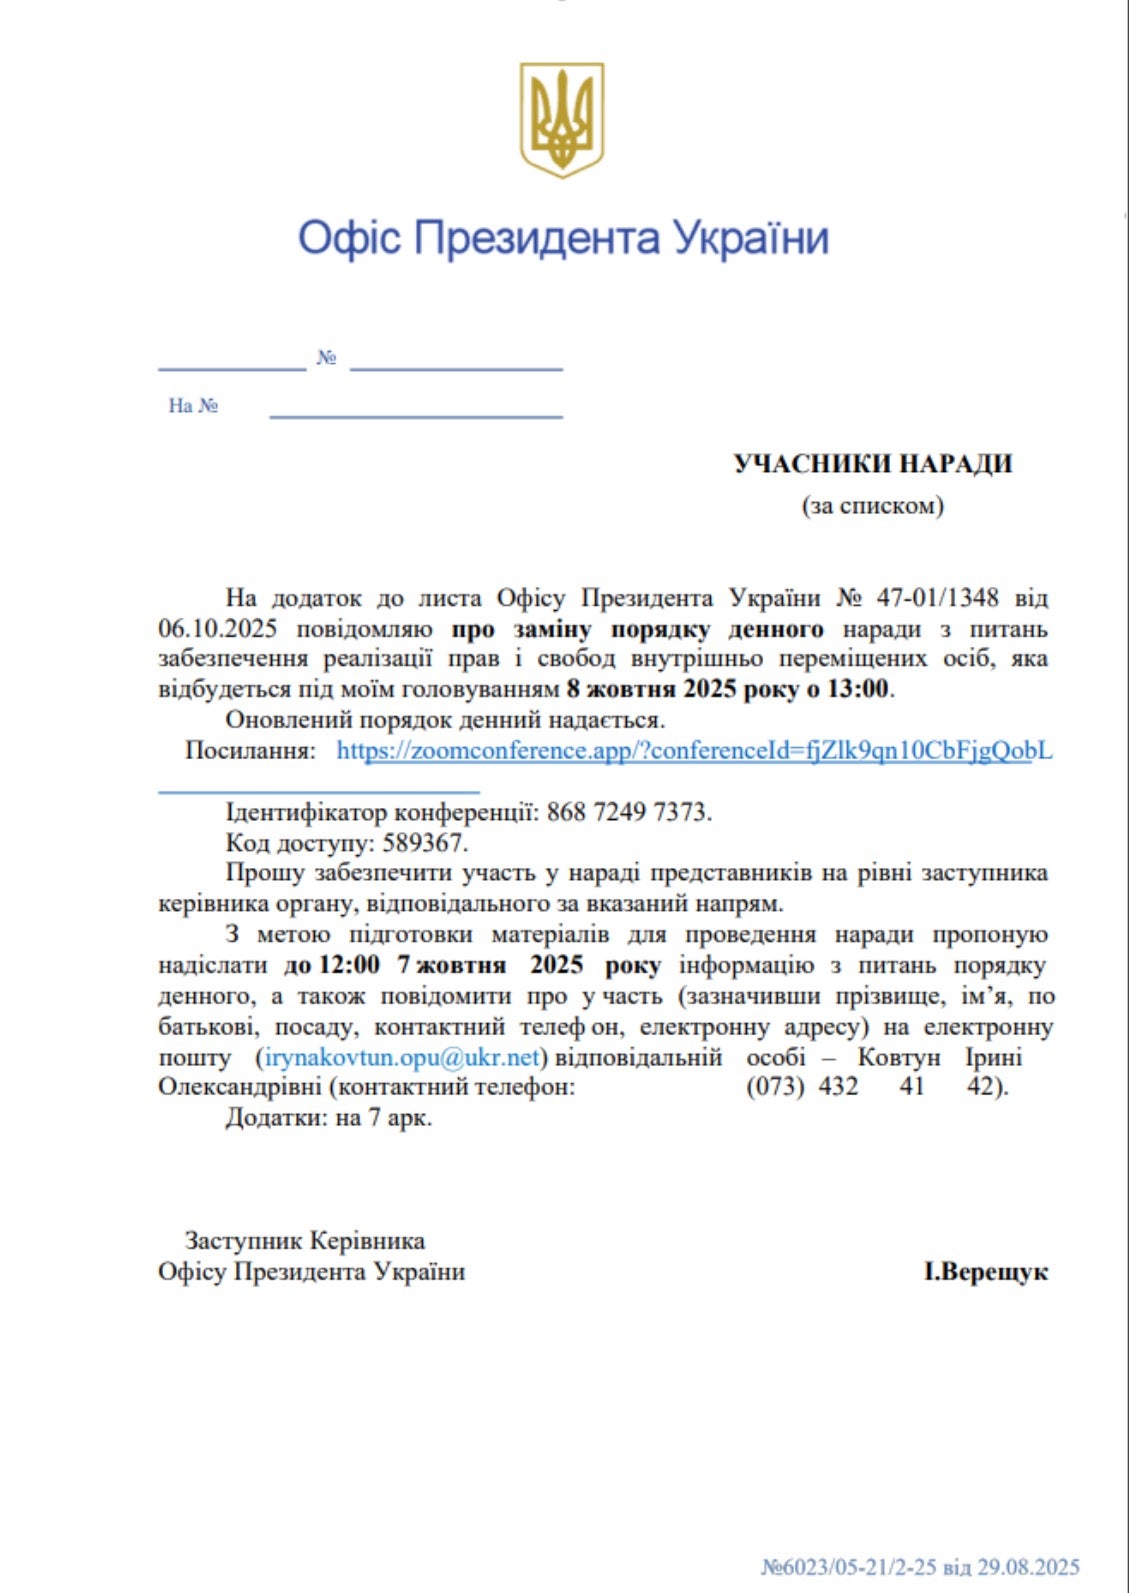
A coordinated spearphishing campaign called PhantomCaptcha targeted NGOs and Ukrainian regional administrations using weaponized PDFs that redirected victims to a fake Cloudflare captcha and coerced them into executing PowerShell loaders. The multi-stage attack delivered a WebSocket RAT and also pivoted to Android lures (princess.apk) hosted on related domains and infrastructure. #PhantomCaptcha #bsnowcommunications #princess.apk
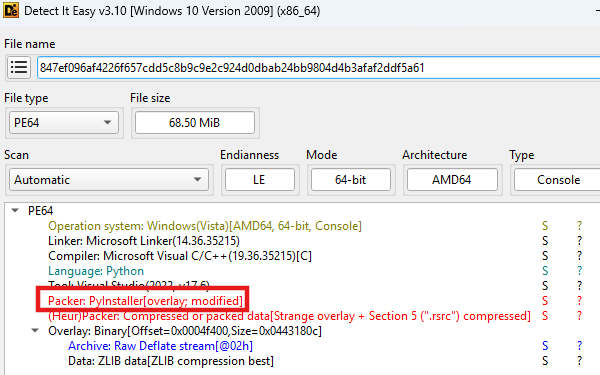
Netskope discovered a new Python-based remote access trojan that impersonates a Minecraft client named “Nursultan Client” and uses the Telegram Bot API as its command-and-control channel to steal Discord tokens, capture screenshots and webcam images, and perform system reconnaissance. The sample includes a hardcoded Telegram bot token and allowed user ID, demonstrates cross-platform C2 capabilities despite flawed Windows persistence, and appears to be a Malware-as-a-Service offering signed “by fifetka”. #NursultanClient #TelegramBotAPI
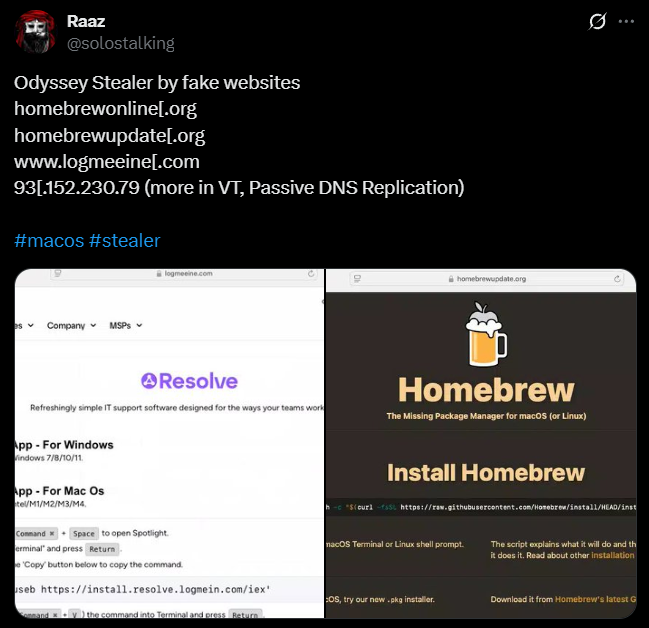
A coordinated campaign is impersonating developer tools and trusted services to trick macOS users into pasting base64-encoded curl commands that fetch and execute installer scripts delivering Odyssey Stealer and AMOS. Operators reuse infrastructure, SSL certificates, and domains (e.g., 93.152.230[.]79, 195.82.147[.]38, bonoud.com) to maintain persistence and scale across at least 85 phishing sites. #OdysseyStealer #AMOS #93.152.230.79 #195.82.147.38

AI-SOC platforms automate triage, correlation, and enrichment to handle large alert volumes, enabling machine-speed operations and a sustainable hybrid SOC with human oversight. The article argues for a co-managed transition where AI handles scale and speed while humans provide context, accountability, and ROI-focused paths for MSSPs and MDRs. #RadiantSecurity #AI_SOC #MSSP #MDR #PagerDuty