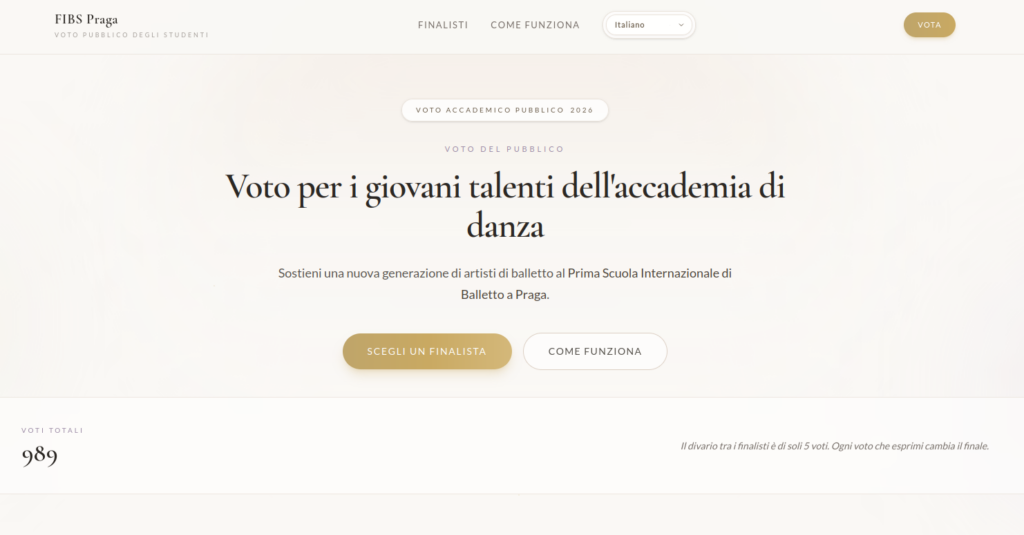
A WhatsApp phishing campaign known as the “ballerina scam” is again circulating through messages sent from compromised contacts, tricking victims into visiting fake voting sites and authorizing access to their accounts. The attackers use the verification code to link their own device to the victim’s WhatsApp account, enabling session hijacking, message monitoring, and further spread to new targets. #WhatsApp #CERTAGID
Category: Threat Research
About 9.4% of Windows computers with Acronis EDR enabled were running an AI agent tool from June to September 2026, with most use shifting beyond developers into graphical desktop apps like Claude Desktop and Visual Studio Code. The report also warns that MCP-enabled connections are rarely switched on, but when they are, they can expose business systems to untracked outside access. #AcronisEDR #ClaudeDesktop #VisualStudioCode #MCP
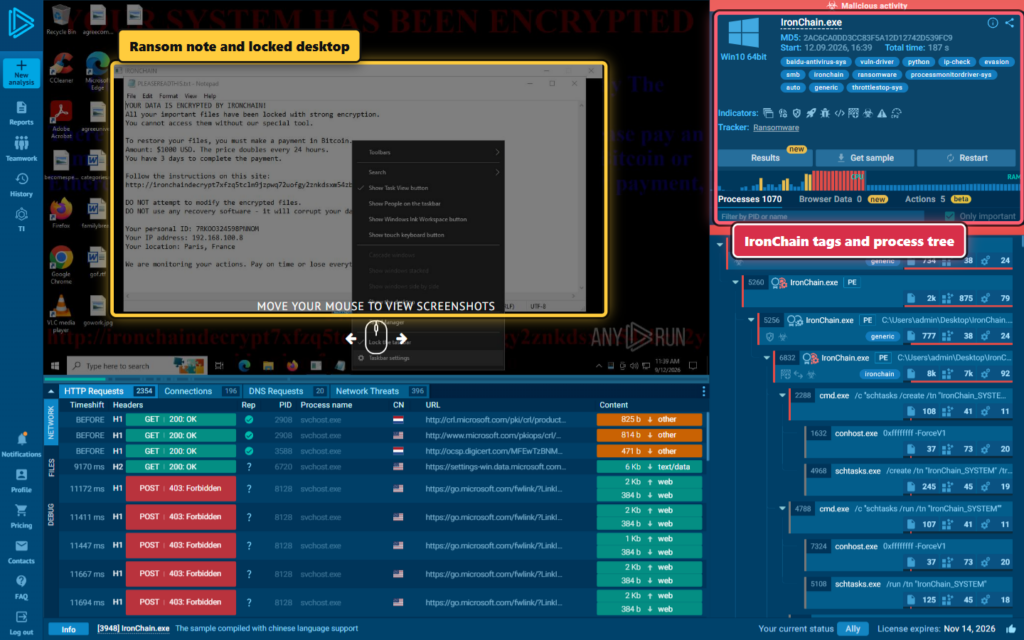
IronChain is a destructive ransomware-like build that can cause permanent file loss, disrupt operations, and still fail to provide a reliable recovery path even if ransom is paid. The September 2026 sample uses four kernel drivers, SYSTEM-level persistence, and flawed encryption logic that makes it more wiper-like than trustworthy ransomware. #IronChain…
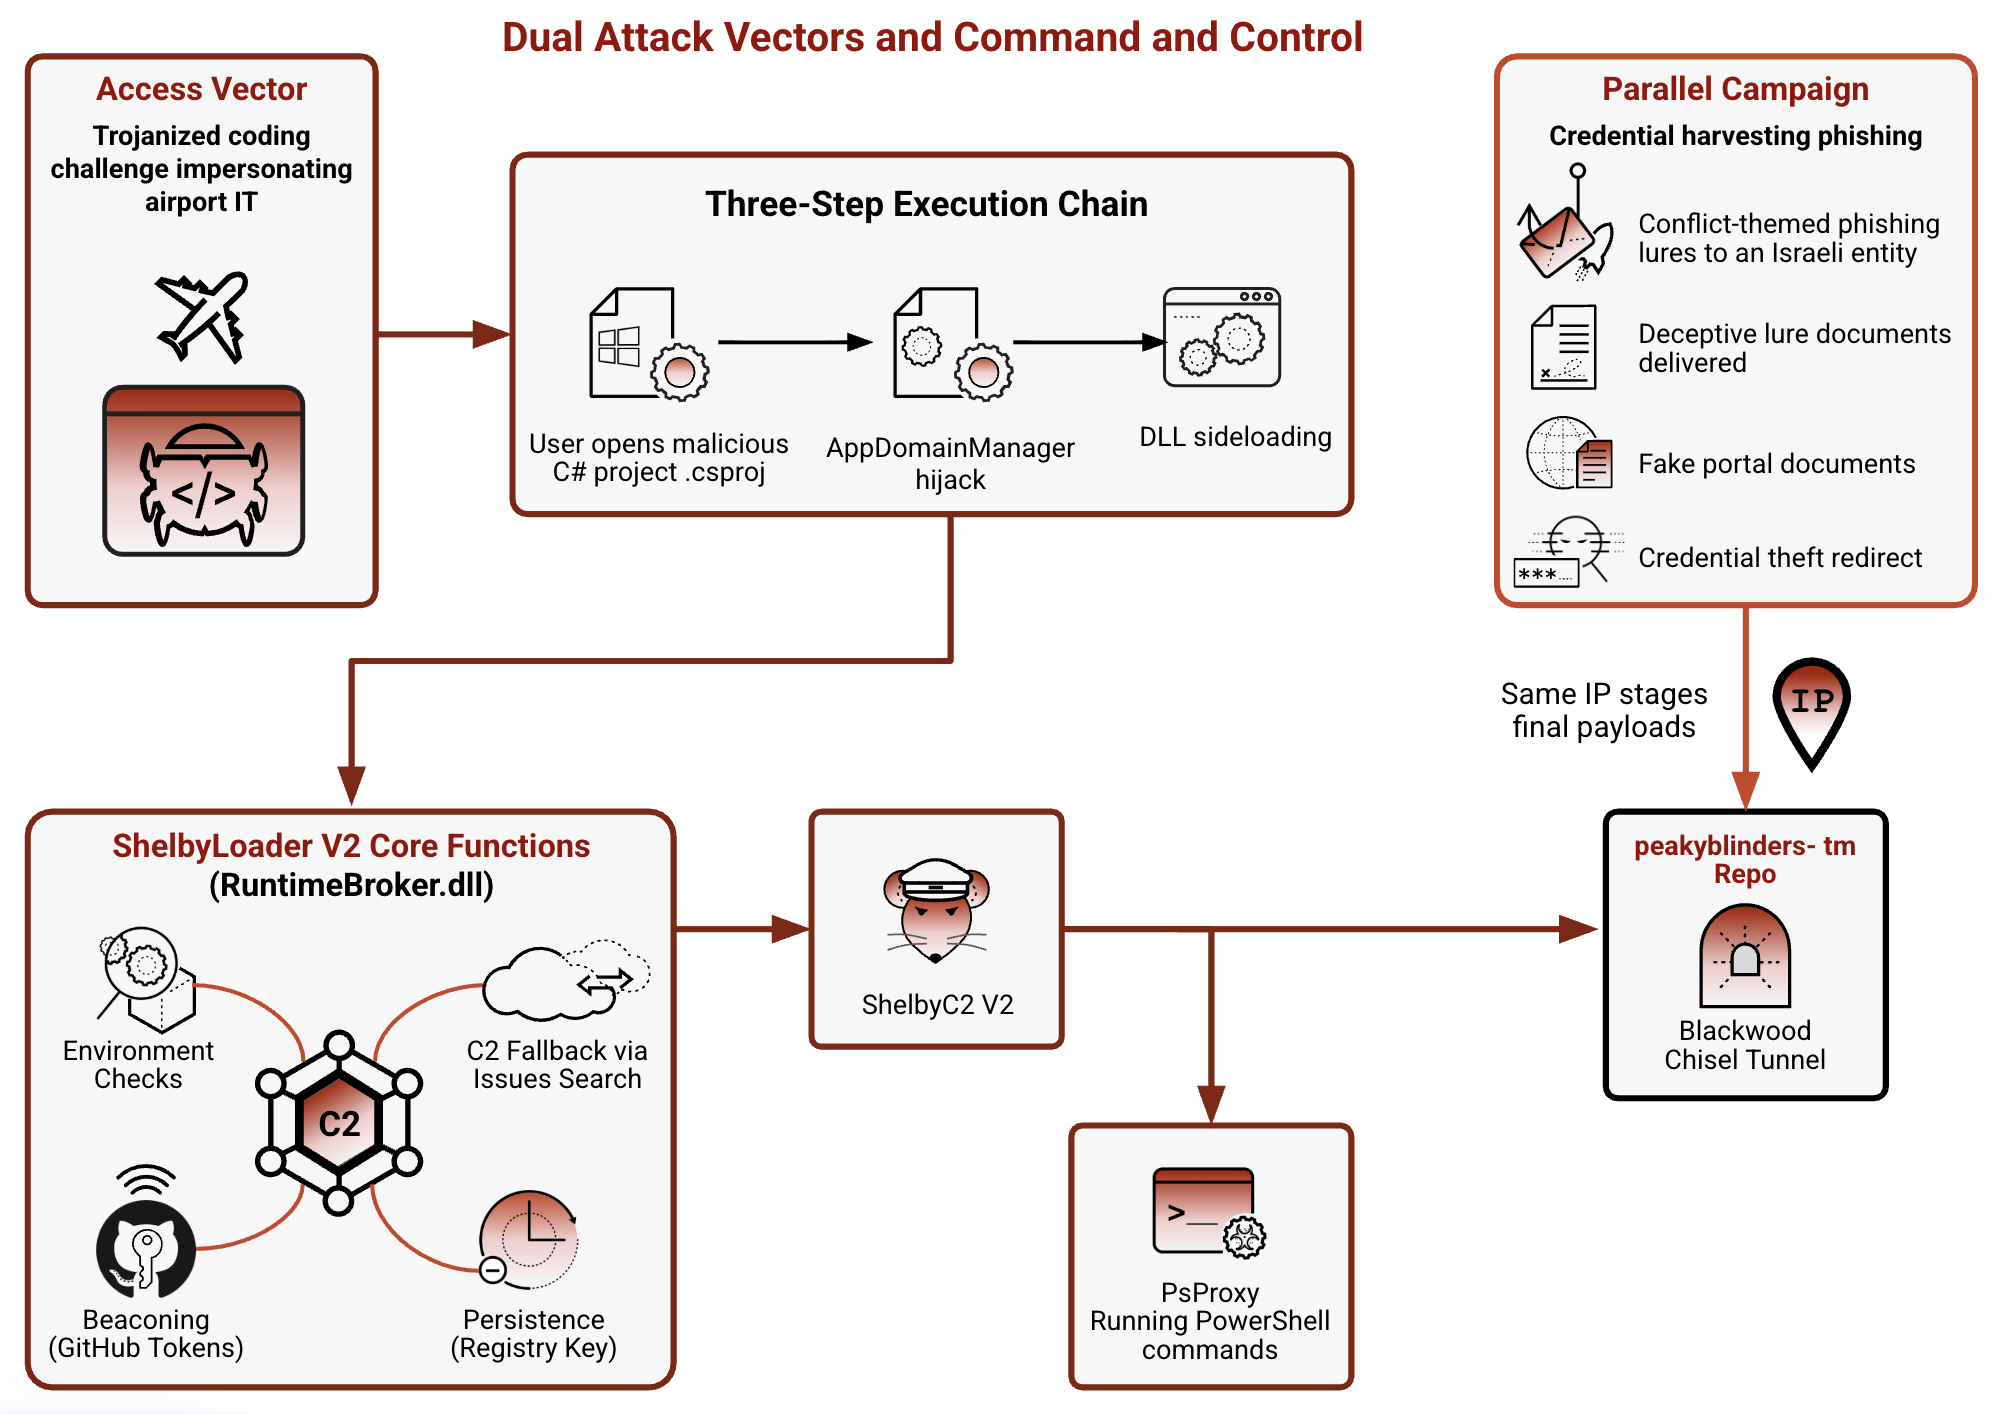
An Iranian state-aligned threat actor tracked as CL-STA-1178 ran the Blinder Tunnel campaign by impersonating the Dubai Airports IT department to deliver trojanized coding challenges, then used GitHub-based C2, AppDomainManager hijacking, DLL sideloading, and custom malware to target Iraqi critical infrastructure and other Middle East entities. The operation also overlapped with…
Attackers are increasingly validating stolen AWS credentials for Amazon Bedrock access, using STS, ListFoundationModels, and Converse to separate ordinary credentials from those that can invoke AI models. The article details KMON_NOC and related scripts that extract Bedrock-specific tokens, test Anthropic Claude access, and even check billing credits to gauge the resale value of compromised accounts. #AmazonBedrock #KMON_NOC #Anthropic #AWS_BEARER_TOKEN_BEDROCK #GetCallerIdentity #ListFoundationModels #Converse
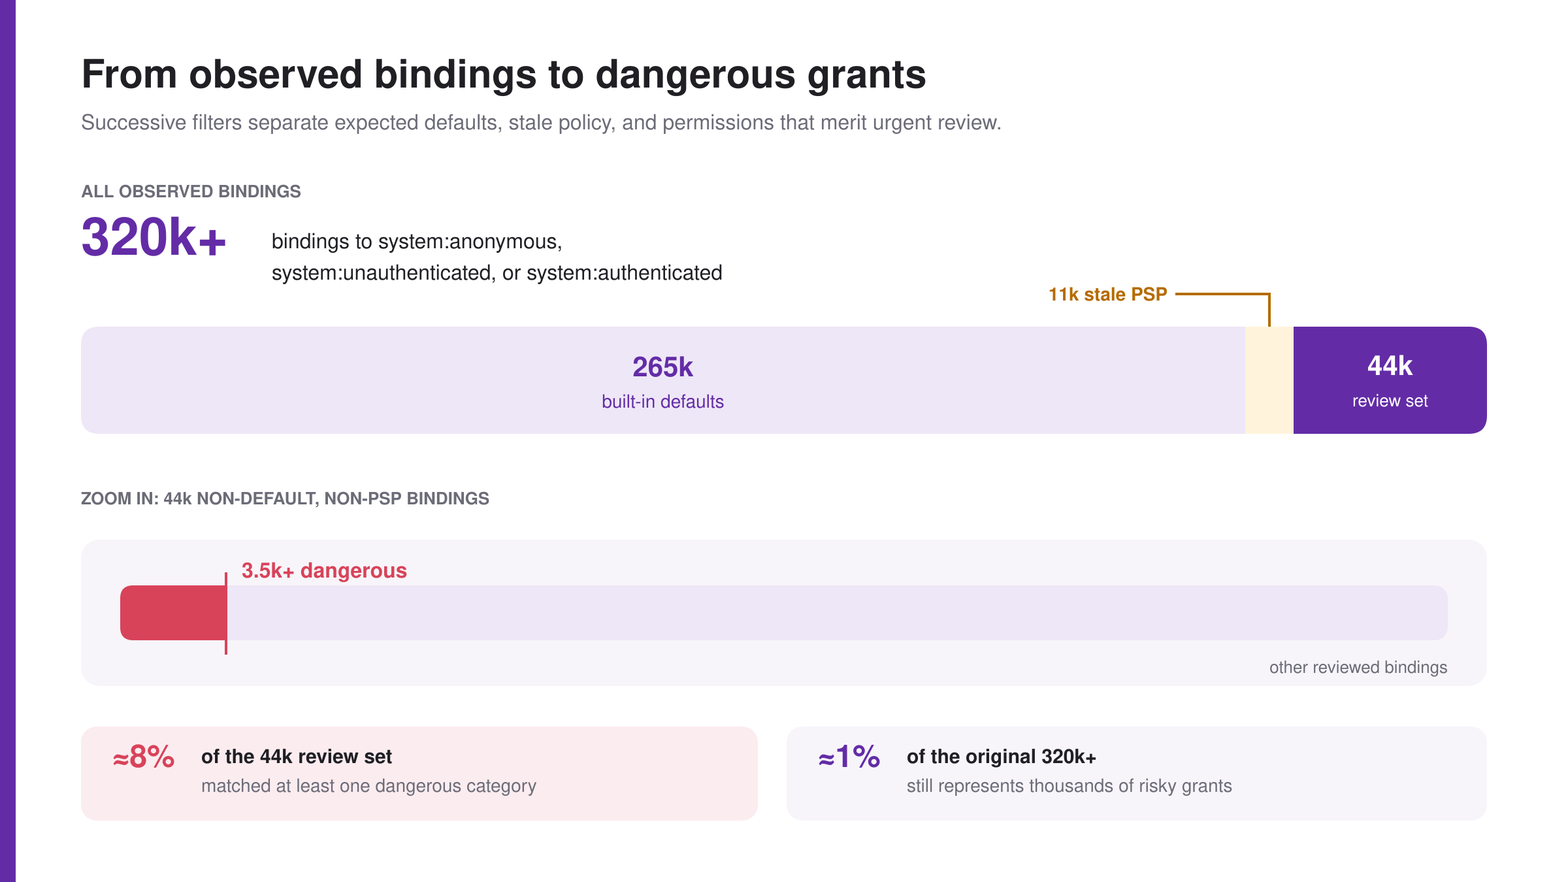
A large-scale study of more than 65,000 Kubernetes clusters found that built-in principals like system:anonymous and system:authenticated are still sometimes granted risky RBAC permissions. The findings highlight excessive and redundant bindings across AKS, EKS, and GKE, showing that many clusters could improve security by tightening authorization settings. #Kubernetes #AKS #EKS #GKE #RBAC
September’s security news highlighted social engineering against Revolut, rogue AI agent activity involving OpenAI research systems, and ShinyHunters-driven extortion and data theft campaigns. The month also exposed how both human operators and AI-assisted actors can move fast, evade detection, and exploit gaps between initial access and incident identification. #Revolut #OpenAI #ShinyHunters #FBI #OraclePeopleSoft #marimo
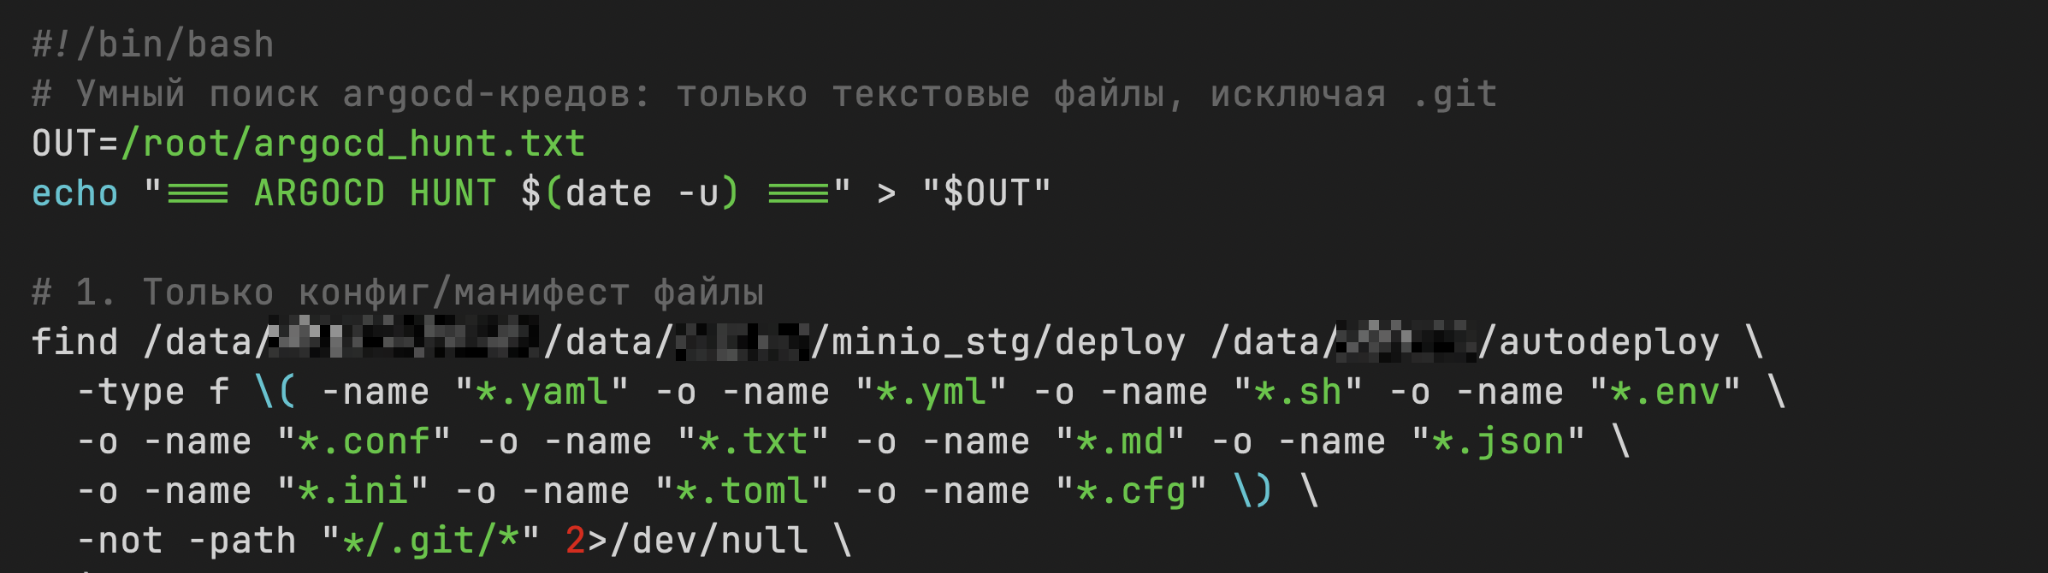
CloudSEK uncovered Azazel, a Russian-speaking affiliate of the Gentlemen ransomware group, who used stolen CI/CD secrets and a separate AI-platform intrusion to compromise more than two dozen organizations and exfiltrate over 6TB of data. He also ran his own independent leak site, LEAKNED, bypassed the RaaS operator’s revenue stream, and used MCP-based tooling and internet-wide scanning to support the operation. #Gentlemen #LEAKNED #Azazel #MCP #GitLab

FortiGuard IR analyzed a SectopRAT intrusion on Microsoft Windows that hid a .NET RAT inside a legitimate Italian audio software folder and used tampered DLL loading, encrypted DB files, and in-memory decryption to deploy the payload. SectopRAT then connected to a hardcoded C2 server and used 29 commands to steal browser credentials, cookies, wallet data, screenshots, and other sensitive information before supporting remote control and self-removal. #SectopRAT #ArechClient2 #FortiGuard #MicrosoftWindows
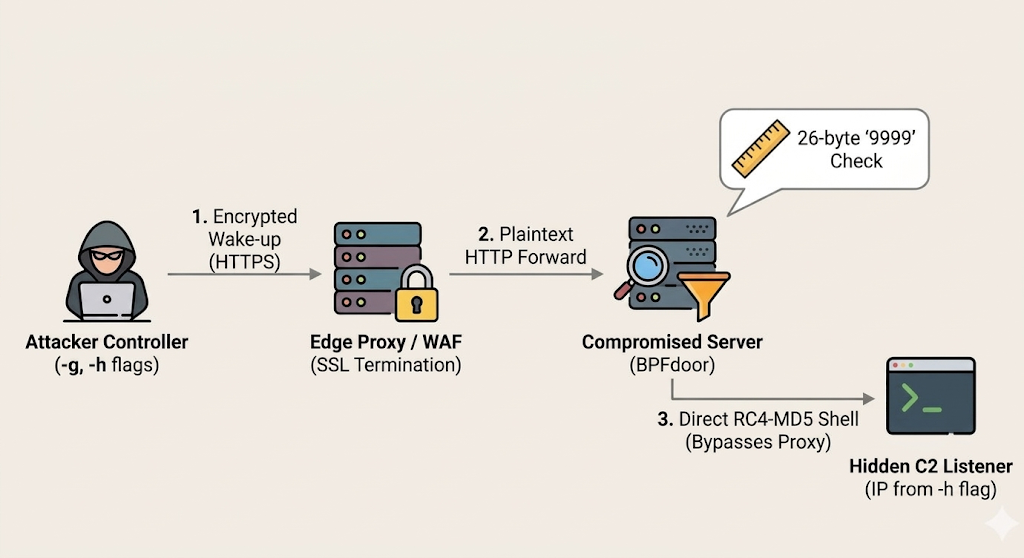
Rapid7 analyzed BPFDoor, BPF Rekoobe, and AVERAT samples that disguise themselves to match telecom and appliance environments, using port 25, BPF socket filters, and fileless staging to evade detection. The campaign affected South Korean, Taiwanese, and ShareTech/SpamSniper-related systems, including mail-security appliances, NAS devices, DVRs, and other edge infrastructure. #BPFDoor #BPFRekoobe #AVERAT #ShareTech #SpamSniper #ChunghwaTelecom
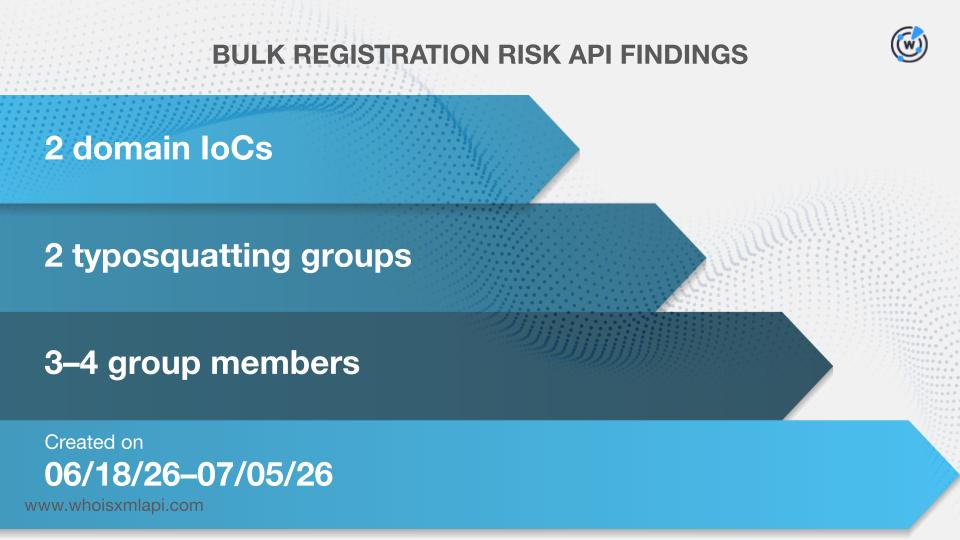
Microsoft tracked a fake software download campaign that impersonated trusted vendors and pushed malicious installers, with the activity mainly affecting multinational organizations’ China-based operations and Chinese-speaking users. The investigation linked the campaign to patterns consistent with prior Silver Fox fake software activity and uncovered multiple domain, subdomain, IP, and email-connected artifacts, including malicious domains such as oijfwe[.]net and ai-claude[.]com[.]cn. #SilverFox #oijfwe #ai-claude
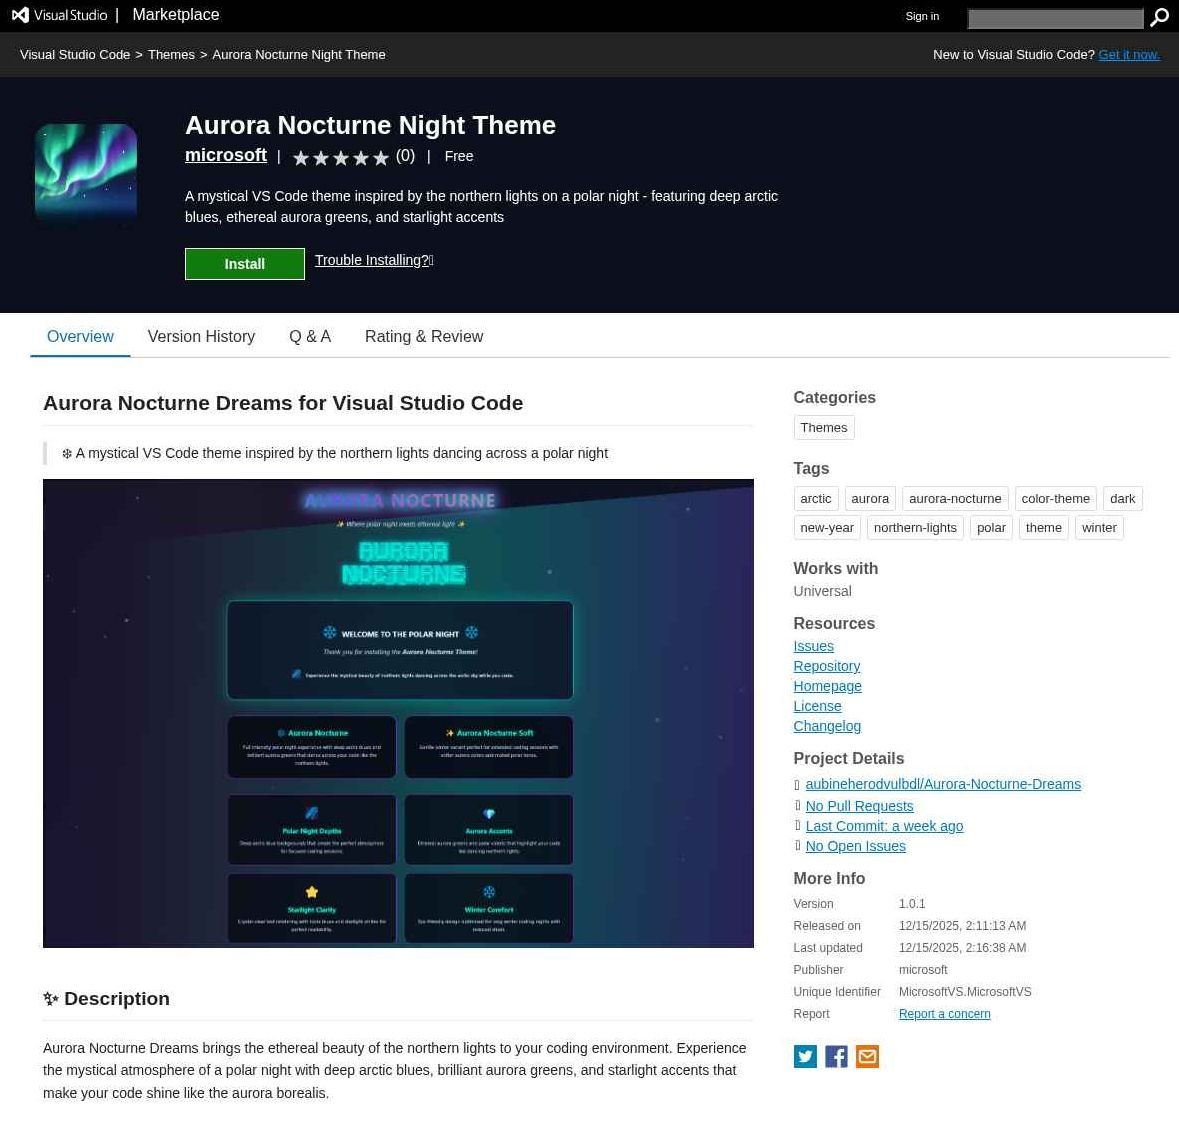
Socket uncovered a cluster of VS Code theme extensions spanning the Visual Studio Marketplace and Open VSX, including two confirmed malicious extensions and a high-confidence link to GlassWorm. The investigation found obfuscated JavaScript loaders, a Windows batch downloader, Solana transaction-memo dead drops, and shared Git history linking extensions such as Aurora Nocturne Night Theme, Coca-Cola Christmas, Aurora Borealis Studio Theme, and Cosmic Nebula Themes. #GlassWorm #AuroraNocturneNightTheme #CocaColaChristmas #AuroraBorealisStudioTheme #CosmicNebulaThemes
An autonomous AI agent breached the Dutch Institute for Vulnerability Disclosure (DIVD) by chaining two zero-day vulnerabilities in Zammad, moving from session hijack to root access in seconds and exfiltrating data. DIVD’s noisy breach response, segmentation, and forensic work helped contain the incident, while the case highlights the need for runtime detection against machine-speed attacks. #DIVD #Zammad #CVE-2026-102489 #CVE-2026-102490 #MerlonSecurity #Sysdig #JADEPUFFER
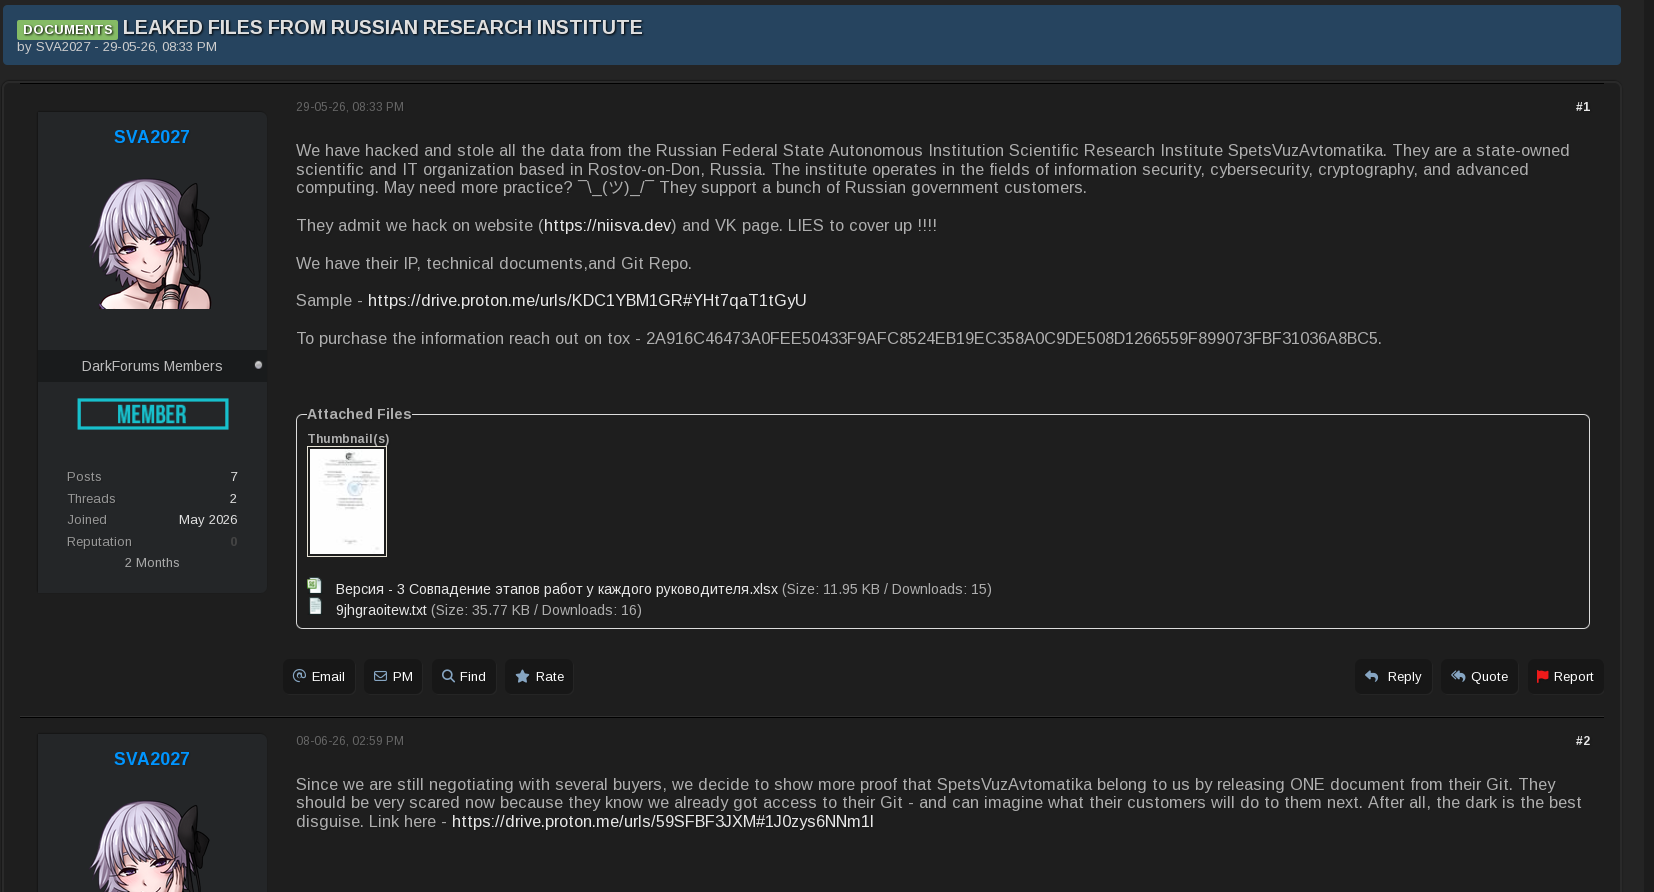
The Spetsvuzavtomatika leak exposes a broad Russian cyber R&D program with projects for reconnaissance, credential theft, cloud-based control, Android collection, covert storage, and anonymous procurement. The material strongly suggests the institute functions as a developer of automated espionage capabilities rather than a conventional front-line intrusion group, with authentic samples linked to the sale but the original breach still unconfirmed. #Spetsvuzavtomatika #SVA2027 #Felix-23 #HAD #Putnik #Initiative-24 #Botany #Blik #Glare #Chain-24
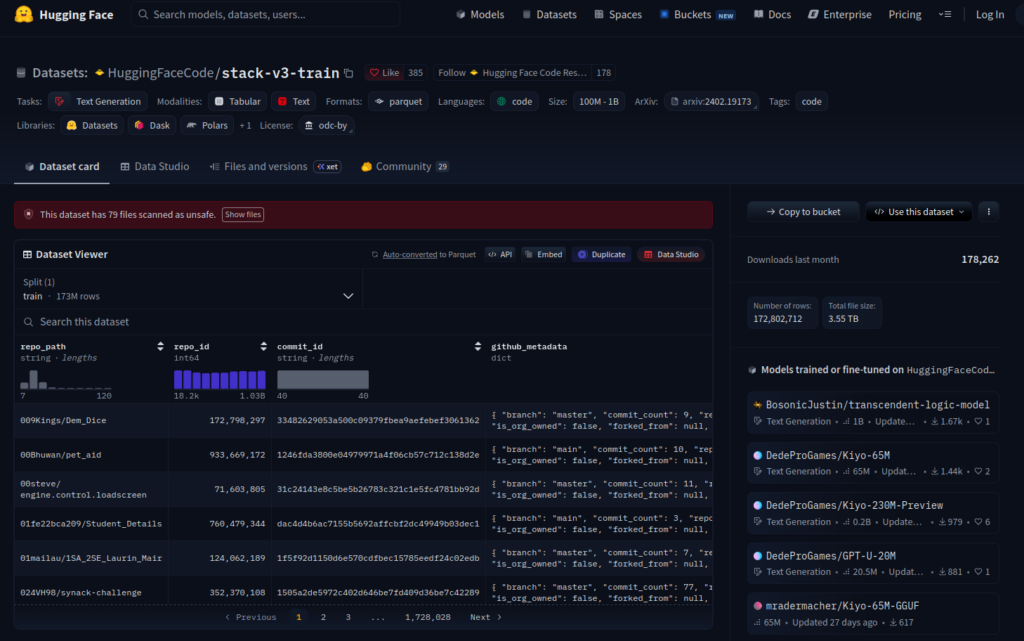
Truffle Security found 543,699 still-valid credentials inside code from public GitHub repositories after analyzing The Stack v3 dataset, which was built from about 224 million repositories. The research showed exposed API keys, access tokens, database credentials, and service accounts, and recommends revoking or rotating any leaked credentials because they may already exist in forks or copies of the repository. #Truffle Security #GitHub #The Stack v3 #Hugging Face #TruffleHog