Truesec observed a malicious installer distributed from conmateapp[.]com that drops UpdateRetriever.exe and conmate_update.ps1, creates artifacts (updating_files.zip, native.zip), schedules a recurring task, and connects to multiple hardcoded C2 domains. The campaign reuses a signing certificate issued to AMARYLLIS SIGNAL LTD and closely mirrors the earlier PDFEditor activity; Truesec published updated IOCs and hashes and recommends isolating/removing the software and blacklisting the listed domains. #ConvertMate #UpdateRetriever_exe #AMARYLLIS_SIGNAL_LTD #PDFEditor
Tag: THREAT HUNTING

Cybersecurity Threat Research ‘Weekly’ Recap highlights a broad spectrum of activity, from APT and state-backed espionage campaigns to email, banking malware, ransomware, phishing, and supply-chain abuse, along with updates on detection and defensive tooling. Key actors and families mentioned include APT35, APT24, ToddyCat, MuddyWater, UNC1549, Curly COMrades, Kimsuky, NotDoor, WaterSaci, Astaroth, Eternidade, Sarcoma, Lynx, Akira, The Gentlemen, Tycoon2FA, Tsundere, PlushDaemon, NKNShell, TamperedChef, and related C2 and advancement trends.
#APT35 #APT24 #ToddyCat #MuddyWater #UNC1549 #CurlyCOMrades #Kimsuky #NotDoor #WaterSaci #Astaroth #Eternidade #Sarcoma #Lynx #Akira #TheGentlemen #Tycoon2FA #Tsundere #PlushDaemon #NKNShell #TamperedChef

Google Threat Intelligence Group (GTIG) details a three-year espionage campaign by PRC‑nexus actor APT24 that deploys a highly obfuscated first‑stage downloader called BADAUDIO to establish persistent access via strategic web compromises, supply‑chain abuse of a Taiwanese digital marketing firm, and targeted phishing. The report analyzes BADAUDIO’s control‑flow flattening, DLL sideloading, AES‑encrypted payload delivery (including Cobalt Strike Beacon instances), advanced browser fingerprinting for tailored targeting, and shares IOCs and YARA rules to aid detection and mitigation. #APT24 #BADAUDIO

Predictive threat intelligence uses AI and behavioral analytics to anticipate attacks before they occur, shifting from reactive to proactive defense. It contrasts with traditional threat intelligence by focusing on Indicators of Attack (IOAs) rather than Indicators of Compromise (IOCs), enabling earlier detection and action.
#IOAs #MITRE ATTACK #SentinelOne #Mandiant #ATT&CK…
Google Threat Intelligence Group (GTIG) reports that PRC‑nexus threat actor APT24 has run a three‑year espionage campaign delivering a heavily obfuscated first‑stage downloader named BADAUDIO—often using strategic web compromises, supply‑chain compromise of a Taiwanese marketing firm, and targeted phishing to deploy AES‑encrypted payloads such as Cobalt Strike Beacon. The report details BADAUDIO’s control‑flow flattening, DLL sideloading execution chain, fingerprinting‑based targeting, extensive infrastructure churn, and provides IOCs and YARA rules for detection. #BADAUDIO #APT24 #CobaltStrikeBeacon #twisinbeth.com
Automated threat intelligence enables machine-speed detection, enrichment, and response to indicators of compromise, reducing mean time to detect and respond while freeing analysts from repetitive tasks. Recorded Future’s Intelligence Cloud delivers this capability through continuous data collection, ML-driven risk scoring, and integrations with SIEM, SOAR, and EDR to enable real-time defensive actions. #RecordedFuture #InsiktGroup
Acronis TRU tracked a global malvertising and SEO-driven campaign named “TamperedChef” that distributes digitally signed fake installers which persist via scheduled tasks and execute heavily obfuscated JavaScript backdoors with remote code execution and HTTPS-based C2. The operators use U.S.-registered shell companies to acquire and rotate code-signing certificates, short-lived domain registrations, and malvertising/SEO to hide infrastructure and quickly recover after takedowns. #TamperedChef #Obfuscator_io
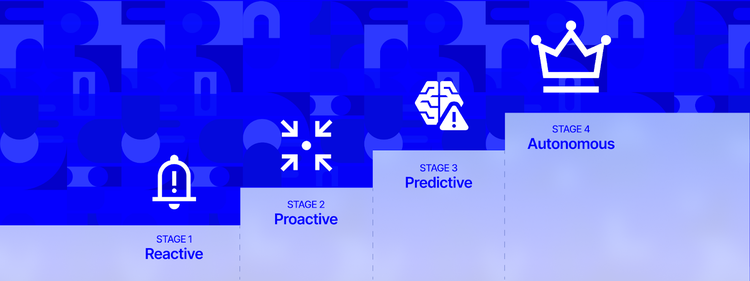
Organizations face information overload from multiple security feeds, which limits their ability to act on threat data; Recorded Future defines a four-stage Threat Intelligence Maturity Model—Reactive, Proactive, Predictive, and Autonomous—to guide operationalizing intelligence into measurable outcomes. #RecordedFuture #ThreatIntelligenceMaturityModel
Microsoft announced a range of security improvements across its products, primarily focusing on Defender, Sentinel, and AI-driven security tools at Ignite 2025. These enhancements aim to enhance attack detection, threat mitigation, and unified security management for cloud, AI, and serverless environments. #MicrosoftDefender #Sentinel #CyberThreatProtection…
Microsoft will integrate Sysmon directly into Windows 11 and Windows Server 2025, eliminating the need for standalone installation. This integration simplifies deployment and enhances security monitoring capabilities, supporting advanced event filtering and threat detection. #Sysmon #WindowsIntegrations

This article emphasizes going beyond superficial metrics to accurately assess detection quality in cybersecurity. It introduces the DRAPE index as a practical tool for evaluating detection reliability and precision efficiency, supported by real-world data analysis. #MITREATT&CK #DetectionMetrics
Cybersecurity Threat Research ‘Weekly’ Recap. This week highlights state-sponsored and APT activity, including APT35’s malware pipeline and SideWinder emulation guidance, plus DragonBreath’s RONINGLOADERloader and KONNI Android operations. It also covers diverse malware families like Lumma Stealer, LeakyInjector/LeakyStealer, Remcos, Amatera, XWorm, Rhadamanthys, and VenomRAT takedowns; ransomware trends with Qilin, Akira, Cl0p, Kraken, and Yurei analyses; phishing and credential theft campaigns; supply-chain and RMM abuse including Anthropic MCP SDK flaws and Triofox CVE; detection and threat-hunting advances; and emergent AI-driven malware, pig-butchering scams, Kubernetes trends, and macOS privilege escalation. #APT35 #SideWinder #Gh0stRAT #RONINGLOADER #KONNI #Lum maStealer #LeakyInjector #LeakyStealer #Remcos #Amatera #NetSupportRAT #XWorm #Rhadamanthys #VenomRAT #Qilin #Akira #Cl0p #Kraken #Yurei #Kimsuky #AI‑drivenmalware #PigButchering #Triofox #CVE-2025-12480 #CVE-2025-24277
Elastic Security Labs uncovered a Chinese-language targeted campaign by Dragon Breath APT (APT-Q-27) distributing a modified gh0st RAT via trojanized NSIS installers and a unique loader dubbed RONINGLOADER. The multi-stage chain uses a signed kernel driver, WDAC policy tampering, PPL abuse of ClipUp to disable Microsoft Defender, and thread-pool based remote injection to terminate and bypass popular Chinese endpoint products. #DragonBreath #RONINGLOADER
eSentire’s TRU discovered campaigns using ClickFix for initial access to deploy Amatera Stealer (a rebranded ACR/AcridRain) and NetSupport RAT, with Amatera leveraging advanced evasion (WoW64 syscalls, AMSI bypass) and extensive crypto-wallet/password manager theft capabilities. eSentire published decryption helpers and detection guidance, and recommends mitigations including disabling mshta.exe, removing the Run prompt, PSAT, and partnering with 24/7 MDR services. #Amatera #NetSupport
This article emphasizes the importance of shifting from traditional signature-based security measures to behavior-driven detection to combat modern ransomware threats effectively. It advocates for a unified, cloud-native approach like SASE that integrates detection, prevention, and operational controls to minimize damage and improve response times. #MITREATT&CK #TTPs…