
Seqrite Labs uncovered Operation DRAGONCLONE, a sophisticated Chinese cyber campaign targeting China Mobile Tietong using DLL sideloading, anti-sandbox techniques, and advanced malware like VELETRIX and VShell. The operation demonstrates extensive reuse of infrastructure and tools, highlighting persistent threats from China-aligned groups. #VELETRIX #EarthLamia…
Tag: THREAT HUNTING
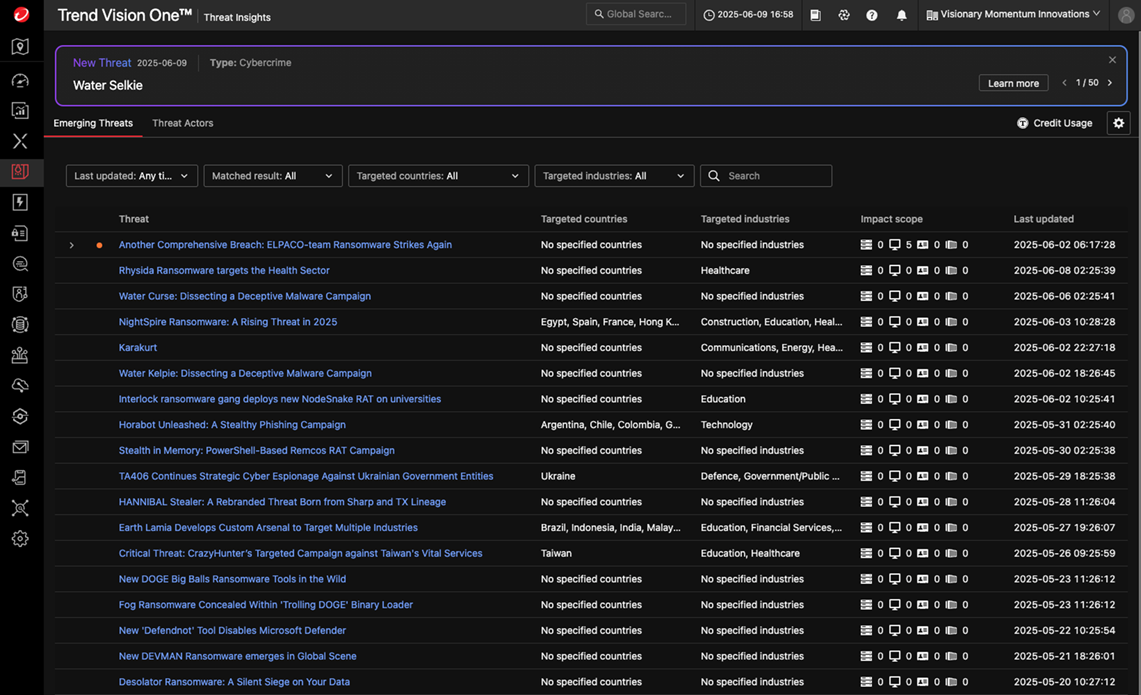
Trend Vision One™ – Threat Intelligence enhances proactive security by providing retrospective scanning and container-aware visibility to detect past and ongoing threats in diverse environments. It integrates real-time data, MITRE ATT&CK mapping, and automated investigations to enable faster, intelligence-driven incident response. #TrendVisionOne #ThreatInsights #ContainerSecurity…

Guardz is a cybersecurity startup focused on providing an all-in-one platform for small and medium-sized businesses, securing $56 million in Series B funding. The company’s AI-powered detection and response platform integrates multiple security functions and expands its reach in the U.S. market. #SentinelOne #MSPs…

The North Korean hacking group Kimsuky has employed a sophisticated infiltration strategy targeting South Korean users via Facebook, email, and Telegram, disguising malicious files as volunteer activities for defectors. This campaign utilizes Korean-specific compressed files and encoded scripts to evade detection, with significant compromises linked to the AppleSeed malware variant. #Kimsuky #AppleSeed
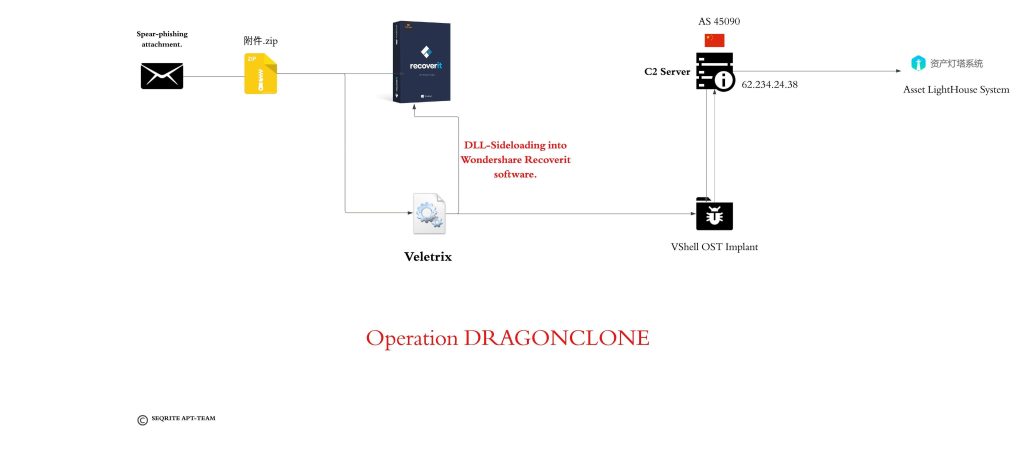
A sophisticated cyber campaign named Operation DRAGONCLONE targeted China Mobile Tietong using VELETRIX and VShell malware, employing DLL sideloading, anti-sandbox, and IPfuscation techniques. The activity is linked to China-aligned threat groups UNC5174 and Earth Lamia, with overlaps to multiple post-exploitation tools and infrastructure. #OperationDRAGONCLONE #VELETRIX #VShell #ChinaMobileTietong #UNC5174 #EarthLamia
DDoS attacks flood systems with excessive requests, causing service disruption, and monitoring Autonomous System Numbers (ASNs) helps identify malicious activity. Effective mitigation involves redirecting traffic based on ASN reputation to maintain service performance and resilience. #DDoS #AutonomousSystemNumbers

A new variant of the Atomic macOS Stealer (AMOS) campaign uses typo-squatted domains mimicking Spectrum to deliver malicious payloads targeting macOS users by harvesting system passwords. The campaign is linked to Russian-speaking cybercriminals and employs multi-platform social engineering tactics with poorly implemented logic in its delivery infrastructure. #AtomicMacOSStealer #SpectrumTyposquatting #RussianCybercriminals
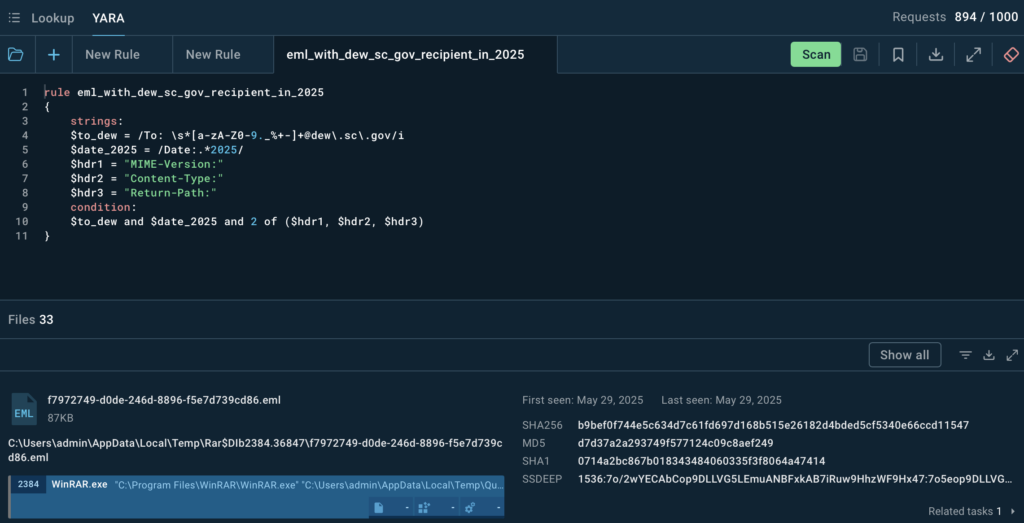
Government institutions worldwide are increasingly targeted by sophisticated cyberattacks, leveraging phishing emails, fraudulent domains, and malicious PDFs. ANY.RUN’s solutions provide critical tools for detecting, analyzing, and mitigating these threats, enhancing organizational cybersecurity resilience. #FormBook #ScreenConnect #SocialSecurityAdministration…
ThreatSpike, a London-based end-to-end cybersecurity provider, has secured $14 million in Series A funding to expand its unified platform that offers real-time detection, response, and penetration testing. The company’s all-in-one solution aims to simplify cybersecurity for mid-sized businesses by combining automation, threat hunting, and vulnerability testing. #ThreatSpike #SeriesAFunding…
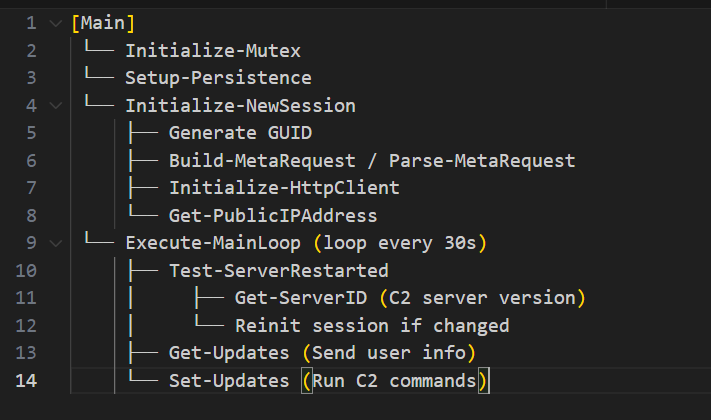
The 2025 variant of the ViperSoftX PowerShell stealer showcases enhanced modularity, stealth, and persistence compared to its 2024 predecessor, with upgraded encryption and victim identification techniques. It targets cryptocurrency wallets and browser extensions while employing dynamic infrastructure synchronization and multilayer persistence mechanisms. #ViperSoftX #PowerShellMalware #CryptocurrencyStealer
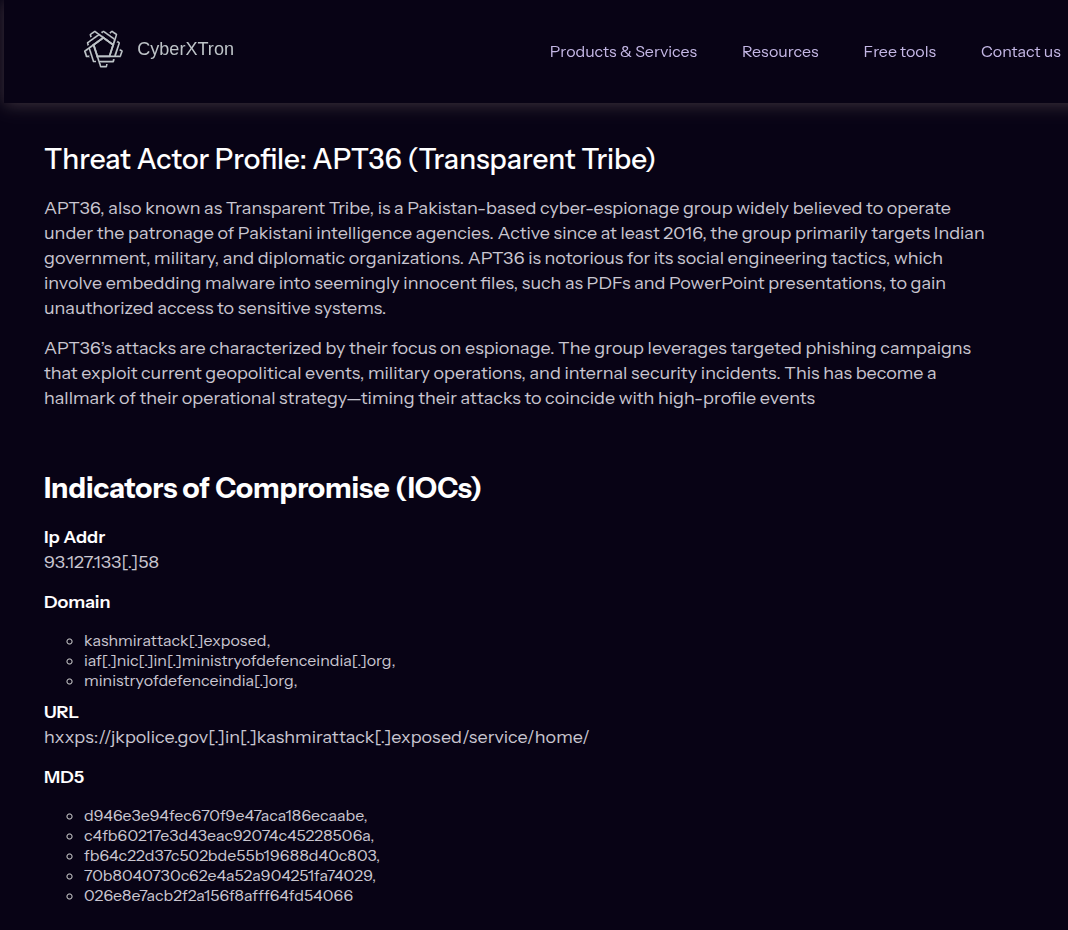
This article explains how DNS history and host response data can be leveraged to discover unreported domains potentially linked to the APT36 group, also known as Transparent Tribe. It details the investigative process using Validin to enrich and pivot on known indicators, revealing additional associated infrastructure. #APT36 #TransparentTribe #Validin

This article offers guidance for OSCP exam retakers and newly certified professionals on how to analyze their performance, learn from mistakes, and plan next steps in their cybersecurity careers. It emphasizes the importance of retrospective analysis, networking, and strategic planning for ongoing growth. #OSCP #PenetrationTesting #CybersecurityCareers

StealC V2 is an advanced infostealer and malware downloader with enhanced stealth features, a JSON-based C2 protocol, and flexible payload delivery capabilities. It targets a broad range of victims worldwide while excluding systems in CIS countries, and employs hardware ID generation and multiple evasion techniques. #StealC #Plymouth #Themida
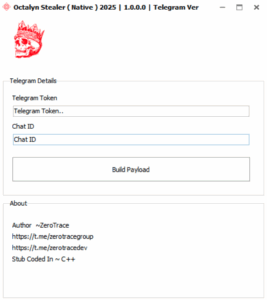
Octalyn Stealer is a Pascal/Delphi-based information-stealing malware that targets Windows systems from XP to Windows 11, using Telegram’s bot API for stealthy data exfiltration. Its user-friendly control panel and availability on GitHub lower the technical barriers for cybercriminals, enabling widespread dissemination through multiple infection vectors. #OctalynStealer #TelegramBotAPI
This article explores the evolving landscape of artificial intelligence, focusing on the distinctions between GenAI, SynthAI, and agentic AI, especially in the context of cybersecurity. It highlights the rising prominence of agentic AI at RSA Conference 2025 and discusses its potential applications and associated challenges. #RSAConference2025 #AgenticAI #SynthAI #GenAI #CybersecurityThreats…