
A widespread zero-day vulnerability in Microsoft SharePoint, ToolShell (CVE-2025-53770/53771), has led to over 396 compromised systems affecting organizations globally. The attacks are highly targeted, primarily impacting government agencies and strategic institutions, with ongoing threats expected. #SharePointZeroDay #ToolShellVulnerability…
Tag: THREAT HUNTING
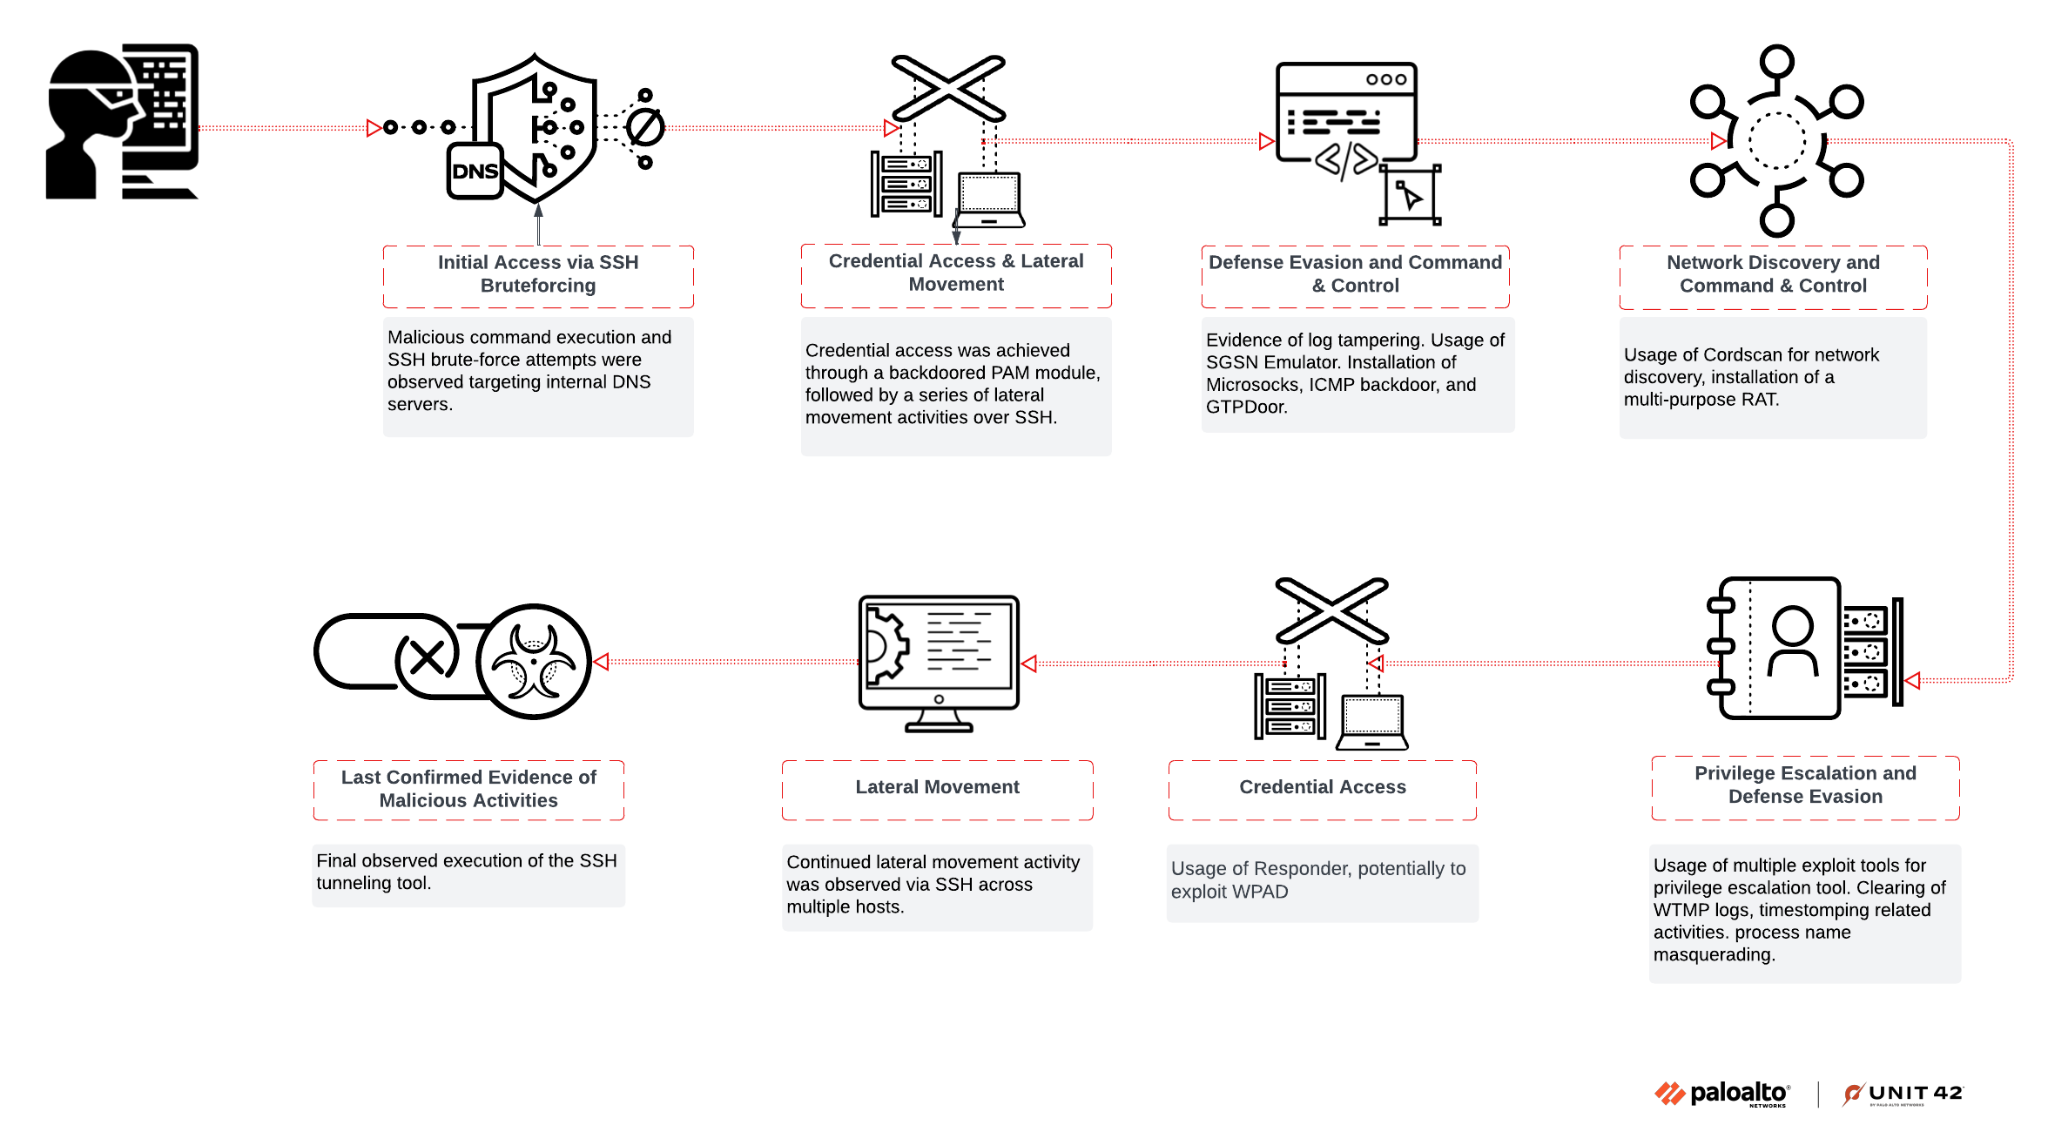
Unit 42 has identified a nation-state linked threat cluster, CL-STA-0969, targeting telecommunications infrastructure in Southwest Asia using custom tools and advanced evasion techniques. The activity involves exploitation of mobile roaming networks and implements various backdoors and implants to maintain stealthy persistence without clear evidence of data exfiltration. #CL-STA-0969 #LiminalPanda #Cordscan…

The Scattered Spider hacking group is targeting data storage tools and using sophisticated social engineering tactics to access sensitive information of large organizations across various industries. Law enforcement efforts have not slowed their ongoing campaigns, which include data theft, malware deployment, and operational disruptions. #ScatteredSpider #Snowflake #DragonForceRansomware #Vishing #CybercriminalForums…

Scattered Spider, a cybercriminal group, is increasingly targeting VMware vSphere environments to take control of hypervisors and deploy ransomware. These attacks emphasize the need for organizations to adopt infrastructure-centric defense strategies to prevent sophisticated intrusions. #ScatteredSpider #vSphere #hypervisorattack…

The cybercrime group known as Scattered Spider is targeting VMware ESXi hypervisors primarily through social engineering tactics rather than exploiting software vulnerabilities. Their campaign focuses on gaining deep access to critical systems, allowing for data theft and ransomware deployment, especially in North American sectors like retail and transportation. #ScatteredSpider #VMwareESXi #UNC3944…

Recent cybersecurity reports highlight active exploitation of SharePoint zero-days by Chinese threat actors and ongoing malware campaigns involving stealers and ransomware like Interlock and Gunra. These developments underscore the importance of prompt patching and advanced threat detection strategies. #ToolShell #CVE-2025-53770 #CVE-2025-53771 #LinenTyphoon #WaterKurita
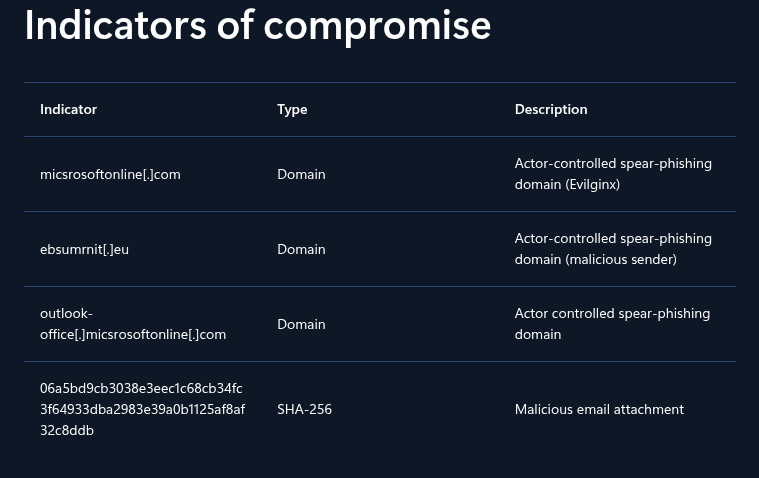
Laundry Bear, also known as Void Blizzard, is a Russian state-sponsored APT active since April 2024 targeting NATO countries and Ukraine using spear phishing and credential theft. Using Validin’s advanced pivoting techniques, multiple additional malicious domains and infrastructure linked to Laundry Bear have been uncovered, expanding beyond initial Microsoft-reported indicators. #LaundryBear #VoidBlizzard #Validin
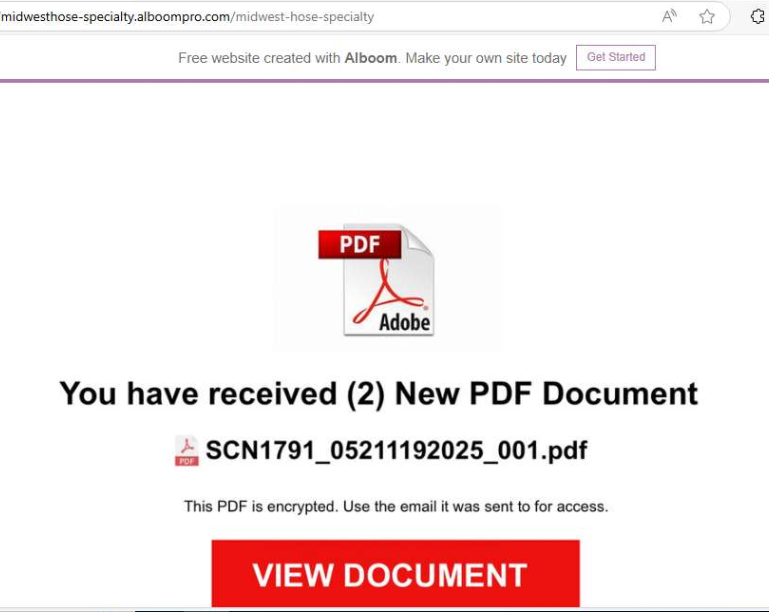
Cybersecurity experts have detected a rise in sophisticated phishing campaigns that mimic Microsoft SharePoint through structurally similar domains and exploited hosting services. These campaigns employ advanced tactics like CAPTCHA challenges and credential theft to deceive users and bypass security measures. #SharePointPhishing #HostingAbuse…

Microsoft Sentinel data lake introduces a modern, cost-effective data management architecture that unifies security data at scale, enabling faster detection and response with AI-powered capabilities. This solution addresses the challenges of managing massive datasets by breaking down data silos and integrating extensive threat intelligence across environments. #MicrosoftSentinel #SentinelDataLake #DefenderXDR
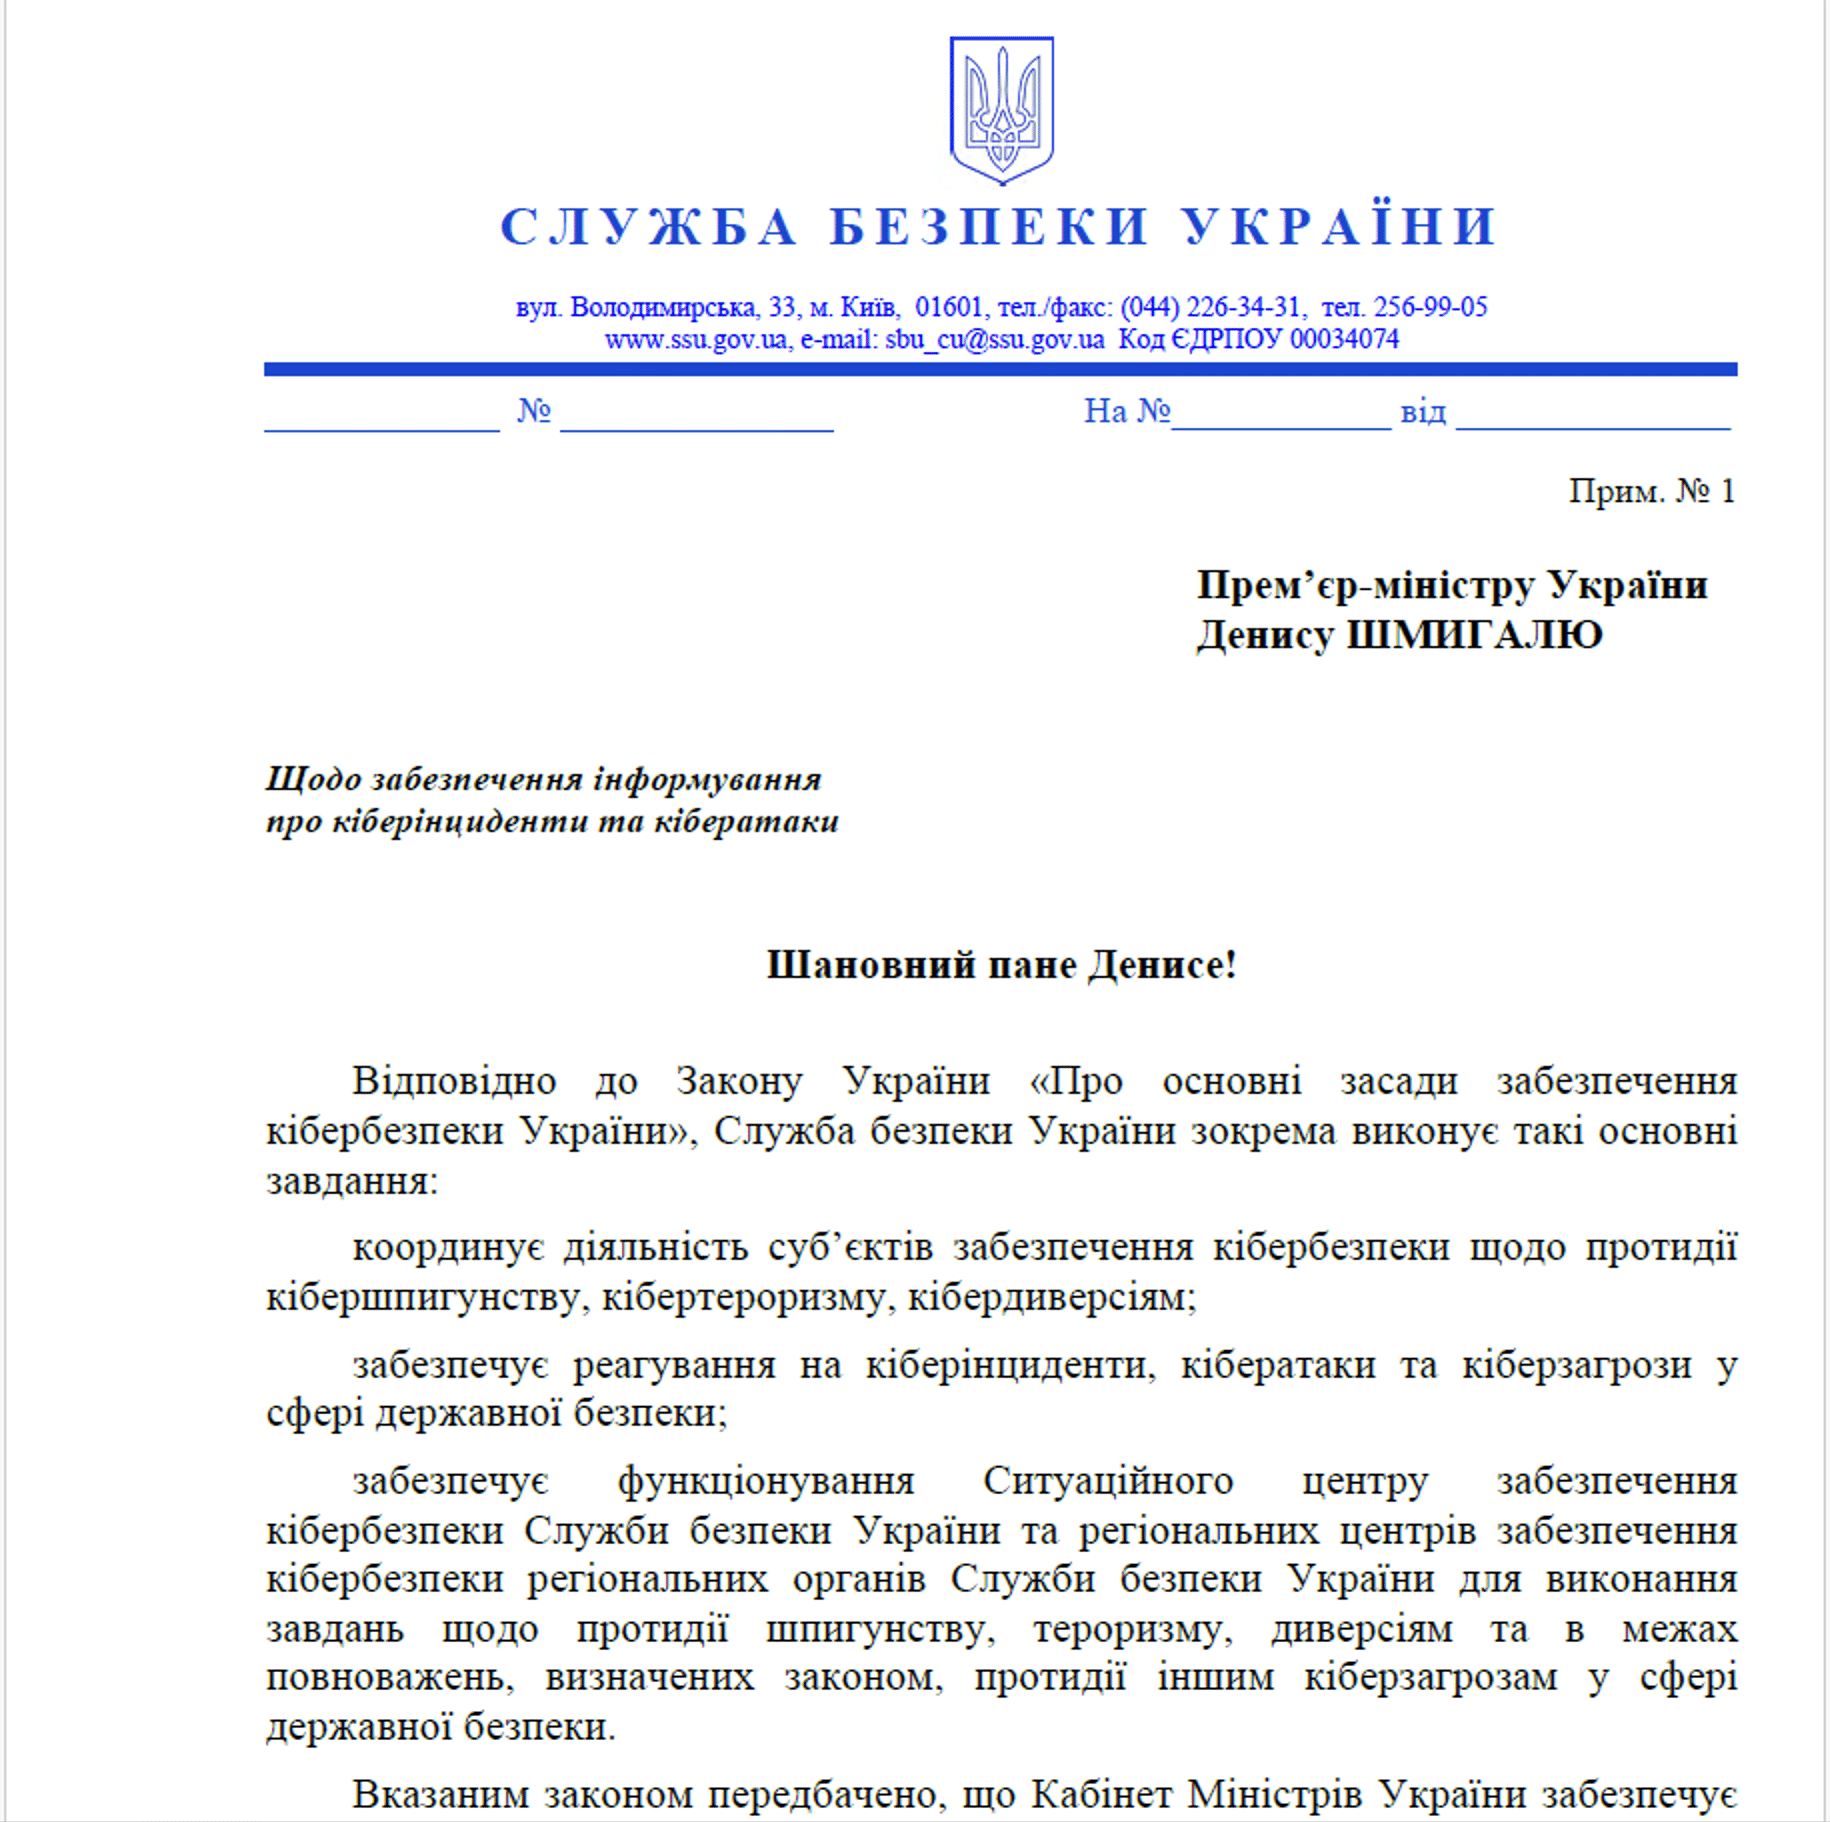
LAMEHUG is the first known malware that integrates large language model (LLM) capabilities directly into its attack methodology, attributed with moderate confidence to APT28 targeting Ukrainian government officials. The malware uses the Qwen2.5-Coder-32B-Instruct LLM via Hugging Face API to dynamically generate and execute commands in real-time, demonstrating a proof-of-concept for AI-powered state-sponsored cyber operations. #LAMEHUG #APT28 #Qwen2.5-Coder

Microsoft reported ongoing exploits targeting on-premises SharePoint servers using vulnerabilities CVE-2025-49706 and CVE-2025-49704 by Chinese threat actors including Linen Typhoon, Violet Typhoon, and Storm-2603. Immediate application of Microsoft’s security updates and recommended mitigations such as enabling AMSI and rotating machine keys are critical to protect affected systems. #CVE-2025-49706 #LinenTyphoon #VioletTyphoon #Storm-2603 #spinstall0.aspx
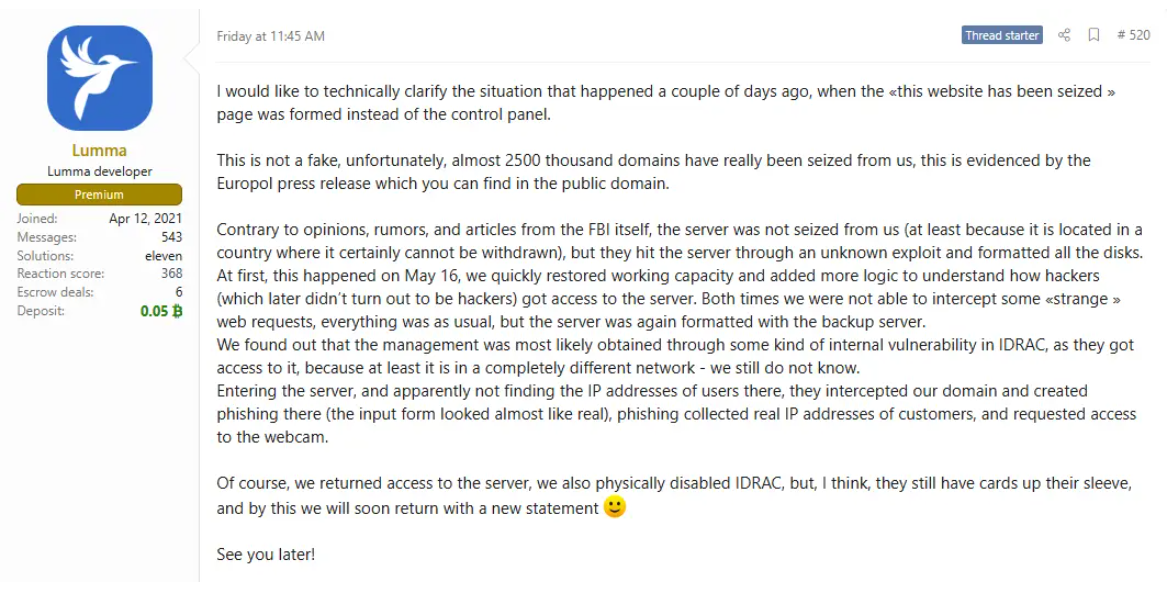
Lumma Stealer malware has resurfaced soon after a major law enforcement takedown, utilizing stealthier tactics and diversified delivery methods to regain its reach. The threat actors behind it, including the group known as Water Kurita, continue to innovate their infrastructure and campaigns, posing ongoing risks to users and organizations. #LummaStealer #WaterKurita…
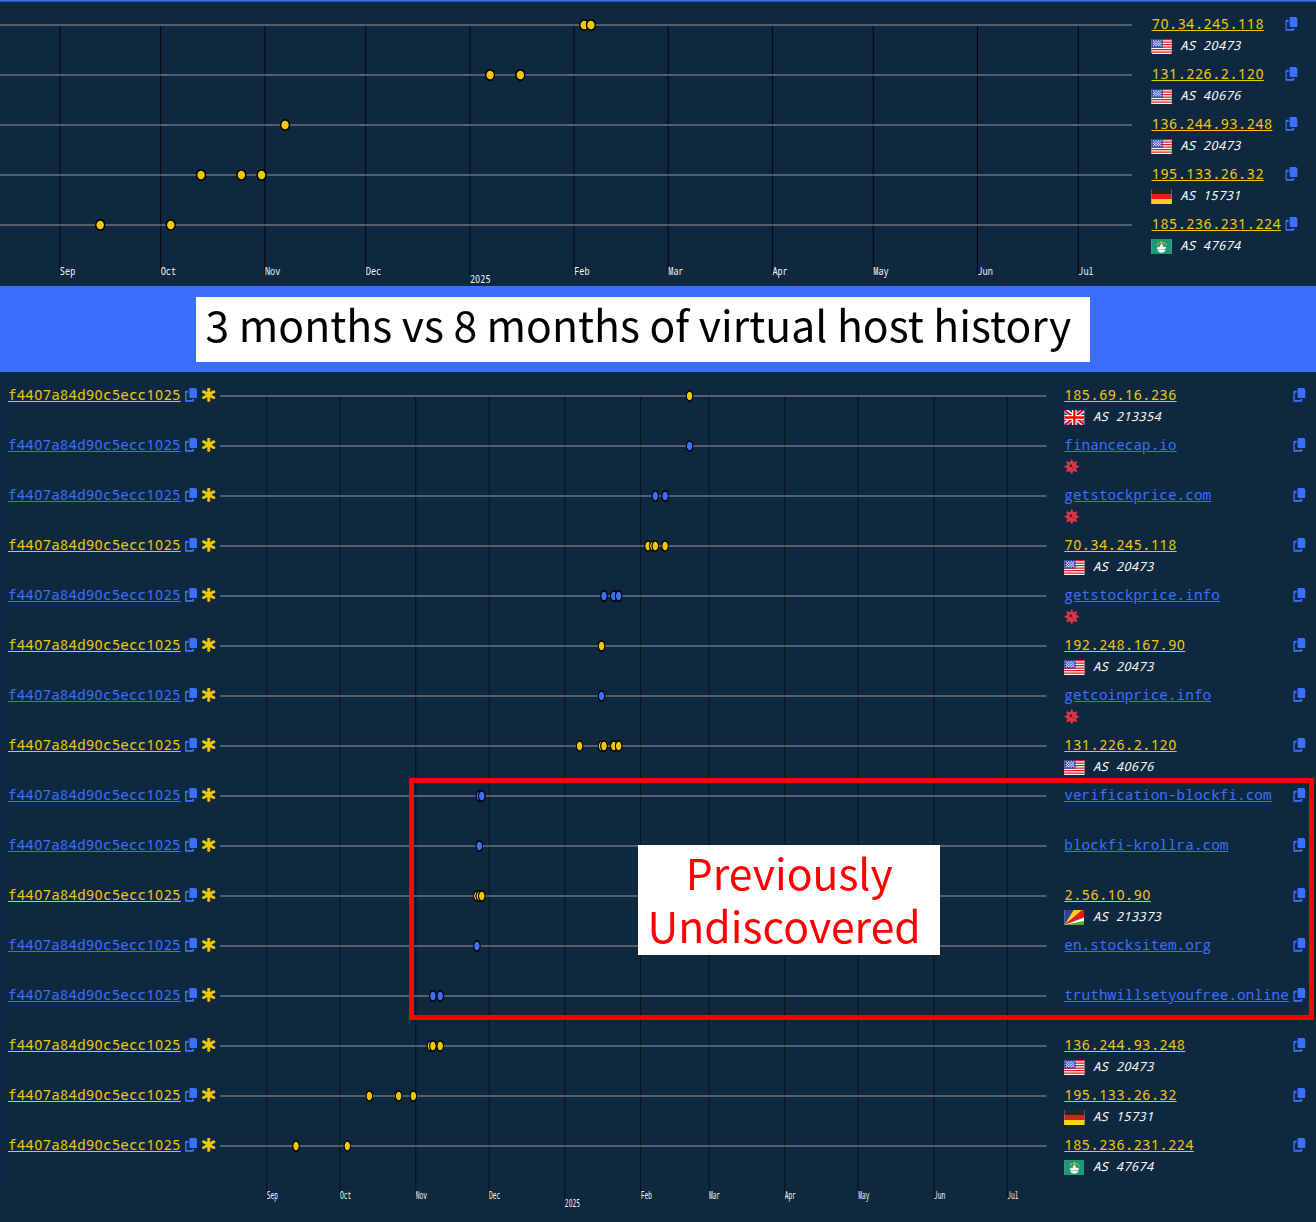
Validin has launched significant enhancements to its threat intelligence platform, including over 8 months of historical HTTPS banner data and on-demand access to full HTTP response artifacts. These upgrades enable deeper threat hunting, malware infrastructure analysis, and incident response capabilities, as demonstrated by uncovering additional Lazarus Group infrastructure linked to the Bybit heist. #Validin #TraderTraitor #LazarusGroup
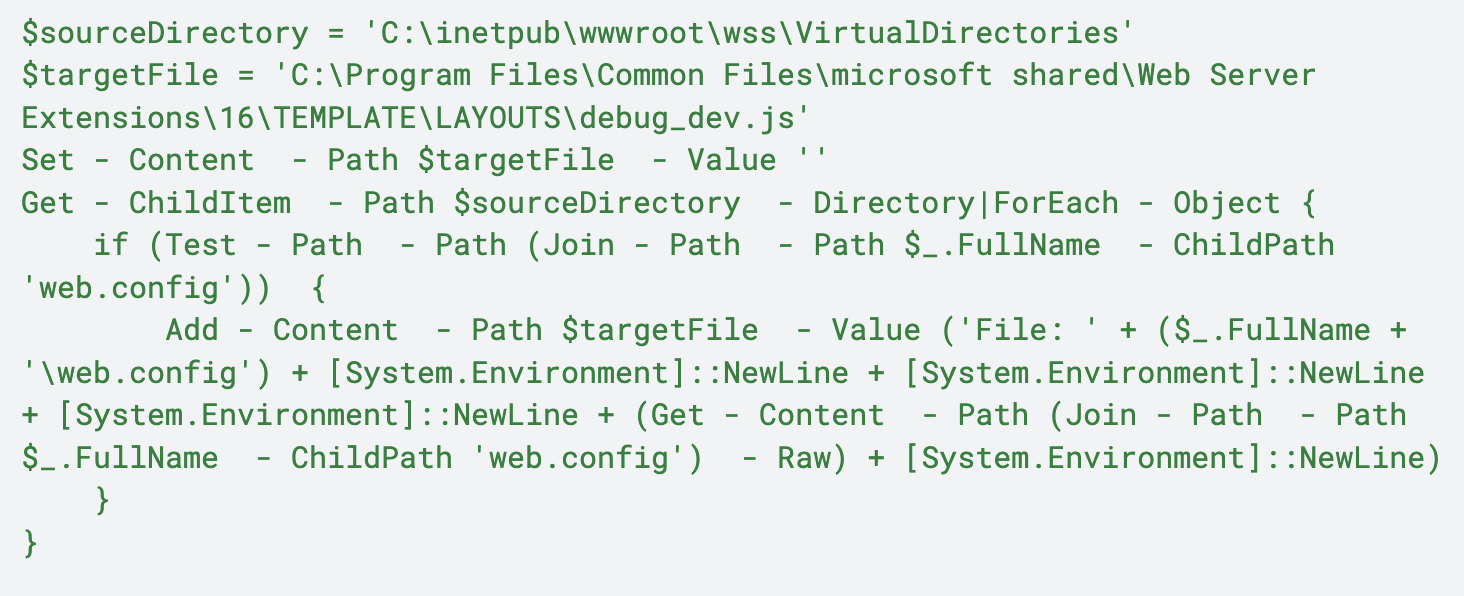
Multiple critical vulnerabilities affecting on-premises Microsoft SharePoint servers have been actively exploited to bypass authentication and gain unauthorized access, leading to data exfiltration and persistent backdoors. Immediate patching, cryptographic material rotation, and professional incident response are strongly advised to mitigate these ongoing threats. #CVE-2025-49704 #CVE-2025-53770 #MicrosoftSharePoint…
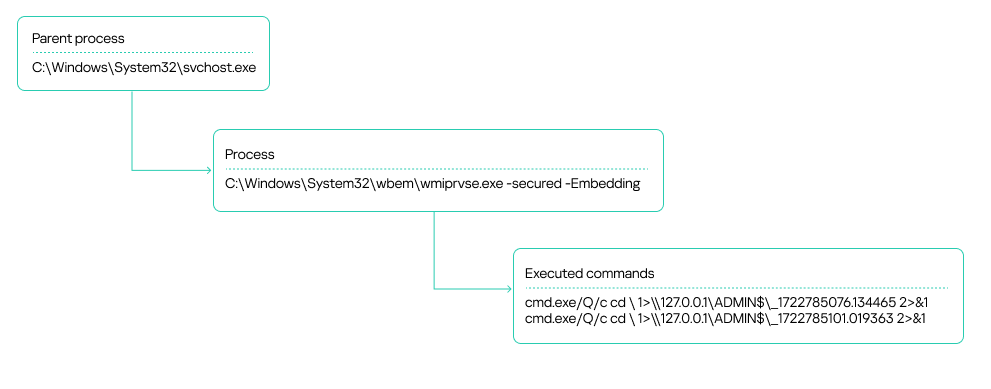
Kaspersky MDR detected a sophisticated APT41 cyberespionage campaign targeting African government IT services, involving custom and publicly available tools such as Cobalt Strike, Pillager, and Mimikatz. The attackers leveraged internal infrastructure for command and control communication, performed credential dumping, lateral movement, and data exfiltration through a compromised SharePoint server. #APT41 #CobaltStrike #Pillager #SharePoint #Mimikatz