
Intezer researchers have analyzed a new variant of ToneShell backdoor linked to Mustang Panda, showing enhanced anti-analysis features while targeting Myanmar. The malware’s evolution reflects ongoing cyber espionage rooted in geopolitical interests by China. #MustangPanda #ToneShell…
Tag: THREAT HUNTING

Vladimir Putin’s foreign policy is driven by a reactive worldview shaped by his life experiences, prioritizing centralized power, strategic flexibility, and the restoration of a Russian sphere of influence using a mix of diplomatic, covert, cyber, and kinetic tools. Western and allied organizations should monitor Kremlin rhetoric and Western policy actions to anticipate escalations and adopt heightened cyber, physical, and personnel protections. #WhisperGate #Sandworm
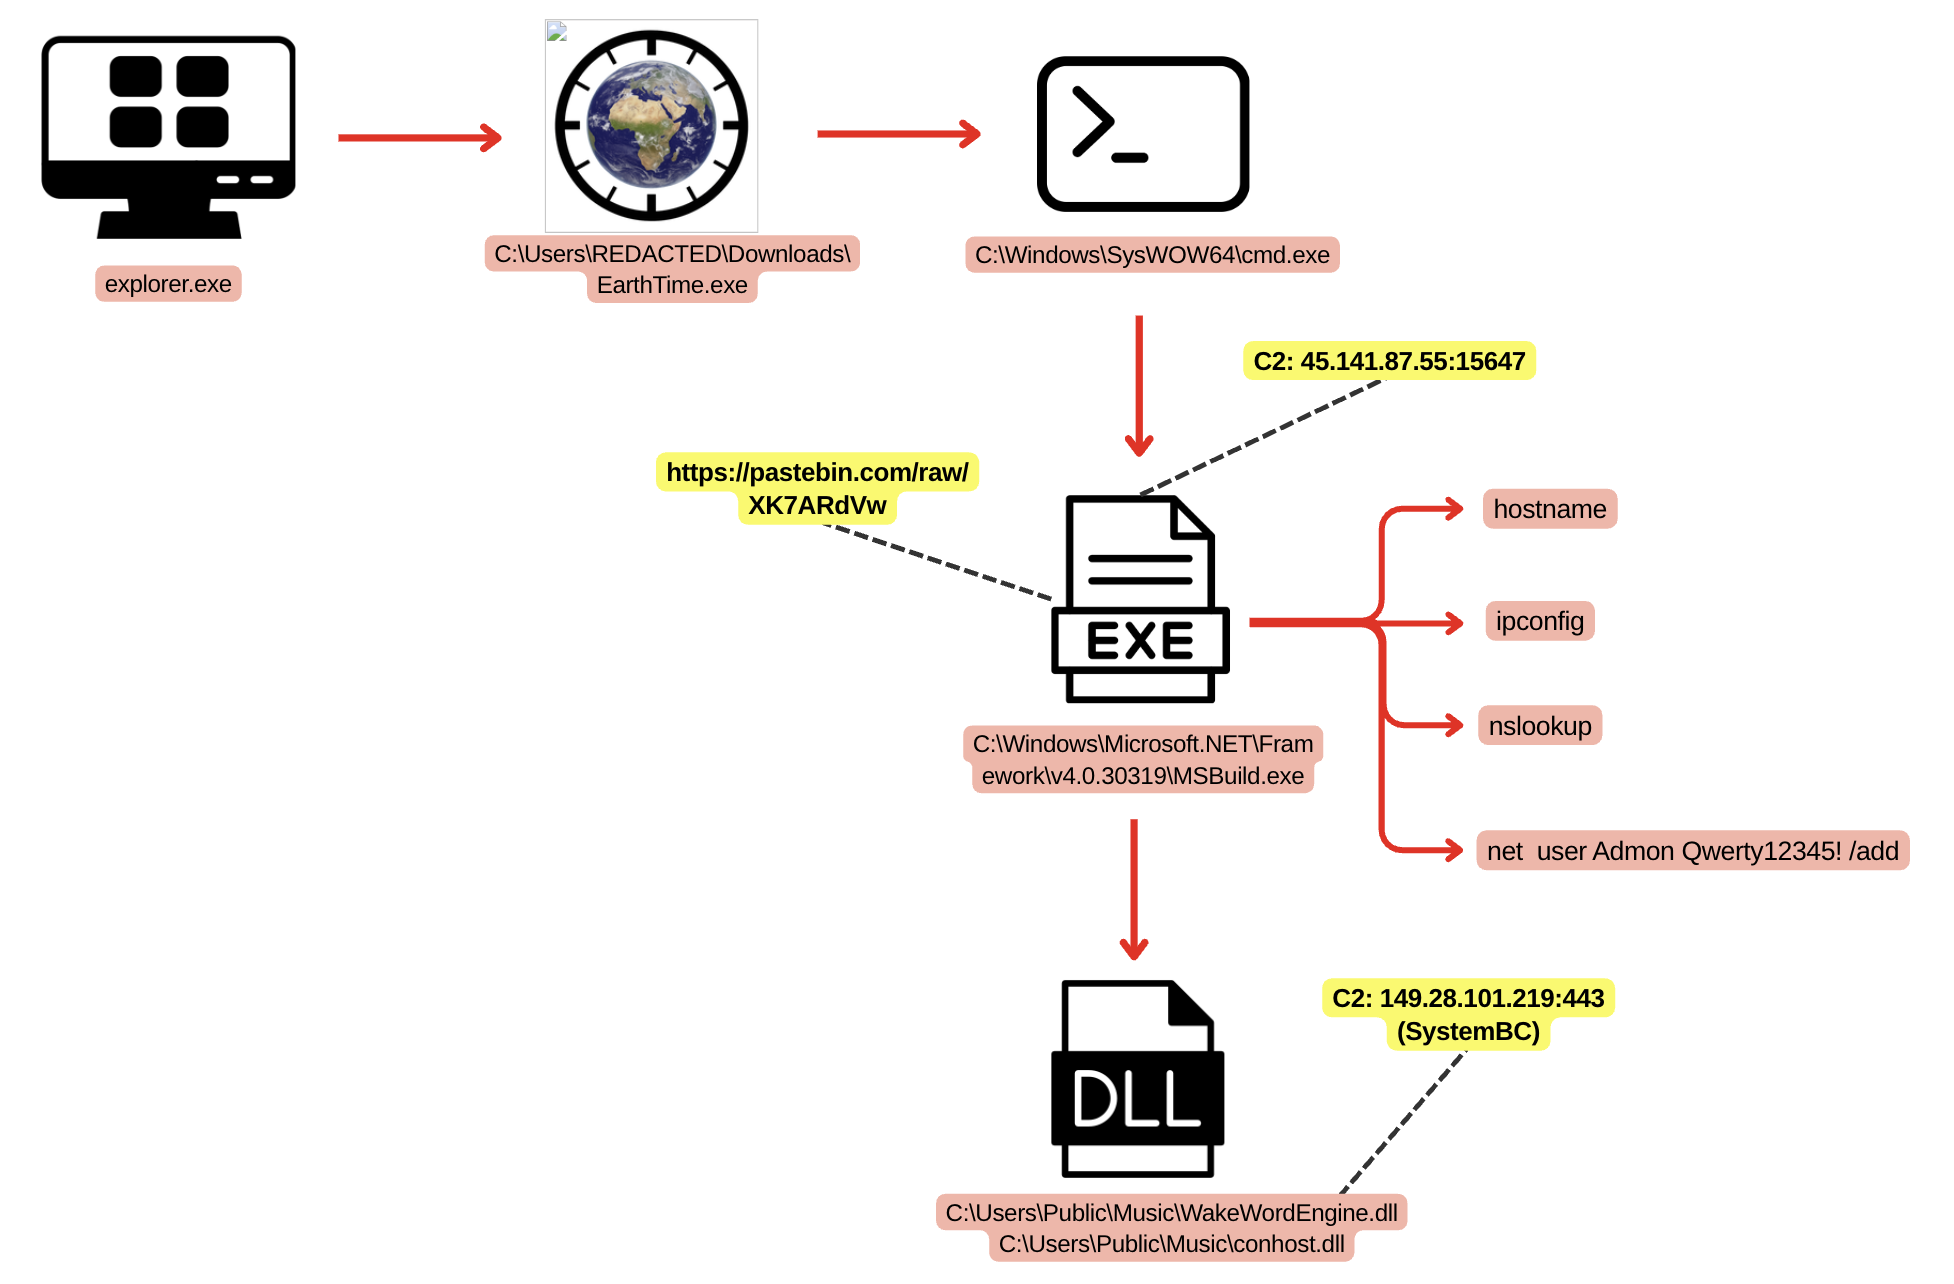
A user-executed malicious EarthTime installer led to deployment of SectopRAT, SystemBC, and later the Betruger backdoor, enabling reconnaissance, credential theft (including DCSync and Veeam credential dumping), lateral movement via RDP/Impacket, and cleartext exfiltration to an FTP host. Artifacts and tooling link the intrusion to multiple ransomware operations—Play, RansomHub, and DragonForce—suggesting a…
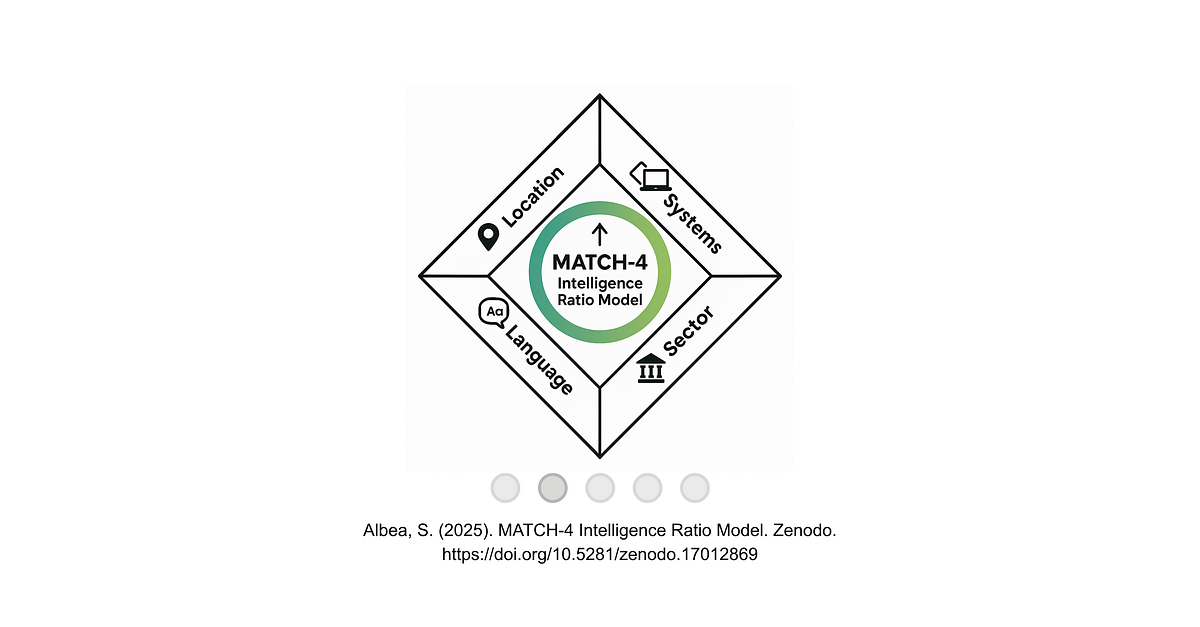
Modern Threat Intelligence feeds contain numerous indicators, but their relevance varies greatly depending on the sector and environment. The MATCH-4 Intelligence Ratio Model helps focus on high-confidence indicators by considering language, location, systems, and sector relevance, improving threat detection efficiency. #ThreatFeeds #Match4Model
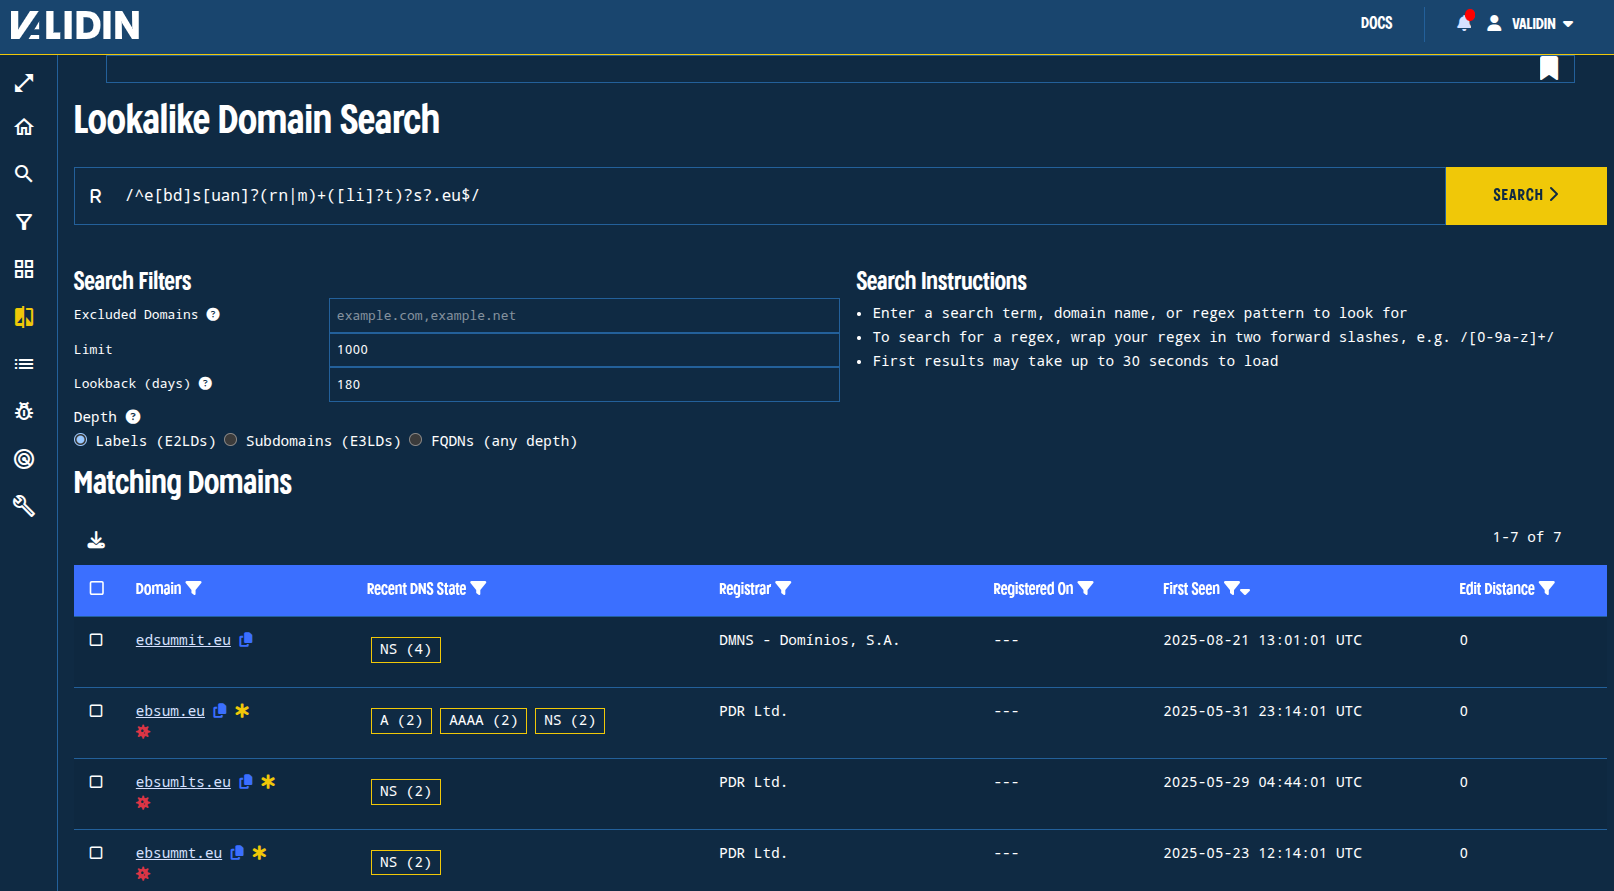
Validin re-tested pivoting and threat-hunting techniques from four recent blog posts (Laundry Bear, phishing/HTTP features, Transparent Tribe, and BlueNoroff) to see which methods still produce novel indicators and active infrastructure. Host response, header/body/hash, DNS/IP, and registration pivots remained fruitful in many cases, producing new domains, IPs, and certificate-based links, while some specific pivots (favicons, title tags, wildcard subdomains) aged out faster. #LaundryBear #TransparentTribe #BlueNoroff
The Gentlemen ransomware group ran a highly tailored campaign using legitimate driver abuse, custom anti-AV tools, Group Policy manipulation, privileged account compromise, and encrypted exfiltration to bypass enterprise defenses and deploy ransomware domain-wide. Victims spanned critical sectors in at least 17 countries, with specific tooling and IOCs including ThrottleBlood.sys, PowerRun.exe, AnyDesk,…

This report by Insikt Group analyzes key threats and attack vectors targeting cloud environments, highlighting misconfigurations, credential abuse, and cloud-native ransomware as major risks. It emphasizes the importance of proper cloud configuration, robust logging, and the use of native cloud security services to mitigate these threats. #CloudRansomware #CredentialAbuse #InsiktGroup
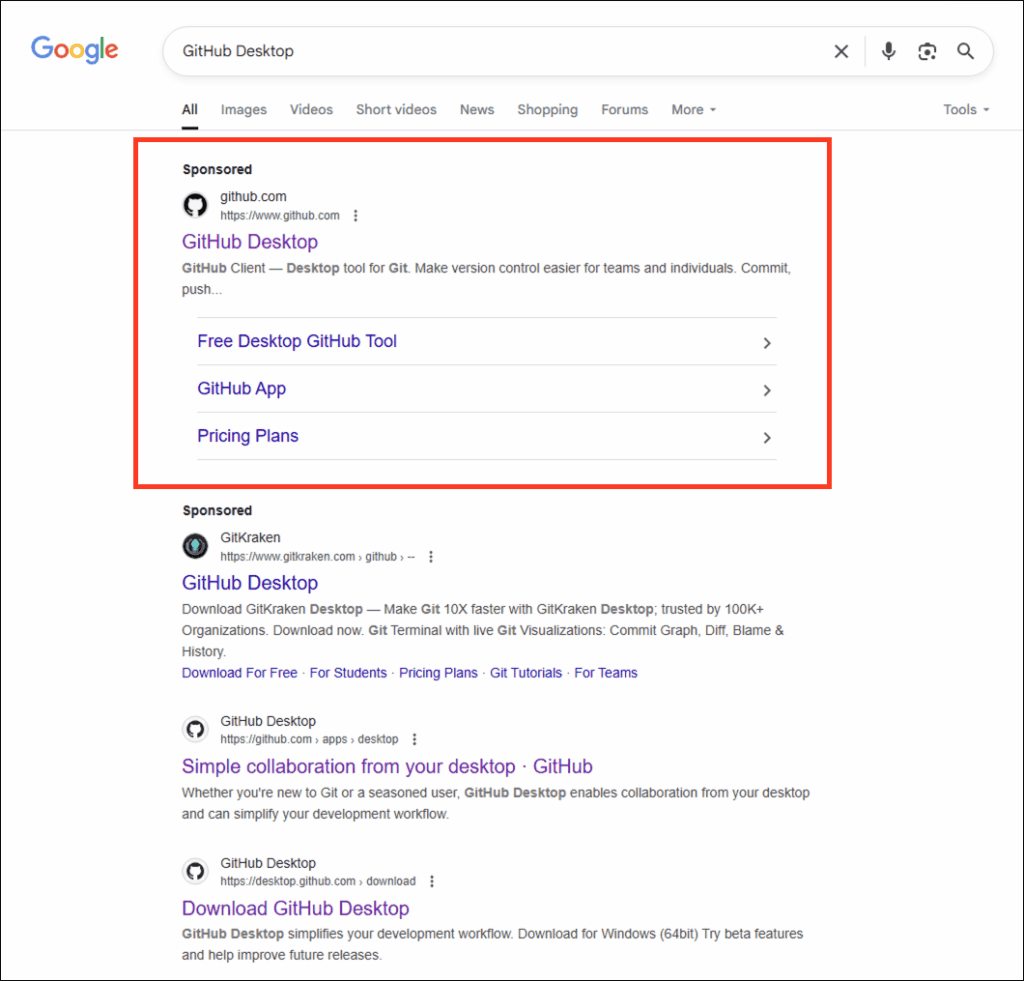
On 19 August 2025 Arctic Wolf Labs disclosed a campaign where attackers used Google Ads and GitHub commit-specific pages to redirect victims to a trojanized GitHub Desktop installer that deploys a GPU-gated decryption loader dubbed “GPUGate.” The campaign delivers a 128 MB MSI with embedded modules and a GPU/OpenCL key-generation routine that prevents execution in many sandboxes and targets Western European IT workers. #GPUGate #AMOS_Stealer
Admin By Request (ABR) provides temporary, audited local administrator access to enforce least privilege, and integrating it with Wazuh centralizes privilege elevation events for faster detection and response. This integration uses Wazuh custom rules to detect denied elevations, repeated requests, and changes to local admin membership, improving visibility into risky privilege…
Salesloft experienced a supply chain-style breach starting with its GitHub account in March, leading to OAuth token theft and subsequent Salesforce data breaches in August. Multiple threat actors, including ShinyHunters and Scattered Spider, were involved, targeting sensitive customer data across various organizations. #GitHubAttack #OAuthTokens #SalesforceDataTheft #SupplyChainBreach
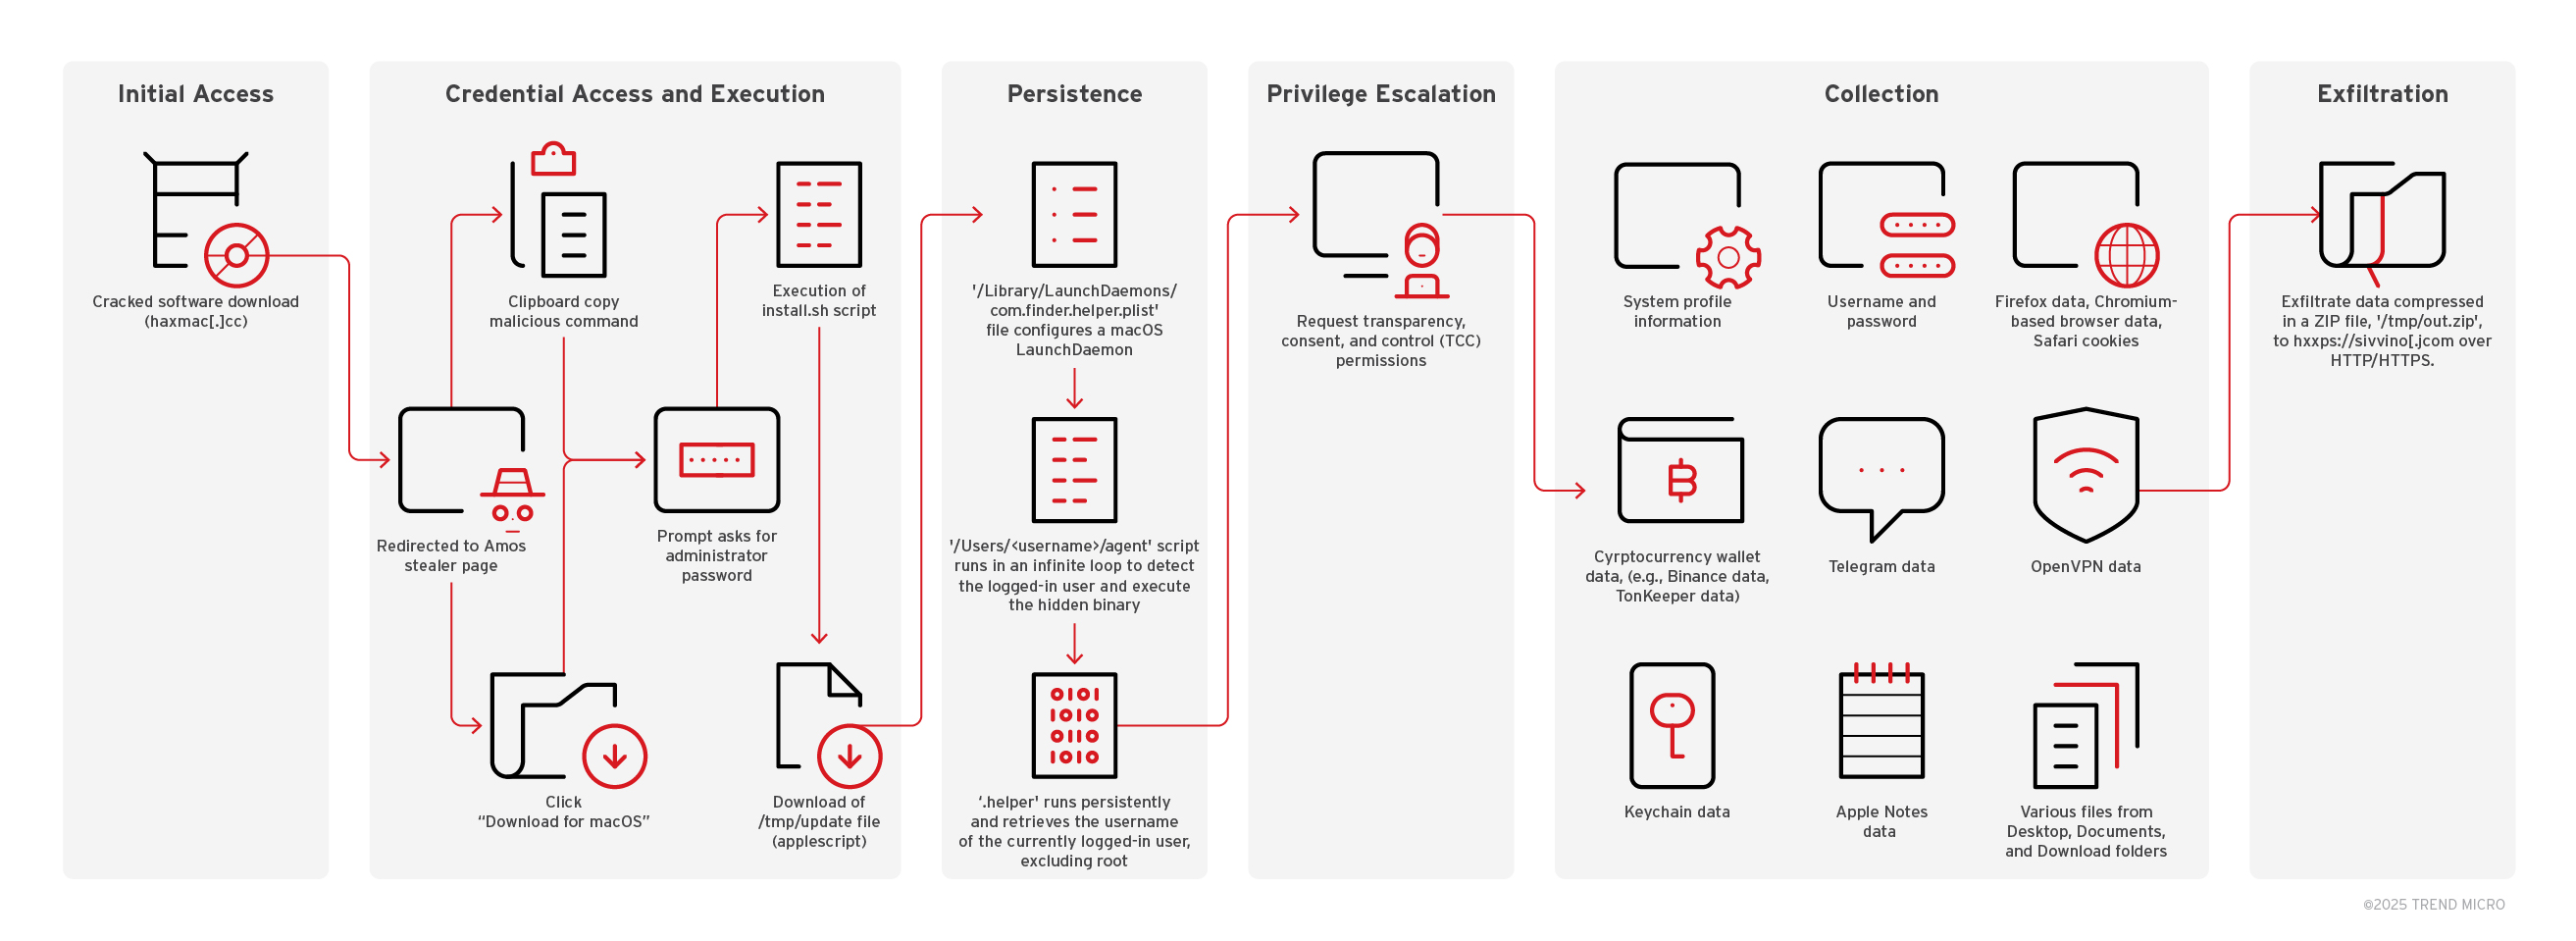
Trend Research analyzed an Atomic macOS Stealer (AMOS) campaign that lures macOS users with trojanized “cracked” apps and malicious copy‑paste Terminal commands to install a data‑stealer. The campaign uses rotating redirector domains and URL rotation to evade takedowns and exfiltrates stolen credentials, browser data, crypto wallets, Telegram data, keychain items, and…
Proofpoint observed an uptick in campaigns delivering Stealerium-based info-stealers between May and July 2025, with multiple low-sophistication cybercrime actors (e.g., TA2715, TA2536) using varied lures and delivery types to deploy the open-source Stealerium and related variants. The malware exfiltrates a wide range of data (browser credentials, cookies, crypto wallets, Wi‑Fi profiles,…

A North Korean state-sponsored group identified as Kimsuky conducted a covert multi-stage campaign using Facebook, email, and Telegram to target defense and North Korea–related activists, delivering password-protected EGG archives containing obfuscated JSE scripts and VMProtect-packed DLLs that establish persistent RATs. The campaign used Korea-specific compressed formats, double Base64/encoded payloads, and Telegram-based C2 communications (woana.n-e[.]kr) to evade detection and maintain long-term access. #Kimsuky #AppleSeed #woana.n-e.kr

An LLM role-playing community was targeted with a backdoor disguised as an “AI Waifu” feature that provides arbitrary code execution and file access via a local agent listening on 127.0.0.1:9999 and 127.0.0.1:4444, enabling remote command execution, file exfiltration, and staged payload delivery. Publicly disclosed IoCs include SHA256 hashes, filenames, local HTTP endpoints, registry persistence key FakeUpdater, and hosting URLs linked to actors using aliases such as KazePsi/PsionicZephyr and Enclave0775. #AIWaifuRAT #PsionicZephyr
Between August 8–18, 2025, a threat actor used compromised OAuth credentials in the Salesloft-Drift integration to exfiltrate large volumes of Salesforce data (Account, Contact, Case, Opportunity) and scanned that data for credentials. Salesloft revoked active Drift tokens and notified impacted customers while Palo Alto Networks Unit 42 urges urgent investigation, credential…