
Daily Recap, critical patch notices hit IBM API Connect with an authentication bypass that could expose protected services, and a critical SmarterMail flaw (CVE-2025-52691) enabling unauthenticated RCE on vulnerable servers, with CISA ordering patches for the MongoBleed flaw following observed intrusions that affected Oracle EBS deployments including Korean Air and the University of Phoenix. The European Space Agency confirmed a breach of external servers, Disney agreed to pay $10 million to settle child data privacy claims related to YouTube content, two ALPHV/BlackCat ransomware operators pleaded guilty, and new info-stealers and malvertising campaigns—ErrTraffic, Lumma, Vidar, Cerberus, and Zoom Stealer—illustrate ongoing threat activity, alongside Intellexa Predator sanctions being reversed. #IBMAPIConnect #CVE2025_52691 #MongoBleed #OracleEBS #KoreanAir #UniversityofPhoenix #EuropeanSpaceAgency #Disney #ALPHV #BlackCat #ErrTraffic #Lumma #Vidar #Cerberus #ZoomStealer #Intellexa #Predator
Tag: SPYWARE

The U.S. Department of the Treasury has removed three individuals linked to the Intellexa Consortium from the sanctions list, raising questions about the reasons for their removal. The Predator spyware, associated with these individuals, continues to pose significant security risks and has been used against civil society globally. #Intellexa #PredatorSpyware…

The U.S. Treasury Department has removed sanctions from three individuals linked to Intellexa’s Predator spyware, reversing previous actions taken in 2024. The spyware, used for espionage by governments worldwide, has raised concerns about national security and civil liberties. #Intellexa #PredatorSpyware…
Researchers have uncovered a new campaign called Zoom Stealer, targeting over 2.2 million browser users through malicious extensions that harvest meeting data. The campaign is linked to the China-based threat actor DarkSpectre, which has a history of large-scale espionage and malware campaigns. #DarkSpectre #ZoomStealer
In early 2025, the Webrat malware family was discovered targeting gamers, security researchers, and students by disguising itself as exploits, game cheats, and cracked software. The campaign involves distributing malicious files via GitHub and other repositories to infect systems and facilitate remote control and data theft. #Webrat #CyberThreats…

ThreatsDay Bulletin: Stealth Loaders, AI Chatbot Flaws AI Exploits, Docker Hack, and 15 More Stories
Cybersecurity is evolving with attackers blending into normal tech environments using sophisticated tactics like open-source tools, AI, and social engineering. The future of defense depends on increased awareness of these subtle and innovative threats. #Nezha #RokRAT…

The ENISA Threat Landscape 2025 report provides a comprehensive analysis of the European cyber threat environment between July 2024 and June 2025, highlighting phishing as the primary intrusion vector and the increasing sophistication of ransomware, state-aligned cyberespionage, and hacktivist activities. It emphasizes emerging trends such as the targeting of mobile devices, supply chain compromises, and the convergence of tactics among threat groups. #ENISAThreatLandscape2025 #Phishing #Ransomware #StateAlignedThreats #Hacktivism #SupplyChainAttacks

A cyber espionage group called “Forum Troll” has shifted its focus from corporate networks to targeting Russian political scientists and economists through sophisticated phishing campaigns. This campaign featured personalized social engineering and utilized known commercial red-teaming tools to infiltrate high-profile individuals. #ForumTroll #RussianAcademics…

Operation ForumTroll conducted targeted phishing against Russian academics in October 2025 using a spoofed e-library domain to deliver a PowerShell-based downloader and an OLLVM-obfuscated DLL loader. The final payload deployed the commercial Tuoni framework and used COM Hijacking for persistence, with C2 infrastructure on fastly.net. #ForumTroll #Tuoni

Operation ForumTroll is a sophisticated phishing campaign targeting individuals in Russia, utilizing zero-day Chrome vulnerabilities to deliver backdoors and spyware. The campaign features personalized emails and uses strategically aged domains to avoid detection, with ongoing threats observed since 2022. #OperationForumTroll #LeetAgent #Dante #Tuoni…
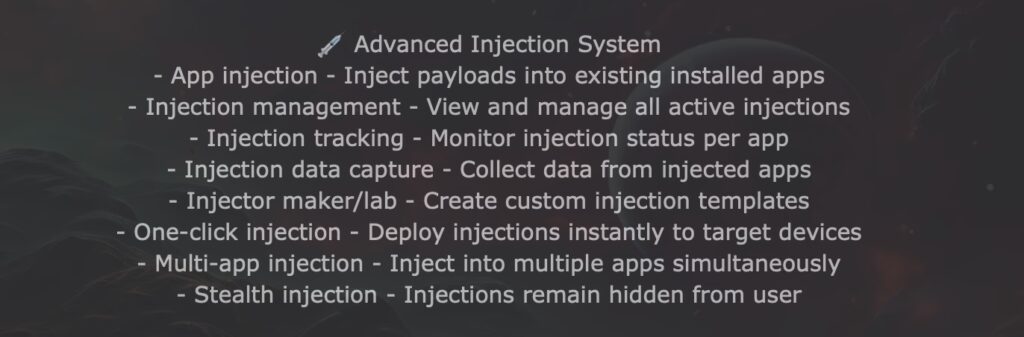
A new Android remote access trojan called Cellik offers extensive surveillance and control features, including real-time screen streaming, keylogging, and data theft. It is sold on the dark web for $150 per month, enabling cybercriminals to bundle malicious payloads into legitimate apps and conduct advanced attacks. #Cellik #AndroidRAT #DarkWebThreats…
Parked and lookalike domains are increasingly weaponized via “direct search” parking and complex traffic distribution systems (TDS) to funnel real users to scams, scareware, spyware, and malware while presenting benign pages to scanners. The report details three distinct domain portfolio actors and examples of delivered threats, including infections by Tedy and typosquats targeting Scotiabank users. #Tedy #Scotiabank

Frogblight is a newly discovered Android banking Trojan targeting mainly users in Turkey that was first disguised as a government court-case app and later appeared as a fake Chrome browser. The malware captures banking credentials via WebView JavaScript injection, collects SMS, app and filesystem data, communicates with C2 servers over REST and WebSocket, and shows signs of active development and possible MaaS distribution. #Frogblight #Turkey
Soverli, a Swiss cybersecurity startup, has raised $2.6 million to develop a sovereign smartphone platform that enhances user security by allowing multiple isolated operating systems on standard mobile devices. This innovative OS can run alongside Android or iOS, providing increased security and continuity even if the main platform is compromised. #Soverli…
The NexusRoute campaign is a large-scale, professionally maintained Android malware and phishing operation that impersonates Indian Government services (mParivahan / e-Challan), distributes malicious APKs via GitHub repositories/GitHub Pages, and operates mass phishing domains to steal UPI, card, and banking credentials. Technical analysis shows a native-backed multi-stage RAT with dynamic code loading, SMS interception, persistence via BroadcastReceivers and foreground services, Socket.IO C2 at 154.61.80.242, and OSINT links to a commercial Android obfuscation/surveillance tooling ecosystem. #NexusRoute #mParivahan