Two malicious Visual Studio Code extensions on the VSCode Marketplace — ChatGPT – 中文版 and ChatMoss (CodeMoss) — collectively installed about 1.5 million times, secretly exfiltrate developer files and data to China-based servers as part of a campaign dubbed MaliciousCorgi. They pose as AI coding assistants but quietly upload opened files (encoded in Base64), can harvest up to 50 workspace files on command, and use hidden analytics SDKs (Zhuge.io, GrowingIO, TalkingData, Baidu Analytics) to fingerprint and profile users without consent. #MaliciousCorgi #VSCodeMarketplace
Tag: SPYWARE
Spain’s High Court has closed its probe into alleged Pegasus spyware surveillance of senior officials after Israel failed to cooperate with multiple requests for information. Judge José Luis Calama said Israel’s refusal breached international obligations after the court found evidence that Pegasus infections — including five infections of Prime Minister Pedro…

The Irish government will draft legislation to legalize law enforcement use of spyware and electronic scanning equipment, with interception requests required to be authorized by a court. The Department of Justice says the bill will include robust legal safeguards and will be developed with the Attorney General’s Office and other state…

Daily Recap, The latest funding rounds show Depthfirst raising $40 million, Novee securing $51.5 million, and isVerified entering stealth with voice-deepfake detection, signaling ongoing investor interest in vulnerability management and identity assurance. It further catalogs vulnerabilities, breaches, and attacks across FortiSIEM, Desktop Windows Manager, Node.js async_hooks, c-ares, Belgian Hospital, Monroe University, Pax8, Victorian Department of Education, RedVDS, Predator spyware, PLUGGYAPE, ConsentFix, Reprompt, third-party risk, and Windows 365/Cloud PC service disruptions. #Depthfirst #Novee #isVerified #FortiSIEM #DesktopWindowsManager #NodeJS #async_hooks #c-ares #BelgianHospital #MonroeUniversity #Pax8 #VictorianDepartmentOfEducation #RedVDS #PredatorSpyware #PLUGGYAPE #ConsentFix #Reprompt #Windows365 #CloudPC
Daily Recap, Attackers are targeting LLMs in a widespread campaign to manipulate model interfaces and access data. Experts warn cyber disruption is now a sovereign risk and outline what CISOs should expect through 2026. #LLMCampaign #APT28 #IranBlackouts #ArmeniaRecords #HungaryAsylum #n8n #GoBruteforcer #GogsRCE #UHCancerCenter #Instagram #Facebook #ApexLegends #PortsBreach #RotterdamPorts #AntwerpPorts
Recent research reveals that Predator spyware, developed by Cytrox and marketed mainly to government agencies, is more advanced and adaptable than previously thought. Its self-diagnostic and anti-analysis features make it a formidable tool for covert surveillance. #PredatorSpyware #Cytrox #Intellexa #NSOGroupPegasus #GovernmentSurveillance…

Hungary has granted asylum to Poland’s former justice minister Zbigniew Ziobro amid allegations of involvement in a major spyware scandal. The case involves charges of embezzlement and illegal surveillance, highlighting political tensions within the EU. #Ziobro #PolishSpywareScandal…
The FBI warns about North Korean APT group Kimsuky using spear-phishing with malicious QR codes, known as quishing, to target government and research organizations. This method bypasses security controls, stealing data and hijacking cloud accounts, making it a high-threat vector in enterprise environments. #Kimsuky #quishing…
This roundup highlights recent cybersecurity incidents including AI data violations, cyberattacks on Jaguar Land Rover, and the arrest related to the Desjardins data breach. It also discusses Chinese cyber activities against Taiwan and US congressional email hacks. #genAI #JaguarLandRover #Desjardins #SaltTyphoon #OwnCloud…

This week’s cybersecurity news highlights active threat actors using honeypots and exploiting known vulnerabilities to distribute malware. Key developments include a fake hack trap by Resecurity, cryptocurrency miners exploiting GeoServer flaws, and a surge in Chinese-backed attacks on Taiwan’s infrastructure. #LAPSUS$ Hunters #GeoServer #MuddyWater…

A Michigan-based stalkerware company owner pleaded guilty to federal charges for selling spying applications aimed at tracking individuals without their consent. This case marks the first successful prosecution of a stalkerware operator since 2014, highlighting increasing legal actions against such threats. #pcTattletale #BryanFleming…
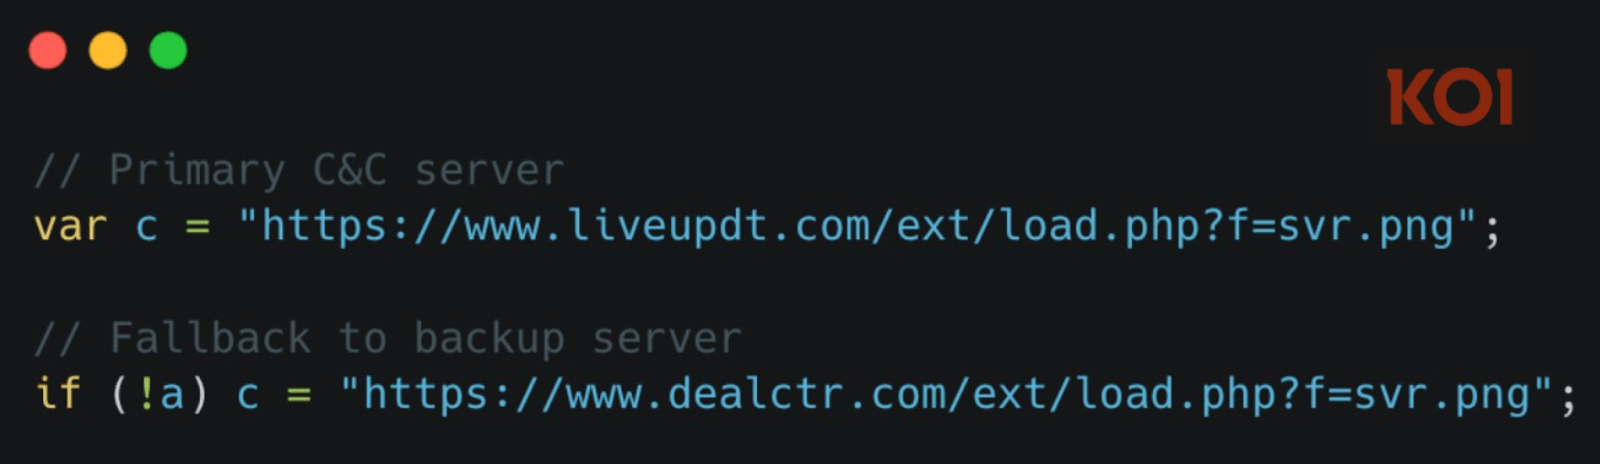
A single, well-resourced Chinese threat actor called DarkSpectre operated at least three large extension-based campaigns—ShadyPanda, GhostPoster, and the newly disclosed Zoom Stealer—infecting over 8.8 million users across Chrome, Edge, Firefox, and Opera using varied techniques including steganography, remote code injection, and real-time WebSocket exfiltration. The Zoom Stealer campaign alone harvested corporate meeting intelligence from 2.2M users by scraping 28+ conferencing platforms and streaming data to attacker-controlled Firebase and cloud function infrastructure. #DarkSpectre #ZoomStealer
The January 2026 Android update addresses a critical vulnerability (CVE-2025-54957) in the Dolby audio decoder that could enable remote code execution without user interaction. This flaw, exploited through specially crafted media files, affects multiple devices and has been patched by Google in December 2025. #CVE-2025-54957 #DolbyDigitalPlus…
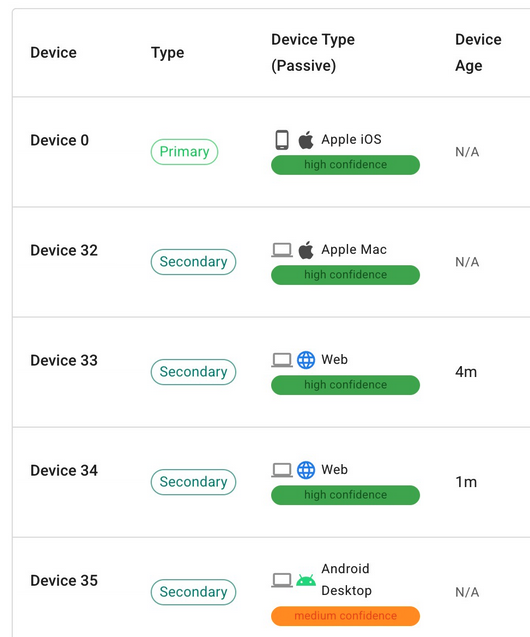
Meta is working to address WhatsApp vulnerabilities related to device fingerprinting and zero-day exploits that allow spyware delivery. Despite some progress, these issues highlight ongoing challenges in protecting user privacy and preventing targeted attacks on the platform. #WhatsAppZeroDay #DeviceFingerprinting…
2025 was marked by significant cybersecurity incidents including high-profile data breaches, advanced cyberattacks, and increasingly sophisticated threat actor activities. Notable events include the PornHub data breach, the ByBit crypto heist, and the rise of AI-powered attacks. #PornHubDataBreach #ByBitCryptoHeist #AIpromptInjections