Daily Recap, the security landscape today spans zero-day exploits patched in Apple WebKit and active Gogs exploitation affecting hundreds of self-hosted instances, along with critical flaws in Varex Imaging, GDCM, and Johnson Controls iSTAR Ultra impacting medical and industrial systems. The report also highlights Lazarus Group and Ashen Lepus espionage campaigns, major data breaches at Coupang and Pierce County Library, and a surge of malware kits and phishing tools including PyStoreRAT, Agent Tesla, BlackForce, GhostFrame, InboxPrime AI, and DroidLock. #LazarusGroup #AshenLepus #Coupang #PierceCountyLibrary #PyStoreRAT #AgentTesla #BlackForce #GhostFrame #InboxPrimeAI #DroidLock #AppleWebKit #Gogs #VarexImaging #GDCM #JohnsonControls #AshTag
Tag: SPYWARE
Apple has issued emergency patches for two critical WebKit zero-day vulnerabilities exploited in targeted, highly sophisticated attacks on specific individuals. These vulnerabilities, tracked as CVE-2025-43529 and CVE-2025-14174, affected various Apple devices and were also addressed by Google Chrome in coordination with Apple. #WebKitVulnerabilities #TargetedAttacks

Apple has released security updates for multiple platforms to fix two critical vulnerabilities in WebKit that have been exploited in the wild, including one previously patched by Google Chrome. These flaws are believed to have been used in targeted spyware attacks, affecting a wide range of Apple devices and browsers. #WebKitVulnerabilities…

Daily Recap, authorities pursue a broad set of cybercrime actions—from Myanmar digital arrest-fraud charges and Accenture fraud to FedRAMP-related contractor concerns and indictments targeting Russian-linked hacktivists. The recap also flags data breaches and privacy risks at Pierce County Library, LastPass fines, Petco Vetco exposure, doorbell and camera privacy debates, and widespread vulnerabilities and malware activity including NANOREMOTE, BRICKSTORM, Mirai, CastleLoader, Spiderman Phishing, DroidLock, and large Docker Hub credential leaks.
#NANOREMOTE #BRICKSTORM #WarpPanda #LastPass #PierceLibrary #Petco #Vetco #DroidLock #CastleLoader #SpidermanPhishing #DockerHub #Mirai

This week’s cyber stories highlight the rapid evolution of digital threats, from malware in movie downloads to sophisticated botnets exploiting system vulnerabilities. The Threatsday Bulletin provides a concise overview of major security incidents and emerging risks in the cyber landscape. #Mirai #LummaStealer…
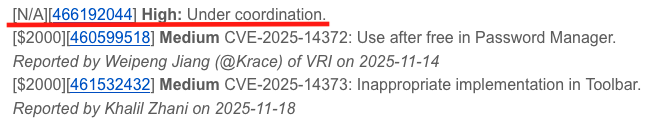
Google has released a security patch for the Chrome browser to fix a high-severity zero-day vulnerability actively exploited in the wild. The flaw is likely a memory corruption issue that could enable remote code execution or sandbox escape, often targeted in government espionage campaigns. #ChromeZeroDay #V8JavaScriptEngine…
Daily Recap, Microsoft released its December security updates addressing 56–57 flaws, including 3 zero-days and active exploits, while Adobe patched nearly 140 vulnerabilities and SAP and other vendors issued urgent fixes. Threat actors and incidents highlighted include North Korea-linked React2Shell operators exploiting to deploy new EtherRAT variants, CastleLoader/CastleRAT under GrayBravo expanding its infrastructure targeting logistics and transport, Storm-0249’s stealthy ransomware tactics, and high-profile breaches and investigations involving Coupang, HSE, and the Khashoggi spyware allegations. #EtherRAT #CastleLoader

The widow of Jamal Khashoggi has filed a lawsuit in France claiming that Saudi Arabia used Pegasus spyware to monitor her devices before her husband’s murder. The complaint links the surveillance to her husband’s killing and highlights ongoing legal actions against the NSO Group for facilitating spyware attacks. #JamalKhashoggi #Pegasus #NSOGroup…
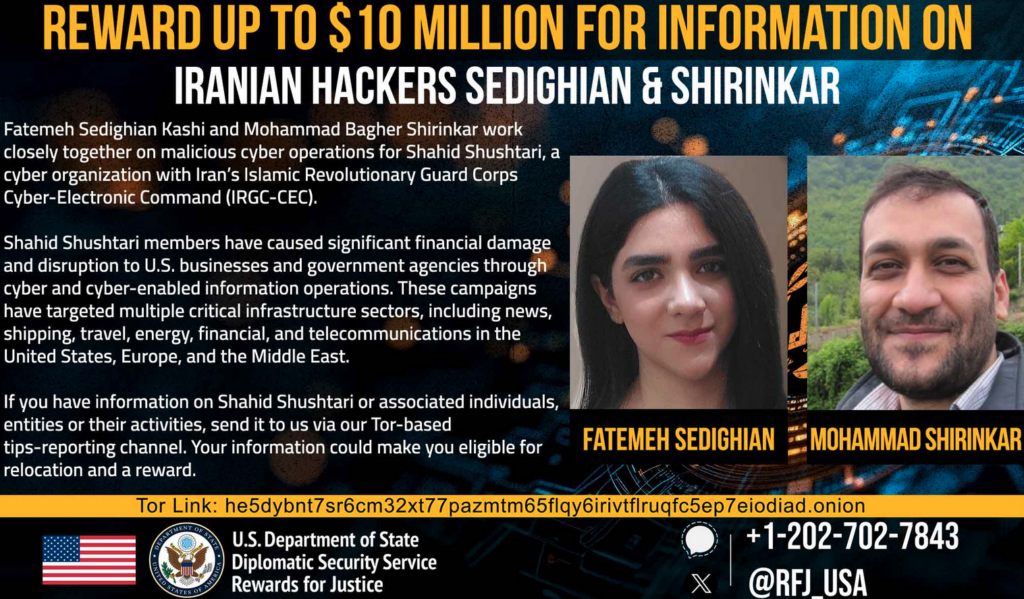
The US government has announced a $10 million reward for information on the Iranian hacking group Shahid Shushtari, linked to Iran’s IRGC-CEC. The group has conducted cyberattacks against critical infrastructure and influence operations globally, including targeting the 2024 Olympics and US elections. #ShahidShushtari #IRGC-CEC…

Cybersecurity experts have uncovered new Android malware families FvncBot and SeedSnatcher, as well as an upgraded ClayRat version with enhanced capabilities. These threats target banking, cryptocurrency, and personal data, demonstrating evolving tactics in Android malware. #FvncBot #SeedSnatcher #ClayRat…
Google and Apple have issued global cybersecurity alerts warning users of targeted surveillance by state-linked hackers and commercial spyware vendors like Intellexa. These notifications highlight the growing threat of government-backed digital espionage and the widespread use of advanced spyware tools worldwide. #Intellexa #StateLinkedHackers…
Daily Recap, exploits ranging from React2Shell flaws in React/Next.js being actively exploited by China-linked groups to a Cloudflare outage caused by emergency patches highlight persistent risks across web infrastructure. BRICKSTORM activity by PRC-linked actors targeting VMware vSphere in U.S. networks, alongside campaigns such as Array Networks gateway exploitation, Sha1-Hulud supply-chain worm, and Intellexa and Predator surveillance tools, illustrate a broad threat landscape. #React2Shell #BRICKSTORM

A new report reveals that Intellexa’s Predator spyware has been used to target civil society members in Pakistan and potentially other countries, employing sophisticated zero-day exploits and various infection vectors. Despite international sanctions and public scrutiny, the company continues to develop and deploy invasive surveillance tools with possible human rights violations….
Internal leaks reveal Intellexa staff had direct remote access to at least 10 Predator customer systems, including surveillance dashboards and live targeting operations. The leaked documents expose how the sanctioned spyware vendor continues to operate despite US sanctions, with active deployments and infection vectors such as silent advertising-based infections. #Intellexa #PredatorSpyware…
Daily Recap, regulatory moves span India withdrawing the Sanchar Saathi mandate and the UK’s cookie-enforcement push, with broader state activity highlighting Russia’s connected-car vulnerabilities and sanctions related to cyber espionage. The week also features critical RSC bugs in React/Next.js, LNK flaws, Elementor/King Addons WordPress exploits, a record AISURU DDoS with up to 4 million bots, Predator spyware activity, and data breaches at Freedom Mobile and Marquis alongside Rhysida ransomware pressure on local governments. #SancharSaathi #PredatorSpyware #AISURU #Rhysida #KingAddons #LNK #FreedomMobile #Marquis