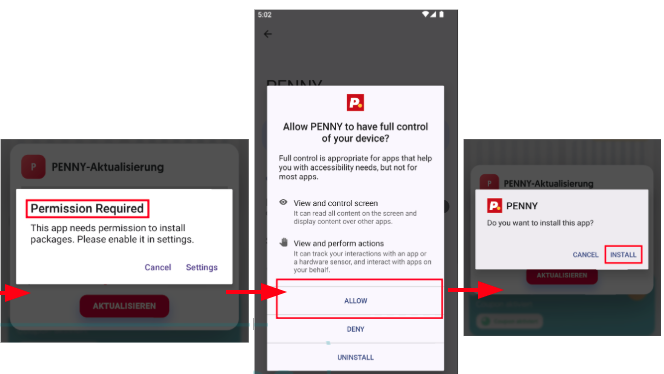
A new Android banking trojan called Albiriox is being marketed on cybercrime forums, with capabilities for real-time device control and overlay attacks. This malware targets over 400 applications globally and is offered as a malware-as-a-service. #Albiriox #RussianThreatActors…
Tag: SPYWARE

North Korean threat actors are conducting a persistent campaign targeting blockchain and Web3 developers by deploying malware through fake coding tests and job interviews. This sophisticated operation involves nearly 200 malicious npm packages, a complex multi-layered infrastructure, and an evolving approach to bypass security measures. #NorthKorea #npmMalware…

Daily Recap, London councils experienced a cyber incident that temporarily disrupted services across local authorities, while a widespread US emergency alert outage affected OnSolve’s CodeRED service and related Georgia Clerks Authority court-filing systems. The evolution of threats—from mass account-takeover fraud to Crypto Copilot-driven DeFi siphoning and state-sponsored web implants—highlights ongoing risk across public-sector, financial, and infrastructure targets and the imperative for effective risk management. #GeorgiaClerks #CryptoCopilot

A recent experiment by Sharjah Police demonstrated how easily people can be misled by QR codes, especially when promising free WiFi. International research indicates that cybercriminals are increasingly exploiting user trust through global QR code phishing campaigns like “Scanception.” #SharjahPolice #Scanception…

Multiple cyber threat actors are actively exploiting commercial spyware to target messaging app users worldwide, using techniques like phishing, QR codes, zero-click exploits, and impersonation. These threats primarily aim at high-value individuals, including government officials and civil society organizations, emphasizing the need for enhanced mobile communication security. #Spyware #ZeroClickExploits…
CISA warns about the increasing use of commercial spyware targeting mobile messaging app users through sophisticated exploits. Threat actors are leveraging zero-day and zero-click vulnerabilities to deliver malicious payloads, especially targeting high-value individuals. #NSOGroup #Landfall…
Write 2 sentences summarizing the content (Cybersecurity News ‘Daily’ Recap). At the end, add hashtags for specific keywords mentioned in the article—such as names of malware, threat actors, or affected organizations/systems. Avoid general terms like #malware, #ransomware, or #cybersecurity. Use this format: #Keyword1 #Keyword2. Start with ‘Daily Recap, ‘
Daily Recap, The recap highlights ongoing third-party app risks with Gainsight tied to Salesforce after unusual OAuth activity, and tracks a large-scale state-backed espionage campaign by APT24 using BadAudio against Taiwan. It also covers Android backdoors like Baohuo and Sturnus targeting messaging apps, critical flaws and active exploitation in WSUS and network devices, plus financial crime, legal actions, and policy shifts shaping the broader cybersecurity landscape. #Gainsight #APT24 #BadAudio #Baohuo #Sturnus #WSUS #ShadowPad #ICAM365 #AsusRouter #DIR-878 #SamouraiWallet #Almaviva #NSO
This week’s cybersecurity roundup highlights a surge in scanning targeting Palo Alto Networks and a major data breach affecting WEL Companies. Key issues include hacking incidents, legal battles over spyware, and new cyberattack techniques like network implants and AI prompt injections. #PaloAltoNetworks #NSOGroup #WELCompanies…
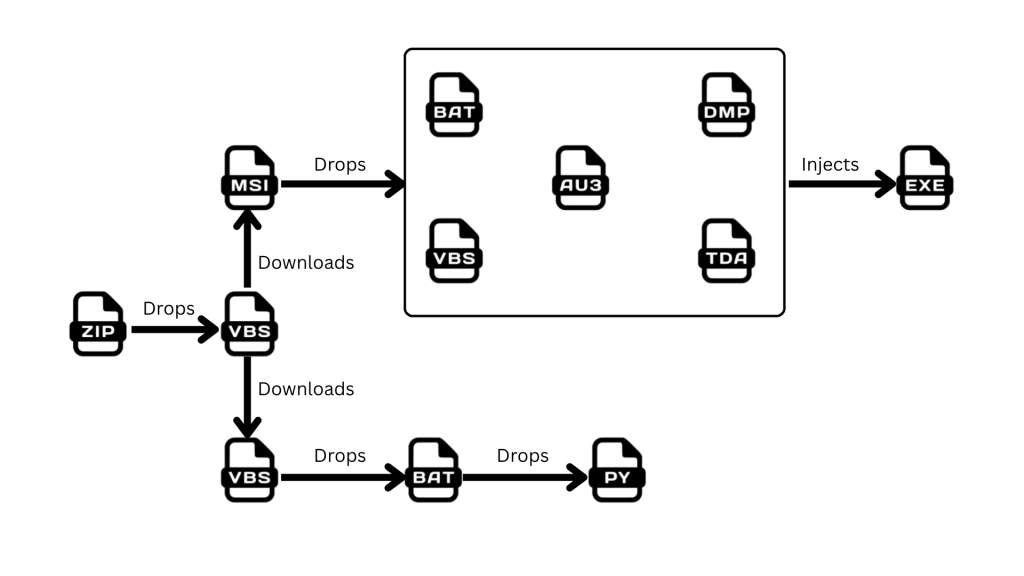
K7 Labs uncovered a Water-Saci campaign targeting Brazil that spreads a banking trojan and SorvePotel-related components by abusing WhatsApp Web via a Python/Selenium-based automation script and in-memory payload delivery. The attack chain begins with a phishing ZIP containing an obfuscated VBS that downloads an MSI and VBS to install Python, ChromeDriver, and a whats.py script that harvests contacts, sends in-memory payloads through WhatsApp Web, and reports results to PHP C2s. #SorvePotel #Water-Saci

NSO Group is appealing a court order that requires it to cease targeting WhatsApp with its Pegasus spyware, which affected 1,400 users. The company claims the ruling could threaten its existence and hinder law enforcement operations, arguing the judge misinterpreted how Pegasus operates. #NSOGroup #Pegasus #WhatsAppTargeting #CFAA…
A new Android banking trojan called Sturnus targets secure messaging apps like WhatsApp, Telegram, and Signal to steal sensitive information. It can conduct overlay attacks, log keystrokes, and remotely control infected devices, posing a significant threat to financial institutions and users in Europe. #Sturnus #AndroidTrojan #ThreatFabric #FintechThreats…
Amazon’s threat intelligence describes how Iranian threat groups have used cyber operations to enable physical attacks, illustrating a rising trend in hybrid warfare. These cases show the increasing integration of cyber reconnaissance with kinetic military actions, emphasizing the need for enhanced defense strategies. #ImperialKitten #MuddyWater…

Trustwave SpiderLabs discovered Eternidade Stealer, a Delphi‑compiled banking trojan distributed via a WhatsApp‑propagating worm and social engineering that steals contacts and delivers an MSI dropper which deploys credential‑stealing components. The campaign uses IMAP‑based dynamic C2 retrieval, localized Brazilian targeting, encrypted C2 commands, and overlay/keylogging capabilities. #Eternidade #Casbaneiro
A China-linked threat actor called PlushDaemon is hijacking software update traffic through a new implant named EdgeStepper to carry out cyberespionage. This group has targeted multiple countries and industries using sophisticated malware and network hijacking techniques. #PlushDaemon #EdgeStepper #SlowStepper

Meta has introduced the WhatsApp Research Proxy tool to facilitate research into WhatsApp’s network protocol, aiming to improve security and understand platform abuse. The company emphasizes efforts to lower barriers for researchers, backed by over $25 million paid in bug bounties and recent security updates addressing vulnerabilities and data exposure issues….