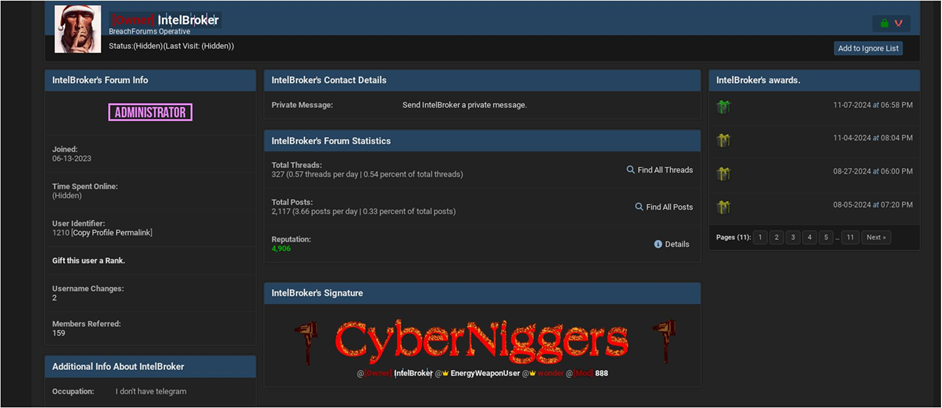
IntelBroker is a sophisticated cyber adversary linked to various high-profile data breaches and illicit data trading, operating primarily through BreachForums. The actor has developed ransomware, conducted significant breaches, and engaged in dark web data sal…
Tag: THREAT HUNTING
Victim: First Federal Savings & Loan Country : US Actor: play Source: http://k7kg3jqxang3wh7hnmaiokchk7qoebupfgoik6rha6mjpzwupwtj25yd.onion/topic.php?id=dDMdHMUIdmiLUv Discovered: 2025-02-25 22:33:10.065349 Published: 2025-02-25 22:31:41.214168 Description : Geographical location: North America…
Summary: The first quarter of 2025 saw intensified cyber threats as cybercriminals launched sophisticated malware attacks, including the NetSupport RAT and Lynx Ransomware. A range of malware families employed advanced tactics for infiltration, persistence, and data exfiltration, leaving organizatio…
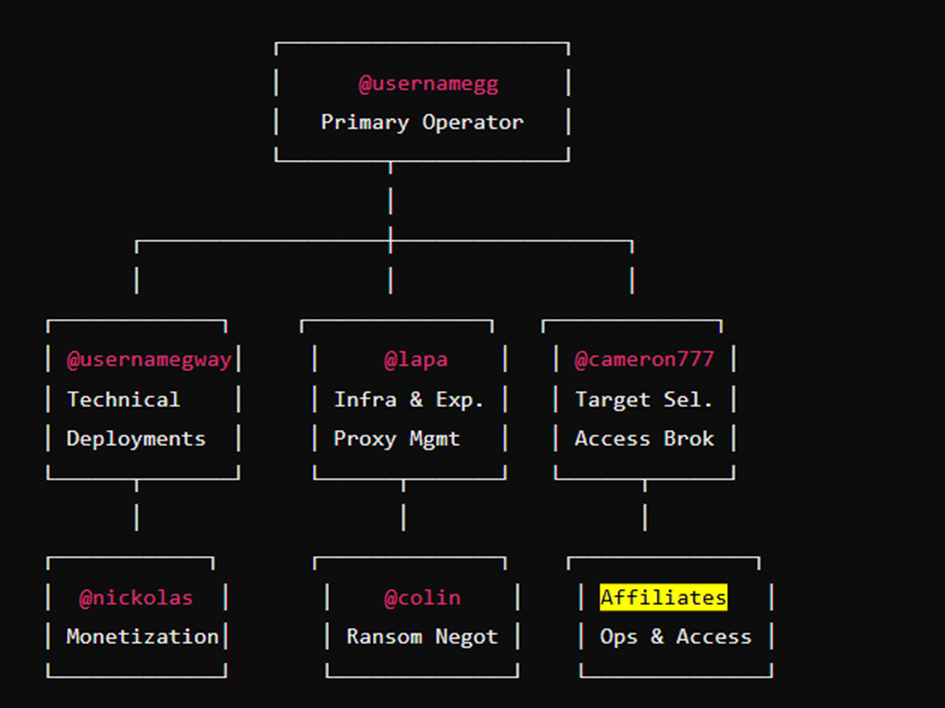
This article provides insights into the Black Basta ransomware group, detailing their structure, attack tactics, and associated tools. Through a recent leak of their chats, critical information about their operational methods has been revealed, allowing for th…

The attackers masquerade as customers, leveraging social engineering tactics to trick support agents into downloading malicious files. The attack begins with the creation of fraudulent support tickets by attackers using newly registered accounts….

Systems become vulnerable when compiled with the _USE_SQLITE_ option, which activates SQLite integration for hints database management, and when administrators enable ETRN commands without proper serialization safeguards….

Organizations using Sitevision CMS are urged to upgrade to version 10.3.2 or later and ensure proper configuration of WebDAV access controls while rotating passwords for sensitive keystores….
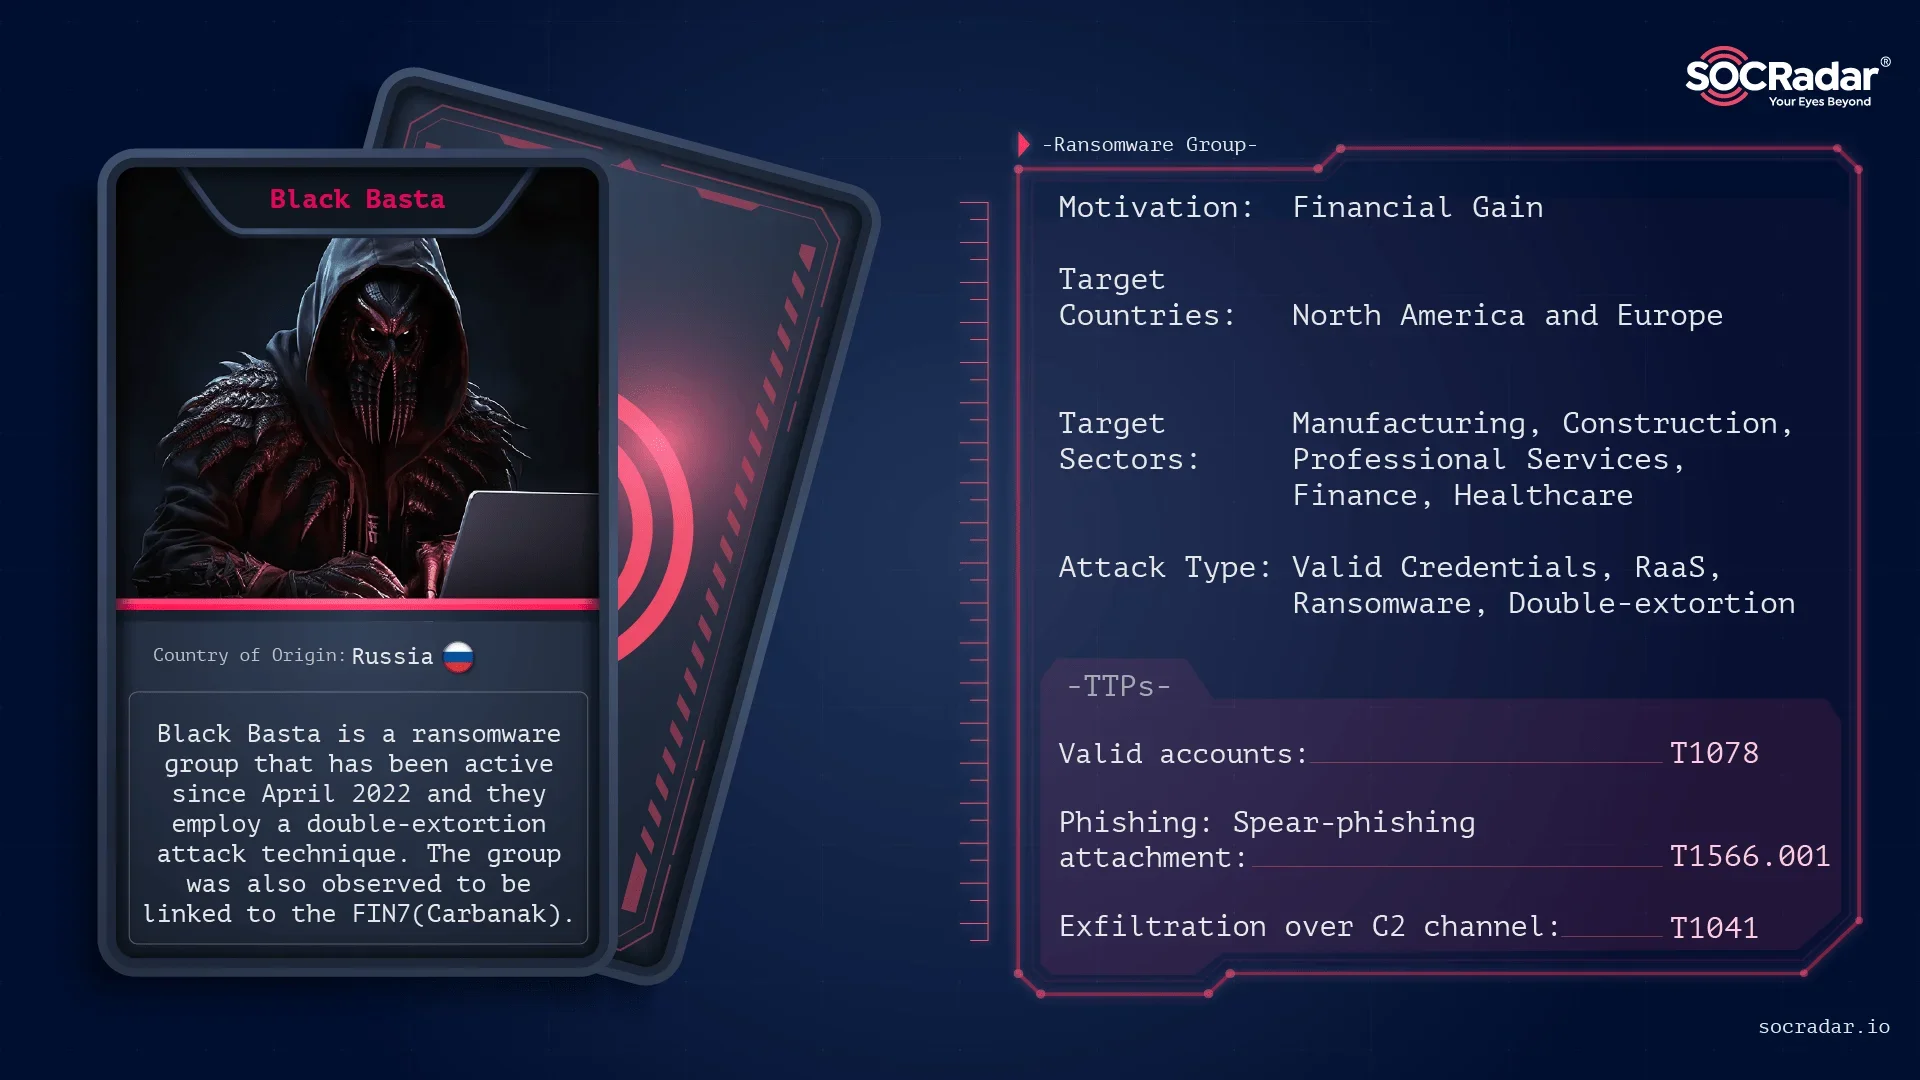
On February 11, 2025, leaked internal chat logs from the notorious Black Basta ransomware group surfaced, exposing internal conflicts and their alleged targeting of Russian banks. The revelations include significant instability within the group, with key membe…

A recent investigation has uncovered a malicious application, DriverEasy, masquerading as a legitimate Google Chrome update to steal user credentials.The malware leverages Dropbox’s API to exfiltrate sensitive information….
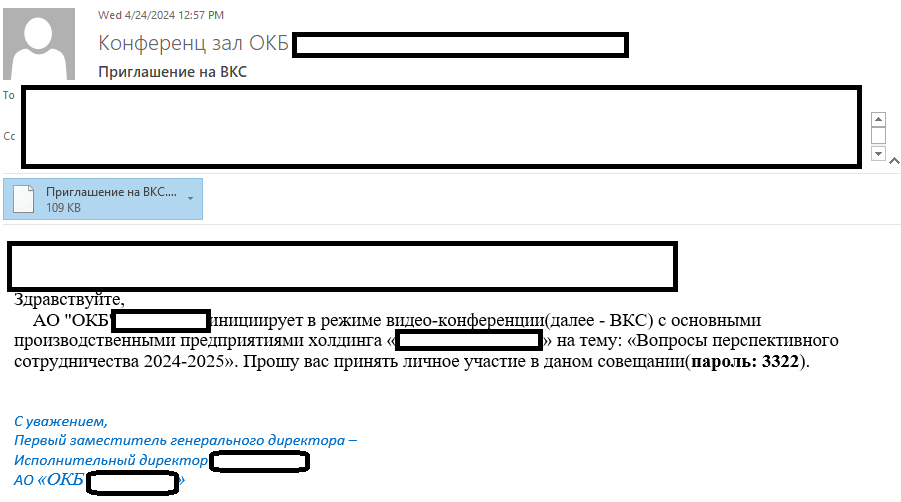
Angry Likho, an APT group also known as Sticky Werewolf, has been active since 2023, targeting government agencies and large organizations primarily in Russia and Belarus through spear-phishing campaigns. The group employs sophisticated techniques involving ma…
The recent CVE-2025-0108 vulnerability in Palo Alto Networks’ PAN-OS allows unauthorized access to the management interface and execution of PHP scripts, posing significant risks despite not enabling remote code execution. There’s a growing trend of exploit at…

Delivered primarily through phishing emails containing malicious attachments or links, the malware exfiltrates stolen data to its command-and-control (C2) server via SMTP or Telegram bots….
Introduction In the ever-evolving landscape of cybersecurity, staying ahead of threats requires a diverse toolkit and a wealth of knowledge. This article compiles a comprehensive list of resources, including tools, rules, and templates, designed to aid cybersecurity professionals in their quest for…

These advisories flagged under ICSA-24-191-01 (Update A) and ICSA-25-035-02 (Update A), address high-severity flaws that could enable remote code execution and denial-of-service attacks across industrial environments….
Summary: New findings by iVerify reveal that zero-click Pegasus spyware is affecting a broader range of individuals, including business executives, not just members of civil society. During December alone, Pegasus was detected on 11 out of 18,000 tested devices. This alarming trend increases concern…