Agentic AI is transforming security operations by enabling autonomous agents to efficiently tackle incidents, enhancing decision-making, and automating routine tasks. Its integration into security frameworks allows for real-time threat detection and response, …
Tag: THREAT HUNTING
Salt Typhoon is an APT group allegedly linked to China’s Ministry of State Security, targeting U.S. infrastructure and government entities with a focus on corporate data theft and espionage. Their operations include advanced techniques and have resulted in num…

This article analyzes APT attacks leveraging political and social issues in South Korea, with a focus on a spear phishing campaign distributing malicious files via email. The attack targets users in the North Korean sector using social engineering tactics to a…
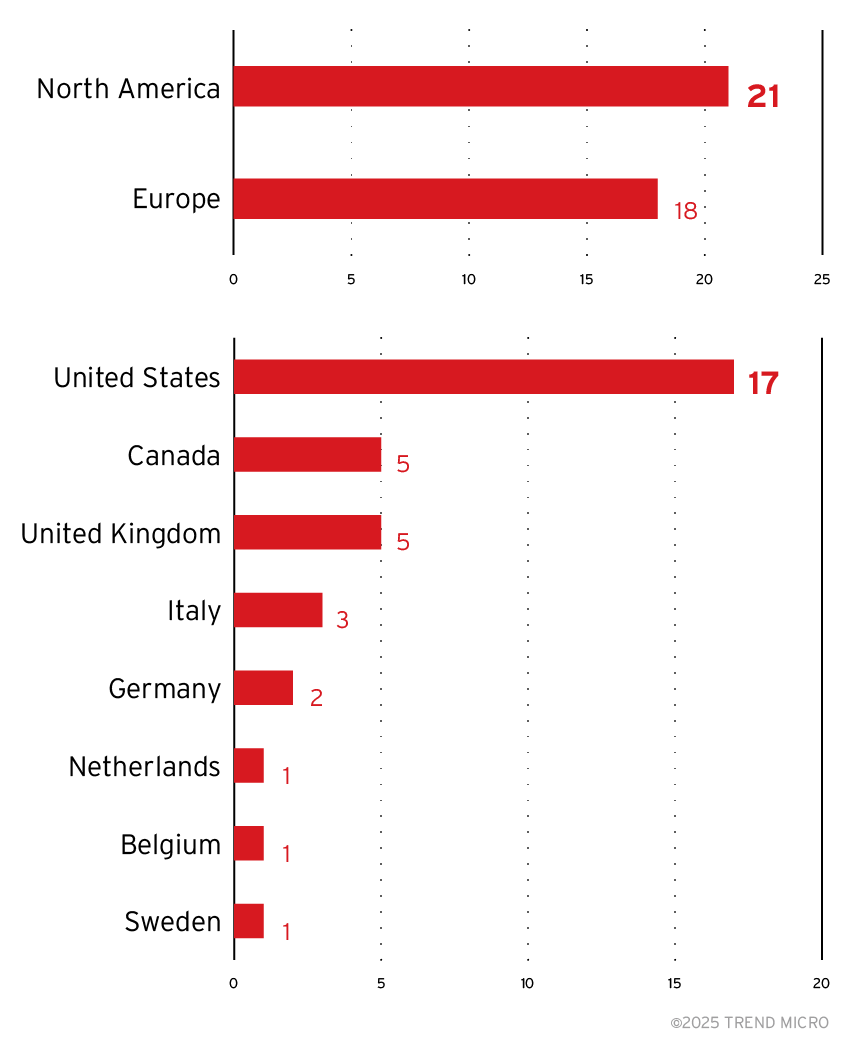
In this blog entry, we explore the tactics employed by the Black Basta and Cactus ransomware groups to compromise systems and exfiltrate sensitive information. They leveraged social engineering, remote access tools, and the BackConnect malware to establish per…

Summary: Cisco’s acquisition of SnapAttack aims to enhance Splunk’s security information and event management (SIEM) platform by incorporating advanced threat detection capabilities leveraging artificial intelligence. SnapAttack’s technology provides real-time visualizations and support for the MITR…
This study offers a comprehensive examination of Advanced Persistent Threats (APTs), focusing on their dynamics, techniques employed, and preventive measures. The article discusses the identification of APTs, the reasons behind attacks on Turkey, and their geo…

Security operations teams are overwhelmed by a surge in cyber threats, necessitating a smarter approach rather than simply increasing manpower. The evolution of generative and agentic AI, particularly multi-agent systems, is set to transform how security opera…
The 2024 Darktrace Threat Report provides a comprehensive analysis of emerging cyber threats, attack campaigns, and vulnerabilities encountered over the year. It highlights evolving tactics like edge device evasion, Ransomware-as-a-Service, and targeted exploitation of critical infrastructure, offering vital insights for cybersecurity professionals. #OperationLunarPeek #RansomHub
Major cybersecurity vendors, including Dragos, publish comprehensive annual reports detailing threats, attack techniques, and industry trends in OT/ICS security. These reports typically include key statistics, threat actor profiles, malware analyses, and strategic recommendations to improve resilience across critical infrastructure sectors. #OTSecurity, #ICS, #ThreatIntelligence, #CyberThreats, #Vulnerabilities, #Malware, #Ransomware, #GeopoliticalRisks
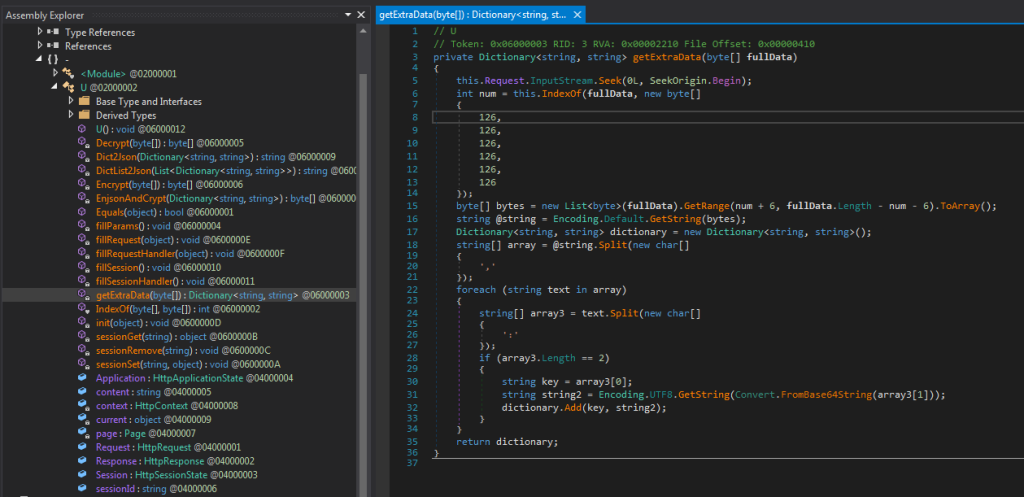
This article details a SOC investigation uncovering a sophisticated web shell employed by Chinese-speaking threat actors. The analysis reveals the web shell’s capabilities as a lightweight exploitation framework and outlines practical detection strategies for …
https://github.com/jivoi/awesome-osint A curated list of amazingly awesome open source intelligence tools and resources. Open-source intelligence (OSINT) is intelligence collected from publicly available sources. In the intelligence community (IC), the term “open” refers to overt, publicly…
https://github.com/notthehiddenwiki/NTHW/tree/nthw There are already 2853 links on our wiki! 💥 Intro We believe that knowledge should be free! So we collected many valuable links from various specialists in their fields and created this wiki. Regardless of whether you are just starting your adv…

This article concludes the “Linux Persistence Detection Engineering” series by exploring advanced persistence mechanisms in Linux. Key topics include manipulation of GRUB and initramfs for persistence, exploitation of PolicyKit (Polkit) permissions, D-Bus conf…

This article discusses the ongoing cyber warfare between Russia and Ukraine, highlighting various attacks perpetrated by both sides against government entities, military targets, and human resources. It details significant events, cyber techniques, and implica…
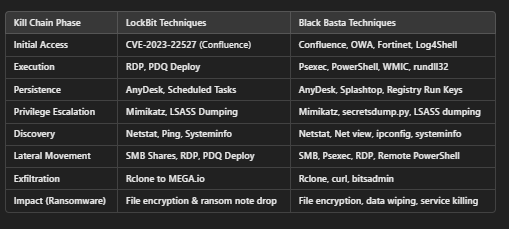
This article analyzes the tactics, techniques, and procedures (TTPs) of the LockBit and Black Basta ransomware groups, specifically focusing on their exploitation of Confluence software. Their similarities and differences are explored, along with methods for d…