The Lotus Blossom, also known as Lotus Panda, is a sophisticated Chinese APT group involved in cyber espionage for over a decade. They have recently enhanced their tactics by deploying new Sagerunex backdoor variants that utilize third-party cloud services and…
Tag: THREAT HUNTING

This article describes a lab project focused on detecting obfuscated PowerShell attacks using Sysmon, Winlogbeat, and the ELK stack. It highlights the challenges presented by attackers utilizing PowerShell and command-line obfuscation, aiming to provide defend…
A sophisticated phishing attack targeting security researcher Troy Hunt on March 25, 2025, successfully compromised his Mailchimp account. The attack was reportedly linked to the group Scattered Spider, employing methods such as social engineering and DNS pivo…

This report reveals a sophisticated malware campaign targeting YouTube creators through spearphishing, utilizing the Clickflix technique to deceive victims into executing malicious scripts. Attackers leverage brand impersonation and exploit interest in profess…
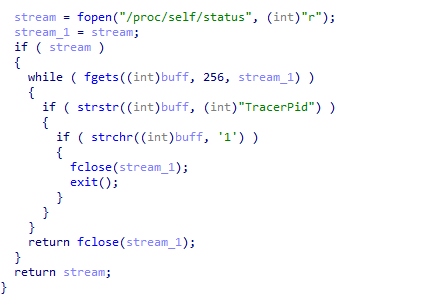
GorillaBot is a newly discovered Mirai-based botnet known for launching over 300,000 attacks in more than 100 countries. This botnet employs sophisticated evasion techniques and secure communication methods with its command-and-control servers. It presents a s…
The Lumma Stealer malware has been observed targeting U.S. State, Local, Tribal, and Territorial (SLTT) government organizations through fake CAPTCHA verification pages that trick users into executing malicious PowerShell scripts. This malware, available as a …
This article outlines a method for tracking malicious infrastructure through proactive threat hunting. It emphasizes starting with an IP address to unveil links to malware delivery via domains and certificates, leading to better detection of adversary command-…
A newly identified malware named “문서열람 인증 앱” (Document Viewing Authentication App), linked to a North Korean-backed APT group, has been detected. This malicious application poses as a legitimate document viewing tool but is designed to perform keylogging and i…
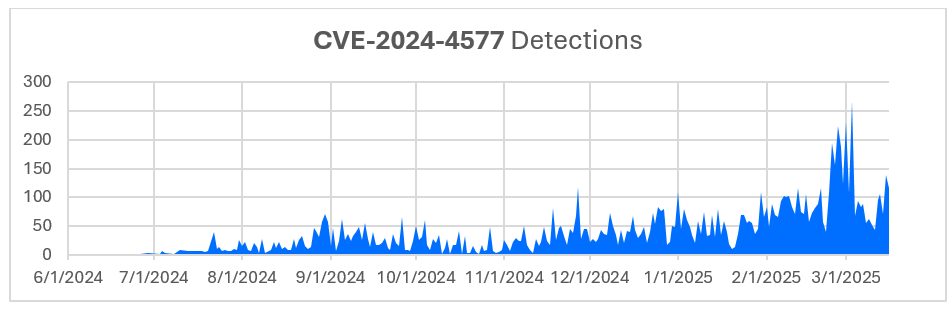
In June 2024, Bitdefender Labs highlighted a critical security vulnerability (CVE-2024-4577) in PHP affecting Windows systems in CGI mode, allowing remote code execution through manipulated character encoding. This vulnerability has seen an increase in exploit…
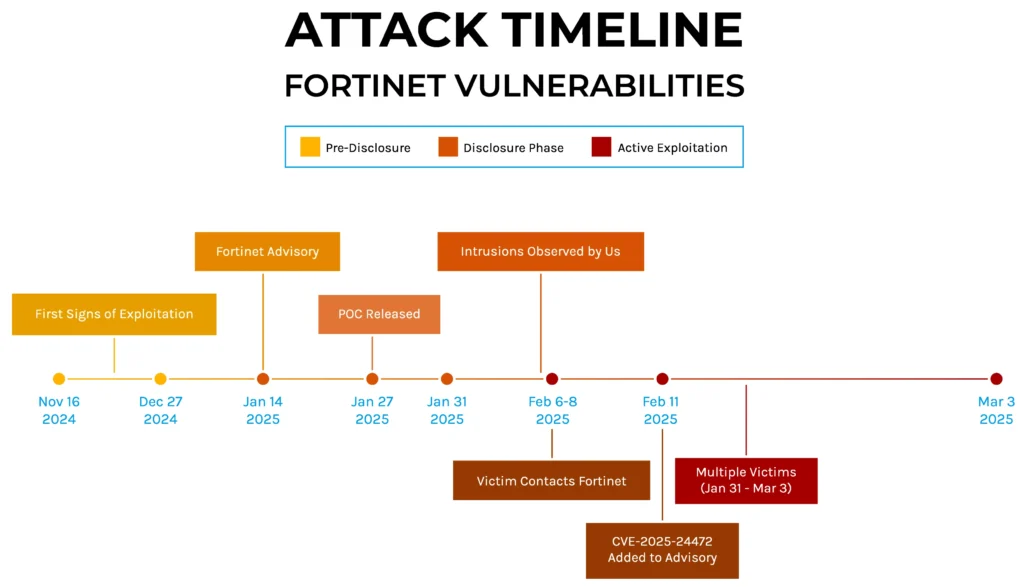
Forescout Research has identified a new ransomware strain, dubbed SuperBlack, linked to the threat actor “Mora_001”, exploiting vulnerabilities in Fortinet devices. This threat actor is connected to the LockBit ransomware ecosystem and demonstrates sophisticat…
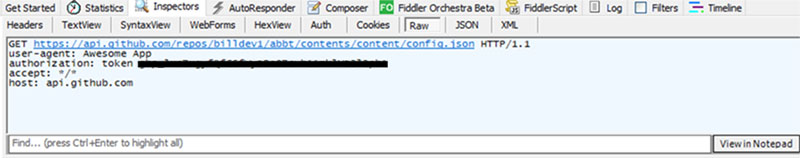
Trend Research has identified new versions of the Albabat ransomware targeting Windows, Linux, and macOS platforms. The group is utilizing GitHub to facilitate their ransomware operations. Organizations are advised to enhance security protocols and implement p…
The CrowdStrike 2025 Global Threat Report analyzes the evolving cyber threat landscape in 2024, highlighting the rise of enterprise-like adversaries, rapid attack techniques, and the use of artificial intelligence by threat actors. It emphasizes the importance of proactive, AI-driven defenses to counter sophisticated cyber threats globally. #Cybersecurity #ThreatLandscape #CrowdStrike #AI #AdversaryTactics

This article discusses a malware that skillfully employs obfuscated VBScript and PowerShell to evade detection and complicate analysis. The attacker uses various obfuscation techniques, including irrelevant comments, time-based delays, and string manipulation,…
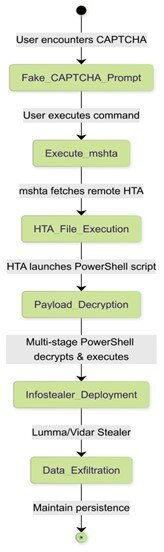
The article discusses a recent investigation by Trustwave SpiderLabs that uncovered a campaign leveraging fake CAPTCHA verifications to execute malicious PowerShell scripts, leading to the deployment of infostealers like Lumma and Vidar. The multi-stage attack…

The article discusses the rise of the Extended Internet of Things (XIoT) and its implications for cybersecurity. As connected devices proliferate, they increase automation and innovation while also expanding the attack surface for potential cyber threats. The …