
OUTLAW is a persistent, auto-propagating coinminer that utilizes simple techniques such as SSH brute-forcing and modification of commodity miners for infection and persistence. By deploying a honeypot, researchers gained insights into how OUTLAW operates, reve…
Tag: THREAT HUNTING

In recent spear-phishing attempts, the Konni APT has impersonated South Korean government entities such as the National Human Rights Commission and the National Police Agency to instigate fear of human rights violations and hacking incidents. The attacks utili…
Summary: The video discusses an interview with Rob Allen, Chief Product Officer at ThreatLocker, focusing on the integration of AI in security products and the challenges in the cybersecurity landscape. It addresses recent vulnerabilities in Microsoft systems and various security updates required to…
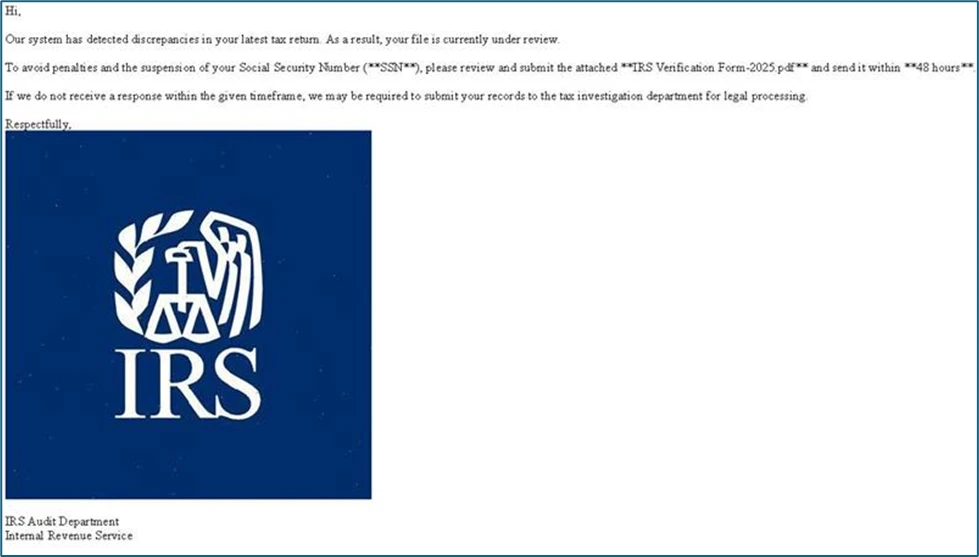
As the tax season approaches in the U.S., Microsoft has noted an increase in phishing campaigns using tax-related themes to steal sensitive information and deploy malware. These campaigns exploit various techniques, including URL shorteners, QR codes, and legi…
The article discusses a malware analysis report linking the Mustang Panda/Red Delta threat actor to various cyber espionage activities targeting governmental and non-governmental organizations across multiple countries since 2014. Through the analysis, several…
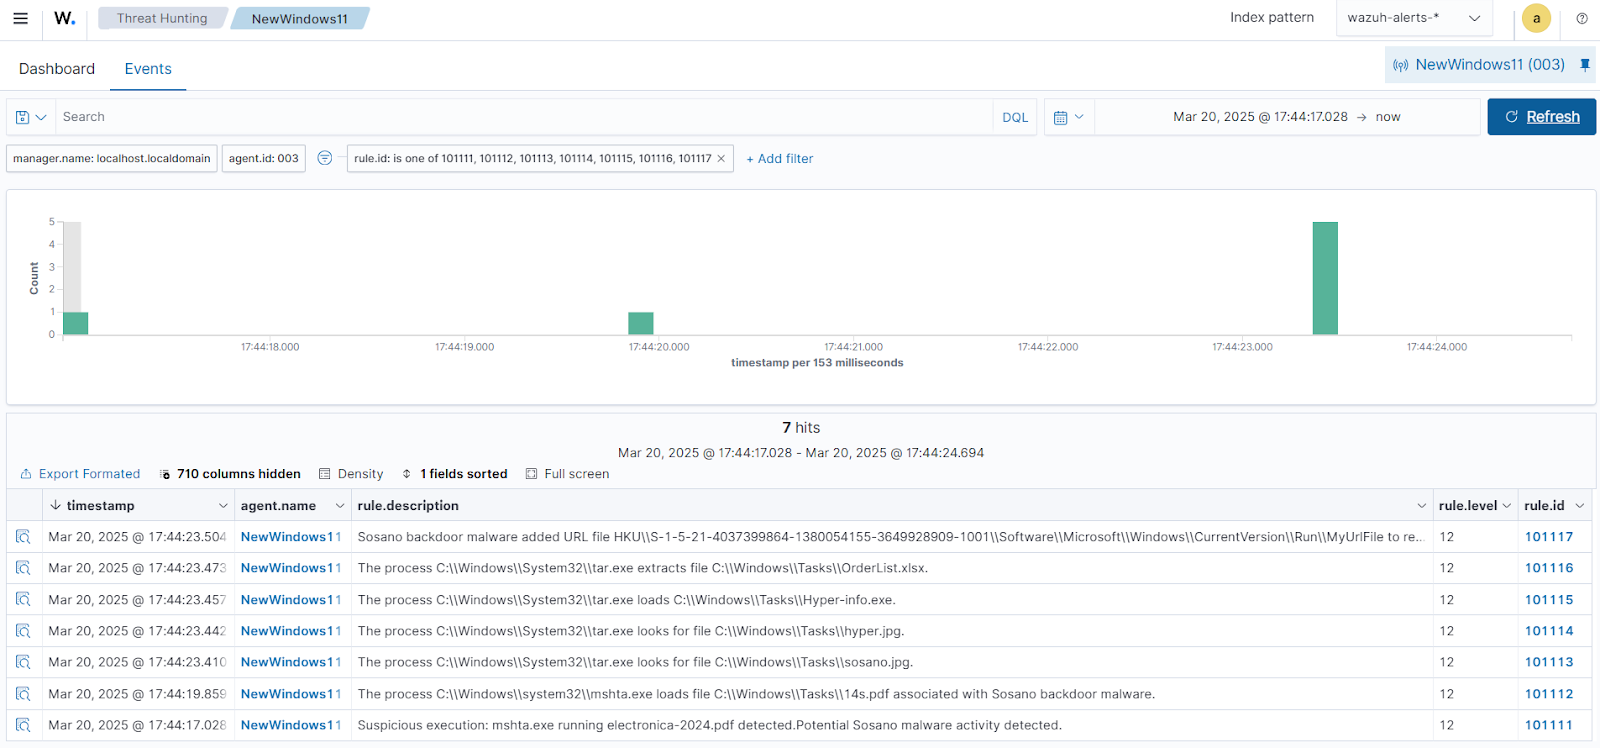
The Sosano backdoor is a sophisticated malware strain targeting critical sectors using polyglot files and spear-phishing via compromised email accounts. This article details how to detect and remove Sosano on Windows endpoints using Sysmon integration and customized Wazuh rules with Active Response automation. #Sosano #INDICEMSElectronics #Wazuh…
This content explores the significance of Cyber Threat Intelligence (CTI) in improving organizational security and understanding the threat landscape. It delves into the motivations of various types of threat actors, their tactics, and how to effectively mitig…
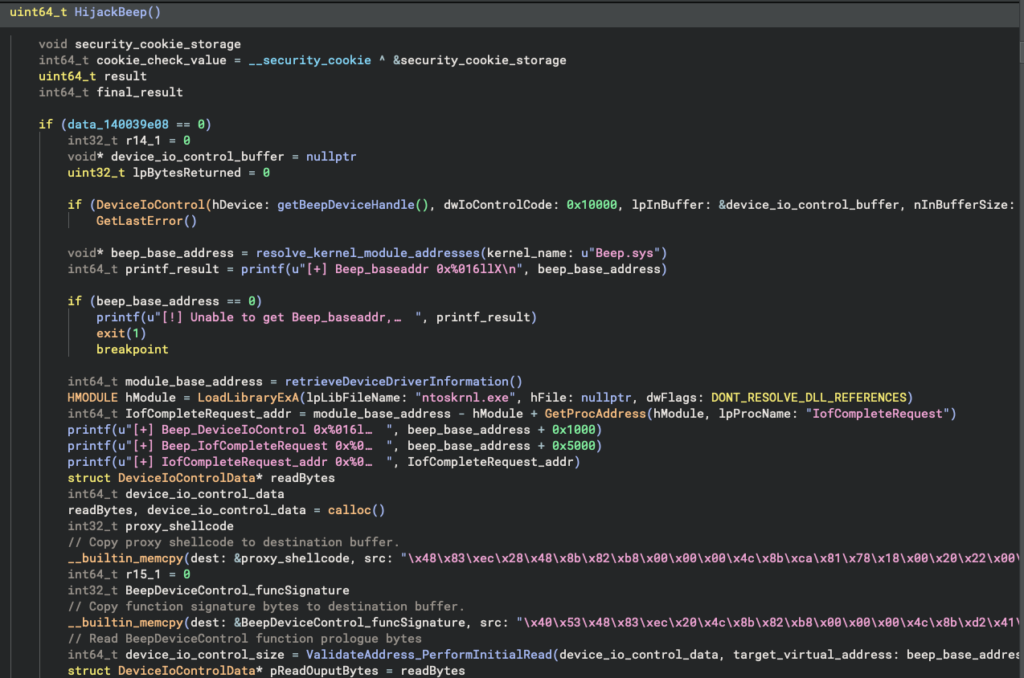
The article discusses a sophisticated ransomware attack involving Qilin ransomware, which utilizes the technique of bring-your-own-vulnerable-driver (BYOVD) to bypass traditional Endpoint Detection and Response (EDR) measures. The analysis uncovers the exploit…
ClickFix is a deceptive delivery method exploiting user interactions and clipboard functionalities to initiate malware execution. This technique has gained popularity among cybercriminals for malware deployment, including credential theft. Vigilance against su…
Summary: Many organizations face significant gaps between their expected and actual security control effectiveness, often realizing these deficiencies only after a breach occurs. Current traditional testing methods are inadequate for truly validating security measures, leading to blind spots that ma…
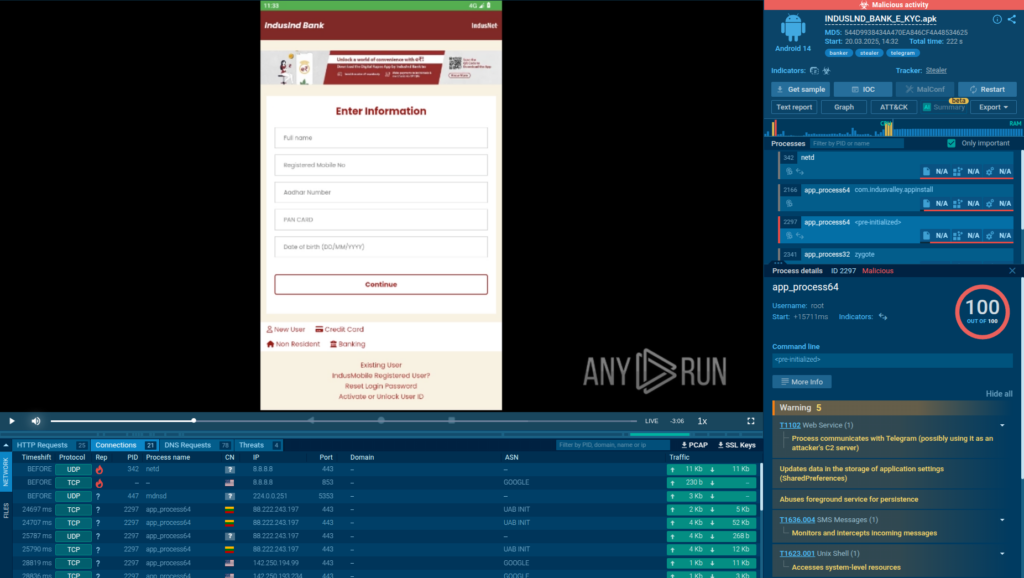
The report discusses Salvador Stealer, a new Android malware posing as a banking application to steal sensitive user data, such as banking credentials and personal information. The malware employs phishing techniques and has multiple methods for exfiltrating d…

Summary: Threat actors are aggressively probing Palo Alto Networks GlobalProtect secure remote access instances, with over 24,000 unique IP addresses engaged in login scans, signaling a potential exploitation of vulnerabilities. The activity peaked between March 17 and March 26, primarily originatin…
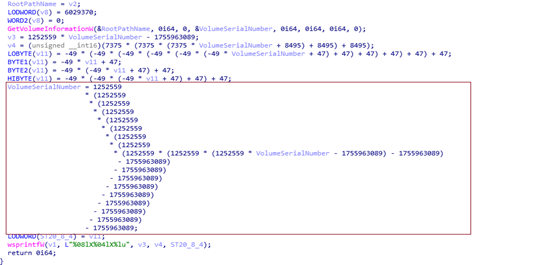
SvcStealer 2025 is a sophisticated information-stealing malware delivered through spear phishing emails. It captures sensitive data from victims, including credentials and cryptocurrency wallet information, and sends it to a command and control (C2) server. Wi…

The article provides a detailed analysis of ValleyRAT, a remote access Trojan used by the Silver Fox threat organization. The malware employs various techniques, including deploying both a Trojan and a decoy PDF, to deceive victims while establishing a connect…
Summary: The video discusses an upcoming online cyber security conference called Continuum con, which offers hands-on workshops focused on blue team cyber security defense. Unlike traditional conferences filled with dull presentations, attendees will actively engage in practical exercises across var…