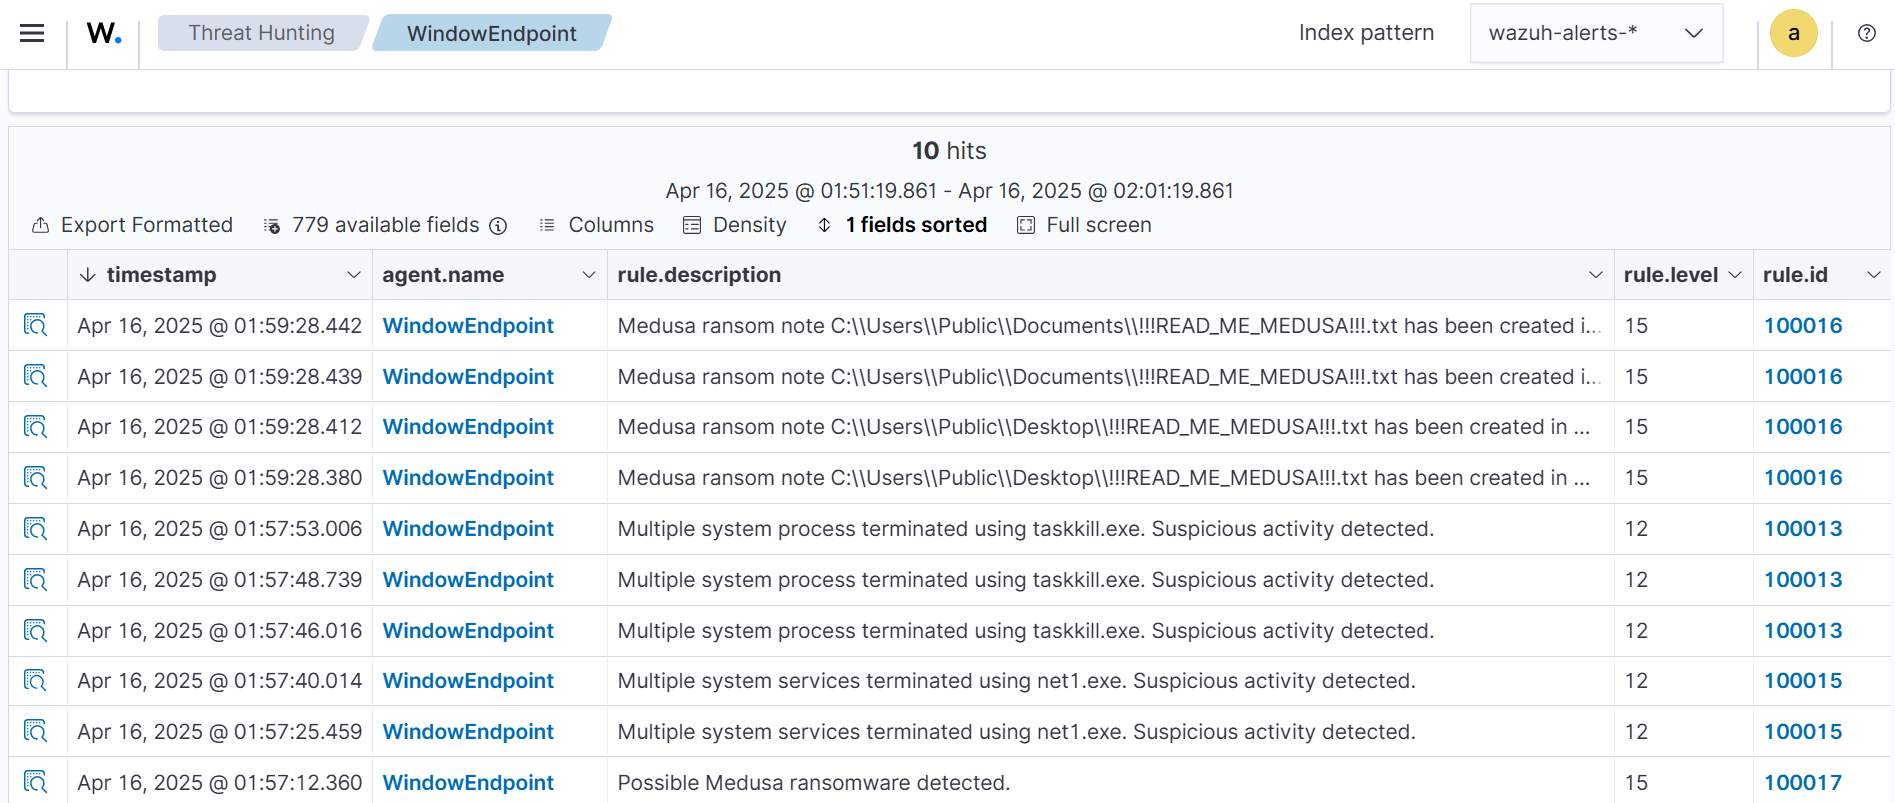
Medusa ransomware, a ransomware-as-a-service first seen in 2021, targets Windows systems mainly through phishing and exploiting unpatched vulnerabilities, causing significant disruption across multiple sectors. This article explains how to detect and respond to Medusa ransomware using Wazuh’s monitoring, detection rules, and YARA integration for proactive removal. #Medusa #Wazuh #YARA…
Tag: THREAT HUNTING

Microsoft Defender XDR is a comprehensive cybersecurity solution that integrates data from various sources to improve threat detection, response times, and forensic investigations. It offers a unified platform that enhances security across endpoints, identitie…
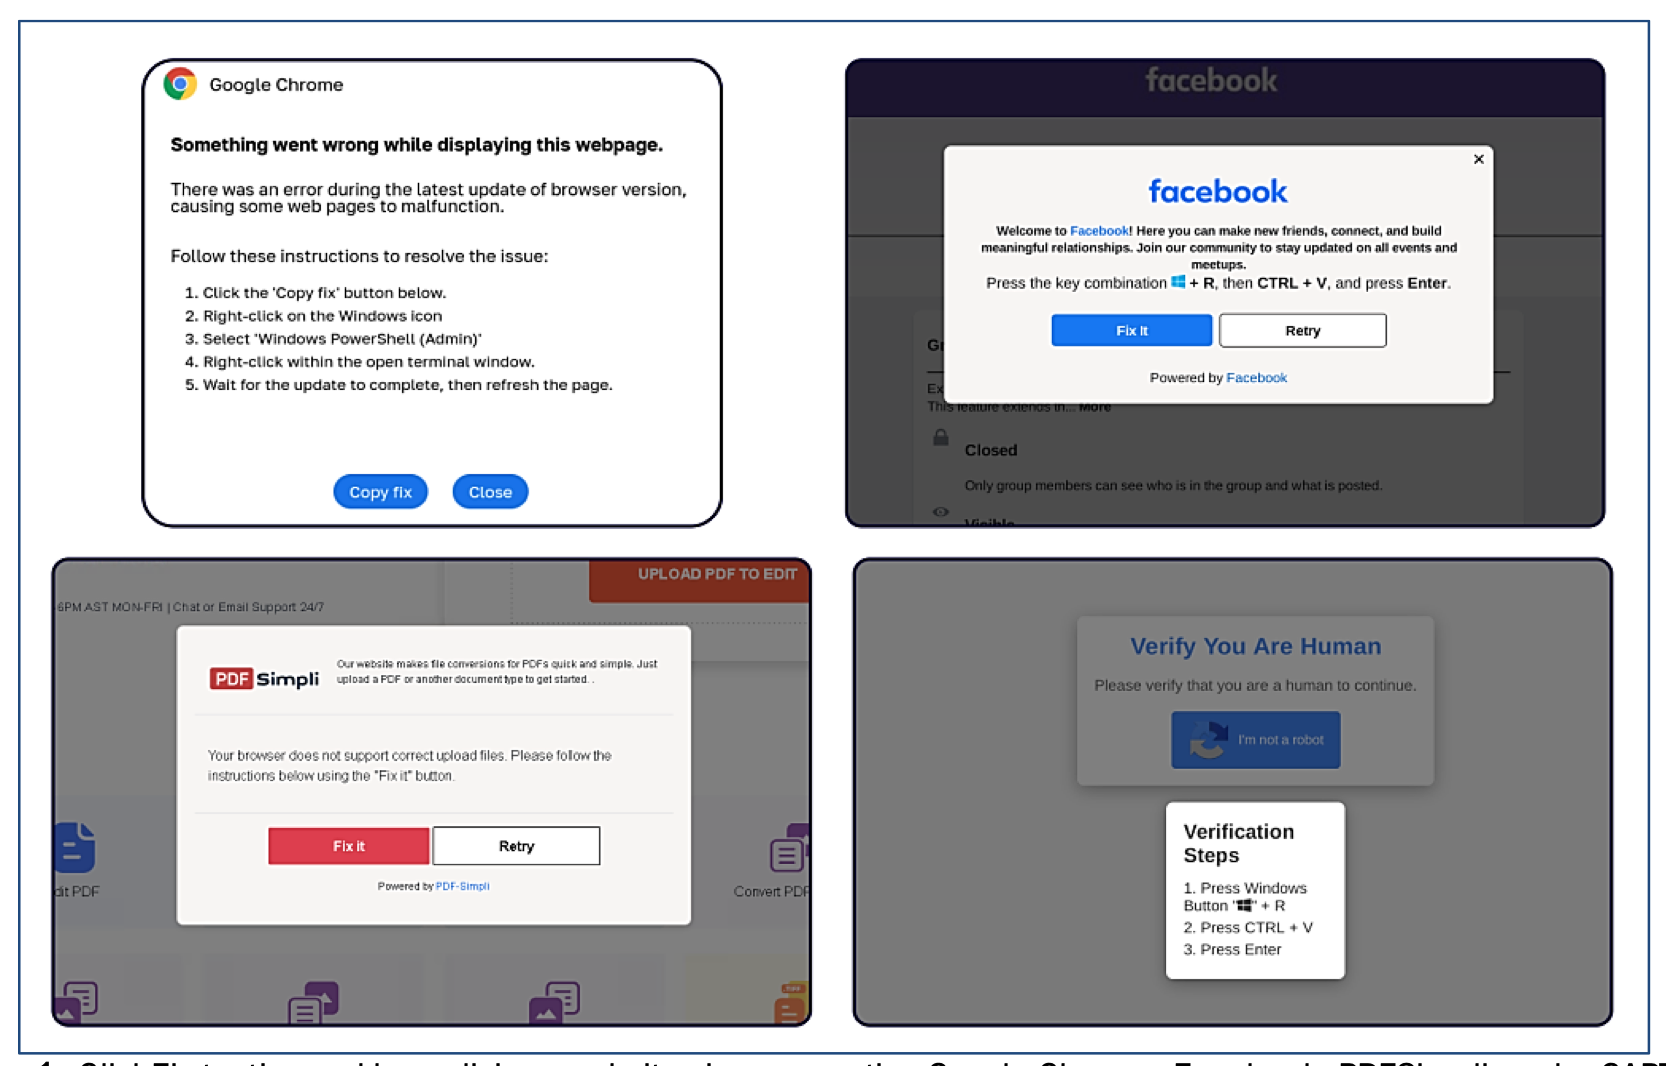
This article discusses the ClickFix technique used by adversaries to deliver malware, particularly highlighting its association with the Lumma Stealer. The ClickFix method involves social engineering, tricking users into executing malicious commands through se…

Kubernetes has rapidly transitioned to a widely adopted tool for managing containerized applications, with 66% of users deploying it in production. However, security challenges persist, leading to project delays and revenue losses for many organizations. The u…

Summary: Exaforce, a startup from San Francisco, has raised million in Series A funding to enhance security operations centers (SOCs) using AI technology. The company is introducing AI agents called “Exabots” to significantly reduce manual tasks and improve accuracy in threat detection. Founded by i…
This article discusses the limitations of YARA signatures for .NET assemblies that rely solely on strings and explores enhanced detection methodologies, including the use of IL code, method signatures, and specific custom attributes. The piece emphasizes the i…
This report from Datadog highlights significant threats to cloud infrastructure and software supply chain security noted in Q1 2025. Key trends include the increased attention of threat actors on the cloud control plane, continued prevalence of Business Email …

The article analyzes leaked communications from the Black Basta ransomware group, revealing their ongoing operations despite exposure. Significant tactics such as hybrid infrastructure exploitation and social engineering are highlighted. Microsoft Threat Intel…
The MysterySnail RAT, linked to the IronHusky APT threat actor, has resurfaced after years of inactivity. Initially discovered in 2021, recent reports show its deployment in government organizations in Mongolia and Russia, alongside a new variant called Myster…
This article discusses how investigators used Validin UI to trace related infrastructure linked to a malicious ClickFix campaign, which included a phishing site impersonating Booking.com. The investigation revealed numerous domains, IPs, and indicators of comp…
Summary: The video discusses the top five free SOC analyst trainings for beginners, covering simulation training, cyber range platforms, beginner learning courses, and project guides to enhance resumes. Each training resource offers valuable hands-on experience and foundational knowledge for those p…
This content reviews the highlights and key findings from the 2025 Red Report by Picus Labs, focusing on the most common cybersecurity techniques and evolving threats such as infostealers, multi-stage attacks, and advanced evasion methods. It emphasizes the importance of proactive, layered security strategies and highlights recent trends in malware behavior and threat actor tactics. #Cybersecurity #MITREATT&CK #ThreatIntelligence #Infostealers #AdvancedPersistentThreats

Threat actors are increasingly exploiting Remote Monitoring and Management (RMM) software to conduct sophisticated cyberattacks, using tools like AnyDesk, Atera Agent, and MeshAgent for unauthorized access, data exfiltration, and persistence in compromised net…

Credential theft via phishing remains a significant threat to enterprises, particularly through tactics involving cloned login pages and PHP-based phishing kits. Recent campaigns have targeted employee portals, employing advanced techniques to obscure maliciou…
Summary: The video discusses the insights shared by Edna Johnson, a cybersecurity engineer and community volunteer, on their journey into the cybersecurity field, their experience with various organizations and events, and advice for newcomers in the industry. Edna emphasizes the importance of volun…