In Q1 2025, the Top 10 Malware list showed slight changes, with SocGholish continuing its lead for the seventh consecutive quarter. This JavaScript downloader accounted for 48% of detections and poses significant risks by enabling further exploitation. New ent…
Tag: THREAT HUNTING
The article explores the evolving landscape of cybersecurity influenced by Artificial Intelligence (AI). It highlights how AI is used by both attackers and security professionals, detailing the dual-edged nature of its capabilities—from enhancing breaches thro…

Summary: The 2025 RSA Conference in San Francisco is showcasing hundreds of companies announcing innovative cybersecurity products and services. Key highlights include advancements in AI-driven security solutions, new compliance initiatives, and enhanced threat intelligence capabilities. The Securit…

Summary: Ukraine is currently experiencing an evolved form of cyber warfare where digital attacks are integrated with kinetic military actions. A recent report from CERT-UA reveals a substantial increase in cyber incidents alongside a troubling shift towards more sophisticated and coordinated attack…
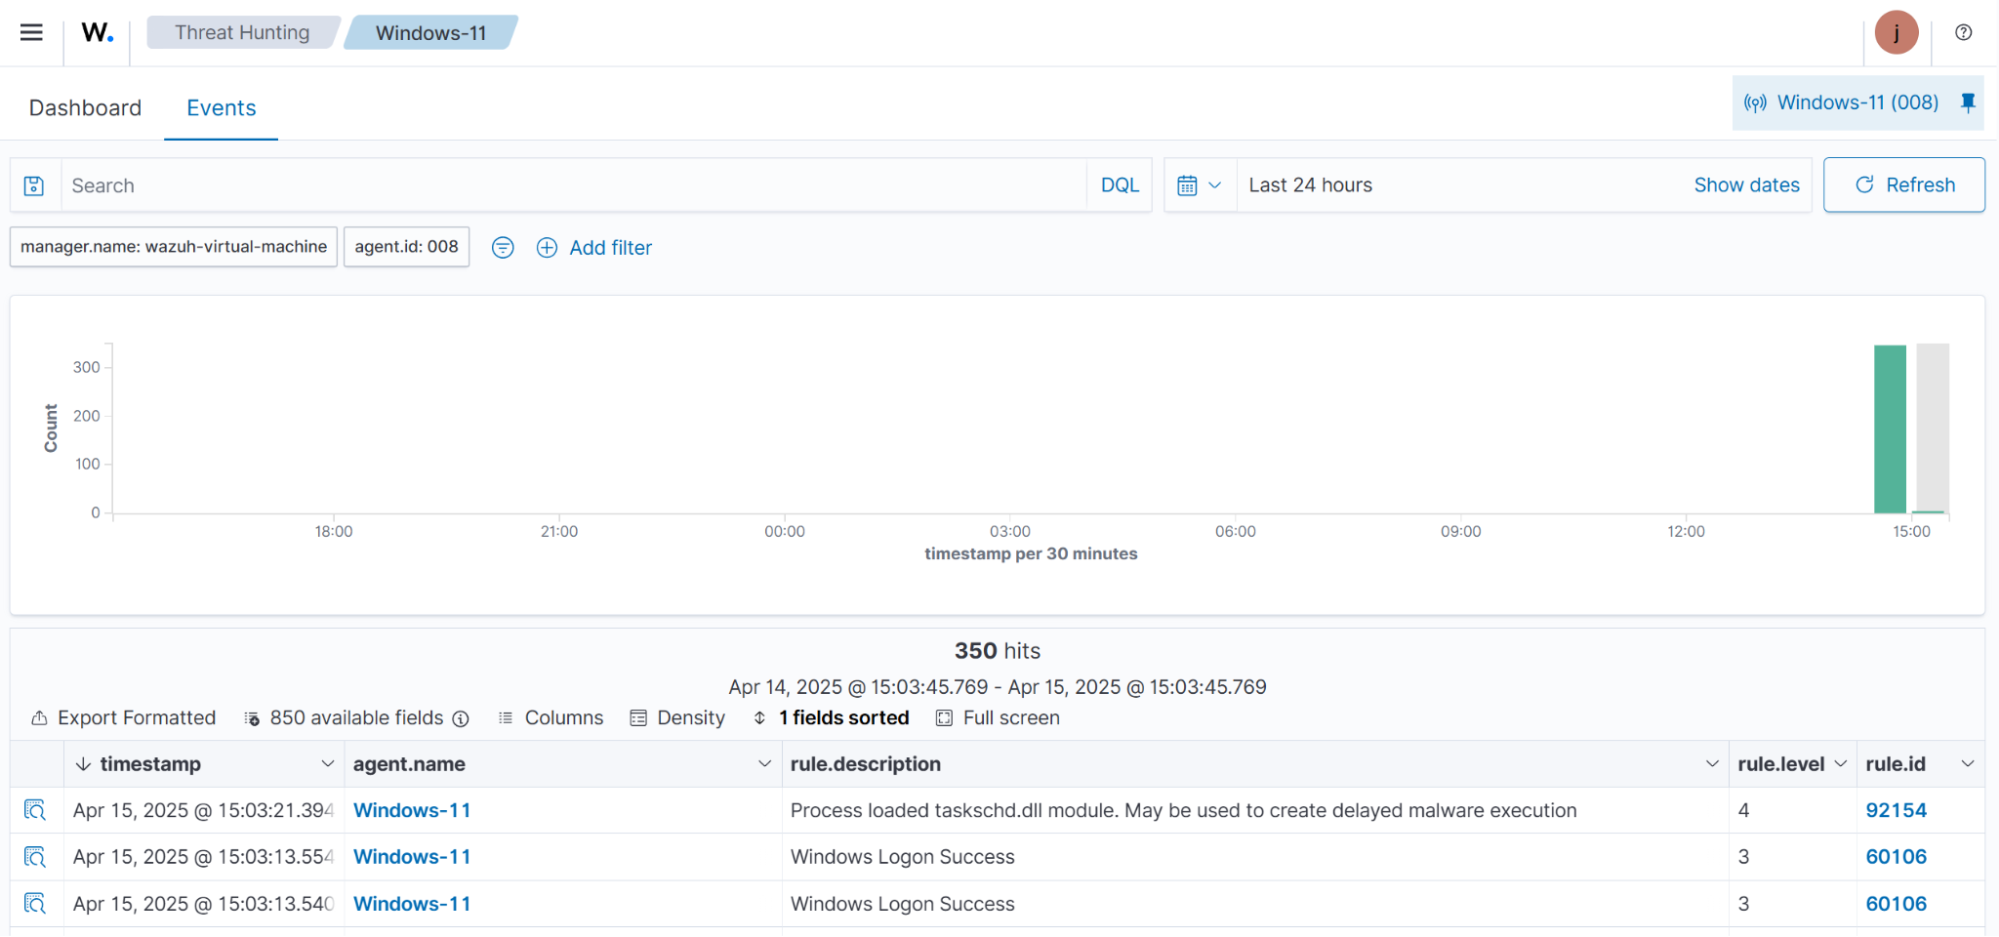
Attackers use various persistence techniques on Windows endpoints to maintain access even after system interruptions, involving scheduled tasks, user account manipulation, service modifications, and registry changes. This article explains how Wazuh detects those persistence methods using Sysmon integration, log analysis, and file integrity monitoring. #Wazuh #Sysmon #MITRE_ATT&CK #WindowsPersistence…

Trustwave SpiderLabs has identified a resurgence of malicious campaigns exploiting deceptive CAPTCHA verifications to deploy NodeJS-based backdoors and Remote Access Trojans (RATs), demonstrating a significant increase in these tactics across several malware c…
MintsLoader is a sophisticated malicious loader first detected in 2024, frequently employed by various threat groups, notably TAG-124, to deliver secondary payloads including GhostWeaver and StealC. The malware utilizes multi-stage infection techniques, evasio…
This month’s threat report highlights the activities of the financially motivated threat actor EncryptHub, detailing their use of ransomware, exploits sales, and advanced malware development in collaboration with tools like ChatGPT. Additionally, the leak from…
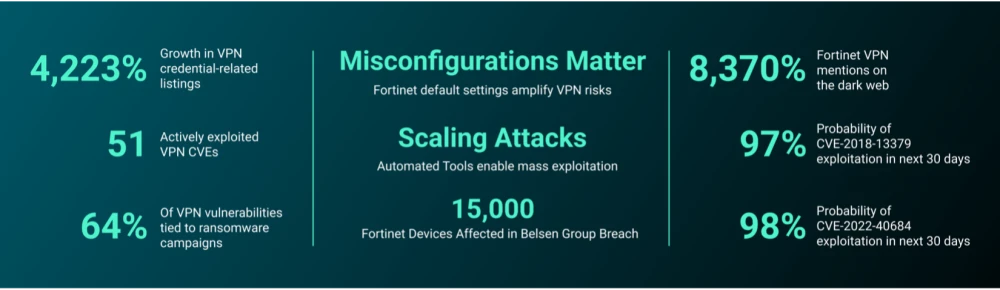
The report discusses persistent vulnerabilities in VPN infrastructures, specifically CVE-2018-13379 and CVE-2022-40684, which remain critical targets for cybercriminals and state-sponsored actors. The analysis highlights a surge in discussions about Fortinet V…

Summary: The RSA Conference 2025 in San Francisco has showcased numerous product and service announcements from various cybersecurity companies. Highlights include innovative AI solutions for employee security training, identity vulnerability management, and threat detection. This digest encapsulate…

eSentire’s Threat Response Unit (TRU) has identified a surge in Tycoon 2FA Phishing-as-a-Service (PhaaS) cases, marking a significant evolution in phishing tactics targeting Microsoft 365 and Gmail accounts. The report discusses sophisticated evasion technique…
This article provides an in-depth look at effective Threat Hunting strategies, including various types of hunts (Intel Driven, Hypothesis Driven, and Data Driven) and their respective execution cadences. It emphasizes the importance of transitioning from hunt …

LummaC2 is an evolving piece of malware designed for information theft, particularly targeting crypto wallets and sensitive user data. It has adopted advanced obfuscation techniques and exploitations of recent vulnerabilities to evade detection. Its modular ar…

This project illustrates the simulation of a malicious insider threat, exploiting Windows server vulnerabilities through the SMB protocol to deliver backdoor malware. Utilizing automation in incident response, the objective is to detect, contain, and eradicate…

Summary: A new malware strain named DslogdRAT has been identified in attacks targeting Ivanti Connect Secure VPN devices, utilizing a basic Perl web shell for initial access. Researchers uncovered its sophisticated design, allowing for remote command execution and evasion techniques, alongside anoth…