ANY.RUN reports that phishing kits are increasingly hosted on legitimate cloud and CDN platforms (Cloudflare, Microsoft Azure, Google Firebase, AWS), allowing attackers to hide malicious infrastructure behind trusted services and evade traditional detection. This trend — driven by kits like Tycoon2FA, Sneaky2FA, and EvilProxy and techniques such as AiTM and reverse-proxying…
Tag: THREAT HUNTING

The 2025 State of Detection Engineering at Elastic summarizes detection engineering work from October 2023 to October 2024, covering real-world incident responses, rule development lifecycles, CI/Detections-as-Code practices, and extensive telemetry and integration enhancements across endpoint, cloud, and SaaS platforms. Key highlights include rapid coverage for the CUPS RCE disclosures, detection and analysis of activity group REF6138 and a DPRK malicious NPM campaign, expansion of kernel and macOS telemetry, an AWS CloudTrail/Okta rule audit (50+ tunings, 40+ new rules, 17 hunting queries), and operational metrics such as processing 500+ malware samples/day with a 99% detection goal. #CUPS #CVE-2024-47076 #REF6138 #ElasticDefend #AWSCloudTrail #Okta #ScatteredSpider #Panix #SWAT #DEBMM #ElasticSecurityLabs #NPM #DPRK

A Farsi-speaking threat actor aligned with Iranian state interests has been linked to RedKitten, a campaign that uses Farsi-named XLSM spreadsheets with malicious VBA macros to drop a C# implant via AppDomainManager injection and deploy the SloppyMIO backdoor. SloppyMIO retrieves steganographic configuration from GitHub and Google Drive, uses the Telegram Bot…
SentinelOne and Censys uncovered roughly 175,000 exposed Ollama hosts worldwide, many operating without authentication, monitoring, or safety guardrails, with 23,000 hosts driving most activity across 130 countries and 4,032 ASNs. About half of these hosts could execute code and access APIs, enabling low-cost abuse for spam, phishing, disinformation, prompt injection, and…
Aisy has launched from stealth with $2.3 million in seed funding to deliver an AI-assisted platform that helps security teams manage and prioritize overwhelming volumes of vulnerability alert tickets. It maps systems from an attacker’s perspective and chains related alerts to surface the most critical issues for remediation while using AI…
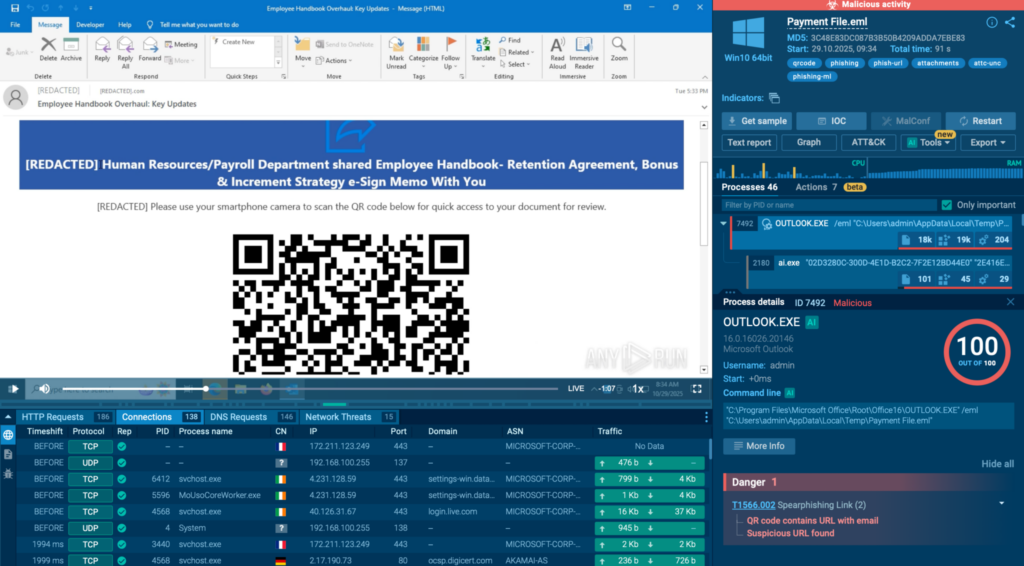
Attackers compromised a contractor’s mailbox and hijacked an active executive approval thread to deliver a phishing link that led through multi-step redirects and Cloudflare Turnstile gates to an EvilProxy AiTM Microsoft credential‑theft page. ANY.RUN researchers detonated the message in a sandbox, revealed the full execution chain, and linked the incident to…
IClickFix is a widespread malicious JavaScript framework that has been injected into over 3,800 compromised WordPress sites since at least December 2024 to display a fake Cloudflare Turnstile (ClickFix) lure and deliver downstream payloads. The framework uses a YOURLS-based Traffic Distribution System, multi-stage obfuscated JavaScript, and clipboard-based social engineering to install NetSupport RAT via a PowerShell dropper. #IClickFix #NetSupportRAT
Russian and Chinese state-backed groups and financially motivated actors have been exploiting CVE-2025-8088 in WinRAR to drop malware into Windows Startup folders using a path traversal vulnerability combined with Alternate Data Streams. The flaw remained widely abused months after RARLAB released WinRAR 7.13, with actors like UNC4895 (RomCom), APT44 (FROZENBARENTS), Turla,…
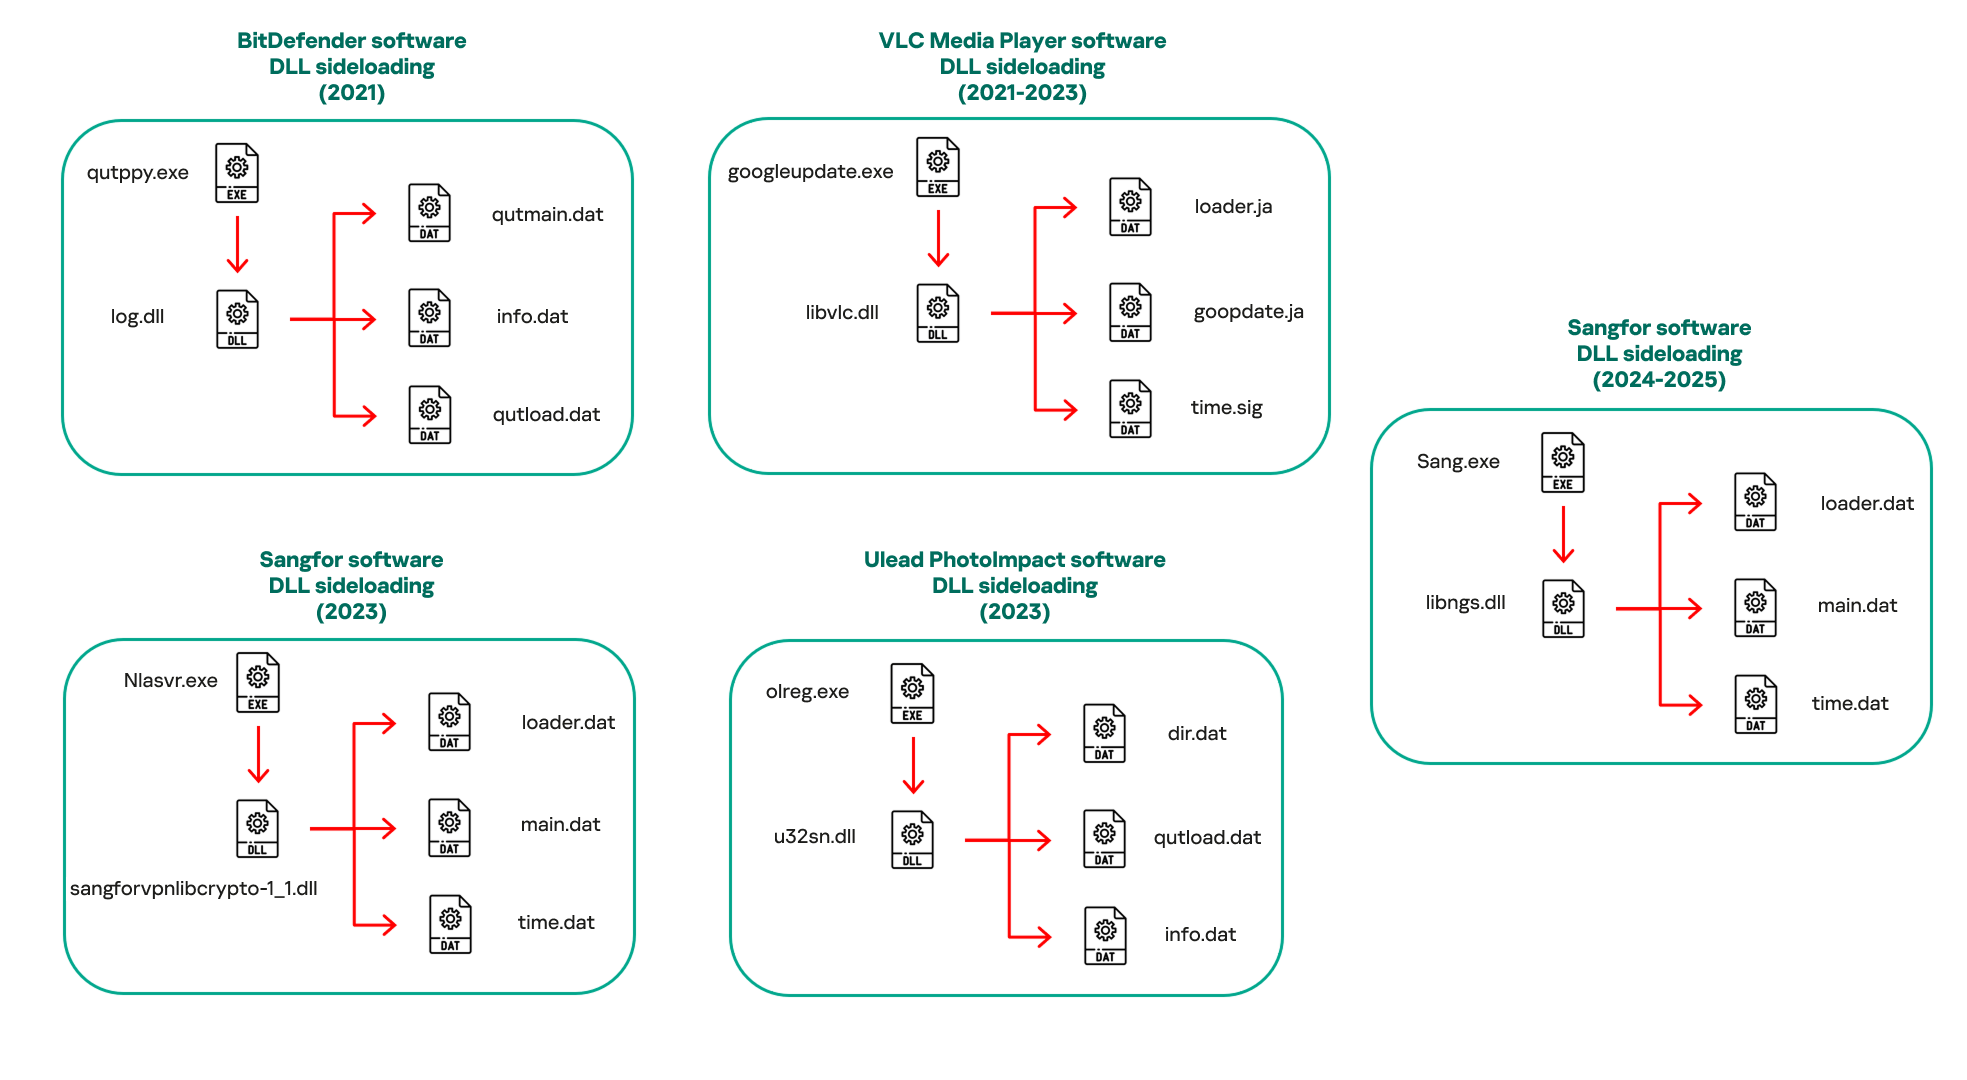
HoneyMyte (aka Mustang Panda/Bronze President) continues active espionage across Southeast Asia and Europe in 2025, deploying an updated toolset that includes an enhanced CoolClient backdoor, browser credential stealers, USB worms, PlugX, ToneShell, QReverse and multiple data-theft scripts. The report details CoolClient’s DLL sideloading execution flow, new features such as clipboard monitoring and an HTTP proxy credential sniffer, and multiple exfiltration channels including FTP, Pixeldrain and Google Drive. #HoneyMyte #CoolClient
Offensive security and red teaming are shifting from periodic exercises to continuous, AI-augmented programs that combine automation, threat intelligence, and human expertise to find and fix vulnerabilities faster. This evolution includes hybrid in-house and external models, greater collaboration with blue teams, and an urgent focus on combating AI-enhanced social engineering. #Bugcrowd…
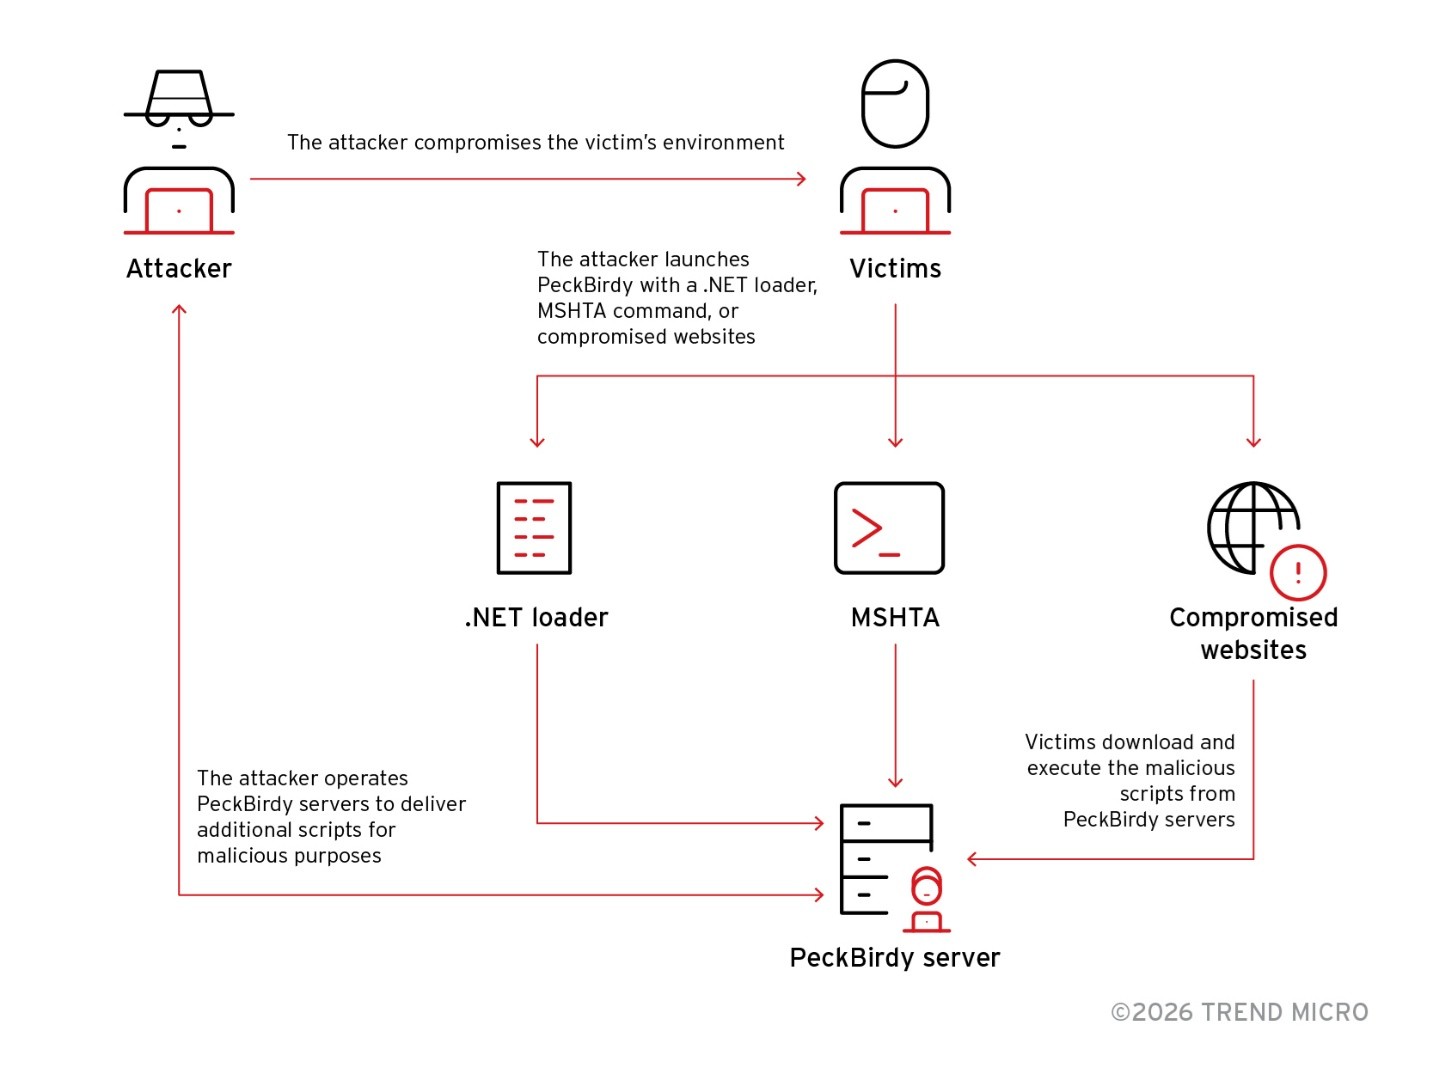
PeckBirdy: A Versatile Script Framework for LOLBins Exploitation Used by China-aligned Threat Groups
PeckBirdy is a versatile JScript-based command-and-control framework used by China-aligned APT groups since 2023 to abuse LOLBins and deliver modular backdoors across browsers, MSHTA, WScript, Classic ASP, NodeJS and .NET environments. Related campaigns SHADOW-VOID-044 and SHADOW-EARTH-045 deployed backdoors such as HOLODONUT and MKDOOR, used watering‑hole and phishing lures, exploited CVE-2020-16040, and…
Comcast Business’s 2025 Threat Report analyzes 34.6 billion events (including 19.5B botnet resource-development events, 9.7B drive-by compromises, 4.7B phishing attempts, and 44,069 DDoS events) to map evolving attacker tactics such as proxy abuse, living-off-the-land techniques, and AI-enabled social engineering. It urges organizations to adopt multi-layered, AI-augmented defenses—prioritizing patching, phishing-resistant MFA, proactive threat hunting, and managed 24/7 SOC services—to reduce exposure and build enterprise resilience. #SocGholish #ComcastBusiness
A new campaign combines the ClickFix social-engineering method, a fake CAPTCHA prompt, and a signed Microsoft App-V script that proxies PowerShell execution to deliver the Amatera infostealer. The attack uses user-pasted Run commands, Google Calendar-based configuration, LSB steganography in PNGs hosted on public CDNs, and in-memory PowerShell stages to load shellcode while stalling in analysis environments. #Amatera #ClickFix
BravoX is a newly observed Ransomware-as-a-Service operation that publicly surfaced on January 23, 2026 after posting a Tor address on the RAMP forum and launching a TOR-based data leak site. The operation currently lists three alleged U.S. victims (two healthcare, one retail) and is advertising a selective affiliate model to scale its activities. #BravoX #RAMP
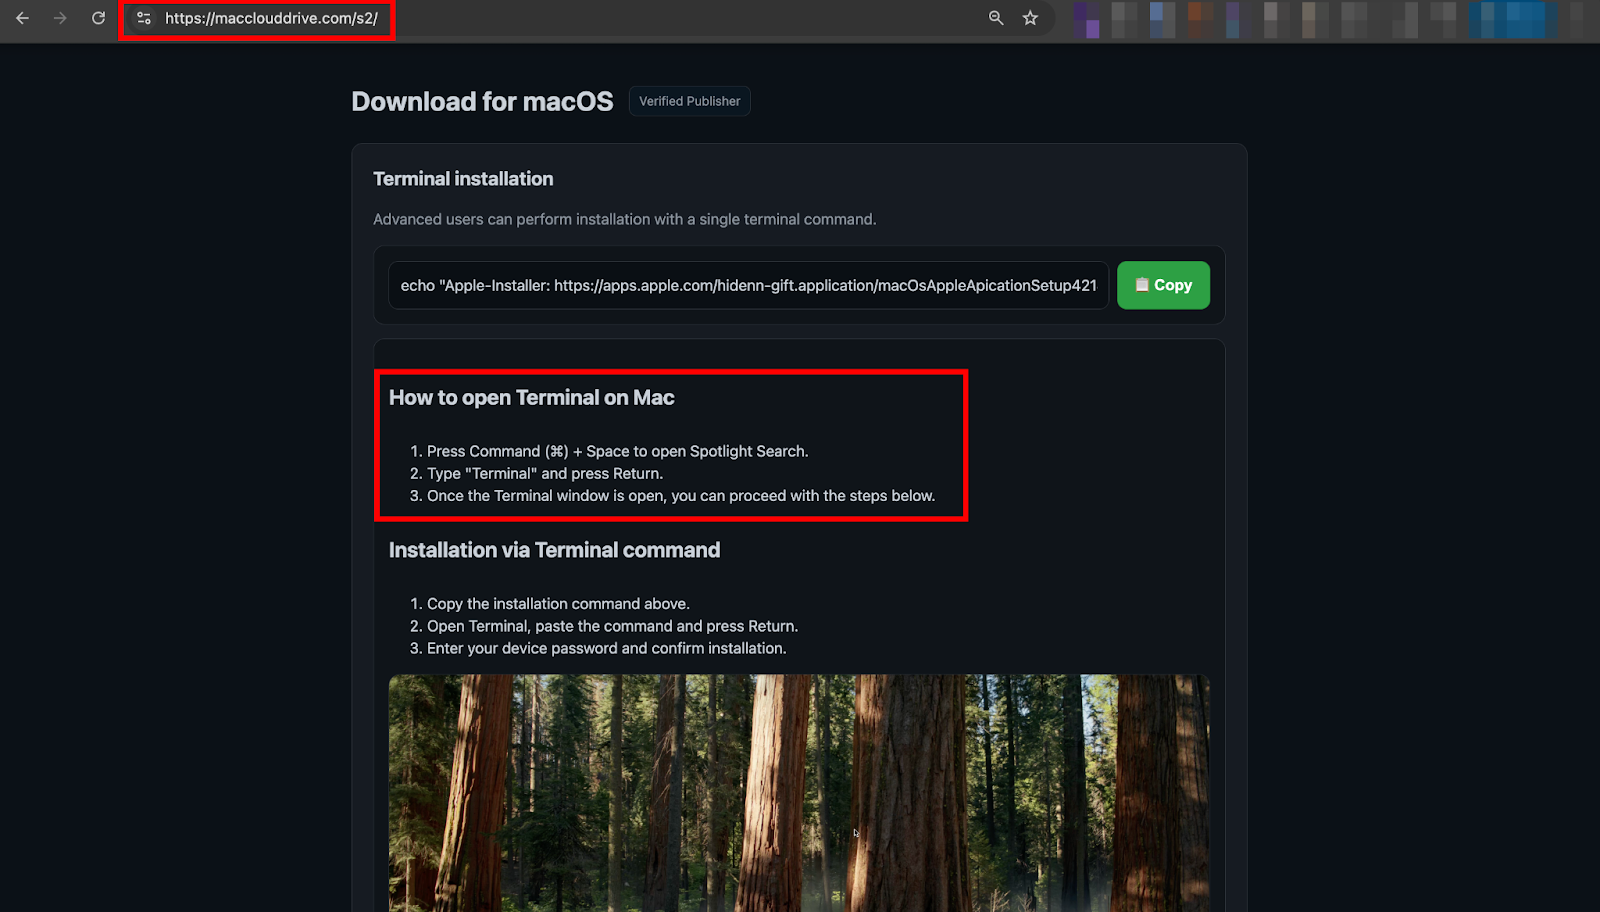
Researchers discovered a ClickFix-style macOS lure (macclouddrive.com/s2) that tricks users into pasting a Terminal one-liner which downloads a daemonized Zsh stager that executes a remote AppleScript to harvest browser credentials, Keychain data, crypto wallets, and other sensitive files. The campaign uses the MacSync infostealer with rotating jmpbowl.* C2 domains and conditionally trojanizes Electron wallet apps (Ledger Wallet.app, Trezor Suite.app) to capture PINs and recovery phrases for long-term phishing. #MacSync #jmpbowl