A new Android spyware called ClayRat is masquerading as popular apps and targeting Russian users through various malicious channels. It can perform extensive surveillance and data theft activities, and efforts are ongoing to block its spread. #ClayRat #AndroidSpyware
Tag: SPYWARE

A new Android spyware campaign called ClayRat is actively targeting users in Russia by impersonating popular apps and using malicious links and websites. The malware can exfiltrate sensitive data, control device functions, and propagate itself through contacts, making it a significant surveillance threat. #ClayRat #AndroidSpyware #C2Servers…
A group claiming ties to known hacking collectives has announced the theft of data from dozens of Salesforce customers, threatening to leak sensitive records unless paid a ransom. The hackers, including members of Lapsus$, Scattered Spider, and ShinyHunters, targeted major organizations like Disney, Toyota, and Google. #Lapsus$ #ScatteredSpider #ShinyHunters #SalesforceDataLeakage #ExtortionCampaign…

Cybersecurity Threat Research ‘Weekly’ Recap. The update covers ongoing abuse across Messaging & Social Platforms, including WhatsApp/Android trojans, fake groups targeting seniors, SMS smishing, and AI-generated clone sites harvesting PII. It also highlights ransomware and extortion trends (Yurei, FunkLocker, BQTLock), notable APTs and long-term intrusions (Phantom Taurus, Confucius, Goffee, Lunar Spider, Scattered Lapsus$ Hunters, Lazarus), malware distribution & infrastructure abuse (WordPress malvertising, Detour Dog, WARMCOOKIE, Rhadamanthys, ClickFix, XiebroC2), Linux threats (Koske, FlipSwitch), and threat intel/detection tooling guidance (YARA hunting, intel ops best practices).

Daily Recap, The article covers extortion and ransomware activities (Scattered Spider/LAPSUS$ threaten Salesforce, Toyota, Disney, Google; Cl0p-Oracle extortion linked to patched vulnerabilities and FIN11) alongside data breach incidents (Discord third-party breach; Renault UK; Shamir Medical Center). It also highlights actor activity and evolving malware campaigns (Detour Dog with Strela Stealer; Rhadamanthys MaaS; Confucius Group’s AnonDoor), plus notable vulnerabilities and privacy issues (Palo Alto Network scans; Splunk flaws; DrayTek CVE-2025-10547; ALPR surveillance debates) and industry responses (Signal SPQR; Oneleet funding). #ScatteredSpider #LAPSUS$ #Cl0p #FIN11 #DiscordData #RenaultUK #ShamirAttack #DetourDog #StrelaStealer #Rhadamanthys #AnonDoor #ConfuciusGroup #PaloAlto #Splunk #DrayTek #ALPR #FlockRaven #Signal #SPQR #Oneleet
Daily Recap, The day’s recap covers extortion campaigns tied to Oracle data theft, notable APT activity like Confucius shifting to AnonDoor, and new ransomware incidents impacting brands such as Asahi, with ongoing vulnerability disclosures including Meteobridge, Festo, and DrayTek. It also highlights privacy/legal actions, defense updates, and smishing infrastructure trends shaping the threat landscape. #Clop #FIN11 #ShinyHunters #Lapsus$ #CrimsonCollective #RedHat #Oracle #Asahi #Meteobridge #Festo #DrayTek #Confucius #AnonDoor #CavalryWerewolf #FoalShell #StallionRAT
This cybersecurity roundup covers recent updates from Microsoft, new espionage tactics, and data breaches affecting government agencies and private companies. It highlights emerging threats, innovative defense tools, and measures users can take to protect their digital assets. #MicrosoftSentinel #CitrixBleed…
Daily Recap, Scattered Spider, WestJet, Allianz Life, Motility, RemoteCOM, Red Hat, ENISA, Phantom Taurus, OpenShift AI, WireTap, Datzbro, soopsocks, OneLogin, F‑Droid, Asahi, Brave, Zania, WireTap, Scattered Spider.

European members of parliament are questioning why the EU is funding spyware companies like Intellexa Alliance and Cy4Gate, which have been linked to unlawful surveillance and targeting civil society. This funding raises concerns about transparency, governance, and the impact on democracy, rights, and rule of law. #SpywareFunding #EUBudget #CivilSocietySurveillance…

Attackers created fake Facebook groups targeting active seniors to distribute Android malware posing as event registration apps, sometimes asking for sign-up fees to phish card details. The primary malware observed was the Datzbro trojan (and occasionally the Zombinder dropper), delivered via links or messages and capable of audio/video recording, overlay phishing,…
Researchers have uncovered two new Android spyware campaigns, ProSpy and ToSpy, that use fake app upgrades and impersonation websites to steal sensitive user data. These campaigns target users in the UAE and deploy stealthy, persistent malware with sophisticated data exfiltration techniques. #ProSpy #ToSpy #UAE #AndroidSpyware #SignalFakePlugins
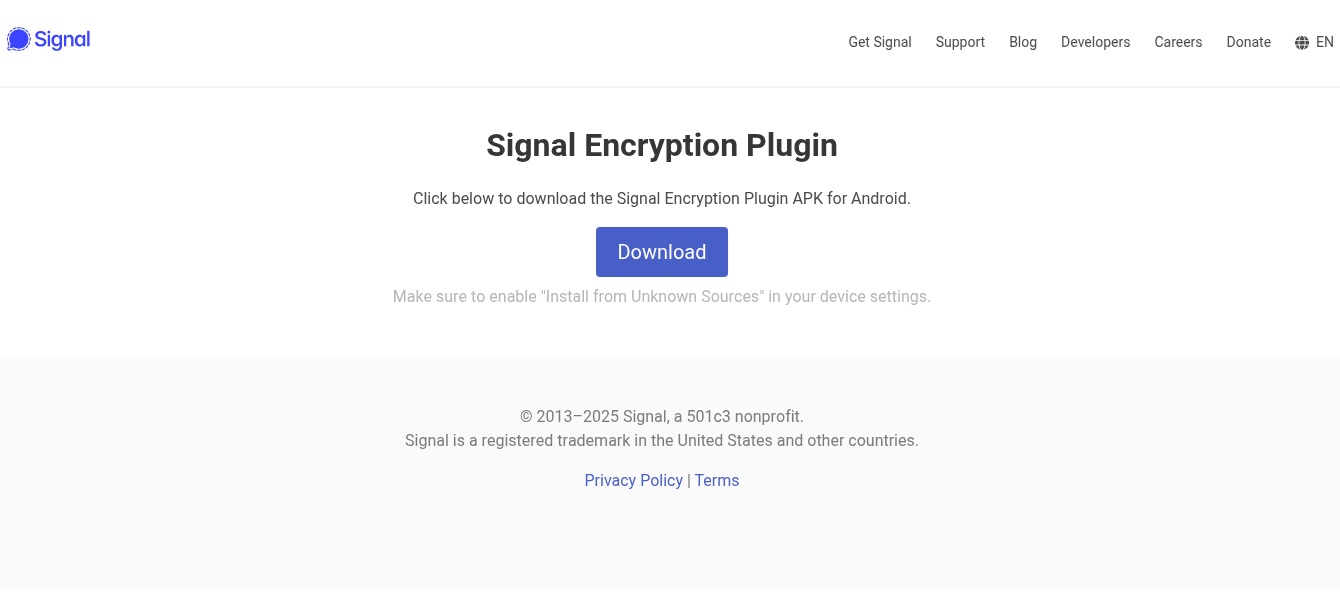
ESET researchers discovered two undocumented Android spyware families—Android/Spy.ProSpy and Android/Spy.ToSpy—that impersonate Signal and ToTok to trick users into manually installing malicious APKs from deceptive websites, with confirmed targeting of users in the United Arab Emirates. Both families persist on devices and exfiltrate sensitive data (including ToTok .ttkmbackup files) to active C2 servers, and known samples/domains and hashes have been shared. #Android/Spy.ProSpy #Android/Spy.ToSpy

Cybersecurity experts have uncovered Android spyware campaigns, ProSpy and ToSpy, that impersonate popular apps like Signal and ToTok to target users in the United Arab Emirates. These malicious apps are distributed through fake websites and social engineering, exfiltrating sensitive data from infected devices. #ToTok #ProSpy…
Cybersecurity researchers have uncovered new Android spyware campaigns, ProSpy and ToSpy, concealed within fake messaging apps targeting users in the United Arab Emirates. These campaigns utilize fake websites and app stores to install persistent spyware capable of stealing sensitive data, with ongoing operations linked to command-and-control servers. #ProSpy #ToSpy #ESET #UAE…

A significant data breach has compromised personal information of nearly 14,000 individuals monitored by RemoteCOM’s SCOUT surveillance software and contact details of law enforcement staff. The leak raises concerns over the security of sensitive surveillance data and the potential threats faced by both monitored persons and officers. #RemoteCOM #SCOUTsoftware…