
SentinelLABS uncovered a sophisticated spearphishing campaign called “PhantomCaptcha” targeting humanitarian and government organizations in Ukraine, involving fake verification pages and weaponized PDFs. The attack utilized multi-stage PowerShell payloads and WebSocket RATs to establish stealthy command and control infrastructure, with overlaps linked to Russian threat clusters like COLDRIVER. #PhantomCaptcha #COLDRIVER…
Tag: SPYWARE

A Polish politician was indicted for allegedly transferring funds illegally to purchase Pegasus spyware used for surveillance. The investigation highlights the widespread use of Pegasus to monitor opposition figures in Poland from 2017 to 2022. #NSOGroup #PegasusSpyware…
A one-day spearphishing campaign targeting Ukrainian officials and humanitarian organizations used fake CAPTCHA prompts to deliver a WebSocket Remote Access Trojan. The attack involved social engineering, fake communications, and malware that exfiltrated sensitive system data, with links to possible Russian threat actor infrastructure. #PhantomCaptcha #ClickFix #ColdRiver

Daily Recap, A critical RCE affects over 75,000 WatchGuard Firebox devices and a Windows SMB vulnerability is being exploited in attacks, with additional bug disclosures and a USB recovery fix. Threat actors and campaigns include Snappybee via Citrix, GlassWorm supply-chain, and COLDRIVER Russian malware families.
#WatchGuard #SMB #Snappybee #GlassWorm #COLDRIVER
Daily Recap, A roundup of vulnerabilities, detection tools, North Korea-linked activity, phishing, SIM fraud, breaches, and geopolitical cyber tension highlights recent patches, clever obfuscation techniques, and ongoing threat campaigns affecting enterprises and users worldwide. Authors emphasize the need for timely patching and vigilant monitoring to counter disclosures like ConnectWise Automate RMM, WatchGuard Fireware, Dolby zero-click, and OAuth-based stealth campaigns. #ConnectWise #WatchGuard #Dolby #Cazadora #MSS #NSA

A U.S. federal court has ordered NSO Group to stop targeting Meta’s WhatsApp with its Pegasus spyware and reduced the damages owed from $168 million to $4 million. The ruling emphasizes that NSO’s spyware illegally circumvents WhatsApp’s end-to-end encryption, potentially setting a precedent for protecting digital infrastructure from surveillance threats. #NSOGroup…
The US District Court has issued a permanent injunction banning NSO Group from hacking WhatsApp and targeting its users, reducing the damages awarded earlier this year. This ruling marks a significant legal victory for WhatsApp in its efforts to prevent unauthorized surveillance and protect user privacy. #NSOGroup #WhatsApp…
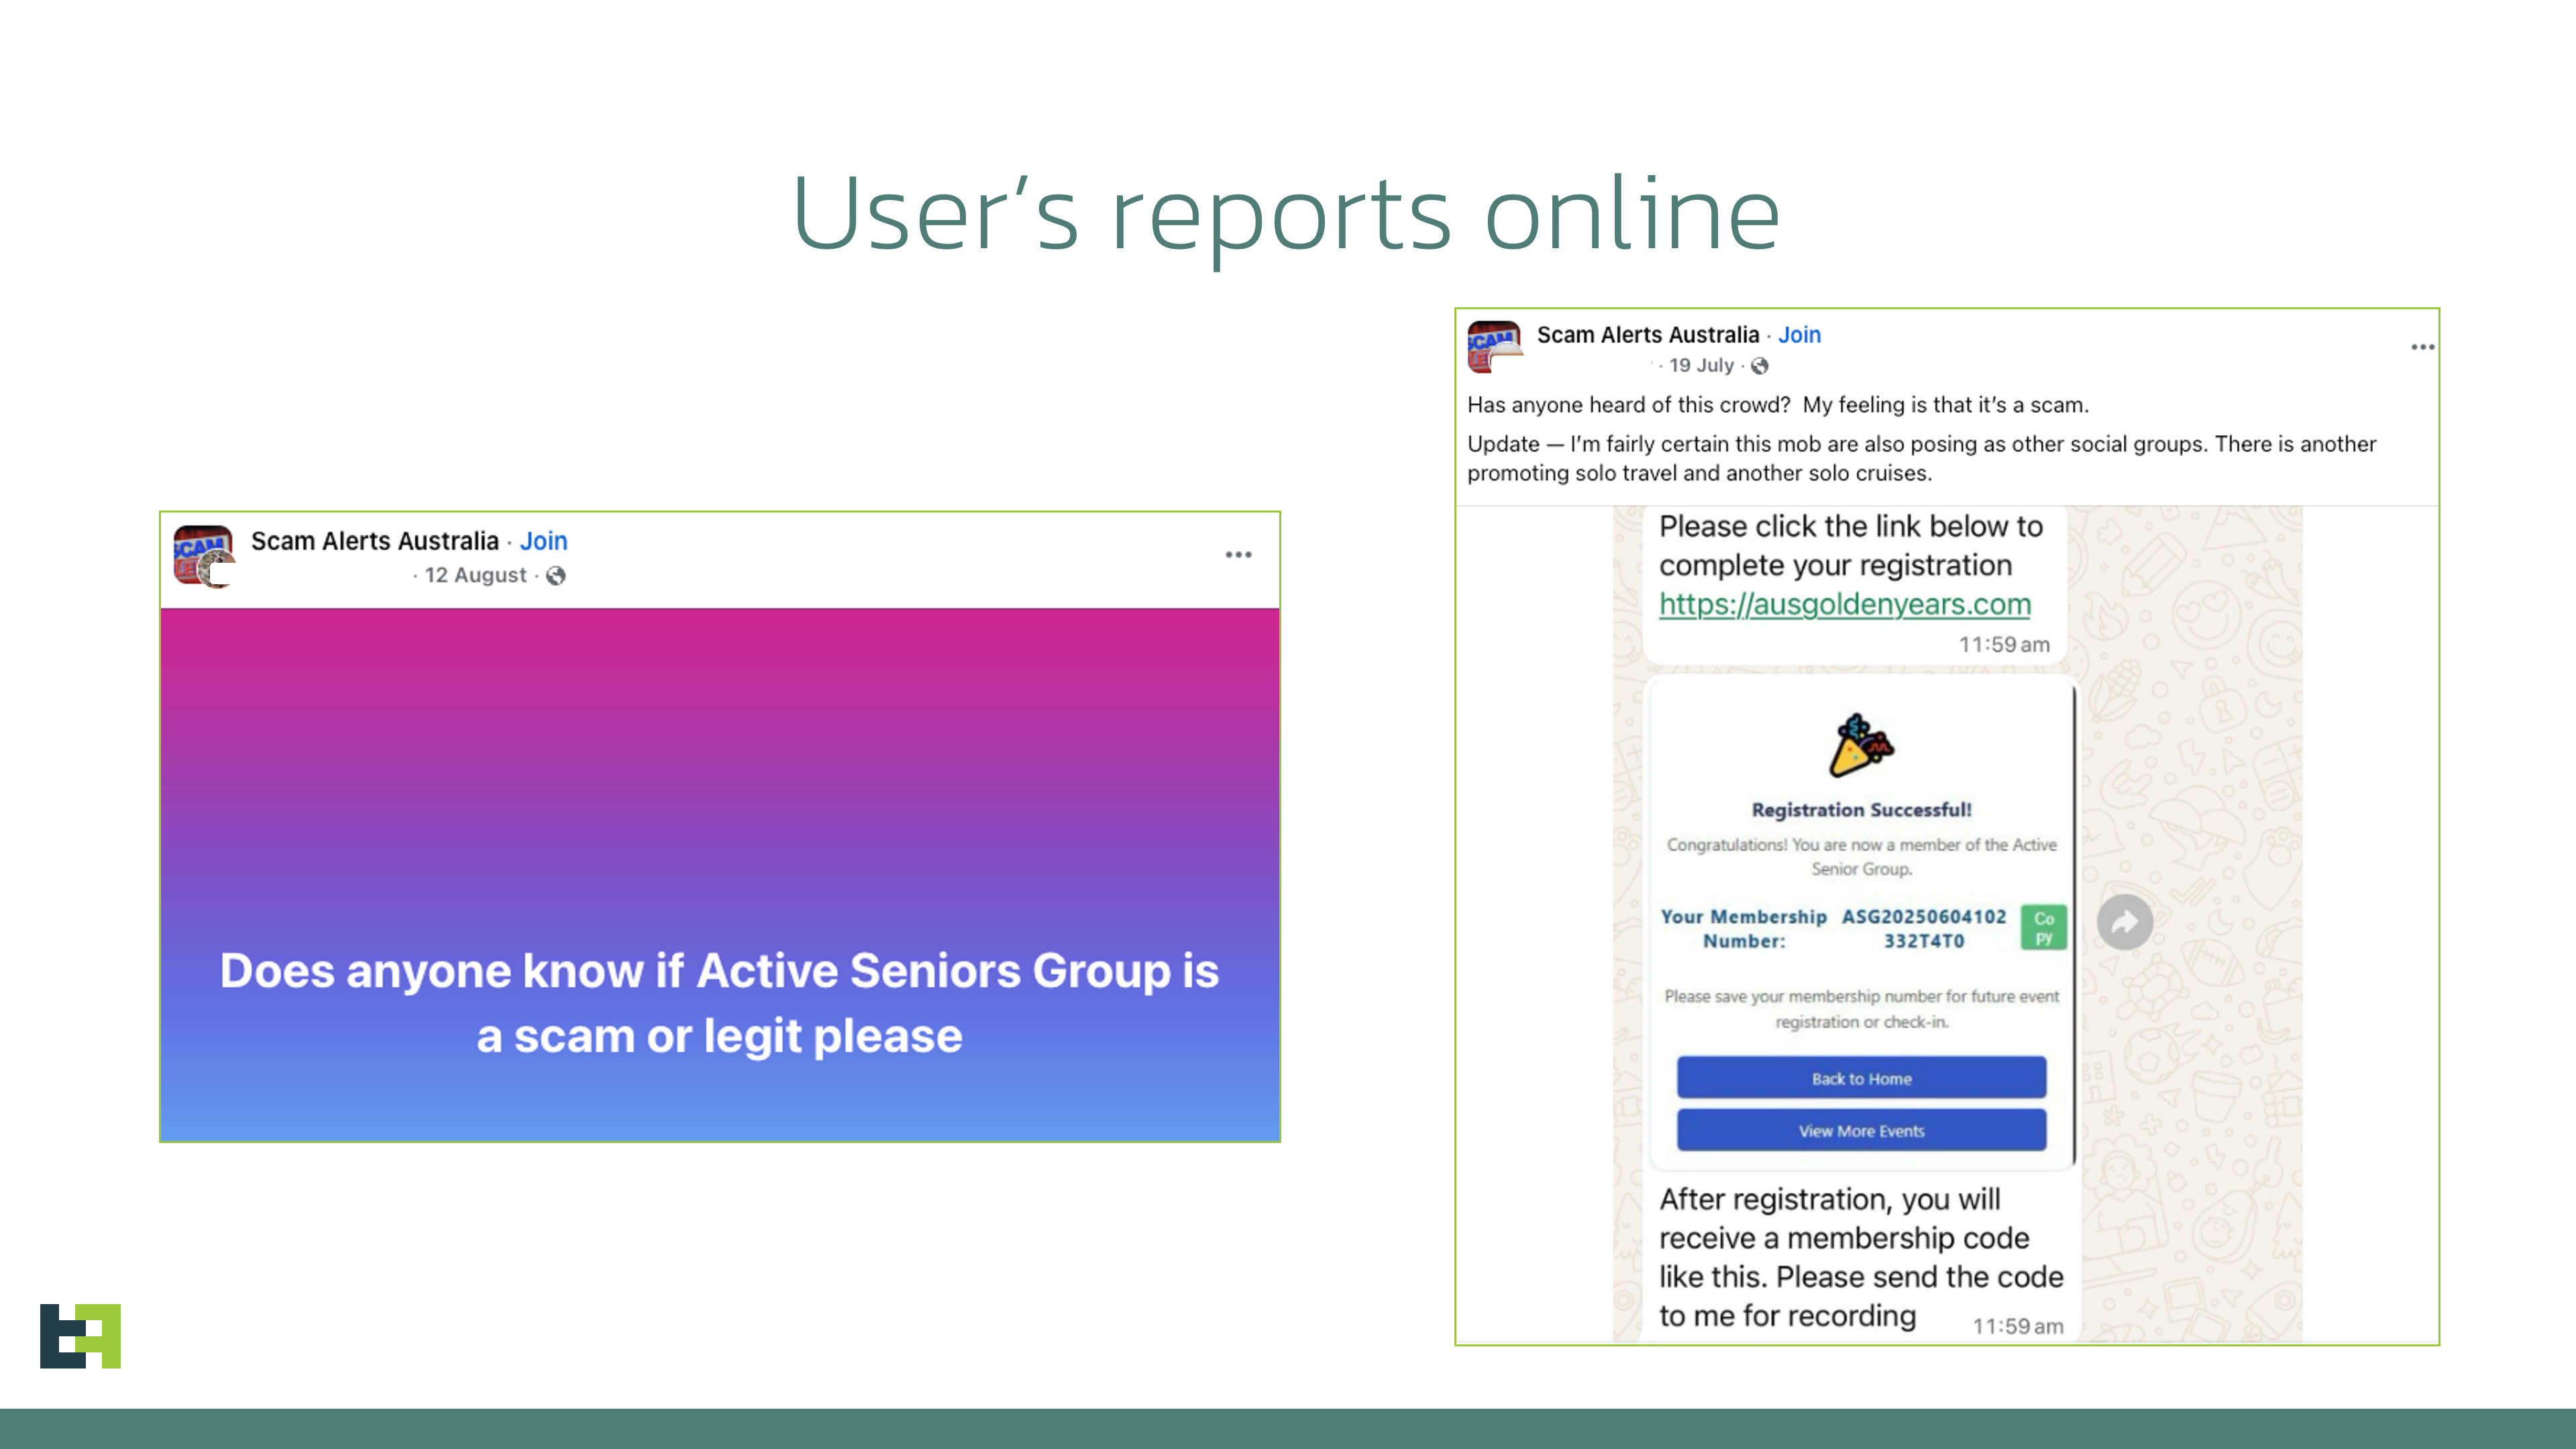
ThreatFabric discovered a Device-Takeover Android Trojan named Datzbro used in social-engineering campaigns that targeted seniors via fake Facebook groups promoting “active senior trips,” enabling remote control, audio/video capture, keylogging, and banking-focused accessibility logging. The malware’s C2 application and builder were leaked, making Datzbro freely available to global threat actors and expanding…
This cybersecurity roundup highlights recent incidents including a major data breach at Capita, supply chain risks in VSCode extensions, and updates on threat actor activities like NSO Group’s acquisition. Key topics also include government agency layoffs, vulnerability patches, and new threat intelligence reports. #CapitaDataBreach #NSOGroup #VulnerabilityPatch…

Cybersecurity Threat Research ‘Weekly’ Recap. The report highlights ongoing package-manager abuse, covert C2 channels, and extortion trends, including malicious npm packages, Discord-based C2, and double-extortion operations. It also covers high-severity vulnerabilities being actively exploited, phishing advancements, information-stealing and MaaS developments, and the rise of malware-less database ransomware, with emphasis on detection challenges and CTI considerations.
#Discord #SonicWall #CVEs #Qilin #RansomHub #Storm-2657 #ChaosBot #LummaStealer #GhostSocks #CastleRAT #XWorm #WhatsAppWorm #ClayRat #CryptoScam #DatabaseRansomware #NVD
Daily Recap, Open-source supply-chain attacks from a North Korean APT targeting npm and Node.js SEA/Electron installers to deliver RATs and ransomware, alongside a Gladinet zero-day being actively exploited. The summary also notes polymorphic RATs, ClayRat Android spyware, BreachForums takedown, and notable data-theft incidents including Sugar Land outage and PowerSchool breach, with updates on Windows 11 EOS and GDPR findings. #Stealit #Contagious npm #ClayRat #PowerSchool #Sugar_Land #Windows11_23H2 #GNU
Daily Recap, A PoC titled fenrir breaches secure boot on MediaTek-powered devices including the Nothing Phone (2a), enabling arbitrary firmware/OS installs and trust-chain compromise; Android spyware ClayRAT masquerades as popular apps to spy on Russian users and exfiltrate data. #Fenrir #ClayRat
Apple is expanding and redesigning its bug bounty program, offering higher payouts and new research categories to incentivize security researchers. The new rewards aim to combat sophisticated spyware and zero-click attacks, with total payouts potentially exceeding $5 million. #Apple #BugBounty #Spyware #ZeroClickAttacks #MemoryIntegrity
This week’s cybersecurity roundup highlights recent exploits, including vulnerabilities in Gladinet’s CentreStack and Triofox products, and attacks targeting Brazilian military via Zimbra. Notable incidents also involve data breaches affecting over 100,000 individuals, sophisticated espionage tools like ClayRat Android spyware, and efforts by OpenAI to prevent abuse of ChatGPT by threat actors….
ClayRat is an evolving Android spyware campaign distributed via Telegram channels and phishing sites that impersonate popular apps to trick Russian users into sideloading malicious APKs. Once installed and granted default SMS handler privileges, it exfiltrates SMS, call logs, notifications, device info, takes front-camera photos, sends SMS/calls, and self-propagates by messaging all contacts. #ClayRat #GdeDPS