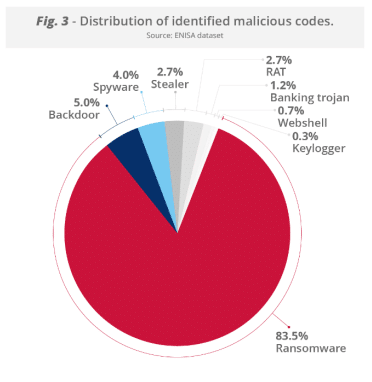
The 2025 ENISA Threat Landscape report highlights that hacktivism, DDoS attacks, and ransomware dominate the EU cyber threat environment. The report emphasizes rising supply chain attacks, evolving tactics among threat actors, and significant impacts on critical sectors. #ENISA #Hacktivism #DDoS #Ransomware #SupplyChainAttacks…
Tag: SPYWARE

Cybersecurity researchers have discovered a global scam campaign using Facebook groups targeting seniors to distribute Android malware called Datzbro. The malware exploits trust, enabling device takeover, credential theft, and financial fraud, with the builder now accessible to criminals worldwide. #Datzbro #AndroidMalware…

The daily recap covers nation-state espionage, ransomware, data breaches, AI-driven security trends, and notable campaigns, including a SonicWall SSL VPN MFA bypass tied to CVE-2024-40766 and a Harrods breach via a third-party supplier. It also highlights AI-enabled phishing with obfuscated SVG payloads, malvertising campaigns distributing spyware, Medusa exfiltration from Comcast, and broader activity from RedNovember and COLDRIVER, with impacts on multiple sectors. #SonicWall #Harrods #Medusa #RedNovember #COLDRIVER #TradingView

A sophisticated malicious advertising campaign has been exploiting verified accounts on Google and YouTube to spread malware promising free TradingView Premium access. This campaign hijacks legitimate channels, uses fake ads and hidden videos to deceive users, and distributes spyware like Trojan.Agent.GOSL. #TradingView #TrojanAgentGOSL…
The DeceptiveDevelopment campaign by North Korean threat actors involves stealing developer identities and distributing malware through fake job offers, primarily targeting cryptocurrency developers. These operations are closely linked to North Korea’s WageMole network, aiming at financial theft and identity fraud. #DeceptiveDevelopment #WageMole #North Korea #cryptocurrency #cyberespionage…

Microsoft Reduces Israel’s Access to Cloud and AI Products Over Reports of Mass Surveillance in Gaza
Microsoft has disabled services for an Israeli military unit after evidence showed its AI and cloud tools were used for mass Palestinian surveillance. The company is reviewing its roles amid reports of aiding Israel’s military operations and mass data collection. #Azure #Unit8200…

Vane Viper is a malicious adtech actor involved in widespread malvertising, ad fraud, and cyber threats using complex infrastructure and shell companies. Its operations have compromised hundreds of thousands of websites, facilitating malware distribution, phishing, and social engineering campaigns. #VaneViper #PropellerAds #Malvertising #CyberThreats…
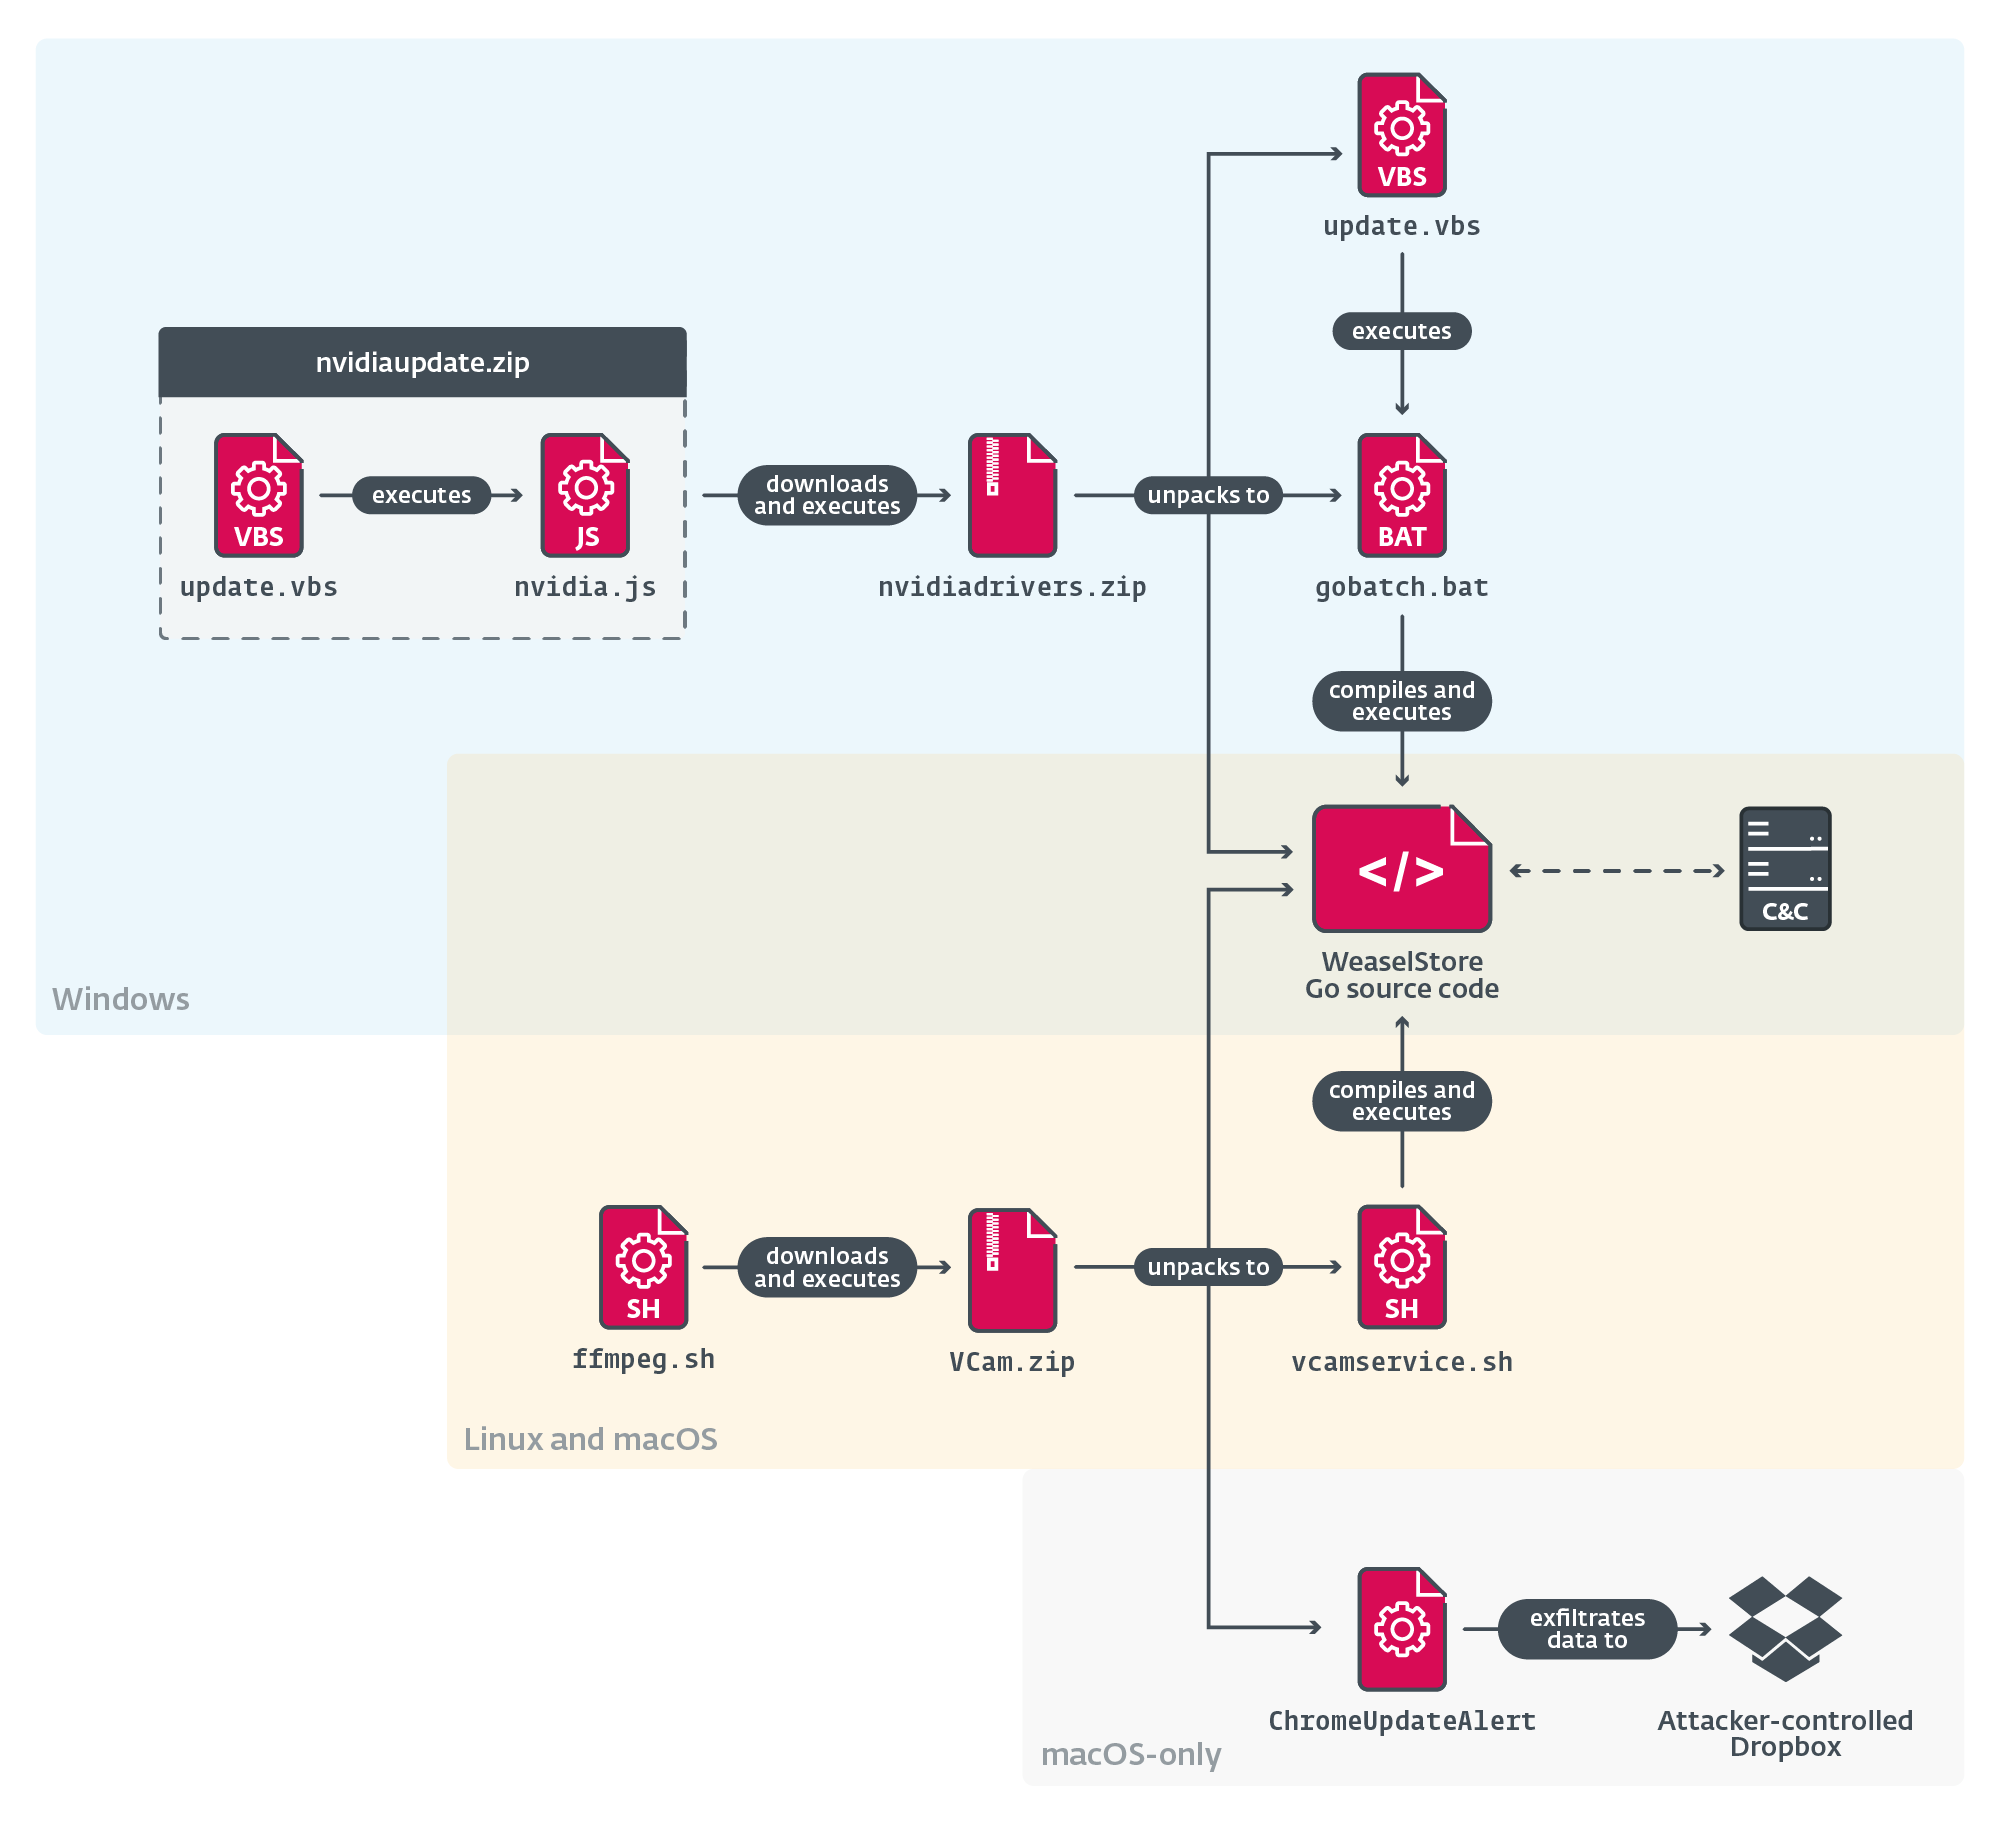
DeceptiveDevelopment is a North Korea-aligned group using sophisticated social engineering—fake recruiter profiles and the ClickFix technique—to deliver multiplatform malware like BeaverTail, InvisibleFerret, WeaselStore, TsunamiKit, Tropidoor, and AkdoorTea targeting developers and crypto-related projects. Research links their operations to North Korean IT worker fraud campaigns (WageMole), showing shared tools, stolen identities, and operational overlap between malware-driven campaigns and employment-fraud schemes. #DeceptiveDevelopment #TsunamiKit

This report details a North Korea-linked campaign called Contagious Interview, which uses multi-platform malware and social engineering tactics to target cryptocurrency developers globally. The campaign involves fake job offers and malicious programming exercises to deliver malware like BeaverTail, WeaselStore, Tropidoor, and AkdoorTea, linked to Lazarus Group tools. #ContagiousInterview #LazarusGroup…
DeerStealer is a multi-stage information-stealing malware distributed via ZIP archives and sold/supported on dark-web forums and Telegram, using signed binaries, legitimate DLLs, and decoy installers to evade detection and maintain long-term persistence. It harvests a wide range of data and exfiltrates it to shifting C2 domains such as telluricaphelion[.]com and loadinnnhr[.]today. #DeerStealer #telluricaphelion[.]com
Google has released emergency updates to patch a Chrome zero-day vulnerability, CVE-2025-10585, which is actively exploited in attacks. The vulnerability stems from a type confusion weakness in the V8 JavaScript engine and has been targeted by government-sponsored threat actors. #CVE-2025-10585 #V8JavaScriptEngine

Apple released security patches for CVE-2025-43300, an actively exploited zero-day vulnerability in their OS frameworks, to prevent memory corruption from malicious images. These updates are critical for targeted individuals as attackers have exploited this flaw in sophisticated campaigns. #CVE-2025-43300 #ImageIO…
This article details APT28’s advanced cyber-espionage activities targeting Ukrainian military networks in 2025, utilizing sophisticated infection chains and cloud-based C2 channels. The campaign showcases innovative techniques such as steganography and malicious use of legitimate cloud services to evade detection. #APT28 #CovenantFramework…
Apple has released security updates to patch a zero-day vulnerability (CVE-2025-43300) affecting older iPhones and iPads, which was exploited in highly sophisticated targeted attacks. The flaw involves an out-of-bounds write in the Image I/O framework, leading to potential remote code execution; Apple and WhatsApp have warned about ongoing exploitation. #CVE202543300 #ImageIO #targetedattacks #AppleSecurity

Apple has released timely updates to fix a critical security flaw (CVE-2025-43300) that has been exploited in targeted attacks using sophisticated methods. These patches also address multiple other vulnerabilities across Apple devices, enhancing overall security. #CVE-2025-43300 #iOSUpdate…