This issue of The Cybersecurity Pulse covers a wide range of security news, including Gemini’s mistaken access during a cybersecurity evaluation, active exploitation of critical flaws in F5, Check Point, Cisco, and FBIjobs.gov-related claims, plus new research and product launches across the AI security landscape. It also highlights major industry moves from Cyera, Jamf, Upwind, Dragos, and OpenAI, showing how agentic AI, detection, and browser security are rapidly evolving. #Gemini #Fencer #Cyera #Jev #OpenAI #MemTensor #OpenClaw #MemoryOS #F5 #CheckPoint #Cisco #EvilTokens #ClaudeOpus55 #Jamf #KeepAware #Upwind #Aegis #Dragos #runZero #NetRise
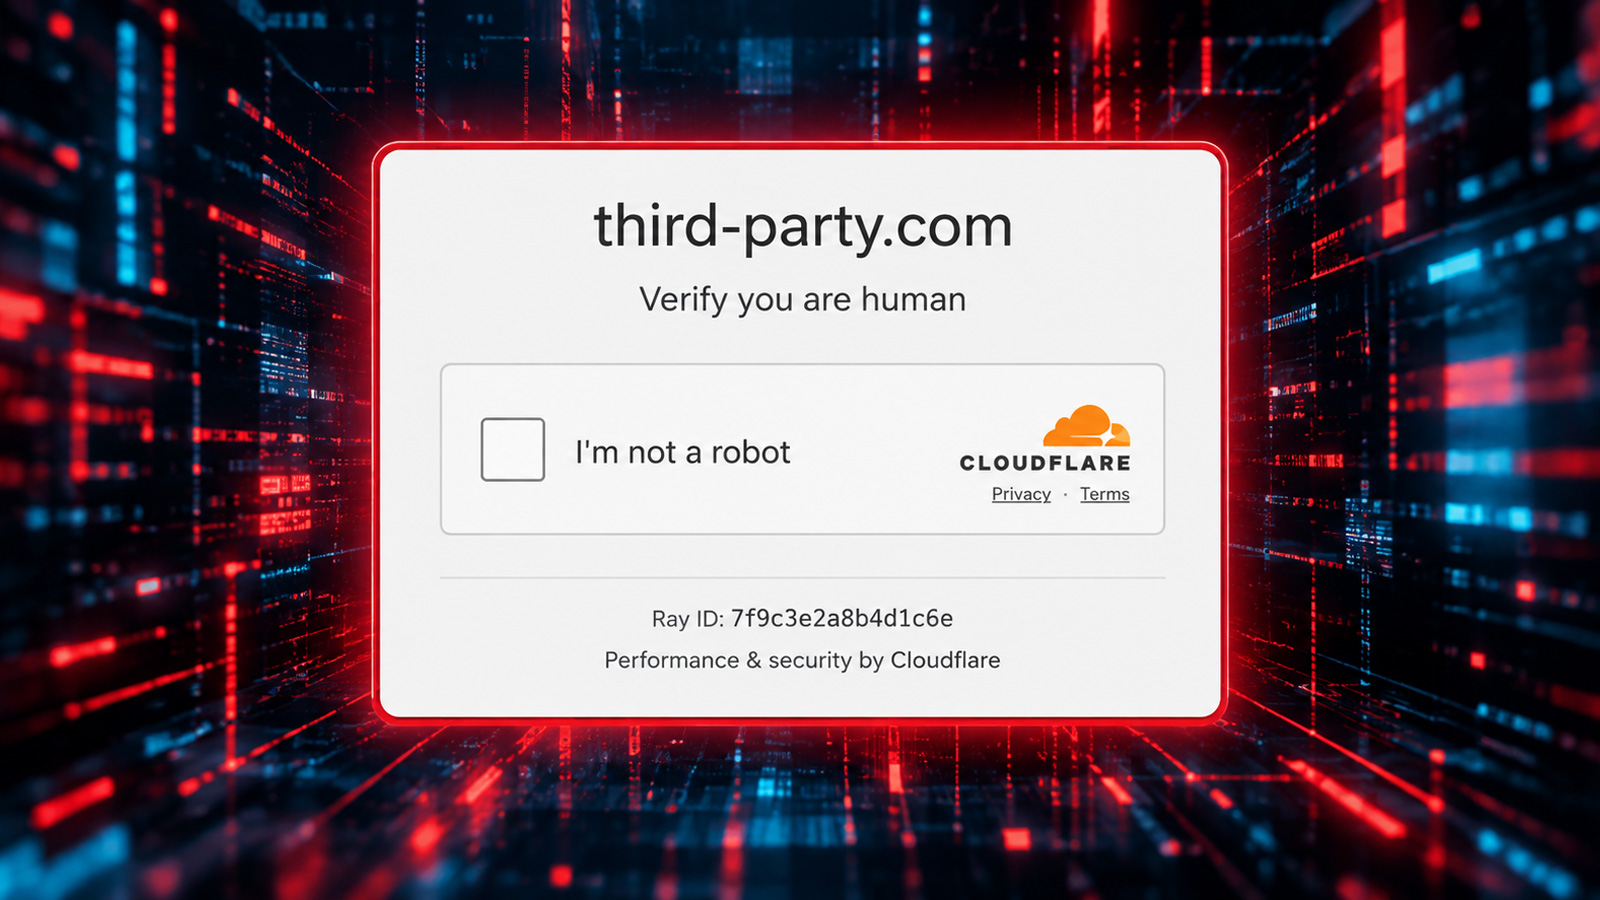
The third-party.com domain, long used as a placeholder in developer documentation, is now serving a fake Cloudflare verification page that tricks Windows users into running malicious PowerShell commands. The ClickFix attack targets only Windows systems and may have been copied into code or docs across many repositories, creating risk if those references are ever opened or executed. #third-party.com #Cloudflare #ClickFix #PowerShell #Windows
Karen Vardanyan, an Armenian national and alleged core member of the Ryuk ransomware gang, was sentenced in U.S. federal court to two years in prison after pleading guilty to computer fraud and conspiracy. Prosecutors said Ryuk carried out more than 2,400 attacks worldwide and extorted at least $15 million, with victims…
U.S. intelligence officials found no evidence that any foreign adversary successfully interfered in the 2024 presidential election, though Russia, Iran, and China each ran influence campaigns to varying degrees. The assessment also highlights growing concerns about AI-enabled election influence efforts and ongoing monitoring ahead of upcoming midterms. #Russia #Iran #China #ODNI…
Ofcom has opened an investigation into Aylo, the parent company of Pornhub, over whether its age-verification controls comply with the UK Online Safety Act and effectively block minors from viewing adult content. The probe centers on Aylo’s use of Apple-based age assurance signals, with Ofcom warning that weak testing or due…
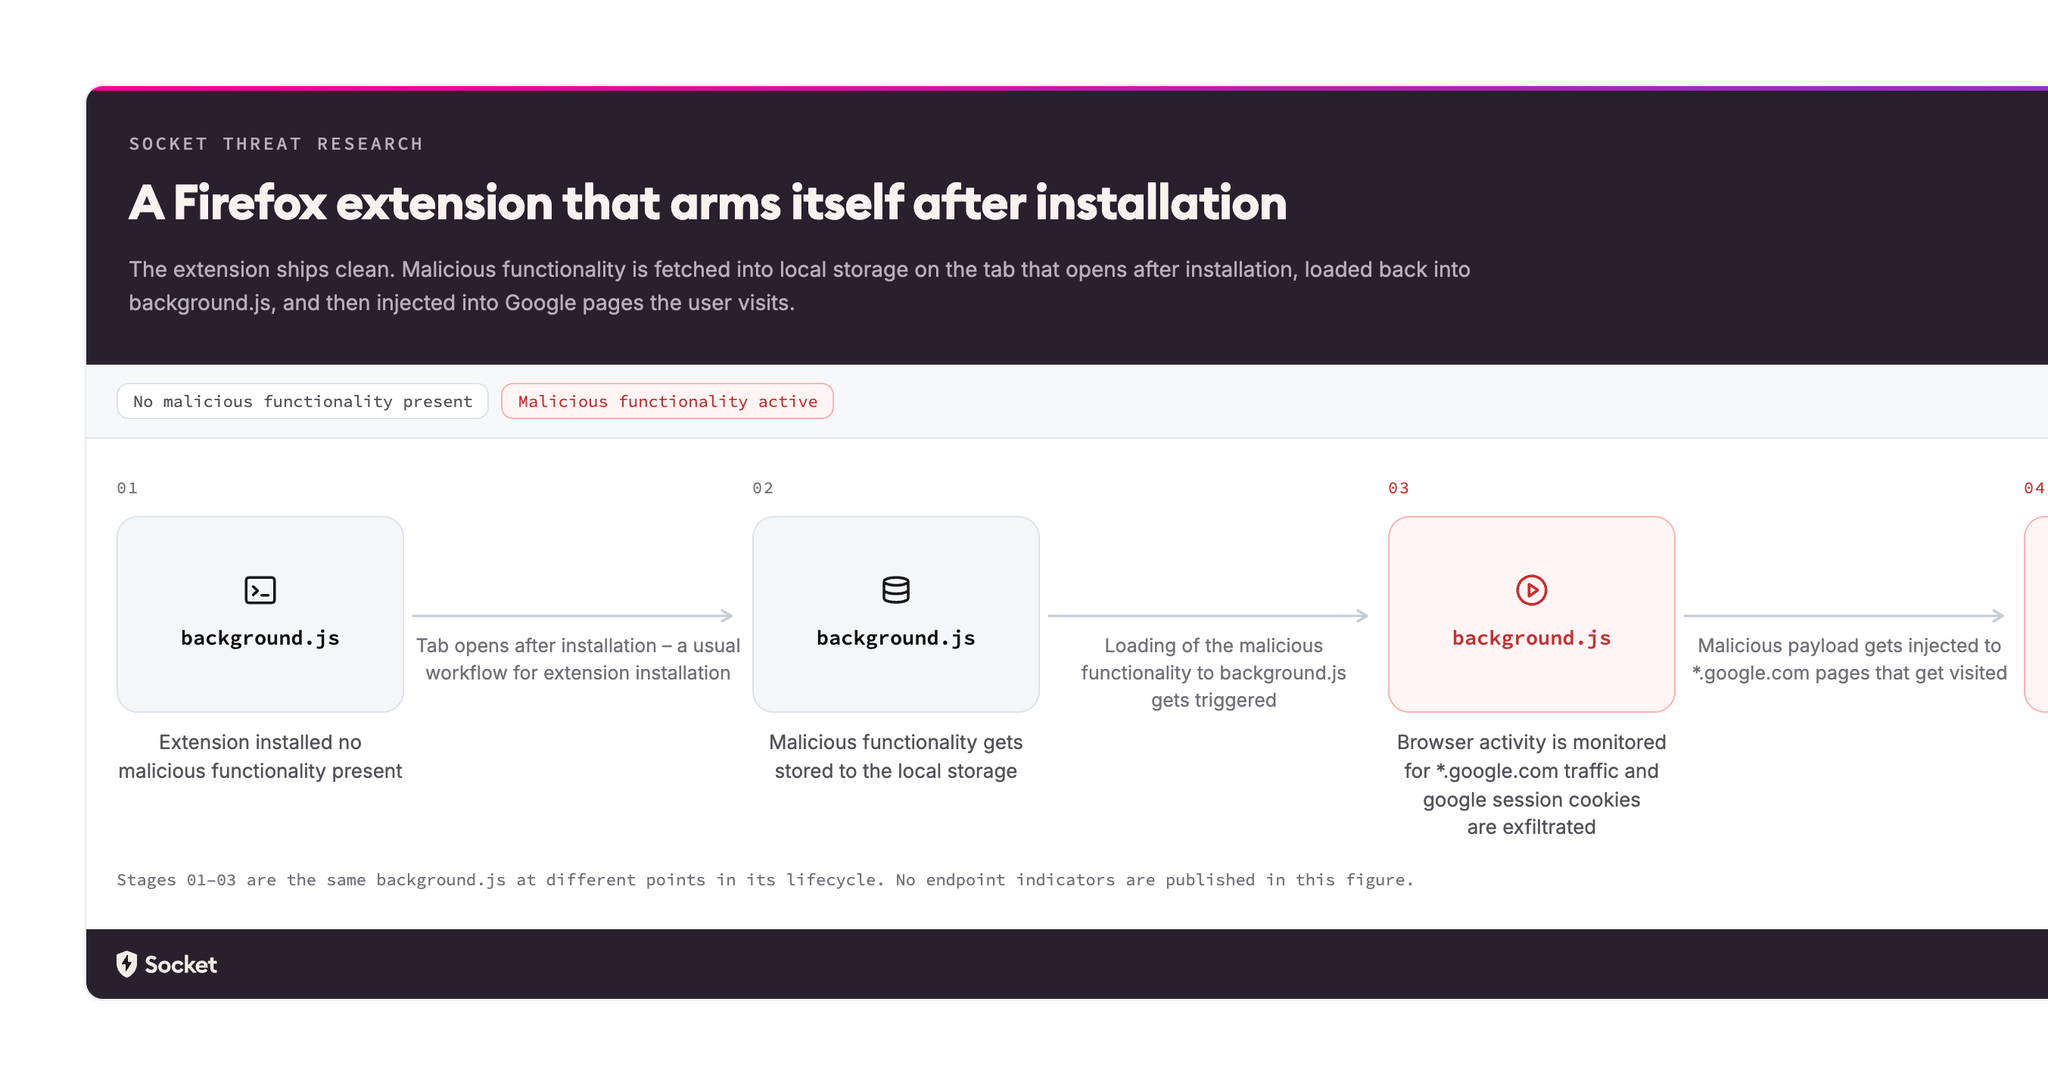
Socket identified a malicious Firefox extension, [email protected], that stays clean until after installation and then downloads a remote payload to automate Google account takeover. The campaign targets Portuguese- and Spanish-speaking users by hijacking Google sessions, stealing oauth_token cookies, and, when needed, forcing password resets through attacker-controlled infrastructure. #[email protected] #pdf.gusercontent.com #accounts.google.com
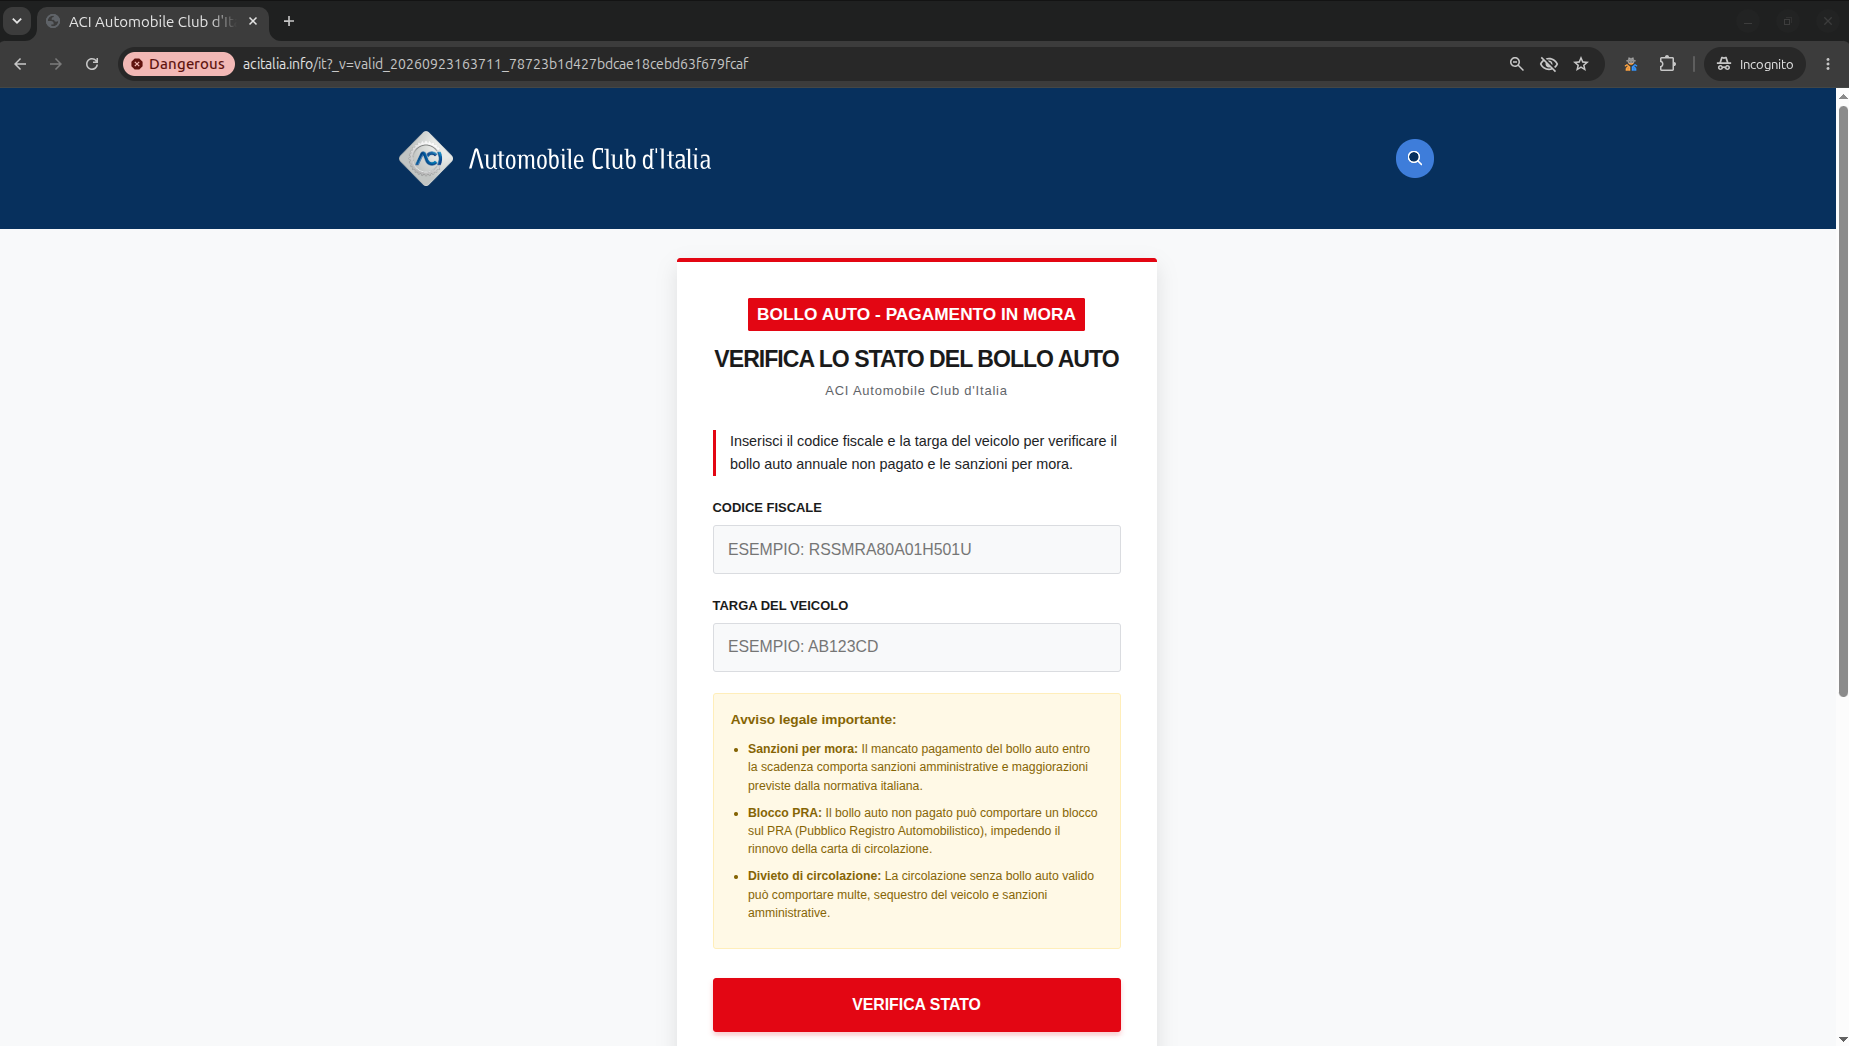
CERT-AGID identified a phishing campaign abusing the name, logo, and graphics of the Automobile Club d’Italia (ACI) to trick users into paying a fake annual vehicle tax debt. The fraudulent sites acitalia[.]info and acitalia[.]click collect personal data and card details while CERT-AGID has requested their takedown and shared the indicators with accredited organizations. #CERTAGID #AutomobileClubdItalia #ACI #acitaliainfo #acitaliaclick

EndZone ransomware claims it exfiltrated all eTeam employee records (15K), including full names, emails, home addresses, DOBs, SSNs, phone numbers, contracts, managers, hire dates, and salaries, demanding cooperation to prevent a leak. eTeam Inc., a global workforce solutions company with $229 million in revenue, is the alleged target of this public ultimatum, with the impacted country(s): #.
Solucioning S.A. in AR, a small (4–5 person) oil-sector contractor with major clients, suffered a HIGH-severity ransomware incident where Barracuda obtained access to confidential files including projects, documents, and blueprints (463 GB). After five days of non-response, the threat actor is reportedly selling/publishing the stolen data, warning of prepared maximum damage. #Argentina
In the US, the emperador threat actor reportedly targeted OnTrac, a major last-mile e-commerce delivery company, and exfiltrated 197k employee PII records as leverage for a $1 million ransom demand, threatening public release. The attackers sent ransom/payment instructions and extortion notices to OnTrac contacts, warning that non-cooperation would result in data being made public and “partners and employees” being targeted. #UnitedStates

CERT Polska says two MikroTik RouterOS SSH flaws, CVE-2026-67279 and CVE-2026-86060, can be chained to give attackers full administrative control of Internet-exposed routers without a password or completed authentication. Evidence of exploitation appeared before patches were released, with logs showing the suspicious SSH username -2 and post-exploitation activity tied to accounts…

Researchers uncovered Go-based malware distributed through two Go Modules and two Terraform providers, marking the first known abuse of HashiCorp’s centralized repository as a malware delivery channel. The activity overlaps with Graphalgo and other North Korea-linked campaigns that use fake job offers, npm, PyPI, Slack, and blockchain-based command channels to target…
IonQ says it has built a real-time quantum error-correction decoder that runs on a single standard CPU, aiming to reduce classical computing overhead in larger quantum systems. In simulations of up to 408 logical qubits, the decoder reportedly added as little as 0.02% processing time under standard noise conditions. #IonQ #QuantumErrorCorrection…
Check Point has confirmed active exploitation of CVE-2026-85102 and CVE-2026-93616, with attackers using VPNs and proxies to hide their origin while targeting Security Gateway and Management web service flaws. CISA has added both vulnerabilities to its KEV catalog, and Check Point has issued patching and mitigation guidance for affected customers. #CVE-2026-85102 #CVE-2026-93616 #CheckPoint #NCSC #CISA
RemControl is a new Android malware-as-a-service platform spread through malvertising and fake Google Play pages impersonating the TVTap IPTV app, with phishing overlays aimed at stealing banking credentials. Group-IB says it targets users across Europe, Canada, and the Middle East, uses a VPN trick to block Google Play protections, and may have been built with AI assistance. #RemControl #TVTap #GroupIB #ToxicPanda #UNKK