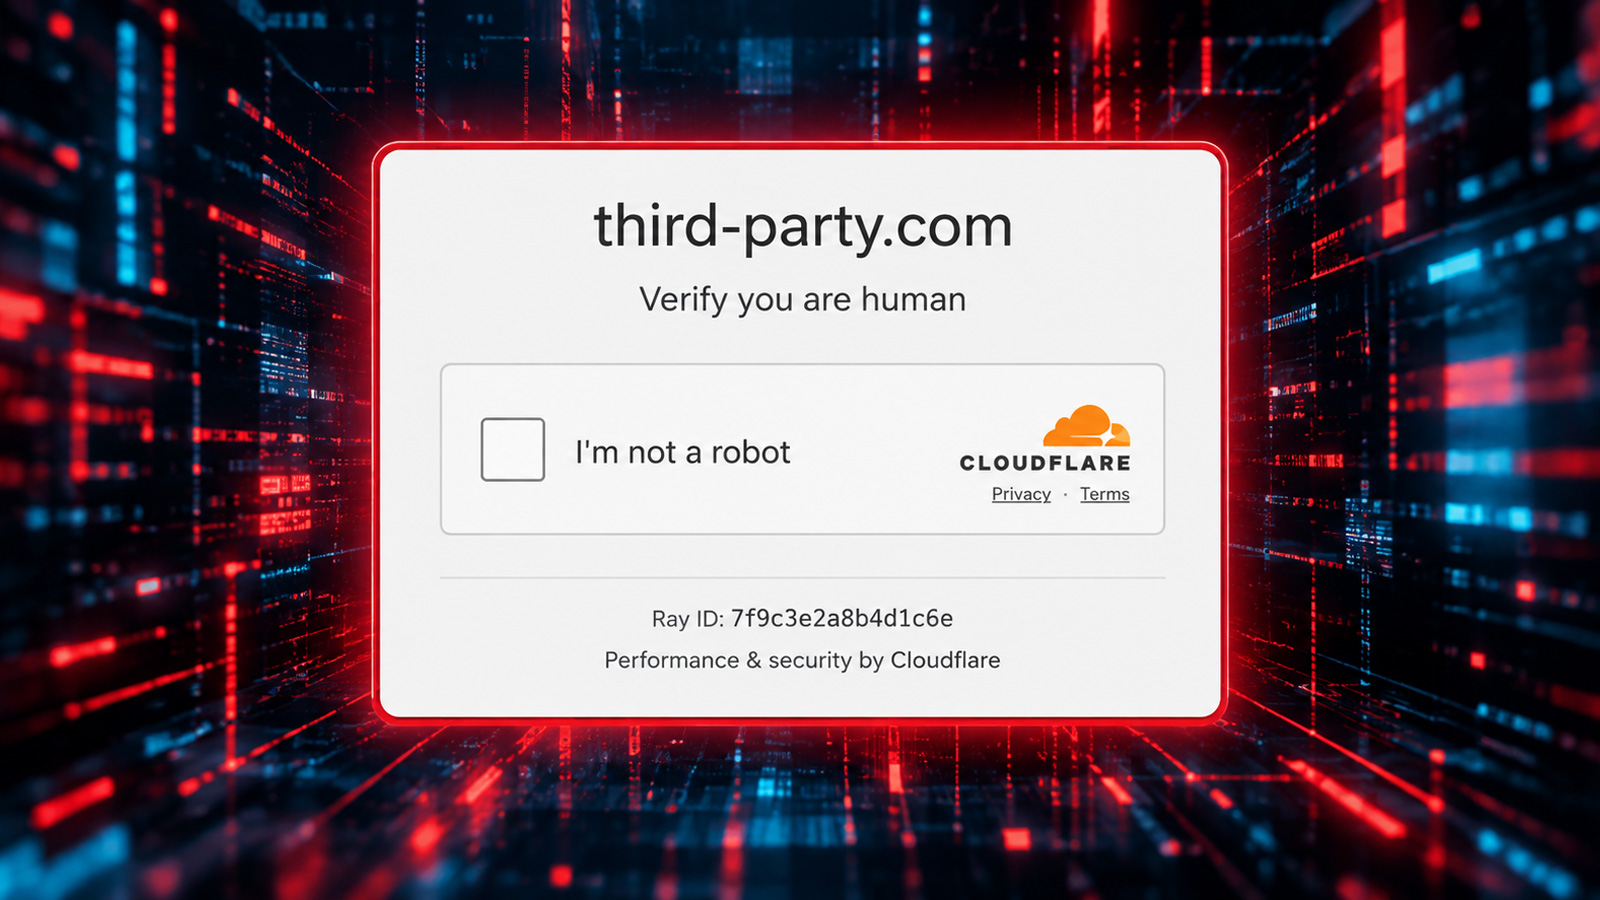
The third-party.com domain, long used as a placeholder in developer documentation, is now serving a fake Cloudflare verification page that tricks Windows users into running malicious PowerShell commands. The ClickFix attack targets only Windows systems and may have been copied into code or docs across many repositories, creating risk if those references are ever opened or executed. #third-party.com #Cloudflare #ClickFix #PowerShell #Windows
Keypoints
- third-party.com is serving a fake Cloudflare security verification page.
- The page uses a ClickFix technique to make users run malicious PowerShell commands.
- The attack targets Windows users and hides from macOS and Linux visitors.
- Clicking the fake verification box copies a payload into the clipboard and instructs users to run it.
- The domain’s long use in documentation makes it risky if copied into real code or tools.