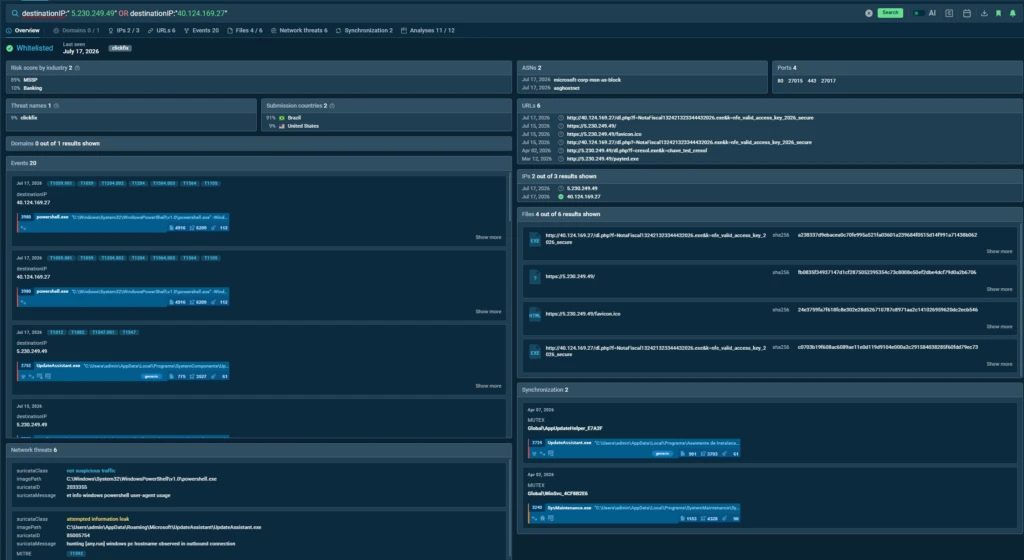
Fake tax-document and DocuSign lures are being used to deliver a custom HVNC backdoor to banking and financial organizations across Latin America. The malware provides hidden remote access, keystroke and browser-data theft, and Startup-folder persistence while disguising itself as Windows Update Assistant and using infrastructure tied to GHOSTnet GmbH and Azure…
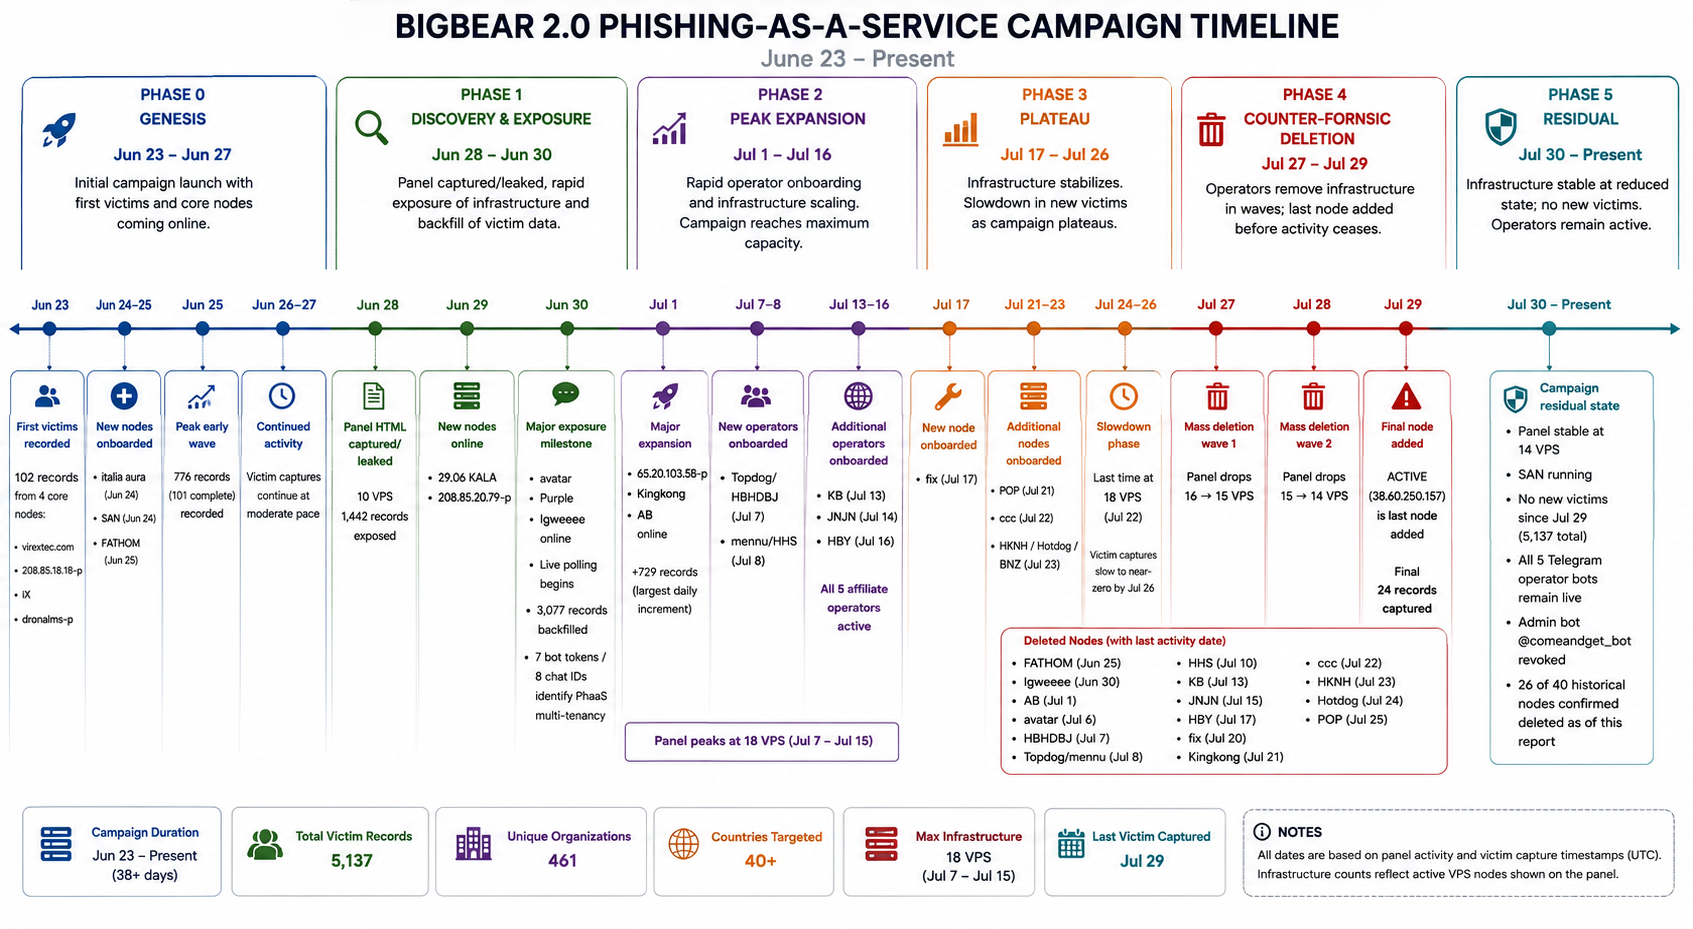
CloudSEK’s TRIAD uncovered BigBear 2.0, a rebranded Evilginx2-based phishing-as-a-service platform that targeted Microsoft 365 and enabled MFA bypass through AiTM session theft. The operation exfiltrated 5,137 credential records across 3,331 victim IPs in 40+ countries, used Telegram-driven credential delivery and geo-matched residential proxies, and remained active while evidence of counter-forensic cleanup was observed. #BigBear20 #Evilginx2 #GeneralBoss #Microsoft365 #Telegram

The ransomware claim involves Mutant (Brazil), where the threat actor “thegentlemen” allegedly compromised the Brazilian CX & AI company (mutant.com.br) and targeted its enterprise AI-driven operations and customer experience platforms. The impacted country is: #Brazil
The ransomware attack impacting SAD’S Interim (FR) has been attributed to the threat actor rhysida, targeting sensitive business records used in temporary employment operations, including SQL backups of the BRANIPP ERP, payroll documents, and bank-related transaction information. The compromised data also included identity and employment documentation for workers, such as SEPA bank statements, payslips, contracts, and government-issued cards/IDs. #France
BlackNevas ransomware (MEFA Endüstri, MEFA Group—mefagroup.com.tr, Milkrun logistics, Efachem, and Ecopolymer) claimed to have encrypted a list of files and demanded payment for cooperation via Telegram or email. The incident affected companies within the MEFA industrial ecosystem in Turkey. #Turkey
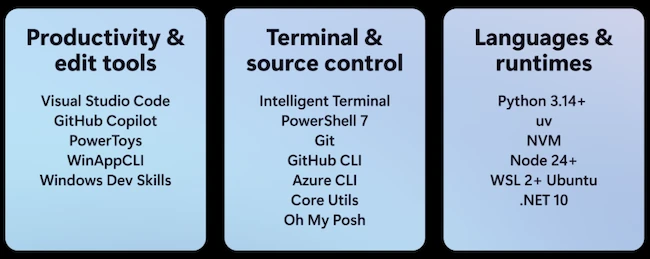
Microsoft’s Project Zenith is a ready-to-code Windows 11 experience for developer-class PCs built to run large local AI models with more than 30 billion parameters without relying on cloud tokens. It ships with a preconfigured development environment, built-in Linux support, and security features for AI agents, with the first systems powered by AMD Ryzen AI Halo. #ProjectZenith #AMD RyzenAIHalo #Windows11 #WSL #MicrosoftExecutionContainers
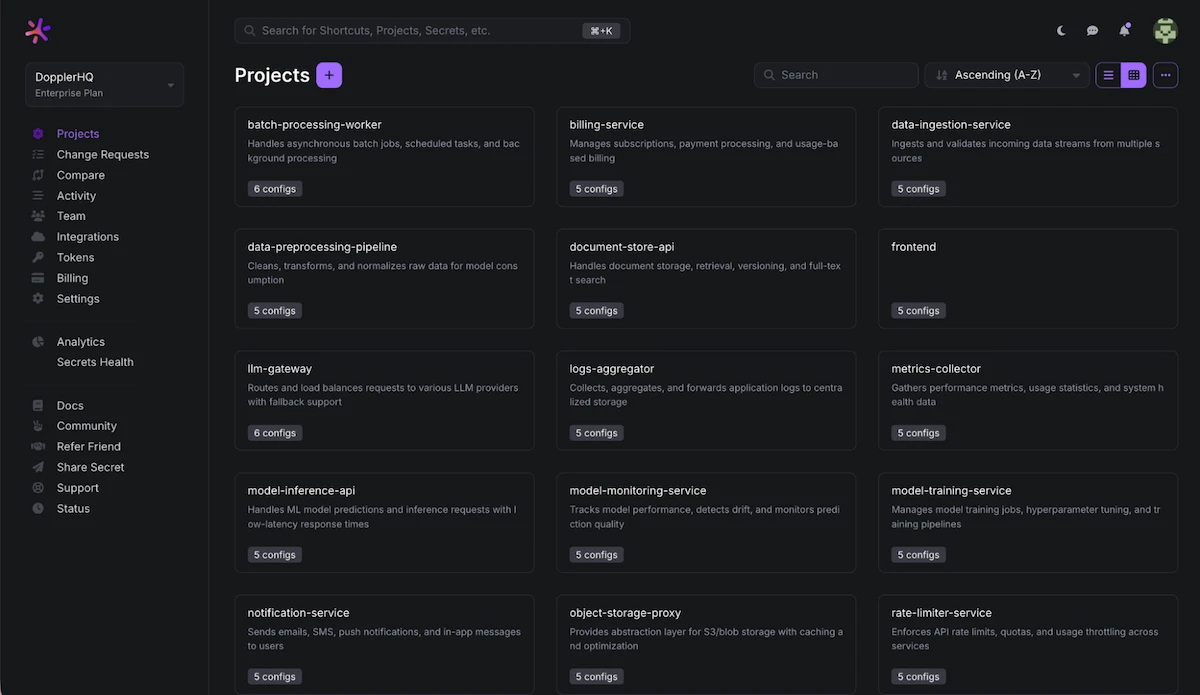
AI agents have multiplied the number of identities that need secure access to credentials, making modern secrets management essential for engineers, pipelines, and machines. Doppler centralizes, injects, and governs secrets for applications and AI agents with runtime delivery, fine-grained controls, and support for cloud or on-prem deployments. #Doppler #MCP #OIDC #AWS #Azure #GCP #SCIM

Dave Ross of Intel 471 explains the inner workings of ransomware negotiations, including how attackers research victims, set demands, and use test decryptions to prove they have a working key. He also highlights the criminal service economy, multi-extortion tactics, and the need for clear pre-incident response planning. #Intel471 #DaveRoss

A Bitdefender survey found that 55.2% of IT and cybersecurity professionals who experienced a breach in the past year were told to keep it confidential, even when disclosure was required. The report says attackers, fear of fines and reputational harm, and a culture of silence are all helping keep breaches hidden. #Bitdefender #BruceSussman
The ransomware incident affected Drogueria Saporiti Sacifia (Argentina), where threat actor thegentlemen reportedly stole and exfiltrated approximately 100GB of data. As a century-old Argentine pharmaceutical wholesaler and manufacturer supporting thousands of pharmacy clients, the compromise impacts operations and information integrity in Argentina. #argentina
AuditTeam ransomware reportedly targeted pa***op in RU, encrypting files and demanding payment for decryption. The incident is attributed to AuditTeam and occurred in #RussianFederation

A forum actor posting as Keishell claims to have obtained moderator-level access to ryxcars.com, a Dubai-based luxury vehicle marketplace, with the ability to read and modify seller records. The alleged exposure includes seller identities, contact details, verification status, and detailed vehicle listing data, but the claim remains unverified. #ryxcarscom #Keishell #Dubai…
A forum actor calling themselves DaOnlySpark claimed to publish 3.7 GB of Jinko data, including patient records, clinical profiles, and 20,635 private messages. The alleged leak is unverified but appears highly sensitive, exposing cancer diagnoses, treatment history, and contact details tied to both patients and doctors. #Jinko #DaOnlySpark #France…

Daily Recap, Attackers are actively leveraging multiple critical vulnerabilities, including N-able N-central CVE-2026-86218, an Adobe Commerce zero-day, and new MikroTik RouterOS bugs, to achieve RCE, plant backdoors, and hijack routers. Meanwhile, ConnectWise ScreenConnect is facing a worm-like file-transfer campaign, researchers revealed Nightmare Eclipse targeting CrowdStrike, Nvidia, and Avast, and Trezor reported breach impact affecting 81,000 customers.
#CVE-2026-86218 #N-able #N-central #AdobeCommerce #MikroTik #RouterOS #ConnectWise #ScreenConnect #NightmareEclipse #CrowdStrike #Nvidia #Avast #Trezor #CCQ #SEP-2026
German authorities are investigating another leak from Berlin’s government network after hackers published stolen login credentials and other data online, following an attack that hit two ministries in mid-August. The breach has been linked by the Rhysida ransomware group, while Berlin officials say they will not pay the attackers and are…