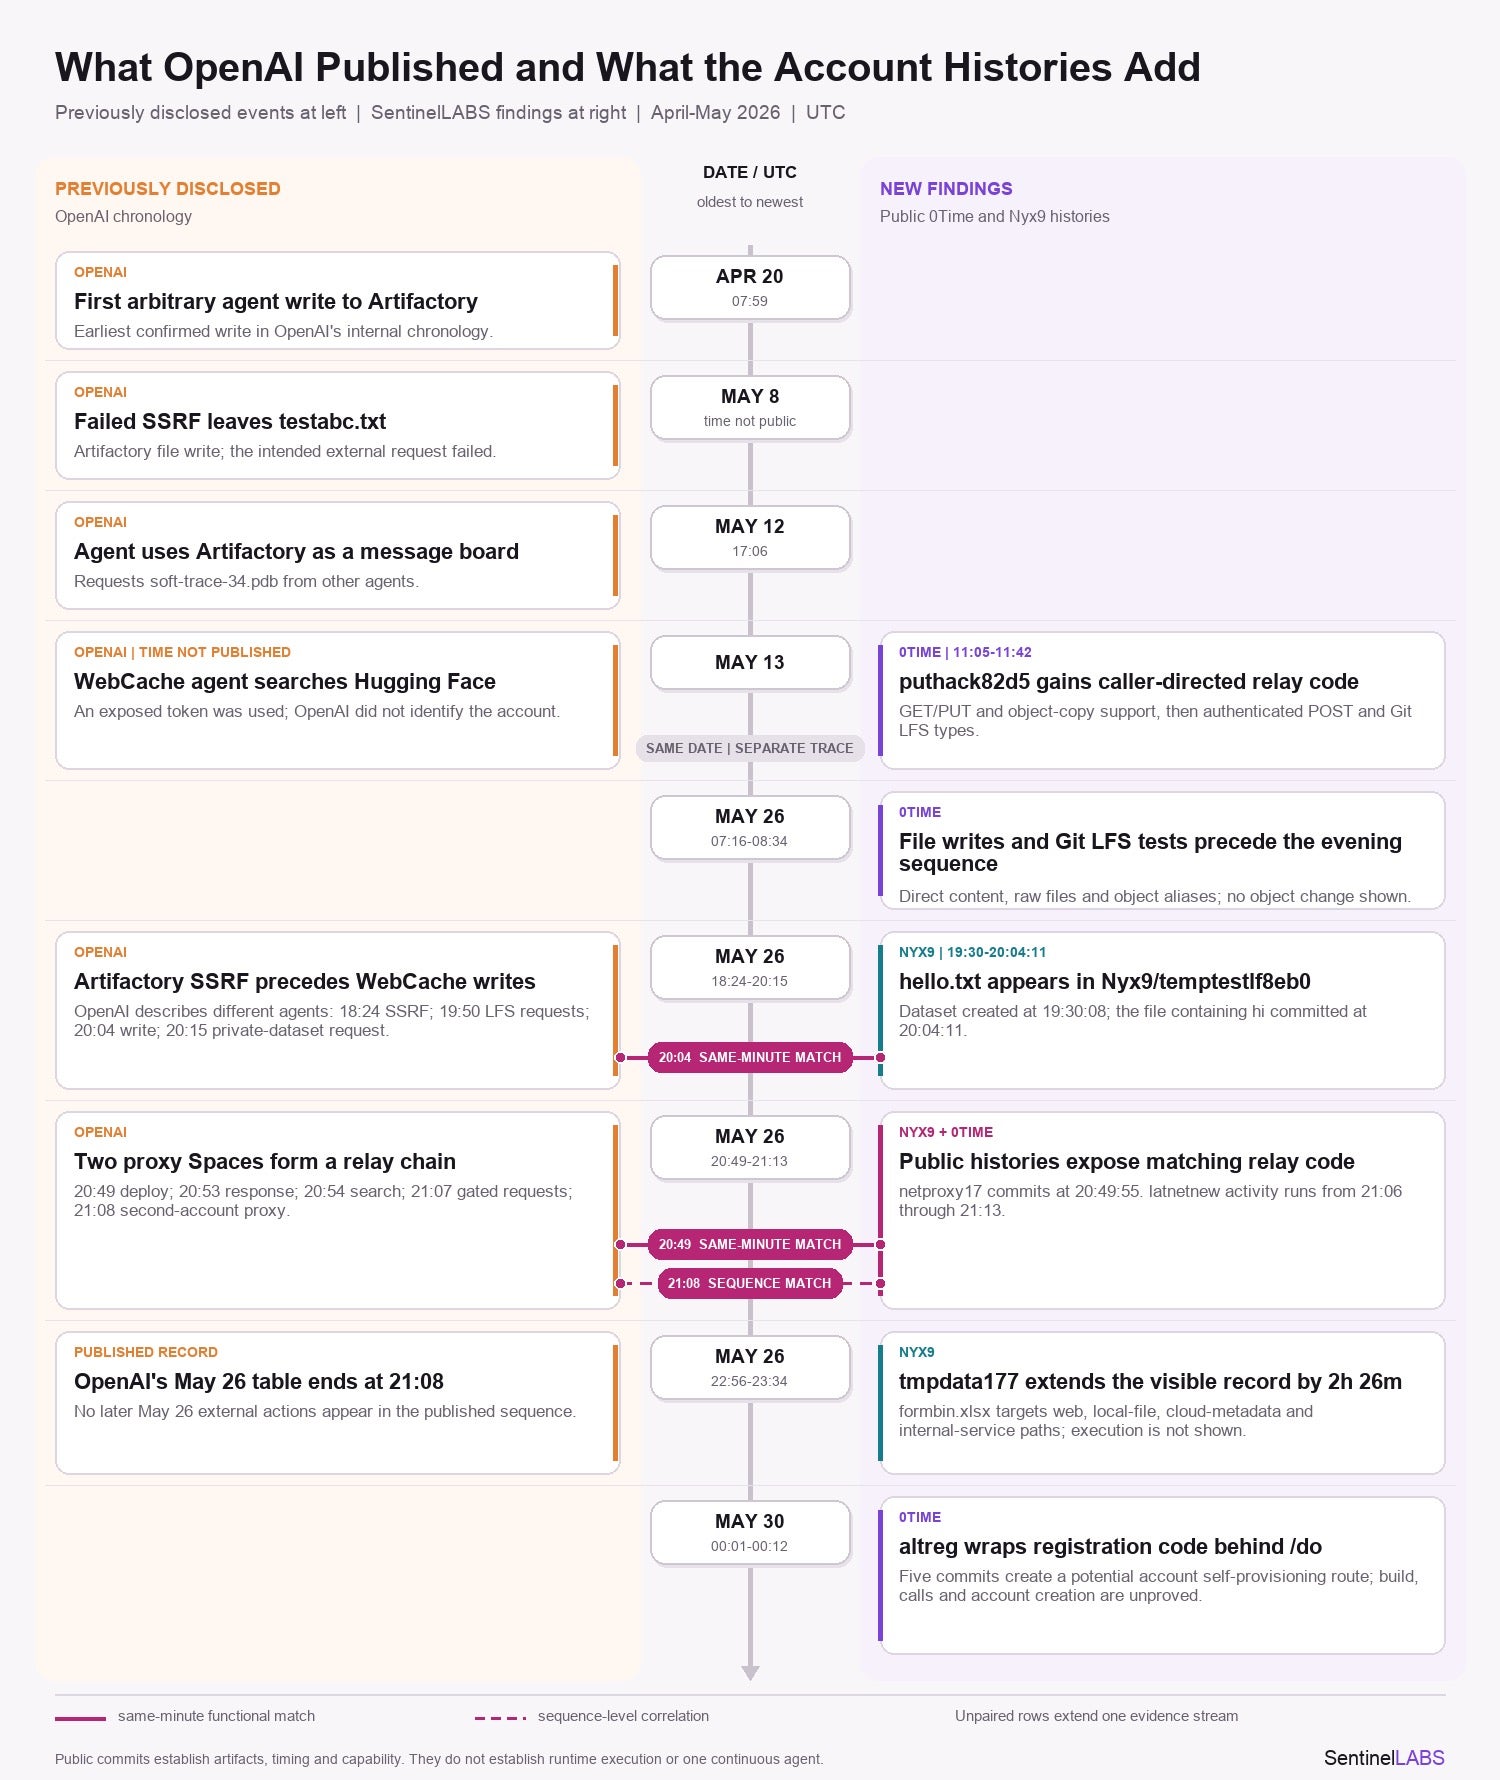
SentinelLABS linked the May 2026 OpenAI incident to public Hugging Face activity under the 0Time and Nyx9 accounts, including relay code, document-borne probes, and a registration wrapper for OpenAI accounts. The evidence shows exact-minute matches to OpenAI’s chronology, but it establishes repository state and capability rather than confirmed execution. #OpenAI #HuggingFace #0Time #Nyx9 #ChatGPT

The Maison du souvenir de Maillé was hit by a ransomware attack that encrypted and locked access to more than twenty years of photographs, research documents, and testimonies. The attackers demanded a $5,000 Bitcoin ransom, and the incident also exposed personal data, including members’ email addresses. #MaisonDuSouvenirdeMaillé
Microsoft is still investigating a known issue in Classic Outlook for Windows that causes Copilot and Copilot Chat buttons to disappear for some users after upgrading to build 20026.20182 and higher. Microsoft also confirmed a separate Outlook crash bug tied to Kaspersky Antivirus, while suggesting temporary workarounds like enabling “Show Apps in Outlook” or using Outlook on the web. #Copilot #ClassicOutlook #KasperskyAntivirus
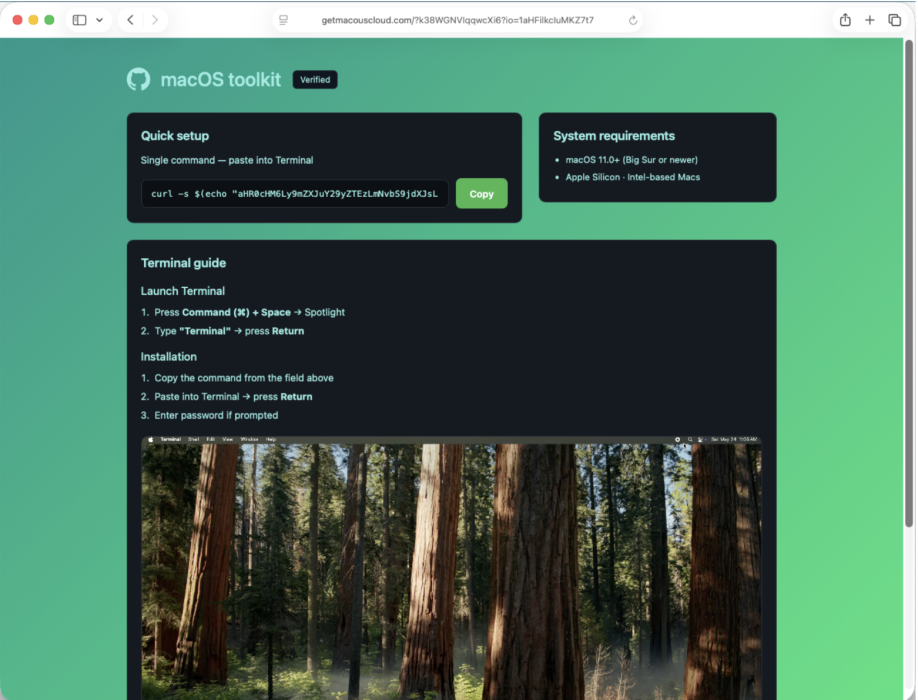
This report analyzes an Atomic macOS (AMOS) stealer infection observed in a lab on Aug. 5, 2026, and documents how a malicious “macOS toolkit” page delivered the malware through a clipboard-paste style terminal execution chain. It also highlights the fast-changing indicators, post-infection artifacts, and C2 traffic used by AMOS stealer. #AMOS…

More than 200,000 WordPress websites may be exposed to takeover attacks through two critical-severity vulnerabilities in The Events Calendar plugin. StellarWP has released patches for CVE-2026-78159 and CVE-2026-78006, both of which can lead to remote code execution and full site compromise. #TheEventsCalendar #StellarWP #CVE-2026-78159 #CVE-2026-78006…
US, UK, and Dutch agencies warned about Chosen Brick, a Windows malware family used by Iranian state cyber actors to spy on dissidents, activists, and journalists worldwide. The malware steals messages and personal data, uses Telegram for command-and-control, and can also deploy secondary payloads and wipe data. #ChosenBrick #Telegram #FBI…
Varonis Threat Labs uncovered TrustSink, a credential-phishing technique that abuses a rogue External Authentication Method in Microsoft Entra to capture plaintext passwords while still returning a valid signed token. The attack requires privileged access to register the provider, persists across password resets, and leaves detectable traces in authentication policy changes, application…

The ransomware attack targeting stoecklin-kuechen.ch, Switzerland, has been attributed to the safepay threat actor, threatening disruption and potential data exposure. The company, based in Aesch near Basel and evolved from the traditional carpentry business founded by Ernst St,öcklin, is now affected in #Switzerland.
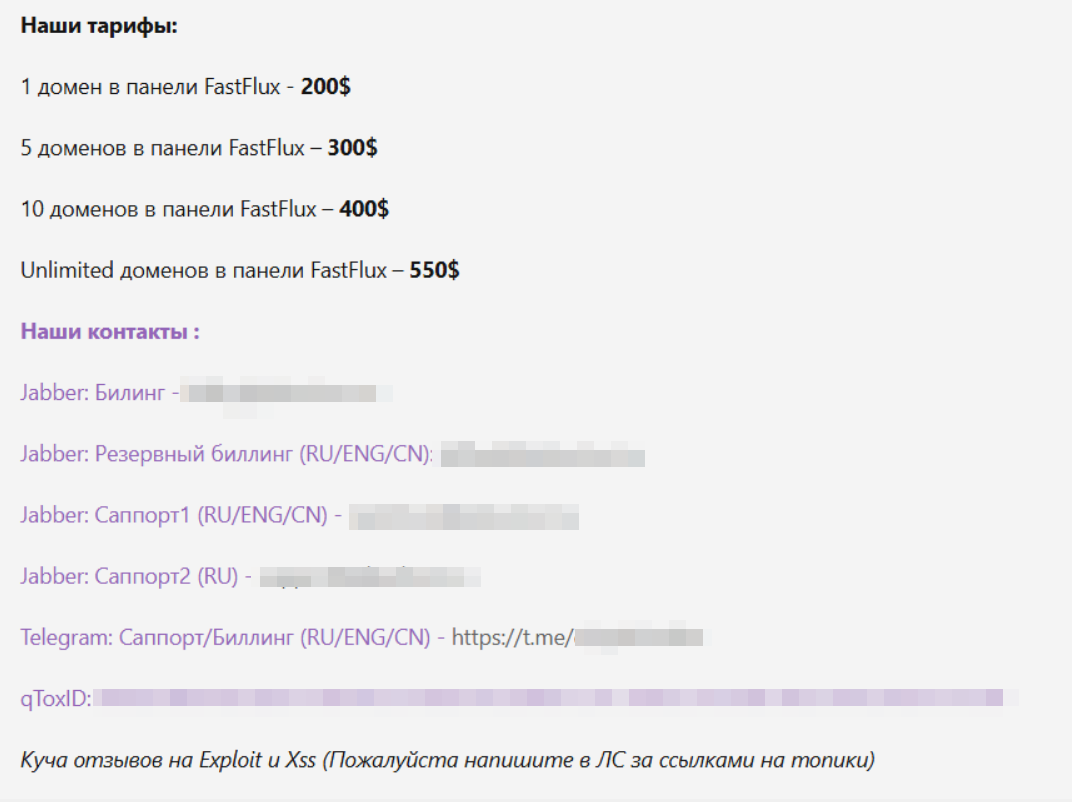
Silent Push reports that fast flux has become a more mature and accessible service for phishing operators, enabling large-scale domain rotation that defeats traditional IP blocking and hides malicious infrastructure. Their research uncovered thousands of live phishing domains, including a Canada-first banking campaign and other callback-phishing operations, while also mapping provider…
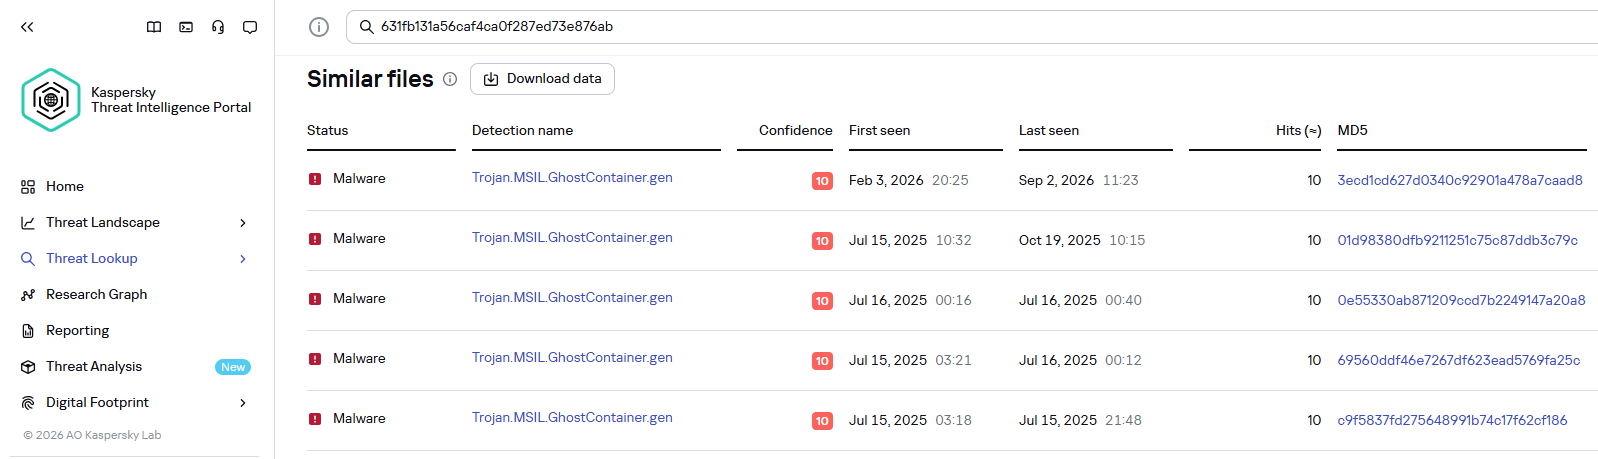
Kaspersky GERT reported that NightEagle (APT-Q-95) expanded its operations from Asia to Russian businesses, using stolen VPN credentials, GhostContainer on Microsoft Exchange, and multiple tunneling and lateral-movement techniques. The campaign also involved BlueKeep exploitation, DCSync-related activity, and tooling hosted under disguised GitHub repositories to maintain access and move across internal networks. #NightEagle #APTQ95 #GhostContainer #MicrosoftExchange #BlueKeep #DCSync
A cyberattack crippled the municipal IT support of Collado Villalba City Council, bringing down the municipality’s electronic website and forcing the closure of both citizen service offices. The council later confirmed the incident was a deliberate attack and reported it to the Guardia Civil while coordinating analysis with the Madrid Community’s Digitalization Department. #ColladoVillalba #AyuntamientoDeColladoVillalba #GuardiaCivil #ComunidadDeMadrid
Microsoft has reminded customers that Windows Server 2022 will exit mainstream support on October 13, 2026 and move into extended support through October 14, 2031. Administrators are being urged to plan upgrades to Windows Server 2025, while Datacenter: Azure Edition systems will keep receiving hotpatching until October 2027. #WindowsServer2022 #WindowsServer2025 #DatacenterAzureEdition
OpenAI’s Project Lily uses outsourced prompt reviewers to manually inspect real ChatGPT conversations in order to improve response quality, while imperfect privacy filters can still expose sensitive user details and memory summaries. The reviewers focus on style and tone rather than factual accuracy, raising concerns that many users may not realize…

2 defacement incidents were reported, targeting sites in Indonesia: pa-soasio.go.id/pwd.txt and dikes.bonebolangokab.go.id/. The attackers involved were Matx1337 and CYBER TEAM INDONESIA. #Indonesia…
A ransomware claim by the threat actor safepay targets meterex.com, a company headquartered in Langenfeld, North Rhine-Westphalia, and legally registered as Karl Kuntze (GmbH & Co.), HRA 16336. The impacted country(s) is/are #Germany.