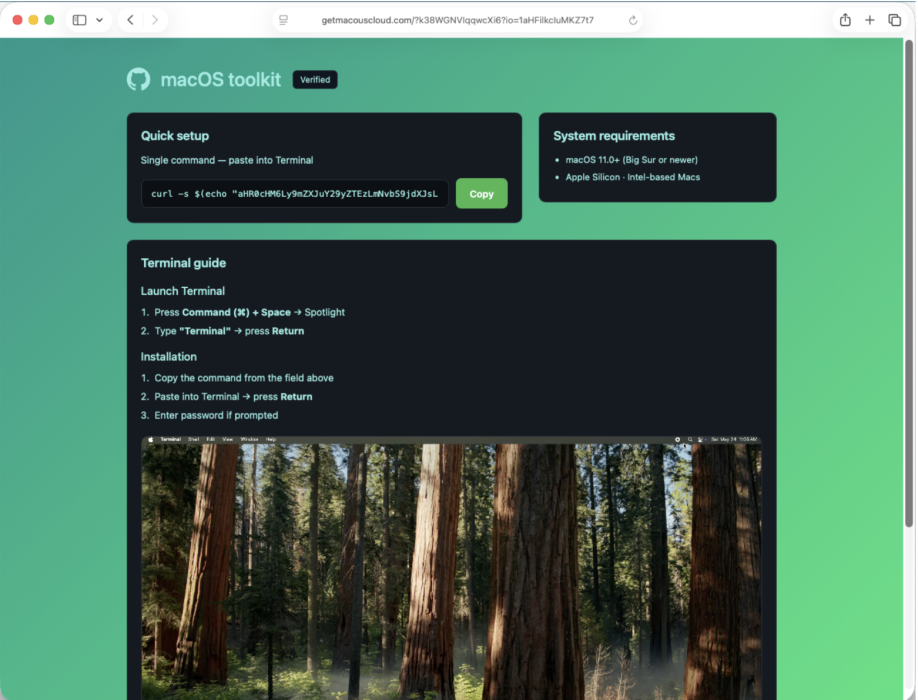
This report analyzes an Atomic macOS (AMOS) stealer infection observed in a lab on Aug. 5, 2026, and documents how a malicious “macOS toolkit” page delivered the malware through a clipboard-paste style terminal execution chain. It also highlights the fast-changing indicators, post-infection artifacts, and C2 traffic used by AMOS stealer. #AMOS #macOS #Unit42 #PaloAltoNetworks
Keypoints
- AMOS stealer is a macOS information stealer advertised on Telegram since at least April 2024.
- The infection analyzed in the article began from a malicious site, getmacouscloud[.]com, posing as a “macOS toolkit” installer.
- The initial pasted command downloaded a Zsh script from ferncore13[.]com, which then unpacked a GZIP/Base64 payload and launched a Mach-O installer.
- Persistence was established through files placed in Library/Application Support paths, including .com.apple.accountsd and .com.apple.metadata.mds.
- The malware requested permissions for Finder, Desktop, Documents, and Notes access during execution.
- Collected data was staged in /tmp and compressed into out.zip, including browser, wallet, Telegram, and file-grabber artifacts.
- Post-infection traffic used HTTP POST requests to C2 IPs that changed between infections, showing AMOS infrastructure and indicators are highly volatile.
MITRE Techniques
- [T1204.004 ] User Execution: Malicious File – The victim followed instructions on a fake setup page and pasted a command into Terminal, triggering the infection (‘we copied text from the page and pasted it into a Terminal window’).
- [T1059.004 ] Command and Scripting Interpreter: Unix Shell – The initial command retrieved and ran a Z-shell script on macOS (‘The command … retrieved a Z-shell (Zsh) script’).
- [T1027 ] Obfuscated Files or Information – The payload was hidden inside Base64-encoded, GZIP-compressed content (‘contains Base64-encoded text for a GZIP-compressed payload’).
- [T1105 ] Ingress Tool Transfer – The malware downloaded additional scripts and a Mach-O binary from remote servers (‘retrieve and run a Mach-O binary’).
- [T1053.007 ] Scheduled Task/Job: Launchd – The plist file and helper scripts indicate persistence through macOS launch mechanisms (‘plist file named starter’, ‘.service’, ‘.mdworker’).
- [T1543.001 ] Create or Modify System Process: Launch Agent – The malware created persistent helper components in application support directories to run on startup (‘a shell script that runs a Mach-O file’).
- [T1119 ] Automated Collection – The stealer gathered multiple categories of local data into a staging archive (‘collected and temporarily saved information … compressed the data into a file named out.zip’).
- [T1005 ] Data from Local System – The archive included local files and application data such as browser, wallet, and Telegram artifacts (‘FileGrabber’, ‘Telegram Data/’).
- [T1041 ] Exfiltration Over C2 Channel – The infection sent HTTP POST requests to a command-and-control server (‘Post-infection traffic consisted mainly of HTTP POST requests’).
- [T1217 ] Browser Session Cookie – The data collection paths and reported credential theft indicate browser-related theft activity (‘stage=credentials’, ‘stage=browsers’).
Indicators of Compromise
- [Domain ] malicious installer page and initial download host – getmacouscloud[.]com, ferncore13[.]com
- [IP address ] command-and-control servers used during infection – 161.35.146[.]120, 188.166.78[.]138
- [URL ] initial Zsh script download and follow-on payload paths – hxxps[:]//ferncore13[.]com/curl/608e70d1338612686917ee5cd300ff7ed8e318dfd787a50257f92142e99bd688, hxxps[:]//grove-89[.]com/api/metrics/run?event=pasted
- [File hash ] AMOS-related samples and binaries – 71781ad8adefb499aee9bcbe1a166e69ccc37a47066682f617d65c76d8cde88c, 6bfcdb4920383375b7e519918df7eb4db751b974b5571a15ce66b82478012620, and 3 more hashes
- [File path ] installer and persistent malware locations – /tmp/helper, /Users/[username]/Library/Application Support/.com.apple.accountsd/AccountsHelper
- [File name ] dropped/persistent artifacts used in the infection – starter, .service, .mdworker, mdworker_shared, out.zip
- [Directory path ] persistence and staging locations – /Library/Application Support/.com.apple.accountsd/, /Library/Application Support/.com.apple.metadata.mds/, /tmp/
- [Stage strings ] C2 URL markers observed in post-infection requests – stage=boot, stage=credentials, and other 6 items
Read more: https://unit42.paloaltonetworks.com/atomic-macos-amos-stealer-activity/