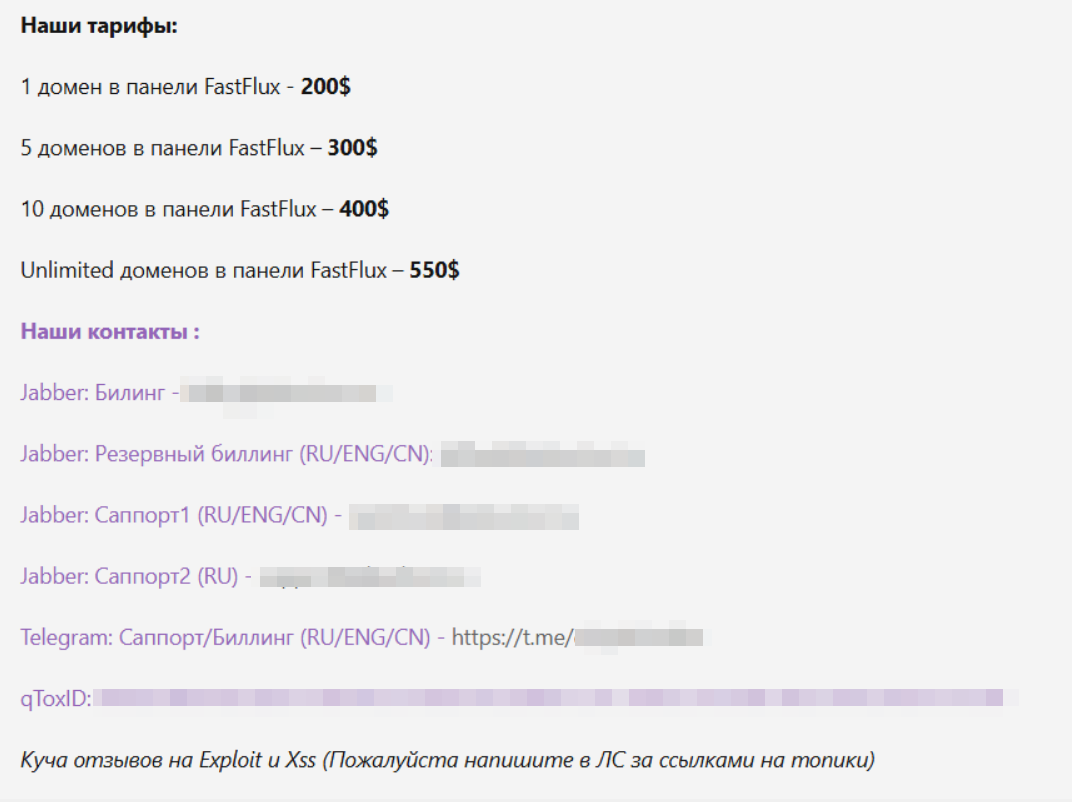
Silent Push reports that fast flux has become a more mature and accessible service for phishing operators, enabling large-scale domain rotation that defeats traditional IP blocking and hides malicious infrastructure. Their research uncovered thousands of live phishing domains, including a Canada-first banking campaign and other callback-phishing operations, while also mapping provider behaviors, detection opportunities, and defensive guidance tied to CISA recommendations. #SilentPush #FastFlux #CISA #Keitaro #MediaLand #ShadowRelay
Keypoints
- Fast flux now functions as a rented service, making it easier for threat actors to run phishing and other malicious operations while complicating detection.
- Silent Push studied the infrastructure from inside by buying a fast-flux service and using the findings to build detection analytics.
- A single query in the Silent Push platform surfaced thousands of live phishing domains, including a large Canada-first banking campaign hidden behind traffic-distribution cloaking.
- The Canadian campaign used Keitaro and victim-specific landing pages, with live operator interaction, credential theft, and fake OTP or verification flows.
- A second cluster supported callback phishing, impersonating fraud teams and security centers while delivering cloned login forms and malicious Windows binaries.
- The research identified fast-flux market activity advertised on criminal forums, including offerings linked to Media Land and a service called ShadowRelay.
- Recommended defenses include DNS-level fast-flux analytics, reputation-based filtering, and use of IOFA feeds to block delegation-layer infrastructure early.
MITRE Techniques
- [T1090.001 ] Proxy: Internal Proxy – Fast flux rotates victim connections through changing proxy infrastructure to hide the true hosting location (‘the technique of rapidly rotating a domain’s DNS records across many IP addresses and networks to avoid detection’).
- [T1568.001 ] Dynamic Resolution: Fast Flux DNS – The operation repeatedly changes DNS answers so the same domain resolves to different IPs over time (‘a single domain rotates across a constantly changing pool of IPs’).
- [T1036 ] Masquerading – Domains and pages impersonate legitimate brands and services such as banks, Canada Post, fraud teams, and security centers (‘bank look-alikes’, ‘pose as “fraud team,” “security centre,” and “live help” pages’).
- [T1566 ] Phishing – The infrastructure is used to lure victims into entering credentials and interacting with fake login or verification pages (‘phishing campaigns’, ‘full cloned login forms’).
- [T1056.001 ] Input Capture: Keylogging – The operator receives keystrokes before form submission, capturing victim input in real time (‘receives keystrokes before form submission’).
- [T1110 ] Brute Force – Stolen credentials are tested against the real bank in parallel to the phishing interaction (‘testing the stolen credentials against the real bank in parallel’).
- [T1204.001 ] User Execution: Malicious Link – Victims are directed to per-user entry URLs and lure pages via text-message-style phishing flows (‘links distributed by text message’, ‘single-use, per-victim entry URL’).
- [T1105 ] Ingress Tool Transfer – A Windows executable is delivered to the victim as part of the fake verification workflow (‘pushes a Windows executable’, ‘password-protected ZIP’).
- [T1071.001 ] Application Layer Protocol: Web Protocols – The phishing kits and callback pages use web forms, live chat, and HTTP endpoints to collect and relay data (‘posts the victim’s username and password to a security.php endpoint’).
Indicators of Compromise
- [Domain names ] Phishing and lure infrastructure – canada-post11[.]com, etranferts[.]com, and other impersonation domains
- [DNS nameserver / delegation ] Fast-flux detection layer – a.dnspod.com, provider-controlled DNS delegation signature
- [File name / path ] Victim-specific landing and credential endpoints – security.php, verify-download.php, and a generated per-victim PHP entry path
- [IP addresses / ASN diversity ] Rotating fast-flux infrastructure – 20 IPs across 13 ASNs over 90 days, plus ASNs 14956 and 58061
- [Brand / service impersonation targets ] Used in phishing lures – Canada Post, Interac e-Transfer, Wise, and major Canadian banks
- [Archive / delivery artifact ] Malicious payload packaging – password-protected ZIP containing a Windows executable