SEVENOAKS s.r.o., a Prague-based Czech Republic enterprise operating in Computer Systems Design and Related Services (3.3 GB), was targeted by ransomware from threat actor emperador. The incident impacted Czech Republic #CzechRepublic
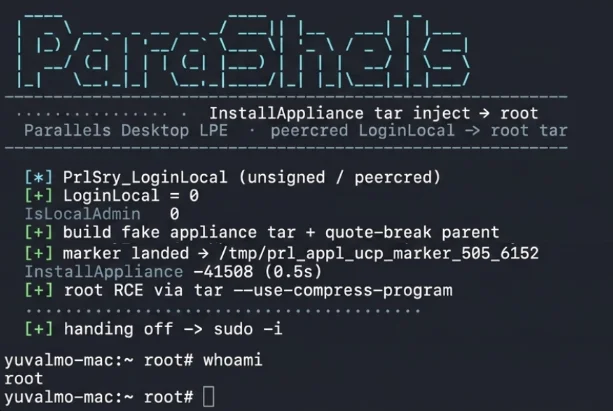
JFrog disclosed CVE-2026-90894, a Parallels Desktop flaw dubbed “ParaShells” that can let any local user on a Mac escalate to root on the host. The issue affects Parallels Desktop for Mac v26.4.0 on Apple ARM-based systems and was fixed by Alludo in Parallels Desktop v27.0.0. #CVE-2026-90894 #ParaShells #ParallelsDesktop #Alludo
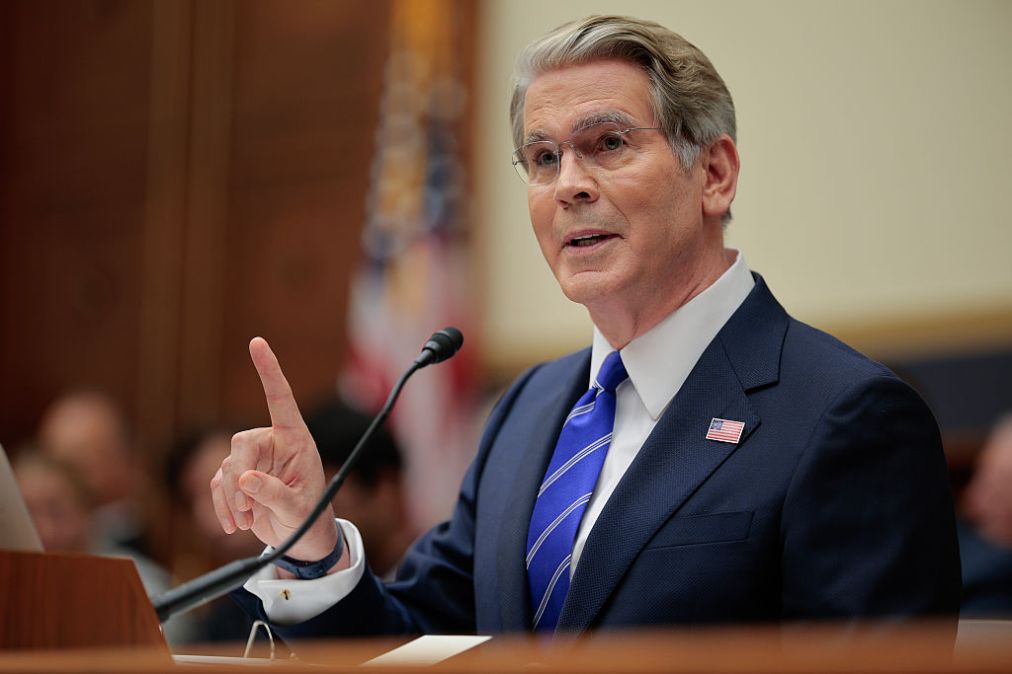
Treasury Secretary Scott Bessent urged lawmakers not to grant AI labs liability exemptions, arguing that creators should be held responsible for what they build and generate. He also said Treasury is working on AI safety after the Mythos model release and is coordinating with banks and labs through Gold Eagle and other discussions. #ScottBessent #Mythos #Anthropic #GoldEagle #HuggingFace
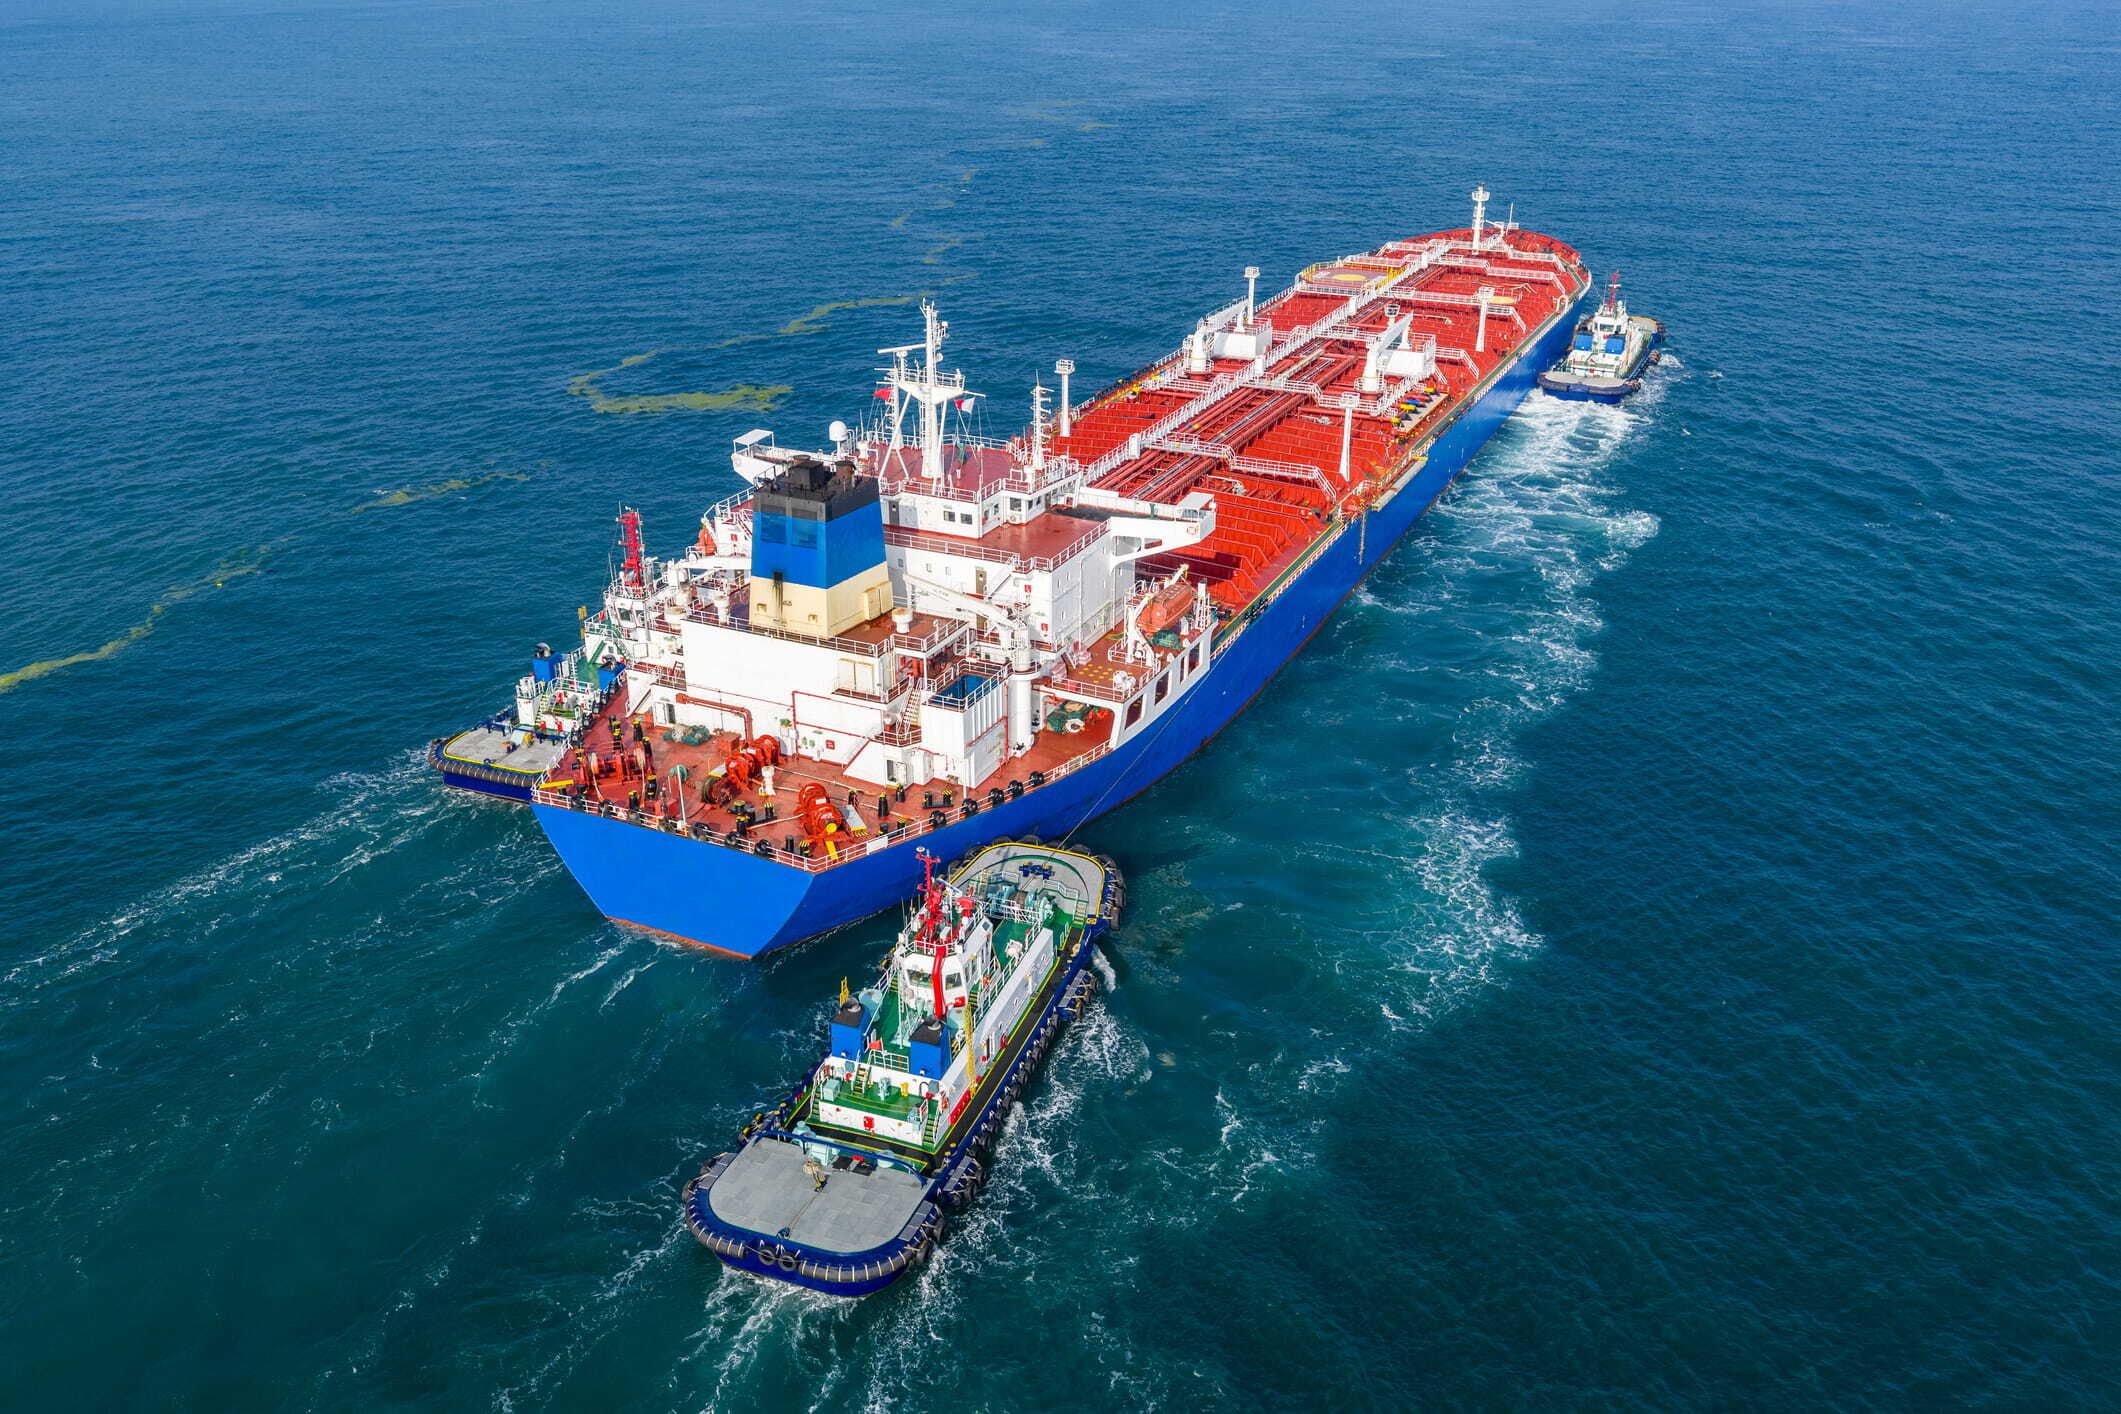
The Coast Guard and FBI boarded two foreign tankers in the Gulf of Mexico after indications that both ships’ networks were compromised, but no operational disruptions or safety impacts have been reported. Investigators are examining possible links to Iran and broader risks tied to “dark fleets” carrying sanctioned oil. #CoastGuard #FBI #Iran #GulfofMexico
This issue of The Cybersecurity Pulse covers major security news, including AI safety debates, Anthropic’s report on stolen API keys, and active exploitation of flaws in PaperCut, Cisco, GitLab, and Microsoft authentication workflows. It also highlights new funding and product launches from Exein, Splunk, Zscaler, DigiCert, and AIUC, showing how defensive security is evolving around AI, identity, and embedded systems. #Anthropic #PaperCut #Cisco #Microsoft #Splunk #Exein #Zscaler #DigiCert #GitLab #AIUC

A forum actor named seraphims is advertising an alleged Generation Tux customer dataset with more than 2.8 million records, claiming it was taken in an August 2026 breach via authentication-bypass SQL injection. The unverified listing says the data includes names, emails, phone numbers, password hashes, and address details, and is being…
A forum actor known as ChimeraZ is claiming to sell a JSON database tied to IAD Group – NosRezo, a French professional referral network, with data on 413,722 people. The unverified listing says the archive contains customer and advisor contact details, service information, and fee amounts, and it is being offered…
A forum actor calling themselves mrwho claims to be selling the full bf.st codebase and database, alleging the forum was compromised during its launch period through a vulnerability in the forum implementation. The post shows a 128-table database listing and sample user records, but the claim remains unverified and payment is…
Attackers are exploiting a critical ConnectWise ScreenConnect vulnerability in the wild, prompting CISA to add it to its actively exploited catalog and order federal agencies to secure systems quickly. The flaw, tracked as CVE-2026-84869, can let attackers with basic privileges transfer or execute files, and more than 1,000 exposed instances remain unpatched online. #ConnectWise #ScreenConnect #CVE-2026-84869 #CISA #Shadowserver
This webinar from BleepingComputer and Material Security will examine real Google Workspace breaches and the critical decisions security teams must make in the first hours after discovering suspicious access. It will also explore how social engineering and malicious OAuth applications enabled access, and which controls can best protect fast-growing companies. #BleepingComputer #MaterialSecurity #GoogleWorkspace #OAuth
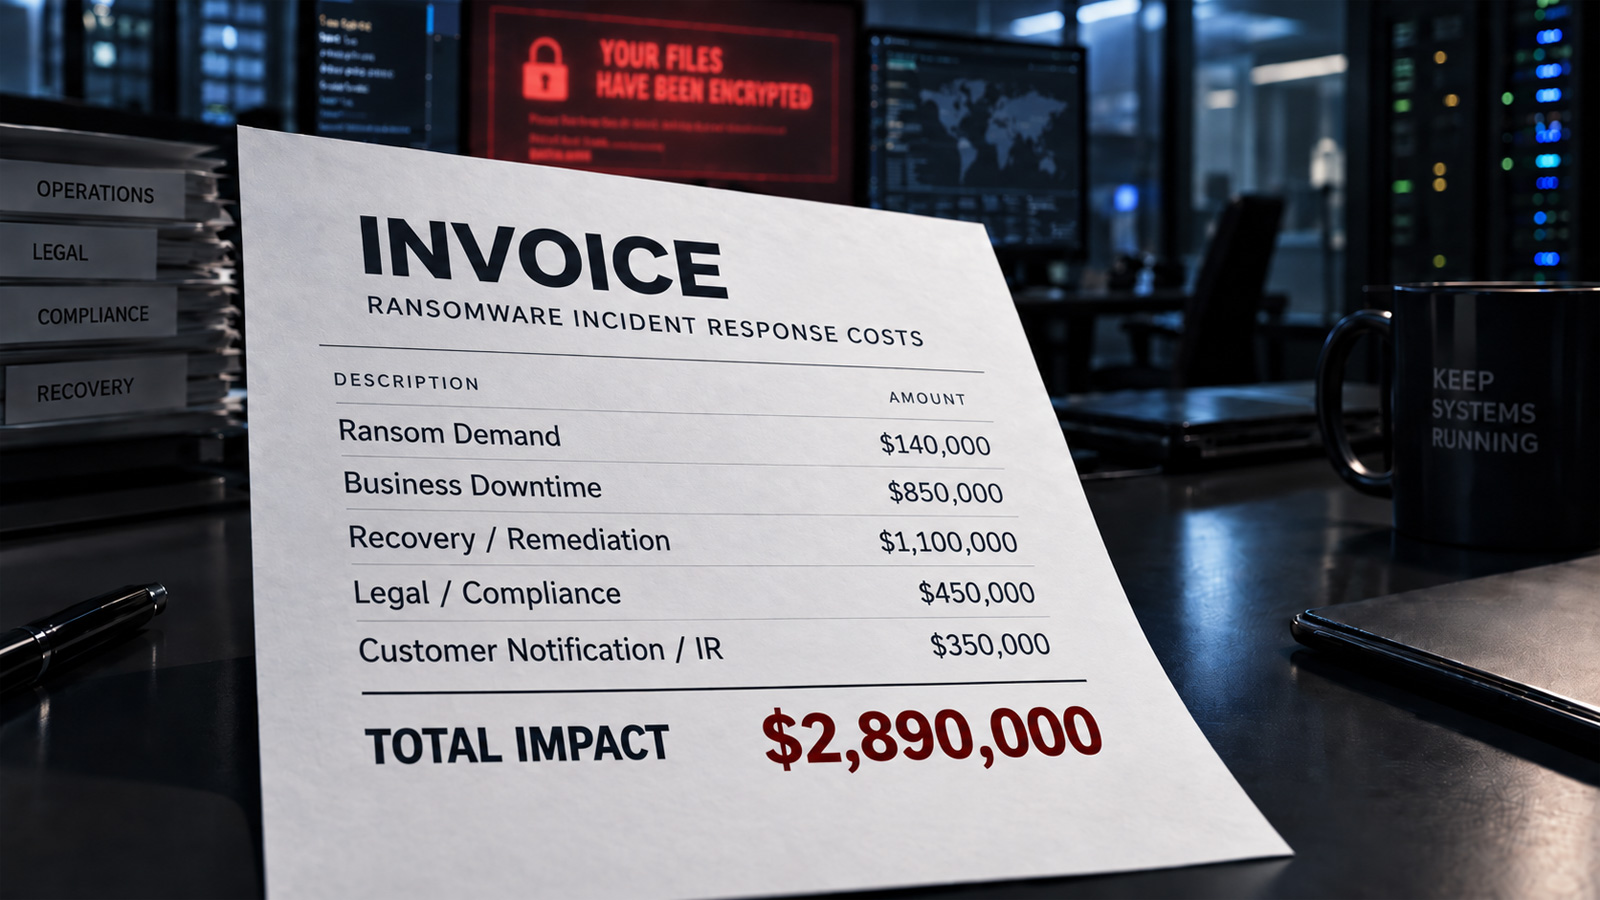
Ransomware costs far more than the ransom itself, with downtime, recovery, legal work, compliance, and business disruption driving the total impact to millions of dollars. A mature BCDR strategy can reduce recovery time, protect backups, and help organizations return to operations faster after an attack. #Datto #BCDR #GDPR #SEC #HIPAA #Techify
The Spanish Data Protection Agency (AEPD) was notified of a suspected AI agent attack that reportedly found vulnerabilities, logged into systems, modified personal data, and accessed financial documents. The incident highlights how AI-driven attacks can increase speed, scale, and adaptability, prompting a review of security and data protection models. #AEPD #OpenAI #GoogleGemini #AnthropicClaude #HuggingFace

The Spanish Data Protection Agency (AEPD) has reported what appears to be the first known personal data breach carried out by an AI agent that chained together multiple stages of an attack. The incident raises new concerns about agentic AI, as defenders may need faster detection, containment, and response tools to…
RatHat is a novel Android malware linked to China-based threat actors that uses smishing, malvertising, Accessibility abuse, and local ADB self-pairing to gain shell-level control and persist on devices. It steals banking and payment credentials, OTP/2FA codes, and lock-screen secrets while using AI-driven automation, covert tunnels, and self-restoring persistence to maintain access. #RatHat #Zimperium #AccessibilityService #ADB #frpc

The ransomhouse ransomware group targeted the Namibian Defence Force (Namibia), seeking ransom after compromising its systems. The Namibian Defence Force comprises the national military forces of Namibia, created after Namibia gained independence from apartheid South Africa in 1990. #Namibia