Keypoints
- Bessent opposed liability exemptions for frontier AI labs.
- He said AI creators should be liable for harms from their models.
- Treasury has focused on AI safety since the Mythos release.
- The administration has worked with AI labs and banks after the Hugging Face cyberattack.
- Bessent backed more U.S. open-source AI to counter China and avoid regulatory capture.
The secretary told House Financial Services Committee lawmakers that the “best way to guarantee safety” is for AI creators to be held “liable for what they build and generate.”
Listen to this article
0:00
Learn more.
This feature uses an automated voice, which may result in occasional errors in pronunciation, tone, or sentiment.
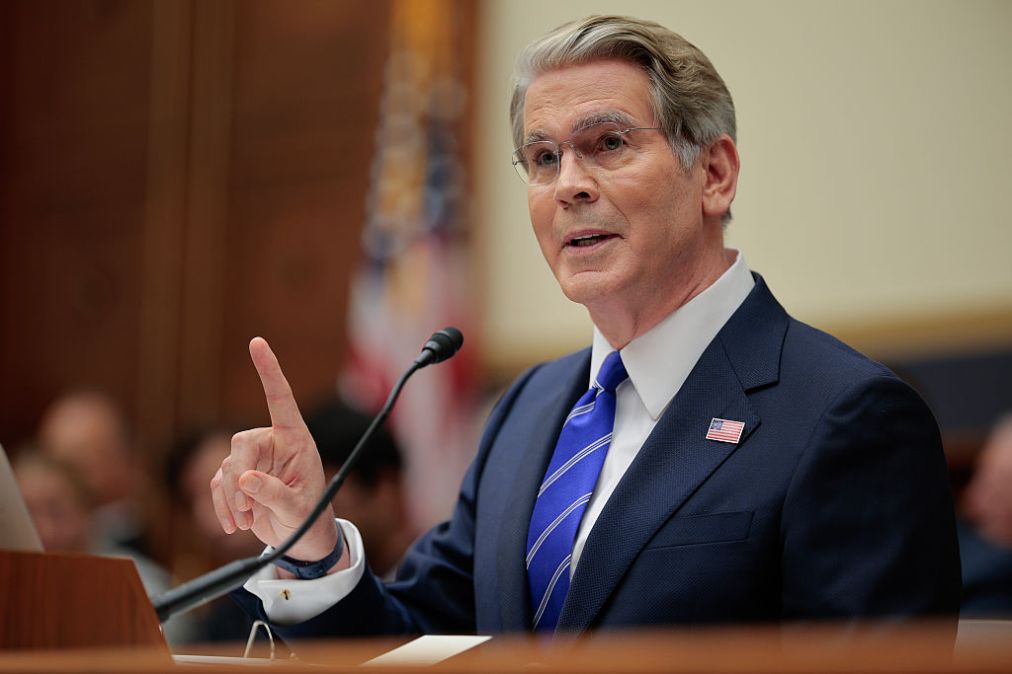
Treasury Secretary Scott Bessent testifies during a House Financial Services Committee hearing in the Rayburn House Office Building on Capitol Hill on Sept.15, 2026 in Washington, D.C. (Photo by Chip Somodevilla/Getty Images)
As calls for an AI slowdown and stronger safety measures around the emerging technology grow louder, Treasury Secretary Scott Bessent urged lawmakers Tuesday to not give in to frontier labs on liability exemptions.
Appearing before the House Financial Services Committee, Bessent was asked by Rep. Juan Vargas, D-Calif., what the Trump administration is doing for AI safety.
Bessent said the department has been “working on safety nonstop since the release of Mythos,” the Anthropic model whose cybersecurity risks prompted an April meeting at Treasury headquarters between the secretary, then-Fed Chair Jerome Powell and bank CEOs.
But going forward, he said it’s clear that what the government “shouldn’t do on safety is to give these labs a liability exemption, which is what they are asking for.”
“The best way to guarantee safety is that the creators are liable for what they build and generate,” Bessent continued.
The Treasury secretary’s comments came days after Anthropic’s Dario Amodei penned an essay calling on AI companies to tap the brakes on model development amid increasingly stark warnings about the technology’s potential dangers.
Though President Donald Trump rejected calls to ease the pace of AI development, OpenAI’s Sam Altman and xAI’s Elon Musk backed Amodei’s slowdown plan.
The Anthropic head’s plan included a note for the federal government to “issue a narrow waiver for certain kinds of safety conversations” while industry works toward voluntary standards. OpenAI, meanwhile, previously backed an Illinois bill to limit liability for AI-fueled harms.
When asked by Vargas to expand a bit on the issue of liability exemptions, Bessent doubled down on his stance.
“The one thing we should not do is give [AI labs] a blank check on liability,” he said. “Because I believe that the best liability, or the best safety guard, is that they will be held responsible. And they are saying that ‘we would like to all slow down, but please give us a waiver on liability,’ which should not be done. And I would encourage everyone in this committee and in both houses not to consider that.”
Liability waivers weren’t the only AI-related topic that came up Tuesday before the committee.
Bessent told Rep. Ritchie Torres, D-N.Y., later in the hearing that in the wake of the Hugging Face cyberattack in July, the administration has huddled with AI labs and the financial sector on AI safety discussions. He applauded the “largest banks” for having “very good cybersecurity resilience.”
Treasury’s coordination with big financial institutions on AI and cybersecurity has been more formalized in recent months with the launch of Gold Eagle, a clearinghouse it oversees with the Cybersecurity and Infrastructure Security Agency that coordinates vulnerability scanning, validation, and patch distribution.
“Our mandate is with the financial sector,” Bessent told Rep. Josh Gottheimer, D-N.J. “And then we have attempted to migrate that knowledge and the learning from the financial sector into other sectors through the Gold Eagle forum.”
Bessent also called for the development of more open-source models built in the United States as a way to “push back against China.”
“We can’t let these large labs have regulatory capture because that will stop innovation,” he said.