
AhnLab SEcurity intelligence Center found ransomware being delivered through a private HTS called UBP Asset, which appears to have been abused by an investment fraud ring that lured victims via Telegram and Band. The attack installed KRSID ransomware through modified HTS components and used a fraud site impersonating Union Bancaire Privee…
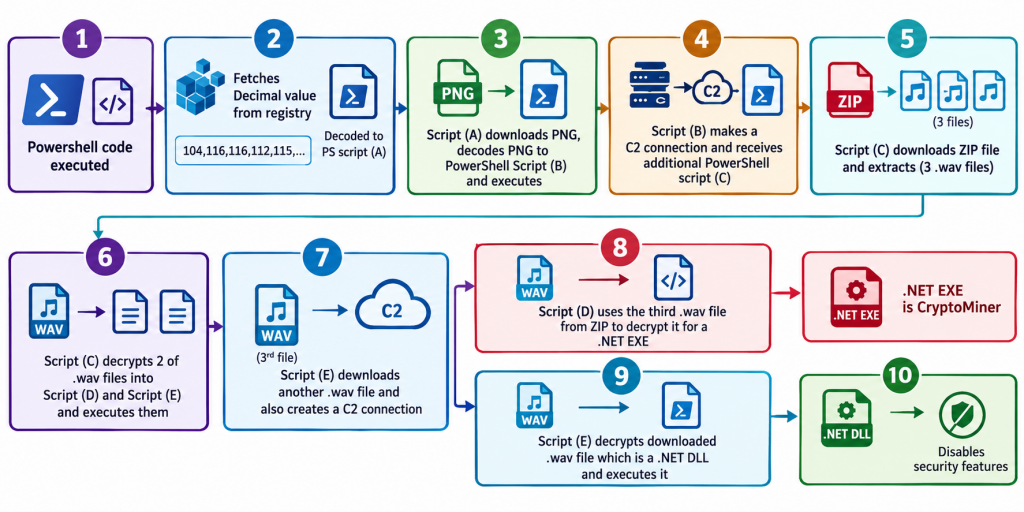
Researchers analyzed a multi-stage infection that used Registry-stored PowerShell, DNS TXT records, PNG and WAV file payload containers, and in-memory .NET loading to hide its activity. The chain ultimately deployed an XMRig-based cryptocurrency miner while maintaining a separate C2 channel and weakening Microsoft Defender and PowerShell logging controls. #XMRig #WinRing0.sys #RealtekHDAudio.wav #sslvalidcert.com #httptls.org
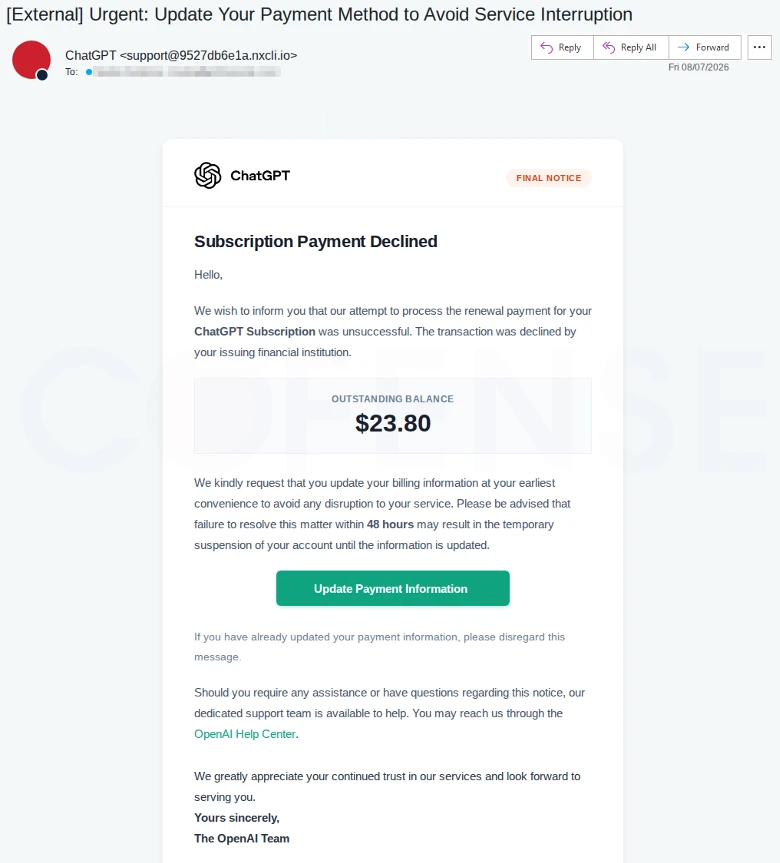
A fake ChatGPT billing email is luring users to a counterfeit OpenAI login page that steals any username and password entered. Cofense traced the attack through a Google redirect and identified indicators tied to the nxcli[.]io host, while urging users to verify the address bar shows auth.openai.com before signing in. #ChatGPT #OpenAI #Cofense #nxcliio

Cisco disclosed CVE-2026-76460, a maximum-severity zero-day in Cisco Identity Services Engine (ISE) that was actively exploited before patching. The flaw lets a remote attacker bypass authentication, take full control of the device, and potentially move laterally across networks managed by ISE. #Cisco #CiscoISE #CVE-2026-76460

AI cybersecurity capabilities are converging quickly, with GPT-6, Mythos, DeepSeek, Kimi, and GLM all narrowing the gap across frontier and open-weight models. The real advantage is shifting away from the model itself and toward proprietary context, workflows, evaluation, and trust that help defenders act safely. #GPT-6 #Mythos #DeepSeek #Kimi #GLM #OpenAI #Anthropic #MoonshotAI #Zai
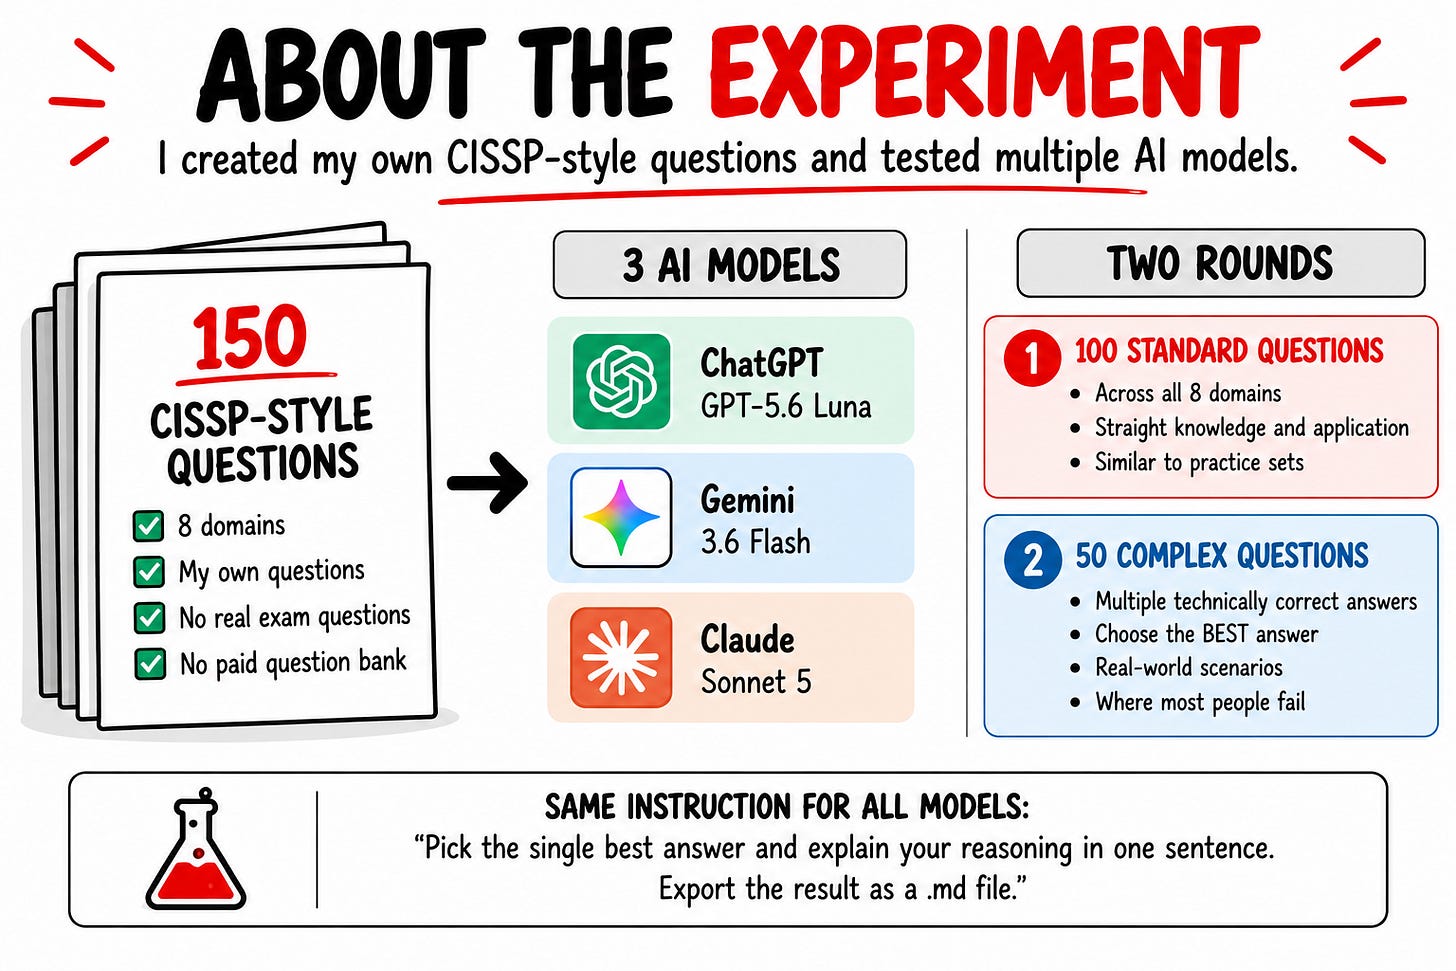
Erich tested ChatGPT, Gemini, and Claude on 150 CISSP-style questions across all eight domains, and all three models scored 150/150. The article argues that AI can excel at recognition-based exam questions, but cybersecurity professionals still need judgment, context, and decision-making in real-world situations. #CISSP #ChatGPT #Gemini #Claude #ErichWinkler

A forum actor using the name Alduin allegedly posted data tied to the Greffe du Tribunal des Activités Économiques de Paris, including records for judges, clerks, magistrates, lawyers, and other administrative staff. The claimed files contain names, emails, API login fields, phone numbers, home addresses, and internal court-related information, but the…
A forum actor posting as Alduin claims to have exposed Zenfirst user, lead, and invoice records, including personal, company, and billing-related data in JSON/JSONL files. The leak is unverified, but if authentic it could enable phishing, invoice fraud, and business email compromise using sensitive details such as invoice numbers, due dates,…
A forum actor posting as spain claims to have released the full updated database of Integra Energía, affecting more than 300,000 customers in Spain. The alleged dataset includes sensitive customer, banking, billing, and electricity-consumption records, but the claim remains unverified. #IntegraEnergía #Spain #spain #IBAN #CUPS…
The European Commission has proposed the EU KIDS Act to block children under 13 from social media and require stricter safety-by-design rules for platforms, including age verification, private-by-default profiles, and limits on addictive features. The plan faces support from many European governments but also strong criticism from tech lobbyists and digital…

Attackers are now exploiting new vulnerabilities in about five days, while many organizations take 43 days to patch, making annual pentesting too slow to keep up. The guide argues that autonomous AI agents can deliver continuous, provable, and validated coverage for web applications, but only if leaders demand strong governance, guardrails,…

A new CVE may look severe, but the real question is whether it can actually be exploited in your environment before defenders validate the risk. The webinar “How to Prove You’re Ready for Mythos-Class Attacks” shows how to replace severity-only prioritization with a faster CVE-to-validation workflow for Mythos-class attacks. #Mythos…
EVA Airways detected a malicious infiltration of its internal network through suspicious IP addresses on September 15, 2026, and confirmed that some employees’ names and business contact details were accessed. The company said it quickly implemented protective measures, notified regulators, and that its operations and services were not affected. #EVAAirways
Evergreen Aviation Technologies Corporation detected a cyberattack targeting certain internal information systems on 2026-09-15 and quickly isolated the affected access points. A forensic investigation is underway with external technical support, while core operations continue normally and no sensitive personal data exposure has been identified. #EvergreenAviationTechnologiesCorporation
Socket researchers found malicious code in the dev-main version of visanduma/nova-two-factor, a Packagist package linked to the broader PolinRider campaign that spreads through compromised developer accounts and Git repositories. The campaign uses Git-based intrusion, hidden payloads, and staged delivery to reach developer environments and later-stage infostealers, while also targeting PHP projects with a new shell_exec execution method. #PolinRider #visanduma/nova-two-factor #Packagist #LaHiRu