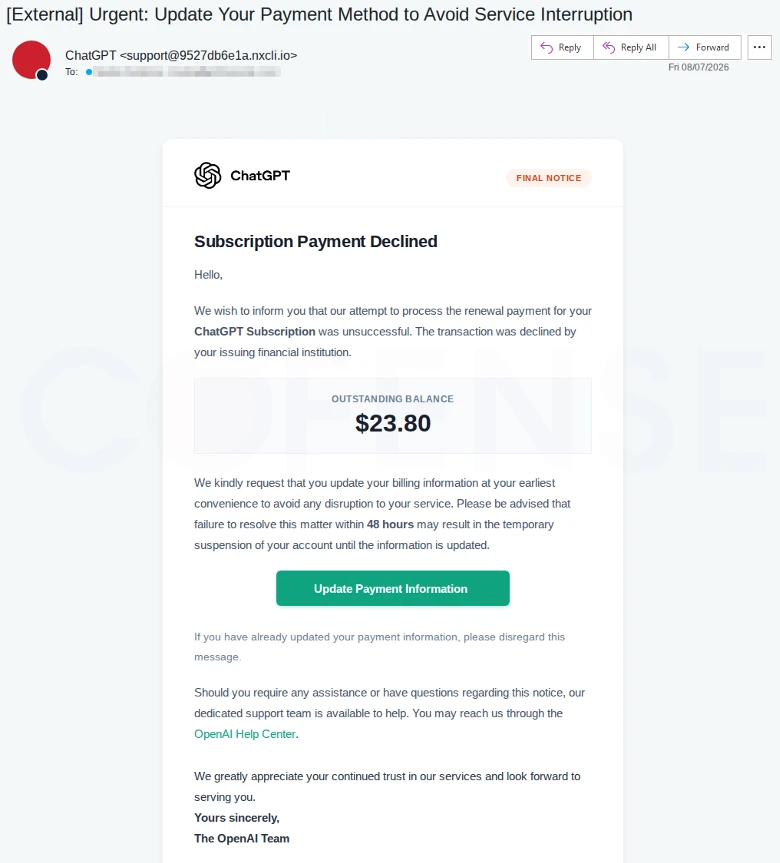
A fake ChatGPT billing email is luring users to a counterfeit OpenAI login page that steals any username and password entered. Cofense traced the attack through a Google redirect and identified indicators tied to the nxcli[.]io host, while urging users to verify the address bar shows auth.openai.com before signing in. #ChatGPT #OpenAI #Cofense #nxcliio
Keypoints
- The phishing email impersonates ChatGPT with a fake payment warning and urgent deadline.
- The message uses OpenAI branding, an outstanding balance, and a “final notice” tag to pressure clicks.
- The payment button redirects through notifications.googleapis.com before reaching the attacker’s site.
- The fake login page captures entered credentials and then sends victims to an error page.
- Cofense advises checking that the sign-in page is auth.openai.com and blocking the listed indicators.
Read More: https://www.helpnetsecurity.com/2026/09/17/chatgpt-phishing-email-openai-password/