A forum actor using the handle “SaltMobile” is claiming to sell a scraped customer dataset tied to Salt Mobile, a Swiss telecommunications provider, with more than 1.09 million records. The unverified listing reportedly includes names, dates of birth, addresses, email addresses, phone numbers, and timestamps, raising concerns about phishing, SIM-swap attempts,…

A forum actor known as GoreSpiders claims to have leaked an iChargePoint database containing 154,944 user accounts after an alleged employee compromise and unpaid ransom demand. The unverified dataset is said to include phone numbers, IP addresses, geolocation details, device information, and payment and order identifiers. #iChargePoint #GoreSpiders…
A forum actor using the name ChimeraZ is offering alleged partial datasets tied to FFTIR, SIA, and Armurerie Lavaux, claiming they include records for 120,158 people across France and Belgium. The unverified listing appears to expose names, phone numbers, addresses, and firearm or ammunition purchase details, creating potential privacy and physical-security…

The ransomware incident targeting hygear.com in Germany was attributed to lockbit5, the Threat Actor known for encrypting victim systems and demanding ransom. yGear specializes in providing reliable and affordable on-site and on-demand hydrogen and industrial services, and the attack disrupted operations within the impacted infrastructure in #Germany
Panzer ransomware impacted K3G Solutions Brazil, a telecom/IT consulting company based in Manaus providing network engineering, ISP support, monitoring, call-center, CDN, and colocation services. The attack caused disruption across K3G’s operations in BR #Brazil
Anubis ransomware targeted Quest Group, encrypting employee data and internal files, while leaving a few unexpected discoveries in its wake. The claim does not specify an impacted country, so the impacted country(s) is listed as #unknown
North Korean hackers linked to WaterPlum, also known as Contagious Interview, are posing as AI companies and other employers to target job seekers, especially software developers and IT professionals. The campaign has infected more than 30,000 devices worldwide and helped move nearly $11 million in cryptocurrency to North Korea through stolen credentials and fake recruiting schemes. #WaterPlum #ContagiousInterview #NorthKorea #FBI
Researchers used Anthropic’s Claude and OpenAI’s Codex to uncover HEIF Heist, a flaw in popular image decoding libraries that could expose sensitive data and enable remote access across major platforms. They warned that vulnerable deployments of libheif and libde265 could put OpenAI, AWS, Meta, GitHub Enterprise, and Discourse systems at risk if patches are not applied. #HEIFHeist #libheif #libde265 #OpenAI #AWS #Meta #GitHubEnterprise #Discourse

Ahmed Hossam Eldin Elbadawy, a core member of Scattered Spider, pleaded guilty to wire fraud conspiracy and aggravated identity theft in connection with extortion attacks from 2021 to 2023. Prosecutors say he and his co-conspirators stole company credentials and virtual currency from victims across entertainment, telecom, technology, cloud, IT, and virtual currency sectors. #ScatteredSpider #AhmedHossamEldinElbadawy #NoahMichaelUrban #TylerRobertBuchanan
Cybercrime is becoming increasingly industrialized, with AI accelerating the speed and scale of threats. Rébiah Bardot-Girard of AXA XL says resilience begins before an attack through strong people, governance, training, and tested crisis exercises. #AXAXL #RébiahBardotGirard
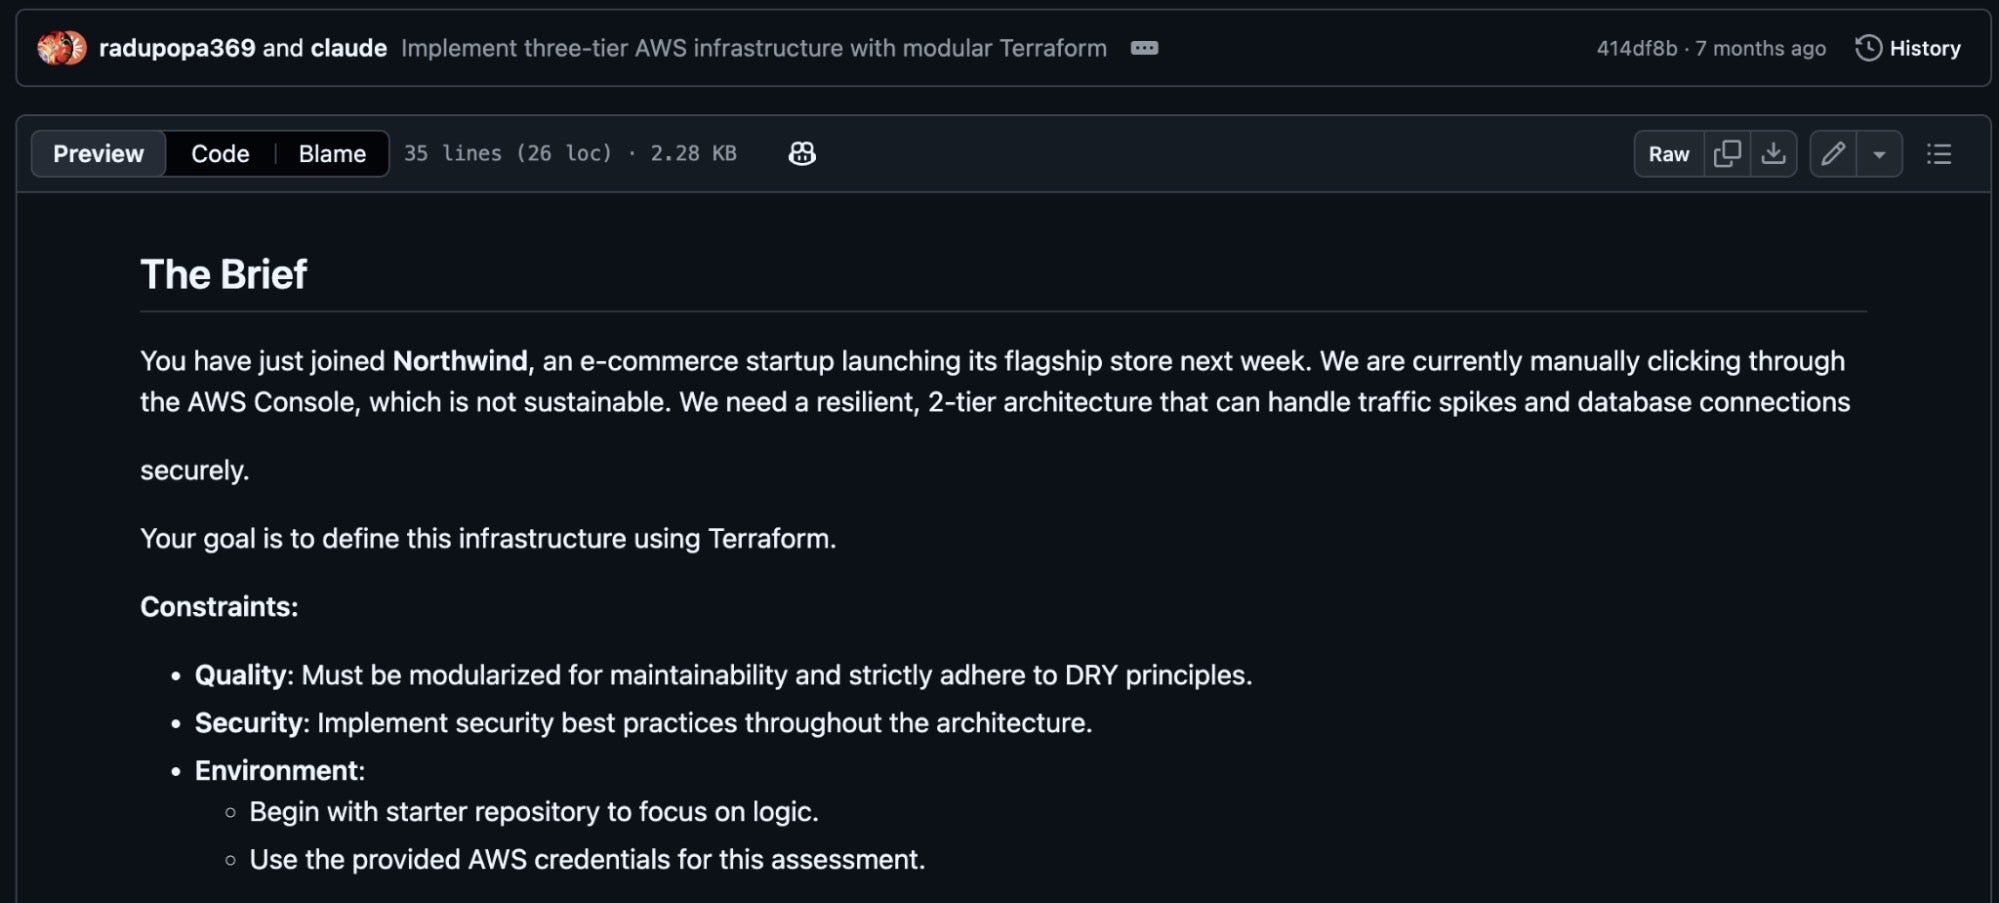
SentinelOne found a second victim of TraderTraitor’s macOS backdoors, showing that the DPRK-linked group also targeted an IT services company through fake job interview lures and weaponized Terraform repositories. The report details how FLATROOF and ROOFDECK were delivered, how ROOFDECK used Nostr-based dead drops and signed commands for C2, and how the campaign relied on typosquatted provider domains and malicious lock files. #TraderTraitor #FLATROOF #ROOFDECK #LayerZero #KelpDAO #Nostr
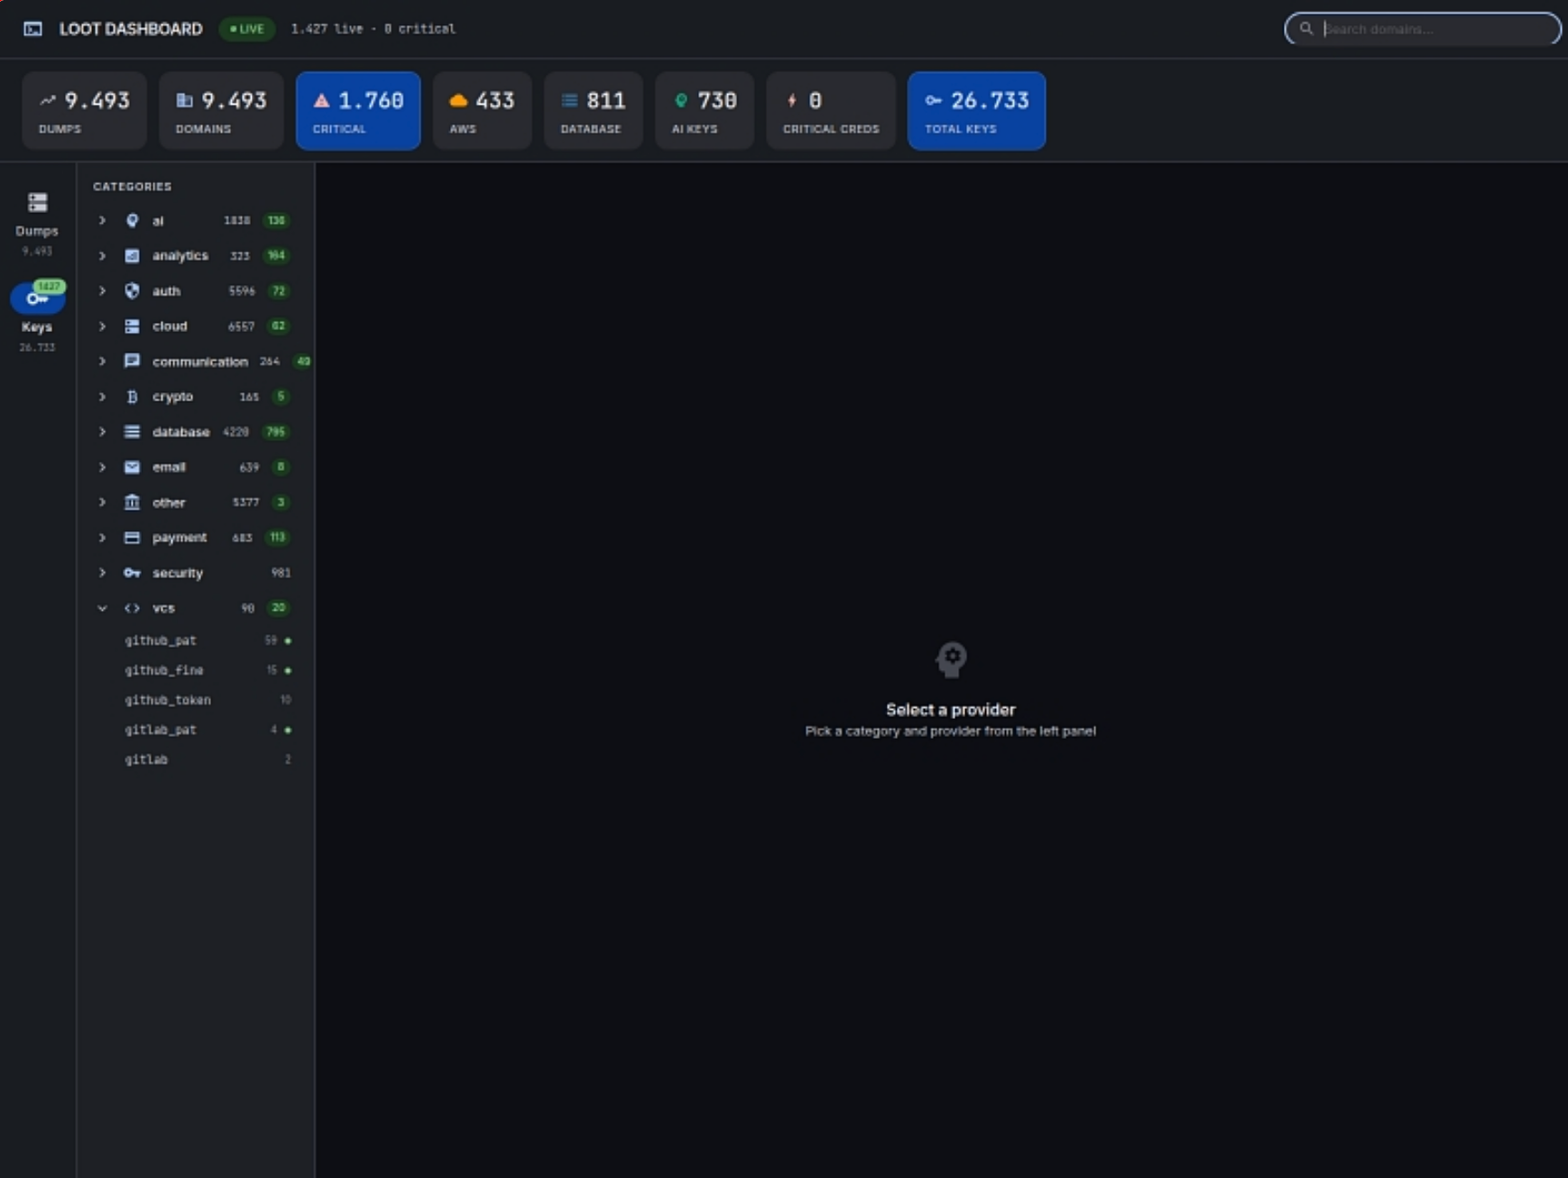
Datadog Security Research identified two unauthenticated credential-harvesting platforms, Loot and UltraVault, that inventory, validate, and operationalize stolen secrets, including AWS and AI service credentials. The activity shows AI-assisted attack workflows, active re-probing of credentials, and exploitation chains tied to vulnerabilities such as react2shell, wp2shell, xss2shell, and joomla2shell. #Datadog #Loot #UltraVault #AmazonBedrock #Anthropic #OpenAI #AWS #CVE-2025-55182 #CVE-2026-63030 #CVE-2026-60137 #CVE-2026-64638 #CVE-2026-48907
A malware campaign is using SEO-optimized GitHub repositories to impersonate LastPass and dozens of other software firms in order to distribute the newly observed Rapuncel information stealer. The chain also installs the Alinubx.sys kernel driver, which is signed through Microsoft and can terminate 145 antivirus and EDR products while stealing credentials, browser data, and wallet information. #LastPass #DelphosLabs #Rapuncel #Alinubxsys #Microsoft
Gyazo confirmed a data breach after attackers exploited a server vulnerability and stole approximately 23.62 million user records, prompting the company to take the service offline for maintenance. The incident also exposed 490 million image metadata records, including details that could potentially help access private images, and users are being urged to change passwords and watch for suspicious activity. #Gyazo #Helpfeel

Transparent Tribe (APT36/Earth Karkaddan) has launched Operation RapidRust against government and defense entities in India and Afghanistan using newly identified tools and typosquatted domains. The campaign relies on private GitHub repositories, Rust-based backdoors, and cross-platform stealers to support stealthy command-and-control, data theft, and USB-based propagation. #TransparentTribe #APT36 #EarthKarkaddan #OperationRapidRust #RUSTYSHADE #RUSTYMOVE…