
Check Point said attackers used a zero-day flaw, CVE-2026-93616, to target Security Management Servers in limited attacks on July 23, and the company later released fixes and hunting guidance. Separately, attackers have been trying to exploit CVE-2026-85102 in Spark firewalls and gateways through VPN connections since September 12, using anonymizing infrastructure…
BigCommerce merchants were hit by a supply chain attack after attackers compromised a Ribon application key and used it to steal customer data from affected storefronts. BigCommerce says the incident stemmed from third-party app credentials tied to Be A Part Of and Fastr, not a breach of its own platform. #BigCommerce…

Universal Auto Group (universalautogroup.com) in the US reported a ransomware incident in which thousands of documents were allegedly stolen by threat actor settra. The attack impacted businesses and operations in #UnitedStates
N0n ransomware targeting AFRICA-TECH (IT services/document processing) in Mali has fully stopped operations after encrypting or destroying shared client document repositories, including scans, attestations, insurance, and embassy files. Recovery is not possible without settlement, with all backups and shadow copies encrypted or destroyed. #Mali
Shinyhunters (claiming to have compromised FBI systems including CJ, HR, Medlink, and more) issued a PSA threatening to expose sensitive data about FBI agents and applicants unless the 2026 Quarter 2 FLASH report is corrected or removed within one week. The message denies it is ransomware/extortion and includes no specified victim country, ending with: #unknown.
Intelligence Center 3.9 adds broader LLM connectivity, including Azure, Claude models, and Mistral, while expanding support for MITRE ATT&CK v19.1 to keep threat mappings aligned with the latest framework changes. The release also delivers workflow improvements such as faster attachment spotting, clearer vendor integration pricing, and more flexible date and time defaults. #IntelligenceCenter #MITREATT&CKv19.1 #Azure #Claude #Mistral
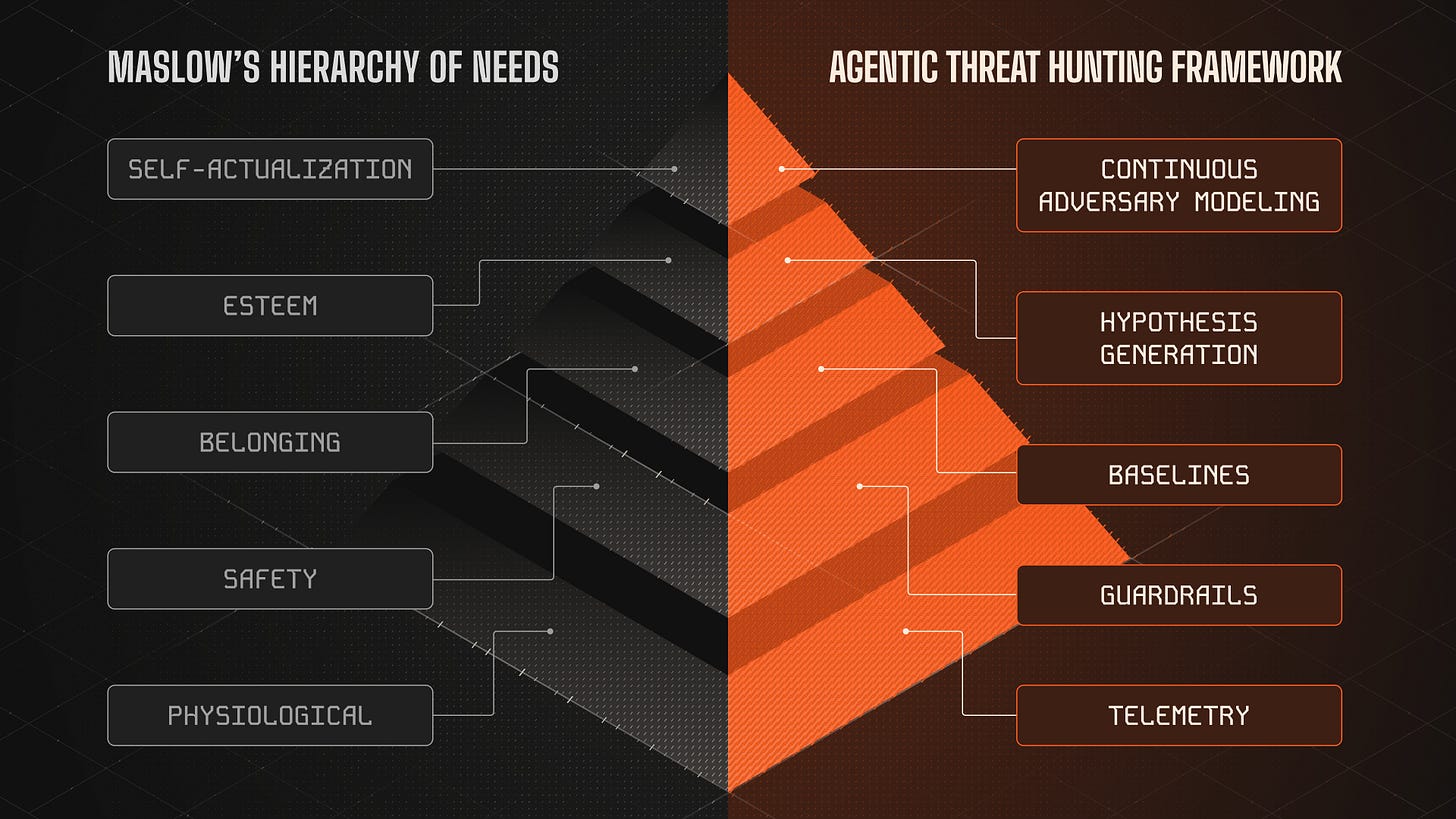
Agentic threat hunting only works when the SOC has strong telemetry, clear baselines, and guardrails, because AI amplifies existing gaps instead of fixing them. Sydney Marrone’s framework shows that tools like ATHF, ADEF, LOCK, and FORGE help teams build the foundation needed for effective hunting and detection engineering. #SydneyMarrone #Nebulock #Splunk #THORCollective #ATHF #ADEF #LOCK #FORGE
ShinyHunters reportedly hacked the CLOP darkweb site, claiming to have stolen data and demanding a large ransom from the Russian cybercrime group. This rival-on-rival attack shows criminal groups undermining each other instead of focusing on additional victims. #ShinyHunters #CLOP
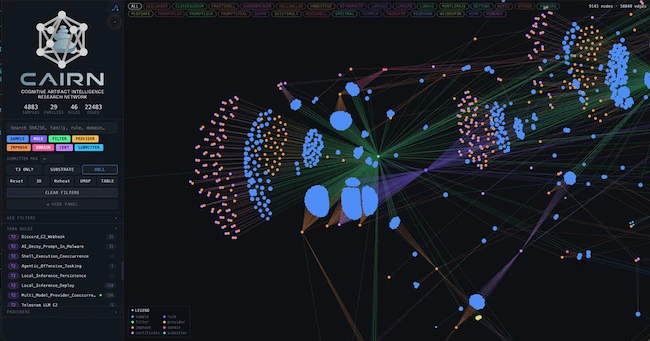
Cisco Talos released CAIRN, an open-source framework that classifies AI-integrated malware using only file metadata and cognitive artifacts, without downloading or executing samples. Their first public finding is CLOSEDQUORUM, a Windows implant that uses multiple commercial LLMs to decide its next move and is designed to steal credentials and crypto wallets. #CiscoTalos #CAIRN #CLOSEDQUORUM #LAMEHUG #CERT-UA #DeepSeek #Qwen #Mistral #Gemini
Microsoft and industry partners disrupted EvilTokens, a phishing-as-a-service platform tied to more than 12,000 compromised Microsoft customer email inboxes across over 10,000 organizations worldwide. The operation used AI-driven tools to support business-email compromise and financial fraud, while law enforcement arrested two suspected operators in the U.K. and seized key infrastructure. #EvilTokens #Microsoft #Storm-2992 #FelixUtomi #WaidiSegunAdams

President Donald Trump defended a hands-off approach to AI regulation even after hacks involving U.S. commercial frontier models intensified calls for oversight. The debate now centers on whether innovation and U.S. competition with China should outweigh stricter safety and liability rules for companies like OpenAI and Anthropic. #DonaldTrump #OpenAI #Anthropic #China
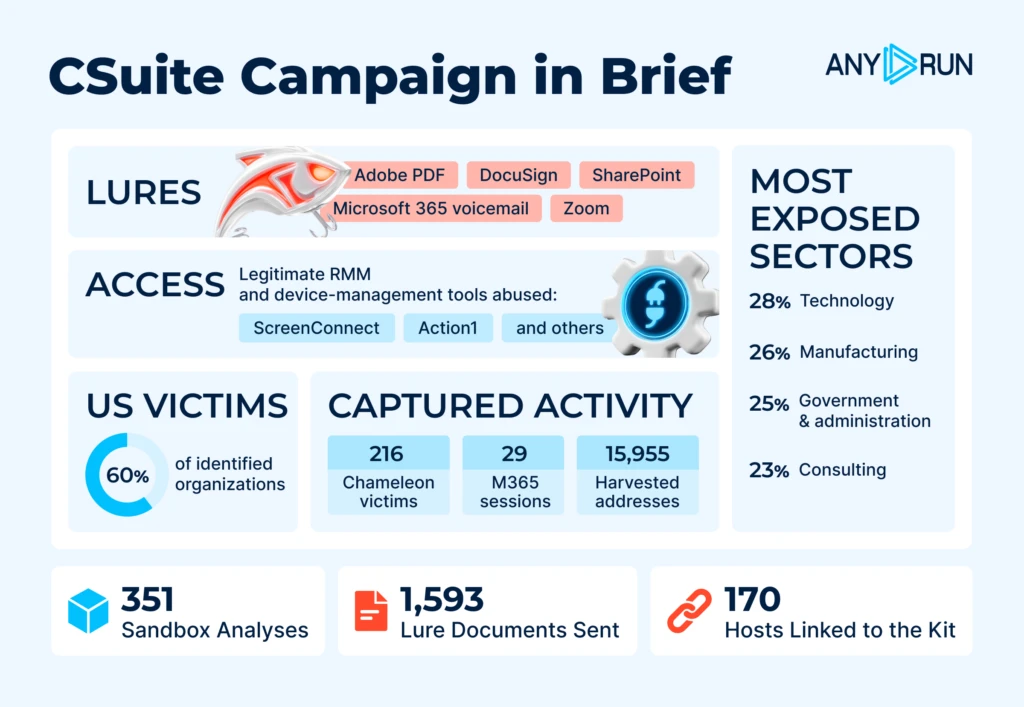
CSuite is a multi-stage phishing and remote-access operation that combines credential theft, Microsoft 365 session hijacking, and delivery of legitimate management tools to compromise both identities and endpoints. The campaign heavily targets US organizations and uses trusted brands like Adobe, DocuSign, Zoom, SharePoint, and Microsoft 365, with shared infrastructure linking the…
Microsoft and its partners disrupted the EvilTokens phishing-as-a-service platform, which compromised more than 12,000 Microsoft accounts across over 10,000 organizations worldwide. The operation used device-code phishing and AI-powered tools to evade MFA, target high-value inboxes, and drive business email compromise campaigns. #EvilTokens #Storm2992 #Microsoft #SpyCloud #HealthISAC
Abdelhamid Naceri, also known as Nightmare Eclipse, has publicly revealed his identity and released BigDiskBuster, a new proof-of-concept exploit that interferes with Windows Defender platform and signature updates. He says the tool works on all supported Windows versions, though it remains buggy, and he also recounted a bitter dispute with Microsoft…
Cyera has secured an additional $400 million in funding from Goldman Sachs Alternatives, lifting its valuation to more than $12 billion and bringing total funding to over $2.7 billion. The company plans to use the capital to expand its agentless data security platform, strengthen AI governance capabilities, and support its growth…