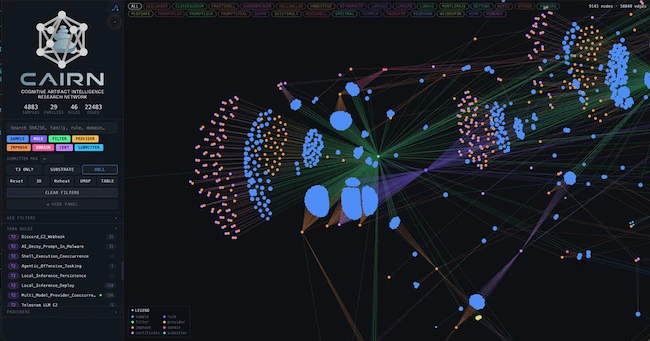
Cisco Talos released CAIRN, an open-source framework that classifies AI-integrated malware using only file metadata and cognitive artifacts, without downloading or executing samples. Their first public finding is CLOSEDQUORUM, a Windows implant that uses multiple commercial LLMs to decide its next move and is designed to steal credentials and crypto wallets. #CiscoTalos #CAIRN #CLOSEDQUORUM #LAMEHUG #CERT-UA #DeepSeek #Qwen #Mistral #Gemini
Keypoints
- CAIRN analyzes malware using metadata only, with no need to run the sample.
- The framework looks for cognitive artifacts such as embedded prompts and AI provider endpoints.
- CAIRN uses three tiers to separate AI-related strings, operational behavior, and named malware families.
- Talos traced AI-specific evasion tricks across unrelated malware samples within 12 months.
- CLOSEDQUORUM delegates tactical decisions to multiple LLMs and avoids a traditional attacker-controlled C2 server.
Read More: https://www.helpnetsecurity.com/2026/09/22/cairn-open-source-framework-ai-malware-closedquorum/