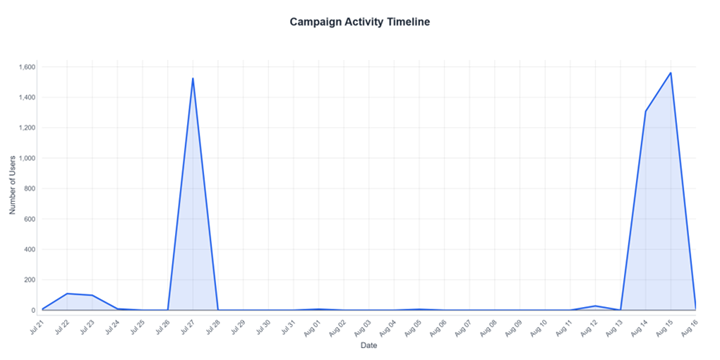
Proofpoint identified UNK_CondorFiltration, an active TeamFiltration campaign that targeted more than 5,700 Microsoft 365 accounts across 28 tenants in Latin America, with a strong focus on Chilean organizations. All seven successful compromises were dormant service accounts with default or predictable passwords and no MFA, and at least one case showed follow-on activity from a German VPN node against Microsoft 365 and Azure services. #TeamFiltration #UNK_CondorFiltration #Microsoft365 #AzurePortal #SharePointOnline
Keypoints
- Proofpoint tracked the campaign as UNK_CondorFiltration and linked it to TeamFiltration based on a hardcoded user agent.
- The attack targeted 5,714 unique accounts across 28 Microsoft 365 tenants, generating 32,825 authentication events.
- The activity was heavily concentrated in Chile, especially against a major retailer that accounted for 78.3% of observed events.
- All 7 compromised accounts were unmanaged functional or service accounts with no legitimate login history.
- The compromises strongly suggest default or predictable passwords that had never been rotated, combined with no MFA enforcement.
- Post-compromise activity included access to Microsoft Office, OneDrive, SharePoint Online, Azure Portal, and attempted corporate VPN access.
- The campaign relied on AWS EC2 infrastructure for spraying and a German VPN node for post-access probing and reconnaissance.
MITRE Techniques
- [T1110.003] Password Spraying – The attacker tested common or default passwords across many accounts in bulk, yielding compromises on dormant service accounts (‘The attacker likely sprayed accounts with default passwords’ and ‘initial compromise via password spray’).
- [T1580] Cloud Infrastructure Discovery – TeamFiltration enumerated accounts and validated their existence through Microsoft 365/Teams services (‘Validates account existence at ~300 emails/sec via the Teams API’).
- [T1078.004] Valid Accounts: Cloud Accounts – The attacker used successfully guessed credentials to sign in to Microsoft 365 accounts (‘All 7 successfully compromised accounts were unmanaged functional/service accounts’).
- [T1021.002] Remote Services: SMB/Cloud Services Access? – The attacker accessed cloud services after login, including Azure Portal and SharePoint Online (‘accessed several Azure apps, including OfficeHome, Azure Portal, and SharePoint Online’).
- [T1213] Data from Information Repositories – TeamFiltration auto-exfiltrated email, chats, and files from Microsoft 365 repositories (‘harvests email, Teams chats, OneDrive/SharePoint files, and Graph API data automatically’).
- [T1105] Ingress Tool Transfer – The backdoor mode could plant or replace files on OneDrive to trigger later execution (‘silently replace files… enabling an attacker to plant malicious files’).
- [T1021.007] Remote Services: Cloud Services – The attacker probed the corporate VPN, Azure Portal, and Microsoft 365 portals from a German VPN node (‘began a post-access sequence: probing the corporate VPN, accessing Azure Portal, browsing SharePoint’).
- [T1528] Steal Application Access Token – The SharePoint Online Web Client Extensibility activity requested an access token for Microsoft Graph or external APIs (‘requested an access token to interact with Microsoft Graph or external APIs’).
Indicators of Compromise
- [User Agent] Hardcoded TeamFiltration client fingerprint used during spraying – Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Teams/1.3.00.30866 Chrome/80.0.3987.165 Electron/8.5.1 Safari/537.36
- [IP Ranges] Primary AWS EC2 spray infrastructure – 3.101.0.0/16, 18.144.76.0/24, and 13.52.201.0/24
- [IP Address] Post-access German VPN node used for probing and portal access – 149.88.104.19
- [Domain / Host] AWS infrastructure and cloud-resolved source locations – amazon.com, cdn77.com, and datacamp.co.uk
- [Application IDs] Microsoft 365 applications accessed during compromise – 1fec8e78-bce4-4aaf-ab1b-5451cc387264, d3590ed6-52b3-4102-aeff-aad2292ab01c, and 00000003-0000-0ff1-ce00-000000000000
Read more: https://www.proofpoint.com/us/blog/threat-insight/Spraying-in-the-Andes-TeamFiltration-Returns