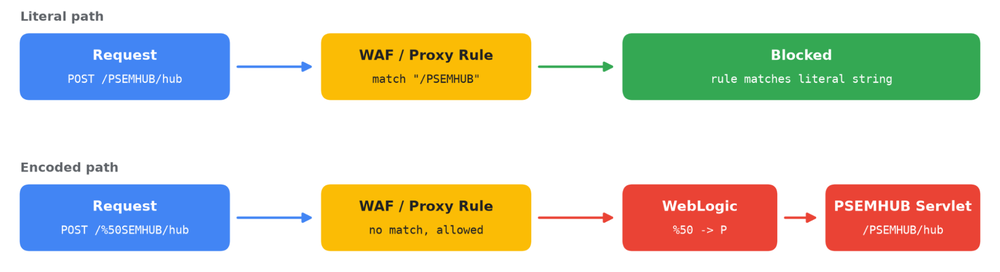
Mandiant and GTIG report renewed mass exploitation of CVE-2026-35273 in Oracle PeopleSoft by UNC6240 (ShinyHunters), using a URL-encoded WAF bypass to reach the vulnerable PSEMHUB endpoint and deploy web shells worldwide. The campaign expanded beyond education into technology, IT services, healthcare, agriculture, transportation, and government, and also involved SIDEEYE, Neo-reGeorg, and MeshCentral infrastructure. #CVE-2026-35273 #UNC6240 #ShinyHunters #OraclePeopleSoft #SIDEEYE #Neo-reGeorg #MeshCentral
The content reports 2 defacement incidents targeting Peru and the Dominican Republic, with the attackers identified as noko and azraelzer0d4y. Both incidents involved website defacements, and the countries mentioned are Peru and the Dominican Republic. #Peru #DominicanRepublic…

A post by the actor “IntelShadow” claims a large dataset linked to EUROCOP and the Valdemoro Local Police in Spain, with 13,349 files and 9.31 GB of compressed data allegedly uploaded. If authentic, the purported records could expose police reports, complaints, official communications, administrative files, vehicle documentation, and personal details tied…

ShinyHunters claims it infiltrated FBI systems by exploiting an undisclosed Oracle PeopleSoft vulnerability, then moved into the Bureau’s AWS GovCloud environment and exfiltrated 2 to 3 terabytes of sensitive records. The group says the attack was retaliation for an FBI alert issued in May, while the FBI says the incident is…

Termite ransomware actors targeted Crossett Home, a leading petroleum transporter based in the Eastern U.S. and Ontario, Canada, aiming to disrupt its operations and services. The attack impacted the United States and Canada. #UnitedStates #Canada
ANZ threat activity is dominated by identity- and access-driven compromise, with credential stuffing, stolen credentials, and initial-access broker sales recurring across financial services, manufacturing, and mining. Qilin is the most active cross-sector ransomware actor, while the report also highlights state-aligned pre-positioning by Volt Typhoon and Salt Typhoon, plus exploited vulnerabilities such as CVE-2023-20198, CVE-2025-59287, and CVE-2026-41940. #Qilin #VoltTyphoon #SaltTyphoon #CVE-2023-20198 #CVE-2025-59287 #CVE-2026-41940
Wallstreet ransomware allegedly targeted Ar Valve Resources, a Kent-based UK distributor of industrial valves and related equipment, potentially disrupting its product sourcing, technical support, documentation, and shipping operations. The claim indicates impacts to the affected organization in #UnitedKingdom
Threat actor emperador claims it compromised Electrolux and OnTrac, threatening to release stolen data about employees if the victims do not respond within one week, after both allegedly refused to discuss the breach. The claim includes references to salary information release for OnTrac and a listed email/session, but no impacted country is provided: #countryname
PKF Hadiwinata, a top-10 accounting and professional services firm in Indonesia headquartered in Jakarta, was targeted by the metaencryptor ransomware threat actor. The attack has impacted the firm’s operations in Indonesia. #Indonesia
Cameron John Wagenius, a former Army soldier, was sentenced to 70 months in prison for extorting telecom and cloud service victims, including AT&T, while using stolen data and hacked credentials. He and co-conspirators tied to the Snowflake breach stole sensitive records from multiple organizations and used the alias “kiberphant0m” in their cybercrime campaign. #AT&T #Snowflake #CameronJohnWagenius #ConnorMoucka #JohnErinBinns

Attackers can abuse SeManageVolumePrivilege to rewrite ACLs on C:Windows, gaining write access to protected system paths and escalating from a standard user to SYSTEM. The article shows three routes to compromise—Print Spooler DLL hijacking, WBEM tzres.dll substitution, and Windows Error Reporting abuse via WerTrigger—highlighting the danger of misconfiguring the “Perform volume maintenance tasks” right. #SeManageVolumePrivilege #SeManageVolumeExploit #Printconfig.dll #tzres.dll #WerTrigger #MSEDGEWIN10
Clop moved its data leak site to a new Tor address after its old server was defaced by ShinyHunters through an unpatched Grav CMS path traversal flaw. Grav confirmed the issue as CVE-2026-42608 and released a fix for the older 1.7 branch in version 1.7.53.4. #Clop #ShinyHunters #Grav #CVE202642608
Kiteworks has warned customers worldwide to shut down their servers for a six-hour window after receiving credible threat intelligence from law enforcement about a potentially imminent attack. The company says this is a precautionary measure, not a response to a confirmed breach, while concerns remain about possible zero-day targeting and the Clop extortion gang. #Kiteworks #Clop #BleepingComputer #Heise
Bitget said hackers stole at least $387.5 million from its exchange after a breach of its wallet services backend, with evidence pointing to North Korea-linked actors. The company has suspended withdrawals, brought in Mandiant and SlowMist, and plans to use its User Protection Fund to cover losses while recovery efforts continue….

A bipartisan coalition of 44 state attorneys general settled a lawsuit against Labcorp for $2.3 million after a 2019 data breach tied to its vendor American Medical Collection Agency exposed the personal information of 10.2 million customers. The agreement requires Labcorp to overhaul vendor oversight, strengthen security controls, and improve incident…