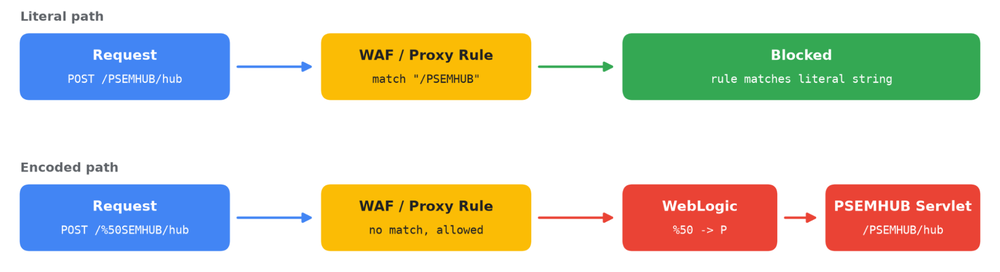
Mandiant and GTIG report renewed mass exploitation of CVE-2026-35273 in Oracle PeopleSoft by UNC6240 (ShinyHunters), using a URL-encoded WAF bypass to reach the vulnerable PSEMHUB endpoint and deploy web shells worldwide. The campaign expanded beyond education into technology, IT services, healthcare, agriculture, transportation, and government, and also involved SIDEEYE, Neo-reGeorg, and MeshCentral infrastructure. #CVE-2026-35273 #UNC6240 #ShinyHunters #OraclePeopleSoft #SIDEEYE #Neo-reGeorg #MeshCentral
Keypoints
- UNC6240 resumed exploiting CVE-2026-35273 after Oracle released a security alert.
- The group bypassed WAF rules by using a percent-encoded PSEMHUB path.
- Attackers deployed x.jsp and u.jsp web shells for command execution and file upload.
- Ple64.exe was used to load the SIDEEYE backdoor and enable persistent access.
- Neo-reGeorg tunneling and MeshAgent were used for lateral movement and remote control.