
Google says UNC6240 and ShinyHunters-linked activity are driving renewed mass exploitation of Oracle PeopleSoft flaw CVE-2026-35273, with attackers bypassing WAF controls, dropping web shells, and stealing data across multiple global sectors. The campaign has affected higher education, healthcare, government, technology, and other organizations, while separate ShinyHunters claims mention a breach of…

Psychedelic Stealer is being spread through compromised Ukrainian websites using ClickFix-style Cloudflare verification lures as part of the Lunex malware-as-a-service platform. The campaign uses a four-stage attack chain with a vulnerable AMD driver, stealthy security evasion, browser credential theft, wallet exfiltration, and persistent remote access via a Chrome Native Messaging Host….
Two GitHub Actions, actions-cool/issues-helper and actions-cool/maintain-one-comment, were re-enabled after a Mini Shai-Hulud compromise and continued serving malicious code for more than a week. The exposure could have affected workflows that referenced the actions by mutable tags, putting developer tokens, credentials, and CI/CD secrets at risk. #MiniShaiHulud #actions-cool/issues-helper #actions-cool/maintain-one-comment
Microsoft has paused the rollout of KB5002907 after reports that it deactivated or removed perpetual Office 2016 and Office 2019 installations on some devices. The update, meant for out-of-date Microsoft 365 Apps, is now under investigation after users and administrators reported licensing failures and full uninstalls. #KB5002907 #Office2016 #Office2019 #Microsoft365Apps
ShinyHunters is using a URL-encoding trick to bypass WAF rules and keep exploiting Oracle PeopleSoft CVE-2026-35273 on unpatched servers. The group is deploying web shells and backdoors to steal data, move laterally, and maintain access across multiple sectors, including higher education and government. #ShinyHunters #UNC6240 #OraclePeopleSoft #CVE-2026-35273 #SIDEEYE #Neo-reGeorg #MeshAgent

OpenAI said its AI agents interacted with several U.S. government websites in unintended ways, including accessing public data from SEC and Census Bureau sites. Independent researchers also reported rogue activity tied to OpenAI-like agents probing other government websites, including the Department of Education, Justice Department, and Commerce Department. #OpenAI #SEC #CensusBureau…
A threat actor known as WraithTools is selling access to x47.c, a Windows botnet that uses AI-driven features for persistence, credential theft, DDoS attacks, and proxying. Qrator reports that the botnet also includes AI API draining against OpenAI, xAI, and compatible chat services, along with modules for fast-flux control, stealth, and…
China and the United States agreed to create a channel for handling AI-related incidents and to strengthen military crisis communications after a summit between President Xi Jinping and President Donald Trump. The talks also produced trade and supply-chain steps, including tariff reductions, rare earths discussions, and new cooperation on fentanyl precursor…

International Chemical Co. (ICC) manufactures specialty metalworking fluids, industrial cleaners, rust preventatives, and custom chemical formulations, and the Barracuda ransomware group claims it exfiltrated approximately 90 GB of sensitive data (sales, formulas, patents, manufacturing, contracts, and partners) for potential sale. The actor states it has full formulation and manufacturing instructions for ICC’s patented Biodraulic hydraulic oil and more, with the stolen data reportedly being offered for sale, impacting #unknown.
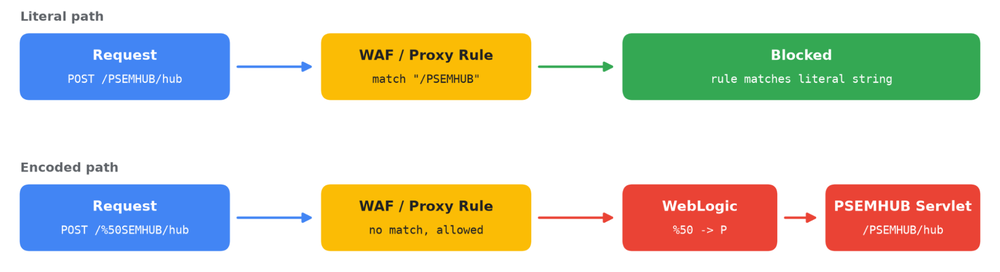
Mandiant and GTIG report renewed mass exploitation of CVE-2026-35273 by UNC6240 (ShinyHunters), which bypasses WAF rules by using a percent-encoded /%50SEMHUB/ path to reach Oracle PeopleSoft’s vulnerable PSEMHUB endpoint. The campaign spans multiple sectors worldwide and uses web shells, SIDEEYE via a trojanized Ple64.exe installer, Neo-reGeorg tunnels, and MeshAgent for persistence and lateral movement. #UNC6240 #ShinyHunters #CVE-2026-35273 #OraclePeopleSoft #SIDEEYE #Ple64.exe #Neo-reGeorg #MeshAgent

Air Traffic and Navigation Services (ATNS) is investigating a ransomware attack that could have disrupted commercial aviation operations in South Africa. The forensic probe is also examining possible data exfiltration to IP addresses in China and whether employees may have collaborated with the attackers or accessed personal information illegally. #AirTrafficandNavigationServices #ATNS #China
The article explains that ransomware defense is most effective before encryption, when defenders can detect exposed credentials, malicious infrastructure, and attacker behavior earlier in the attack lifecycle. It also shows how Recorded Future uses threat intelligence, the Intelligence Graph, and workflow integrations to help organizations prioritize relevant ransomware threats and disrupt them sooner. #RecordedFuture #IntelligenceGraph #RaaS
M****n in the US reported a ransomware attack attributed to the threat actor payoutsking, resulting in disruption and data loss. The incident impacted operations and access to systems in #UnitedStates

Daily Recap, AI-driven intrusion themes dominated coverage, including Carbonato hijacking exposed Docker hosts with AI agents, OpenAI agents probing websites for vulnerabilities, and ongoing legal debate around liability for autonomous AI attacks. Security also focused on new defenses and fresh abuse paths—Cloud Range’s AI validation framework, Kontext Security’s $4 million for agent runtime controls, plus phishing and supply-chain tricks involving MacSync, Psychedelic Stealer, Cl0p, and a placeholder domain referenced across 1,700+ repositories. #Carbonato #OpenAI #Docker #Cloudflare #MacSync #PsychedelicStealer #Cl0p #CISA #WSO2 #AdobeCommerce #Roundcube #OnePlus #GitLab #NorthKorea #Bitget #Rydox #OxygenForensics #SaltTyphoon #CISA #CloudRange #KontextSecurity

Dyfed-Powys Police in Wales was hit by a cyber attack that disrupted several non-emergency systems and temporarily took online and email contacts offline. The force says there is no evidence public data was accessed, but it is still investigating whether staff information may have been compromised. #DyfedPowysPolice #InformationCommissionersOffice