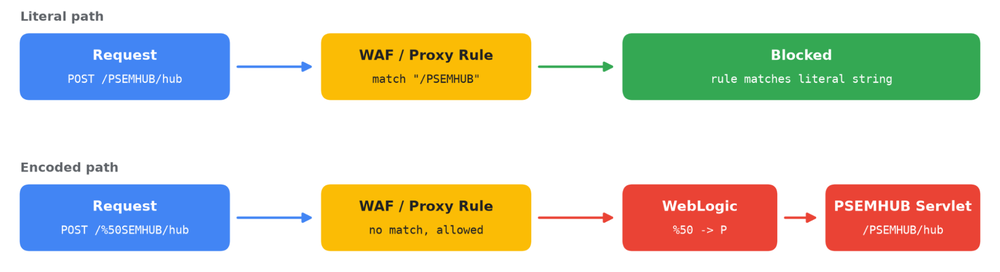
Mandiant and GTIG report renewed mass exploitation of CVE-2026-35273 by UNC6240 (ShinyHunters), which bypasses WAF rules by using a percent-encoded /%50SEMHUB/ path to reach Oracle PeopleSoft’s vulnerable PSEMHUB endpoint. The campaign spans multiple sectors worldwide and uses web shells, SIDEEYE via a trojanized Ple64.exe installer, Neo-reGeorg tunnels, and MeshAgent for persistence and lateral movement. #UNC6240 #ShinyHunters #CVE-2026-35273 #OraclePeopleSoft #SIDEEYE #Ple64.exe #Neo-reGeorg #MeshAgent
Keypoints
- UNC6240 renewed mass exploitation of CVE-2026-35273 after the initial June 2026 zero-day campaign.
- The group bypassed WAF rules by URL-encoding the P in /PSEMHUB/, using /%50SEMHUB/ to reach the vulnerable servlet.
- Targeting expanded beyond higher education to technology, IT services, healthcare, agriculture, transportation, and government.
- Attackers deployed web shells, including x.jsp and u.jsp, to enable command execution and chunked file upload.
- A trojanized installer named Ple64.exe delivered the SIDEEYE backdoor, which communicates with a C2 server over TCP ports 3333 and 3334.
- UNC6240 also staged Neo-reGeorg tunnels and MeshAgent to maintain access, proxy traffic, and support lateral movement.
- Mandiant advises patching Oracle PeopleSoft, disabling or removing EMHub/PSEMHUB where possible, and hunting for file, log, and network indicators.
MITRE Techniques
- [T1596.003 ] Search Open Technical Databases: Digital Certificates – Used to validate and sign the trojanized installer with a legitimate EV certificate (‘signed with a valid Extended Validation (EV) certificate’).
- [T1596.005 ] Search Open Technical Databases: Scan Databases – Used during reconnaissance for identifying targeted environments and related infrastructure (‘Search Open Technical Databases: Scan Databases’).
- [T1595.002 ] Active Scanning: Vulnerability Scanning – Used to identify and validate exploitable PeopleSoft systems before further activity (‘five to 15 POST requests to /%50SEMHUB/hub’).
- [T1190 ] Exploit Public-Facing Application – Exploited Oracle PeopleSoft CVE-2026-35273 through the exposed PSEMHUB endpoint (‘renewed mass exploitation of CVE-2026-35273’).
- [T1027 ] Obfuscated Files or Information – Hid commands and file content using hex encoding, Base64, and path encoding (‘URL-encoding a single character’, ‘hex-encoded commands’, ‘Base64-encoded file chunks’).
- [T1059.003 ] Command and Scripting Interpreter: Windows Command Shell – Ran commands through cmd.exe on Windows hosts (‘spawning cmd.exe’, ‘cmd.exe /c start /b’).
- [T1059.004 ] Command and Scripting Interpreter: Unix Shell – Ran commands through /bin/sh on Linux hosts (‘reconstructing /bin/sh from an ASCII character array’).
- [T1505.003 ] Server Software Component: Web Shell – Dropped JSP web shells into the PSEMHUB.war directory for persistent command execution (‘x.jsp’, ‘u.jsp’, ‘tunnel.jsp’).
- [T1082 ] System Information Discovery – Collected host details such as hostname, OS, and user context (‘hostname and whoami’).
- [T1016 ] System Network Configuration Discovery – Used network and environment checks as part of post-exploitation discovery (‘uname -a’).
- [T1552.001 ] Unsecured Credentials: Credentials In Files – Accessed PeopleSoft service-account-readable credentials and connection strings (‘database connection strings in psappsrv.cfg’).
- [T1090 ] Proxy – Used Neo-reGeorg to tunnel SOCKS5 traffic through HTTP/HTTPS for internal access (‘routes SOCKS5 proxy traffic through ordinary HTTP and HTTPS connections’).
- [T1219 ] Remote Access Software – Deployed MeshAgent/MeshCentral for persistent remote management (‘legitimate RMM tool MeshAgent’).
- [T1048 ] Exfiltration Over Alternative Protocol – Used raw TCP, SSH, rsync, and HTTP POST for data movement and backdoor C2 (‘over raw TCP’, ‘rsync (TCP 873)’).
Indicators of Compromise
- [IPv4 address ] Network indicators and C2/staging hosts – 5.199.162.157, 104.219.234.138, and 162.219.30.165
- [Domain ] MeshCentral-related infrastructure – winmanage-me.network, azurenetfiles.net, and microsoft-entra.net
- [File path ] Web shell and payload locations under PeopleSoft – /webserv//applications/peoplesoft/PSEMHUB.war/x.jsp, /webserv//applications/peoplesoft/PSEMHUB.war/u.jsp
- [File path ] Additional dropped files in the web archive – /webserv//applications/peoplesoft/PSEMHUB.war/tunnel.jsp, /webserv//applications/peoplesoft/PSEMHUB.war/Ple64.exe
- [File name ] Malicious JSP and executable files – x.jsp, u.jsp, Ple64.exe, and other 2 more files
- [SHA-256 hash ] File hashes for identified samples – 48b4a0827da7bbfce9fb52464f8a659dea7a035189c52c506c0bfb4b1c3fe494, 2bee941fb40519d0d1ec52bd79a8f63fc65aac6455c8f2d6b668e3360dfdb5d7, and other 3 more hashes
- [URI pattern ] WAF bypass and exploitation path – /%50SEMHUB/ and /%50SEMHUB/hub
- [TCP ports ] SIDEEYE C2 ports – TCP/3333 and TCP/3334