DAISEN (JP) suffered a ransomware attack attributed to threat actor AiLock, targeting its operations as a leading manufacturer specializing in greenhouses, vinyl houses, and daylight architecture. The incident resulted in disruption caused by the malware and its encryption of victim systems. #Japan
Armored Likho (Eagle Werewolf) ran a new cyber-espionage campaign in Russia using a fake donation app to deliver the Rust-based Still Toolkit, which includes Still Sync for Telegram data theft and Still Audio for covert voice surveillance. The campaign overlaps with earlier Armored Likho activity and uses infrastructure such as orderapiserver[.]info, tg4service[.]com, and srwinservice[.]com. #ArmoredLikho #EagleWerewolf #StillToolkit #StillSync #StillAudio
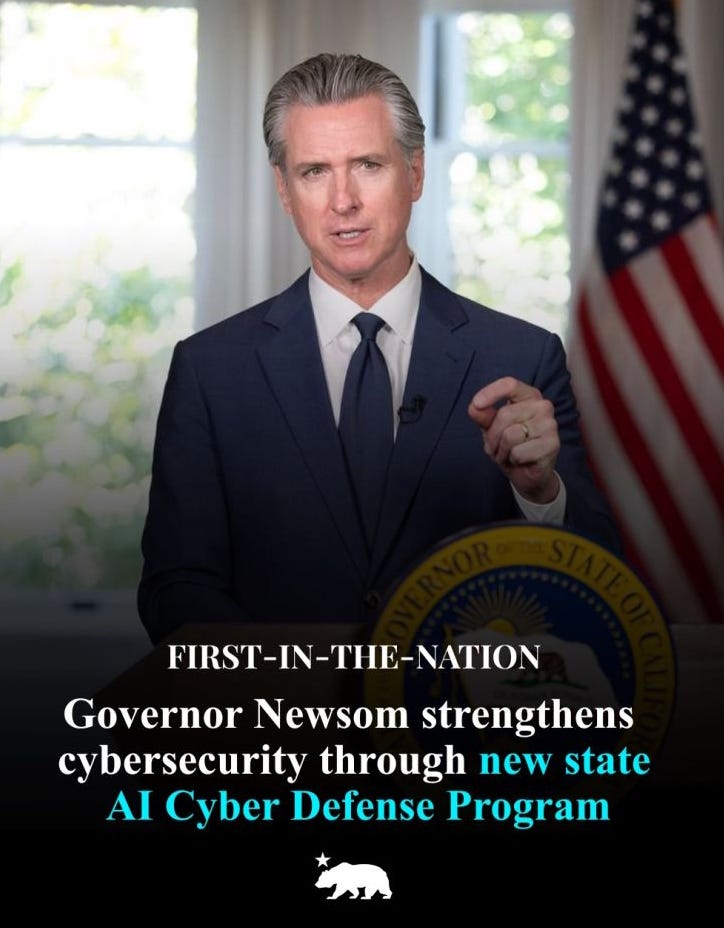
California Governor Gavin Newsom said the state will build stronger defenses to protect critical infrastructure and citizens in the face of growing AI-related risks. The announcement positions California as a leader in proactive AI cyber defense and digital trust. #California #GavinNewsom

An actor using the name exfilar claims to have exposed an unsecured Belgian consumer database containing 148,251 records, including bank account numbers, birth dates, names, addresses, and contact details. The alleged leak is unverified, but the combination of IBANs, home addresses, and dates of birth could enable fraud and impersonation. #Belgium…
Microsoft released fixes for 419 vulnerabilities in a record-setting Patch Tuesday, highlighting how AI-assisted flaw discovery is sharply accelerating the pace of software security issues. The update includes three zero-days, one actively exploited in the wild and linked to Lazarus Group, while the new clustered advisory format may make prioritizing patches…

Threat actors are actively exploiting CVE-2026-55040, a critical Microsoft SharePoint authentication bypass, after Rapid7 released proof-of-concept code. The attacks use forged JWT tokens to impersonate users and administrators, with telemetry showing 12 exploitation attempts across multiple countries and regions. #CVE-2026-55040 #MicrosoftSharePoint #Rapid7…

The ransomware threat actor incransom targeted diabetesandmetabolism.com, a US-based specialty endocrinology clinic in San Antonio, Texas, potentially disrupting the clinic’s operations and patient care. The claim specifically involves an attack against a Hospitals & Physicians Clinics organization serving patients with diabetes and other endocrine/metabolic conditions in the United States. #UnitedStates
Incransom targeted clgroup in the US, leveraging the ransomware to disrupt information technology and business operations. Victim: clgroup (US) #UnitedStates
Safeware Inc. (safewareinc.com), a US-based safety and security solutions provider for first responders, schools, and government agencies, was targeted by ransomware operations attributed to thegentlemen. The incident is reported as impacting the United States. #UnitedStates

There was 1 defacement incident targeting Mexico, with the site https://ixtlanmichoacan.gob.mx/cox.htm compromised. The attacker involved was Trenggalek Cyber Army. #Mexico…
Brighton East Dental Clinic (BEDC) in Australia, operating as BEDC.COM.AU, is a family dental practice providing comprehensive dental care across children’s dentistry, general, cosmetic, and preventative services, with evening hours and emergency support, employing 50 staff and generating about $5M annually. The ransomware claim attributed to threat actor incransom alleges disruption impacting Australia #australia
Qilin ransomware allegedly targeted United Association Local Union 345 in the US, compromising files and demanding ransom payments as part of an extortion scheme. The impacted country(s): #UnitedStates
The ransomware claim alleges that the threat actor nightspire targeted eas**** and encrypted or otherwise compromised the victim’s data; however, the available data details are not available now. The incident is reported without a specified origin country, so the impacted country is listed as #Unknown.
Britain’s ACRO Criminal Records Office was reprimanded by the ICO after repeated breaches over nearly two years exposed sensitive personal data, including information linked to domestic violence victims. The incidents involved unpatched Kentico flaws, ignored Trend Micro alerts, and an attempted Mimikatz deployment, with the Medusa ransomware group later claiming responsibility….
Reco has uncovered the City-Forum campaign, an ongoing data-theft operation that uses custom tools to steal records exposed to anonymous users in Salesforce Experience Cloud and ServiceNow portals. The activity is tied to the IP address 158.220.87.79 and has been linked to broad targeting of organizations worldwide, including attacks against Salesforce Aura and LWR sites as well as ServiceNow Service Portals. #CityForum #Salesforce #ServiceNow #Contabo #AuraInspector #ShinyHunters