A forum user known as 0xSec claims to have published three XLSX user tables from docurba.beta.gouv.fr, exposing 5,152 rows of French planning officials’ names, contact details, job titles, and authority data. The alleged leak also includes administrator and staff flags, verification status, and login indicators, but the claim remains unverified. #docurba.beta.gouv.fr…

A forum user posting as 0xSec claimed to share the database of metabase.dipeeo.fr, a French GDPR compliance provider serving organisations with outsourced Data Protection Officer services and compliance software. The release reportedly contains eleven JSON collections with client, legal officer, user, subcontractor, and processing records, but the claim remains unverified and…
A forum actor posting as 888 is offering what they claim is the MyNewTerm database in a one-time Monero sale, with the alleged breach said to expose 142,653 unique users. The reported data includes applicant email addresses, job application outcomes, recruiter notes, and vacancy details tied to UK education recruitment. #MyNewTerm…

Verifiable search data gives AI and security teams an observable, reproducible input source that improves traceability, testing, and incident review. By replacing opaque signals with structured public search records, teams can better verify citations, monitor drift, and maintain control over model behavior. #SerpApi #AlaaAbdulridha

Daily Recap, South Korean startup platform breach coverage highlighted major key management and secret-handling failures, while Uber was fined nearly $1 billion by Dutch regulators over automated driver-account suspensions and related privacy concerns. On the patching and vulnerability front, Spring received fixes for 91 vulnerabilities and Microsoft warned about August update compatibility issues affecting WPF printing/PDF export and shared a temporary workaround for Windows 11 gaming problems, plus a Venezuelan defendant received a record federal prison term for ATM jackpotting. #SouthKorea #KeyBreach #Uber #DutchRegulators #SpringApplicationFramework #WPF #Windows11 #ATMJackpotting
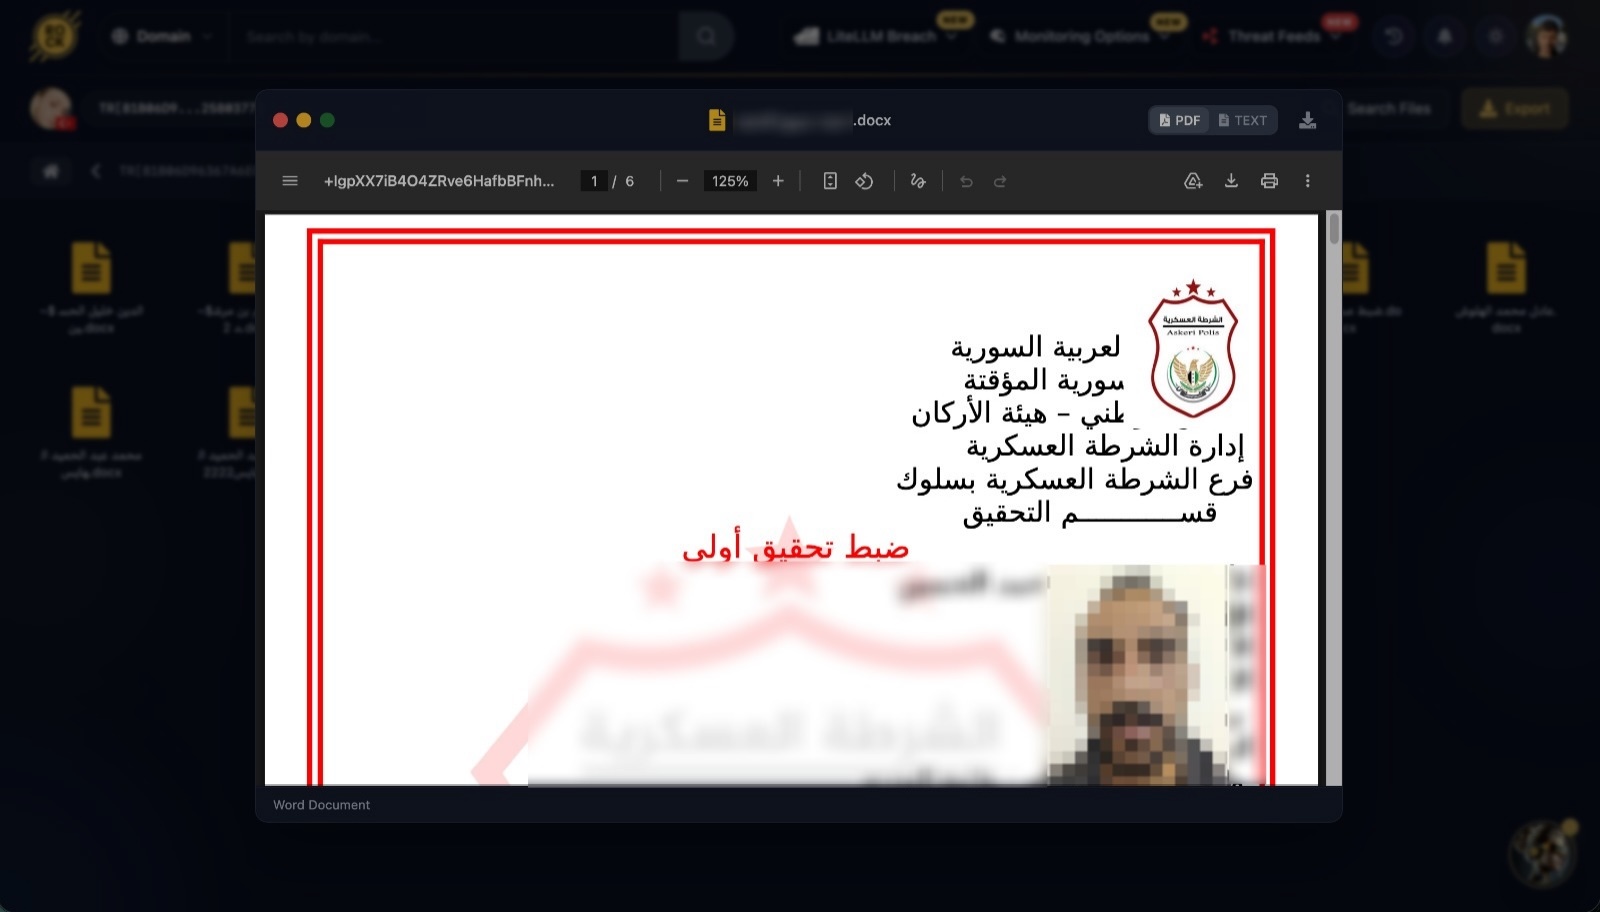
A RedLine infostealer infection on a Syrian National Army Military Police officer’s computer exposed active interrogation records, detainee photographs, family details, and signed confessions from the Suluk unit. The recovered files also showed alleged espionage claims, a soldier-run smuggling network, and at least one rewritten statement, all stored unencrypted on the officer’s desktop. #RedLine #SyrianNationalArmy #MilitaryPoliceSuluk #AhraralSharqiya #JayshalMajd #20thDivision

Oasis Security disclosed a weakness in NVIDIA NemoClaw that could let an attacker-controlled webpage take over a locally hosted Ollama instance and poison a model’s chat template with hidden instructions. NVIDIA fixed the issue for macOS and Linux in NemoClaw v0.0.35, but the Windows and WSL path remains unpatched and is…

The U.S. Treasury has imposed new sanctions on Iranian cyber actors and related networks under Operation Economic Outcast, targeting entities tied to the IRGC and MOIS. The action follows allegations of compromises against U.S. critical infrastructure, cryptocurrency theft, and broader Iran-linked cyber activity against U.S. and allied targets. #OperationEconomicOutcast #IRGC #MOIS…
Franklin Mint Federal Credit Union (FMFCU) experienced a website and digital banking outage after a domain issue disrupted access to its online services. The credit union said transactions continued to process and did not describe the incident as a cyberattack. #FranklinMintFederalCreditUnion #FMFCU #GoDaddy #fmfcuorg
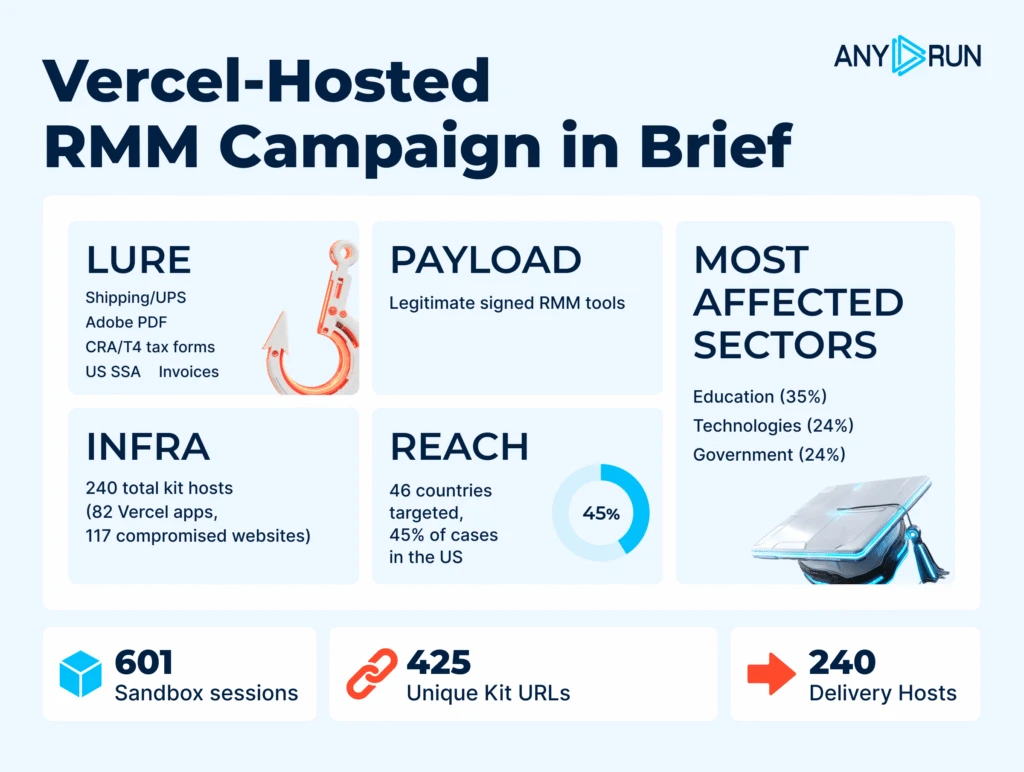
A phishing campaign that starts with fake CRA T4 tax documents is actually a 46-country operation that abuses legitimate remote management software to gain hands-on access to victim machines, with the United States accounting for 45% of observed activity. The kit reuses stable clues like fmtt, font1.woff2, and icons8-microsoft-word-94.png while rotating…
Operation Jackal IV led to 58 arrests and 263 identified suspects in a coordinated crackdown on West African organized crime networks involved in money laundering, scams, and asset concealment. Authorities also uncovered related schemes in Romania, South Africa, Argentina, and Italy, while warning of a growing sextortion trend targeting teenagers. #OperationJackalIV #BlackAxe #TheCom
CISA’s red-team tests found that a government organization was compromised and failed to respond effectively, while a water-sector organization detected the intrusion and quickly quarantined affected systems. Both organizations still had security gaps, including cloud-risk underestimation, missing Conditional Access for workload identities, and weak token revocation processes. #CISA #OrganizationA #OrganizationB

Studio Legale ESE, an Italian law firm providing legal services, was targeted by the direwolf ransomware threat actor, resulting in disruption of operations due to encryption and demands for ransom. This incident impacted IT #Italy
National Kidney Registry (US) reported a ransomware claim involving the direwolf threat actor, targeting its operations that coordinate kidney paired donation programs with transplant centers nationwide. The incident potentially disrupted healthcare services and access to transplant coordination within the United States. #UnitedStates
Unit 42 analyzed 405 AI-enabled malware samples and found that about 97% existed only in repositories, sandboxes, or testing environments, while just 12 appeared on production endpoints. The samples that reached real environments were detected and blocked by existing defenses, including FunkSec ransomware, a trojanized Recipe Lister installer, the Oyster backdoor,…