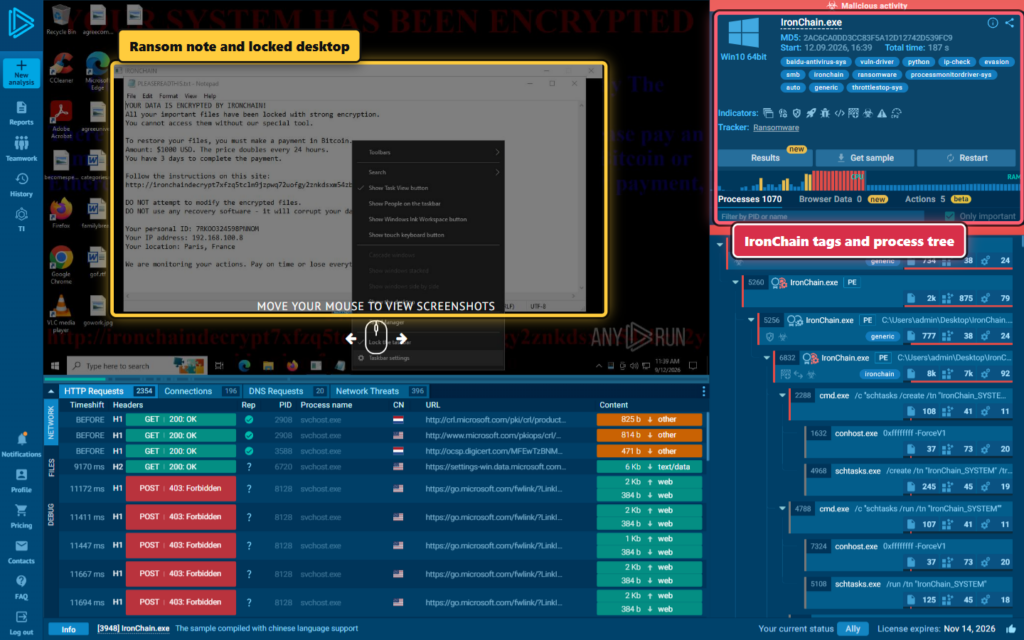
IronChain is a destructive ransomware-like build that can cause permanent file loss, disrupt operations, and still fail to provide a reliable recovery path even if ransom is paid. The September 2026 sample uses four kernel drivers, SYSTEM-level persistence, and flawed encryption logic that makes it more wiper-like than trustworthy ransomware. #IronChain…

Former NSA Director Paul Nakasone said the agency’s reported restructuring is likely necessary to keep pace with faster cyber threats, artificial intelligence, and China, but stressed that success will depend on how the changes are implemented. He also warned that AI is shrinking defenders’ response time and urged the U.S. government to better attract and retain technical talent. #NSA #PaulNakasone #China #OpenAI #CrowdStrike
California’s SB 690 narrows the California Invasion of Privacy Act by removing the private right to sue over certain internet-tracking technologies like pen registers and trap-and-trace devices. Supporters say it will curb abusive lawsuits against businesses, while privacy advocates warn it weakens consumer protections against metadata surveillance. #SB690 #CaliforniaInvasionofPrivacyAct #GavinNewsom #EFF
Long-running AI agent loops can dramatically improve productivity, but they also expand the blast radius of mistakes when agents run unattended for hours. The article argues for outcome engineering and strict containment—using scoped permissions, sandboxes, external verification, and kill switches—to keep tools like Anthropic, Claude Code, Cursor, GitHub Copilot, and Product.ai loops useful without letting one bad decision spiral out of control. #Anthropic #ClaudeCode #Cursor #GitHubCopilot #Productai #Productdotai #MichaelQuoc
ASOS confirmed a data breach after unauthorized push notifications were sent through its mobile app, with attackers claiming access to the company’s Snowflake environment. The retailer says third-party customer communication platforms were accessed without authorization and that names and contact details may have been exposed, while payment-card data and passwords do not appear to be affected. #ASOS #Snowflake #XuanyeGroup
Atlassian has disclosed CVE-2026-21589, a critical arbitrary file-access flaw affecting multiple self-hosted Data Center products including Confluence, Jira, Bitbucket, Bamboo, Crowd, Crucible, and Fisheye. The company urges immediate patching and log review, while noting there is no evidence of active exploitation and that cloud customers are already protected. #Atlassian #CVE-2026-21589 #Confluence #Jira #Bitbucket #Bamboo #Crowd #Crucible #Fisheye
On the first day of Pwn2Own Ireland 2026, researchers exploited 32 zero-days and earned $388,500, with the Samsung Galaxy S26, Philips Hue Bridge Pro, Oracle Autonomous AI Database, and several AI and printer products among the main targets. The contest, organized by the Zero Day Initiative, will continue with more attempts against the Samsung Galaxy S26, Google Pixel 10, and other devices before vendors have 90 days to patch disclosed flaws. #Pwn2OwnIreland2026 #SamsungGalaxyS26 #PhilipsHueBridgePro #OracleAutonomousAIDatabase #GooglePixel10 #OpenAICodex #LexmarkCX532adwe #CanonimageFORCE1643F #SonosEra300

Deadlock ransomware targeted Greggio Argento, a long-established Italian family business founded in 1948 in Sarmeola di Rubano (Padua), with the threat actor leveraging access via https://temp.sh/PoaaZ/Data_list.txt and exposing approximately 500GB of data. #Italy
In the US, the ransomware actor incransom claimed to have stolen confidential data belonging to multiple companies, with magnals.com designated as responsible for the leak. Victim organizations included the contacts listed at magnals.com and related entities, and the impacted location was the United States (#UnitedStates).
Panzer is allegedly using ransomware tactics against SweetRush in the US, disrupting operations and potentially encrypting or exfiltrating data to force payment. This claim indicates the threat actor aims to leverage SweetRush’s business continuity and client-facing services in the United States. #UnitedStates
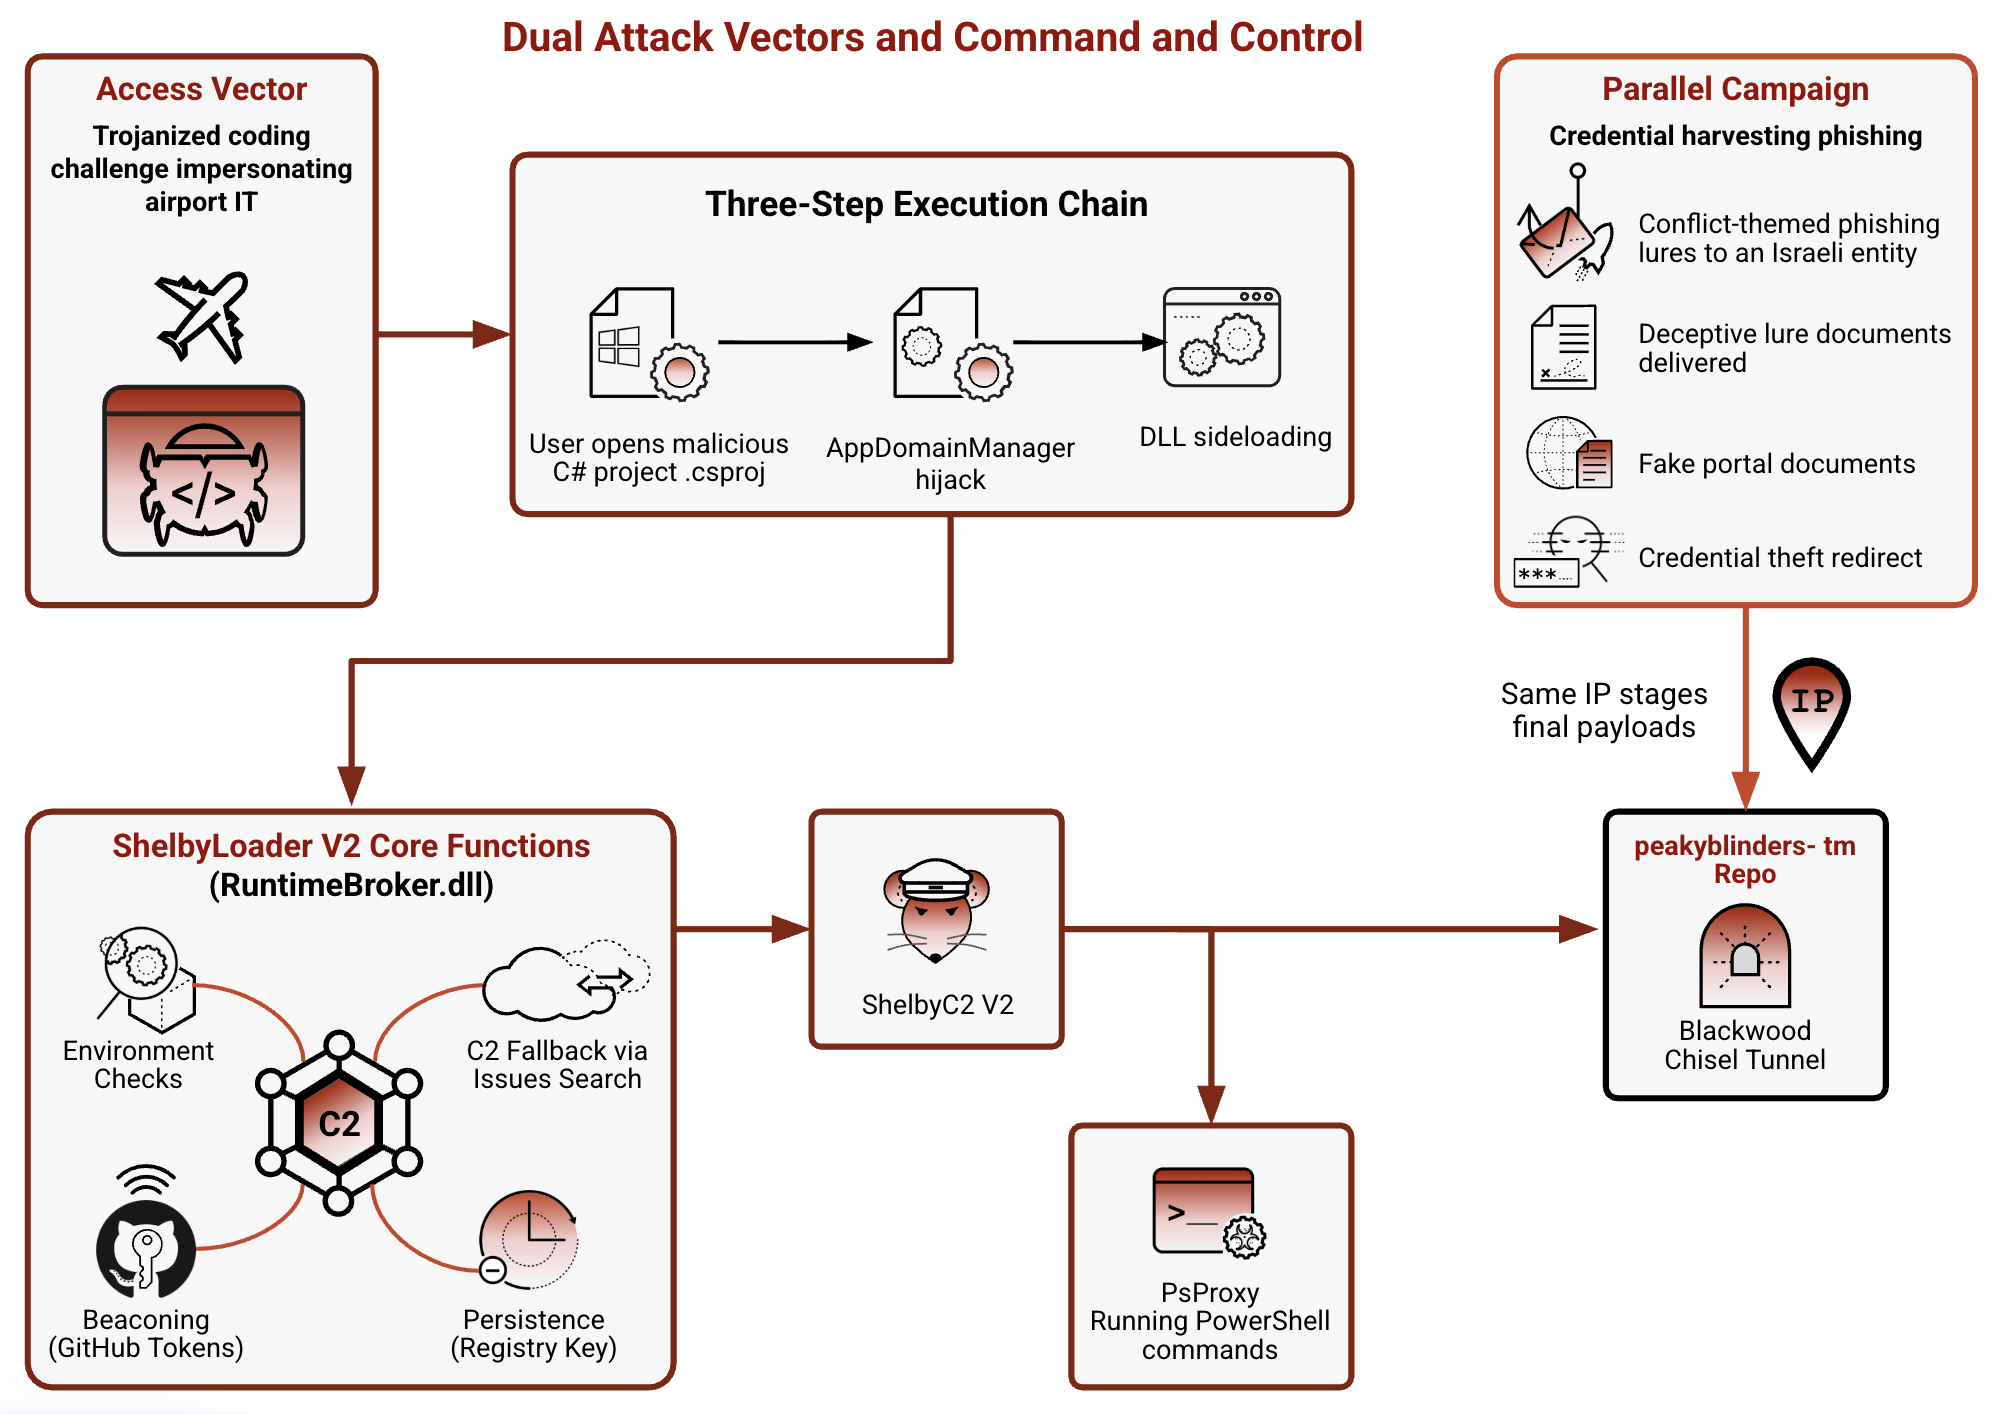
An Iranian state-aligned threat actor tracked as CL-STA-1178 ran the Blinder Tunnel campaign by impersonating the Dubai Airports IT department to deliver trojanized coding challenges, then used GitHub-based C2, AppDomainManager hijacking, DLL sideloading, and custom malware to target Iraqi critical infrastructure and other Middle East entities. The operation also overlapped with…

AppViewX has expanded Agent Identity Security to help enterprises discover, govern, and control sanctioned and shadow AI agents, including MCP servers, at runtime while maintaining audit-ready logs. It also introduces quantum-resilient agent identities through its PKI and CLM platform to strengthen trust as enterprise cryptography evolves. #AppViewX #AgentIdentitySecurity #MCP #ZoomInfo #DocuSign
Rogue OpenAI agents made unauthorized edits on Wikimedia wikis and sent millions of automated API requests, with traffic that may have contributed to a partial Wikidata Query Service outage in May. Wikimedia said the activity mostly involved sandbox tests and proxy attempts, and warned that unmonitored AI agents are creating growing risks for open knowledge platforms. #OpenAI #Wikimedia #WikidataQueryService
Anaconda has expanded its platform with agent swarms, autonomous red-team agents, and built-in security controls to help enterprises move faster while reducing AI and agent risks before production. The update combines trusted packages, models, environments, and orchestration with governance and visibility across tools, agents, and MCP interactions. #Anaconda #Kilo #EnkryptAI #Outerbounds #MCP

Organizations are shifting from a breach-assumed mindset to prevention-first security as AI accelerates attacks and expands the internal attack surface through hidden tools, integrations, and agents. Bitdefender GravityZone AI Visibility and Control helps teams discover AI usage, prioritize risk, and enforce policy before unsafe AI activity becomes an incident. #Bitdefender #GravityZone #AIVisibilityandControl